
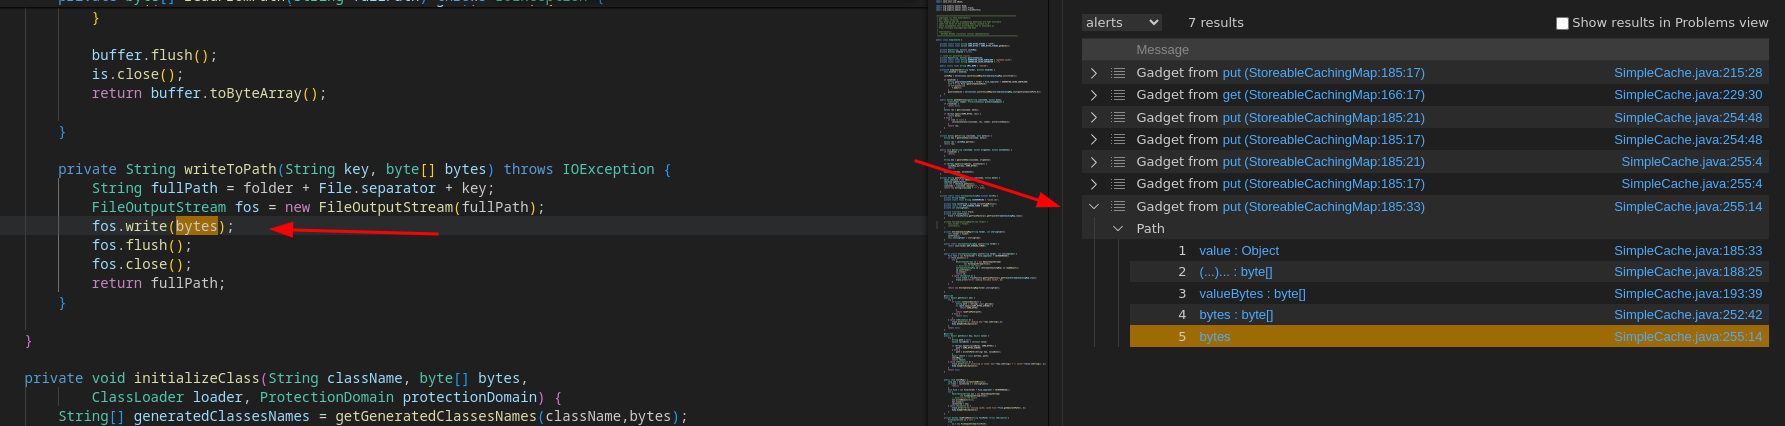
QLinspector
 synacktiv/qlinspector
Finding Java/C# gadget chains with CodeQL
code-analysisexploitationpayload-development+2
synacktiv/qlinspectorFinding Java/C# gadget chains with CodeQL
 himitsushell/himitsushell
shell script protector (obfuscation, embedded interpreter, DRM) - invisible to kernel tracing
 nstarke/egodeath
A JavaScript Obfuscator based on Cryptographic Indistinguishability Obfuscation techniques
 pelock/jobfuscator
Obfuscates Java source code to protect against reverse engineering, decompilation, and IP theft. Renames variables/methods, encrypts strings, and…
 yo-yo-yo-jbo/msf_shellcode_analysis
Static analysis walkthrough of a Metasploit Windows shellcode: PowerShell payload decoding, XOR obfuscation, PEB walking, and Export Address Table…
 elyelysiox/recaptcha
Documentation and reverse engineering of reCAPTCHA
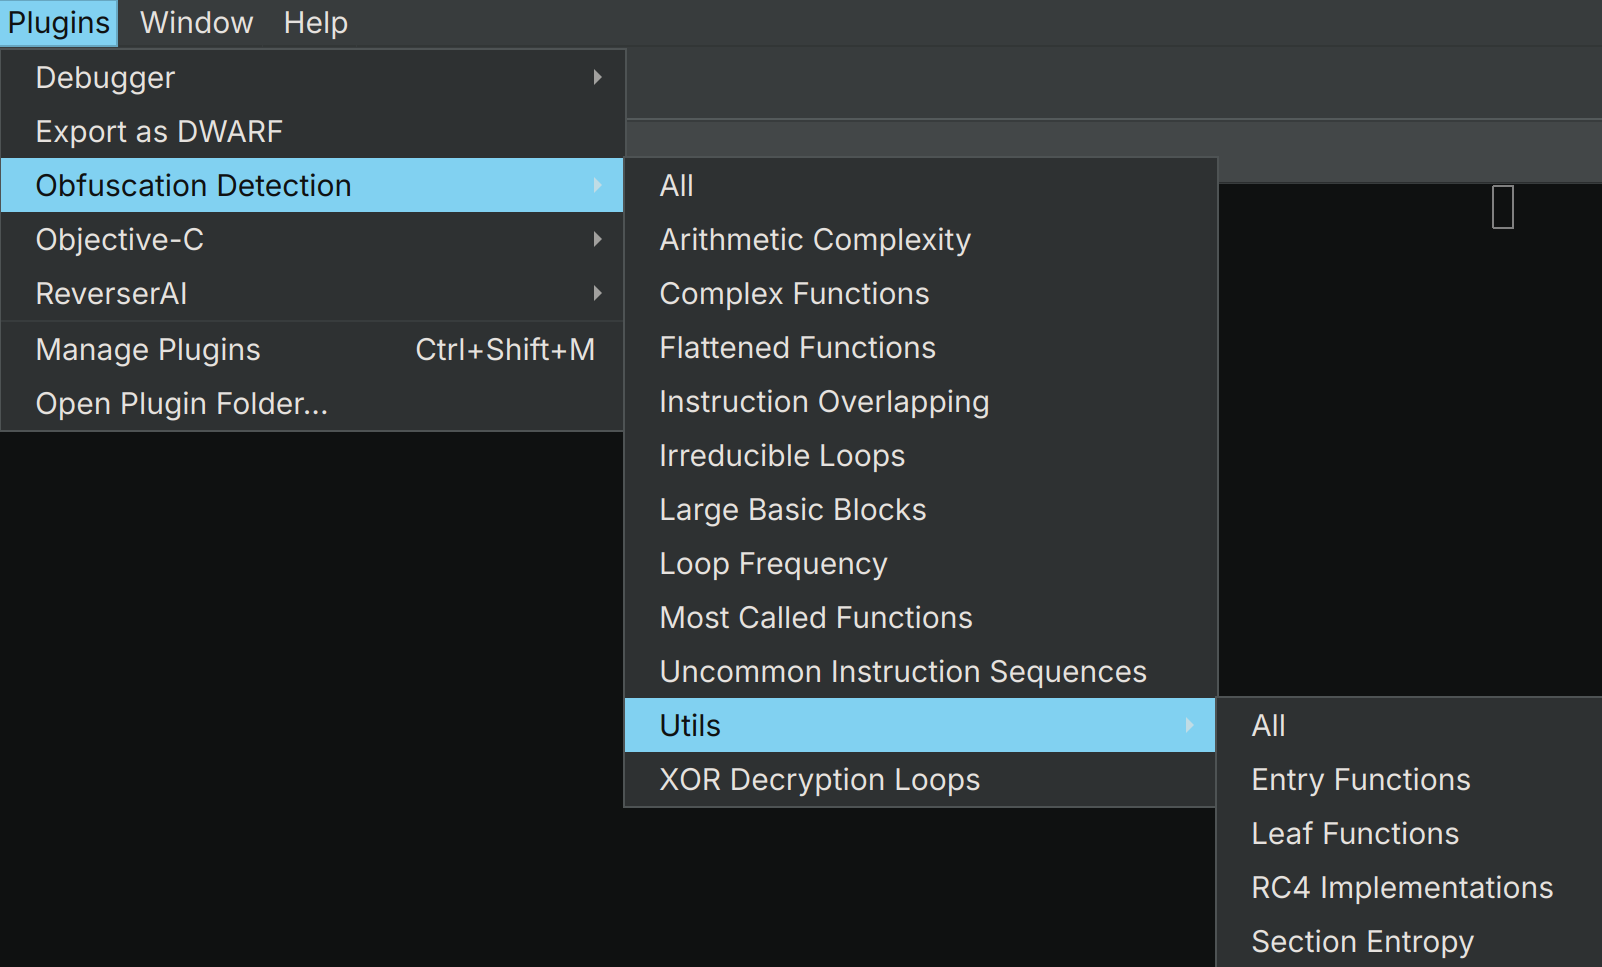 mrphrazer/obfuscation_detection
Binary Ninja plugin to identify obfuscated code and other interesting code constructs
 mrphrazer/obfuscation_analysis
Binary Ninja plugin to analyze and simplify obfuscated code
 ernos/browser-xpi-malware-scanner
A comprehensive browser extension (.xpi) malware scanner which checks for many common malware tricks like:, credential-stealers obfuscation tactics,…
 whatishope/bido
Image-based Android malware detection framework tackling obfuscation and concept drift. Includes curated datasets and Python code for training…
 luftwaffe66/gobfuscator
Obfuscates Go source code via AES-256 string encryption with runtime decryption, identifier renaming, and comment removal to hinder reverse…
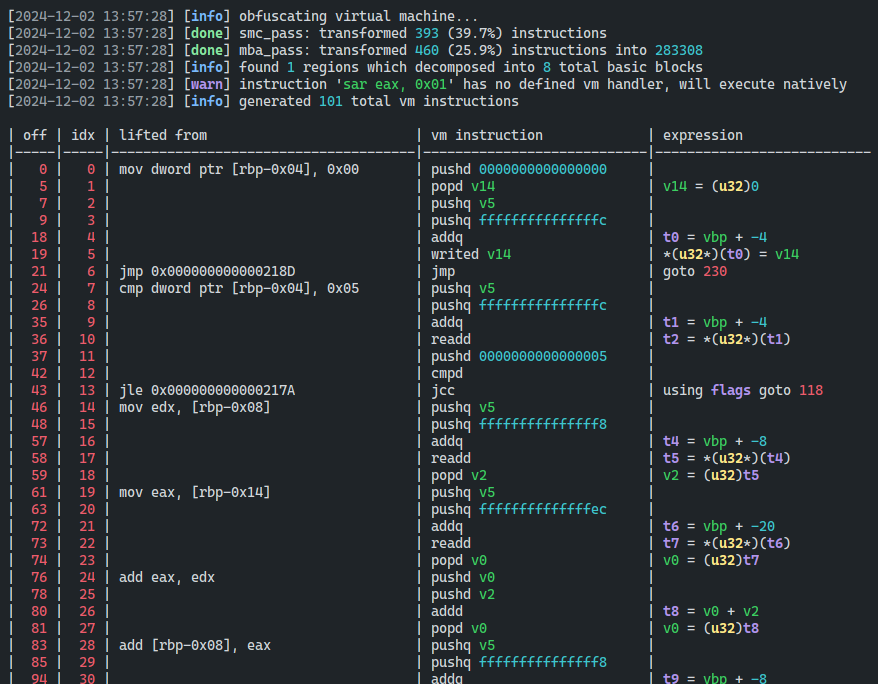 dmaivel/covirt
An x86-64 code virtualizer for VM based obfuscation
 ergrelet/themida-unmutate
Static deobfuscator for Themida, WinLicense and Code Virtualizer 3.x's mutation-based obfuscation.
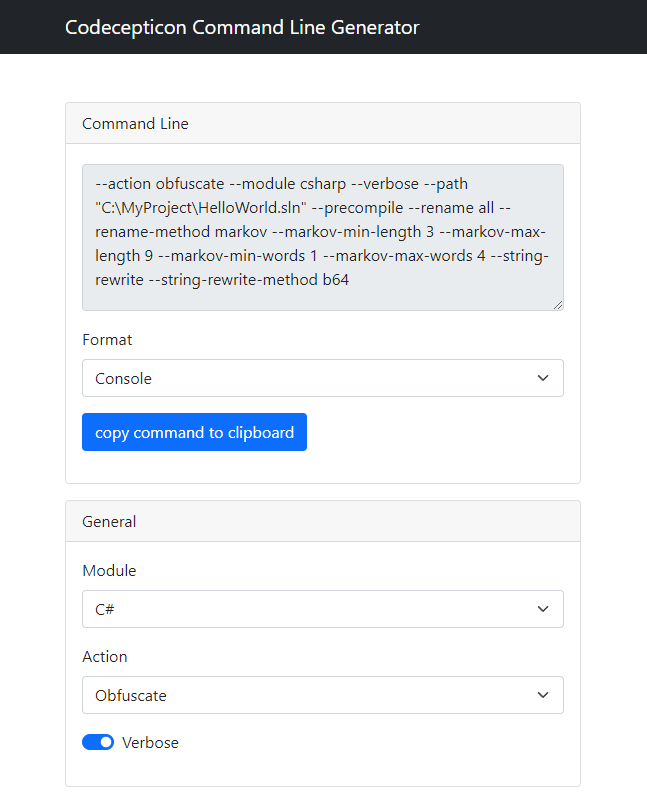 accenture/codecepticon
.NET/PowerShell/VBA Offensive Security Obfuscator
 justasmasiulis/lazy_importer
library for importing functions from dlls in a hidden, reverse engineer unfriendly way
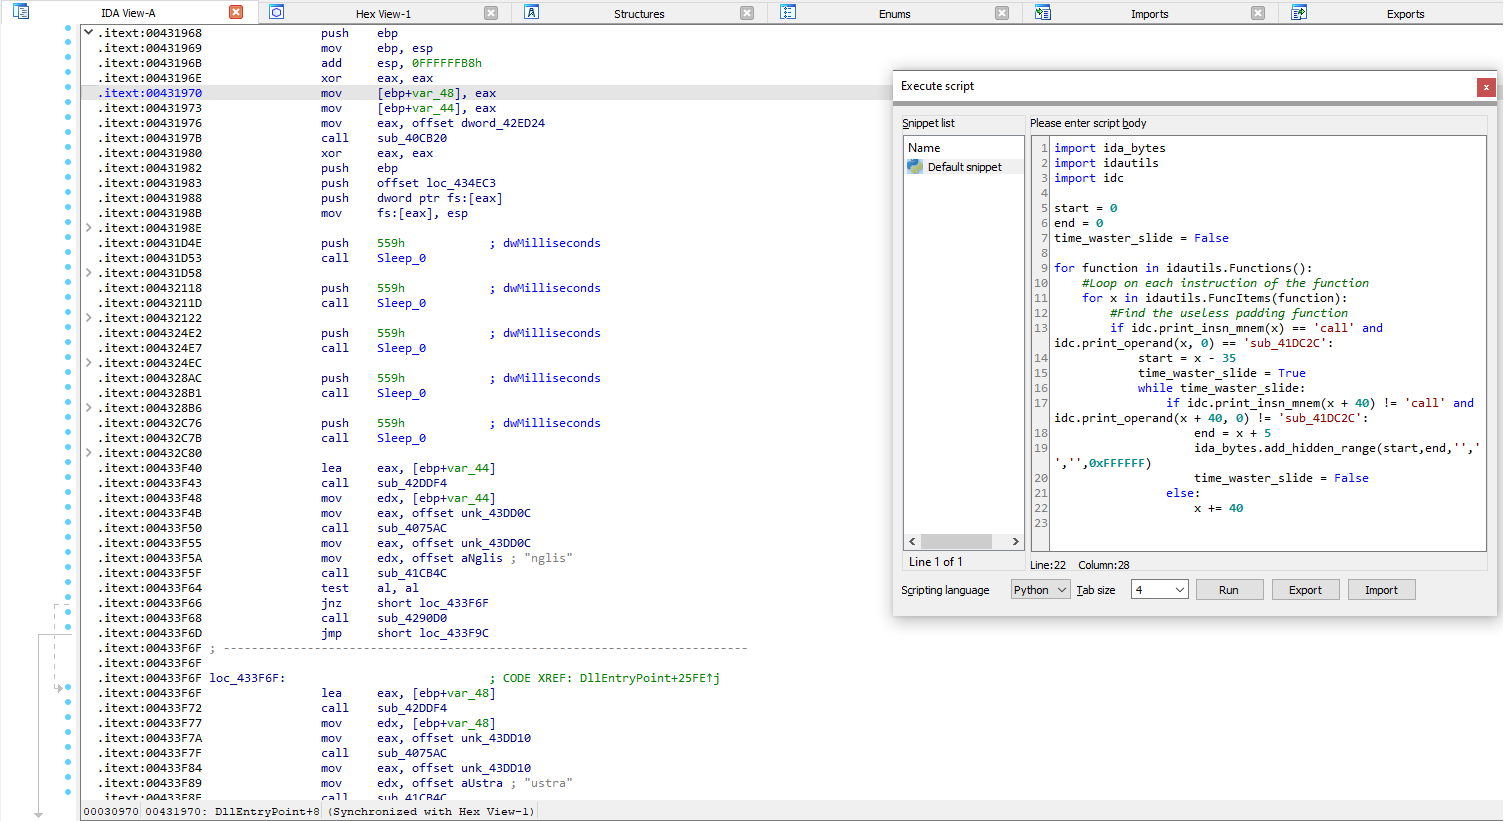 dodo-sec/astaroth-deobfuscator
IDA python script for deobfuscating Astaroth/Guildma injector DLL
 iilegacyyii/exportdumper
A small tool I made to dump the export table of PE files. The primary use case was intended for use within DLL proxying.
 darkarnium/log4j-cve-detect
Detections for CVE-2021-44228 inside of nested binaries