

s5e8835-sboot-probe
 yuki493/s5e8835-sboot-probe
Static S-Boot/LK probe for Samsung Exynos 1380 (s5e8835): SVE-2026-3546 / CVE-2026-21155 resolver patch, four-device coverage, and safety notes.
binary-analysisembedded-systems-securityexploitation+6
1
yuki493/s5e8835-sboot-probeStatic S-Boot/LK probe for Samsung Exynos 1380 (s5e8835): SVE-2026-3546 / CVE-2026-21155 resolver patch, four-device coverage, and safety notes.

 valtersit/java-cve-scanner
Scan Java projects via pom.xml or build.gradle — CVE matching for Maven/Gradle dependencies
 valtersit/ruby-cve-scanner
Scan Ruby/Rails apps via Gemfile.lock — matches gems against ValtersIT CVE database
 rahulreddykarne/ark-wp-scanner
Scans WordPress plugins for missing-guard vulnerabilities using ripgrep signatures, Semgrep rules, attack-surface mapping, and an LLM review cascade…
 daveyd347/secrets-scanner
Dependency-free secrets scanner for source code and git history that detects leaked API keys, tokens, and private keys, with redacted output and a…
 aboutcode-org/scancode-toolkit
🔍 ScanCode detects licenses, copyrights, dependencies by "scanning code" ... to discover and inventory open source and third-party packages used in…
 mosajjal/fortitool
Fortinet Firmware decryption and analysis tools
 filipi86/drogonsec
High-performance open-source security scanner combining SAST, SCA, Secret Detection, and IaC analysis, built for developers and CI/CD pipelines,…
 droncito/aquadecomp
Orchestrates JADX, CFR, Procyon and Vineflower to decompile Android APK/AAB/XAPK/APKS files, with hidden DEX extraction, deobfuscation, signed APK…
 seifheakal/blue-harness
Make your own app expensive to reverse. A build-time audit, harden and verify harness for native binaries and mobile apps, built to counter…
 theauditortool/benchproctor
Open SAST benchmark corpus: 2,938,418 balanced cases, 11 languages, 21 framework targets, 242 emitted categories, and 231 distinct CWE IDs. Score…
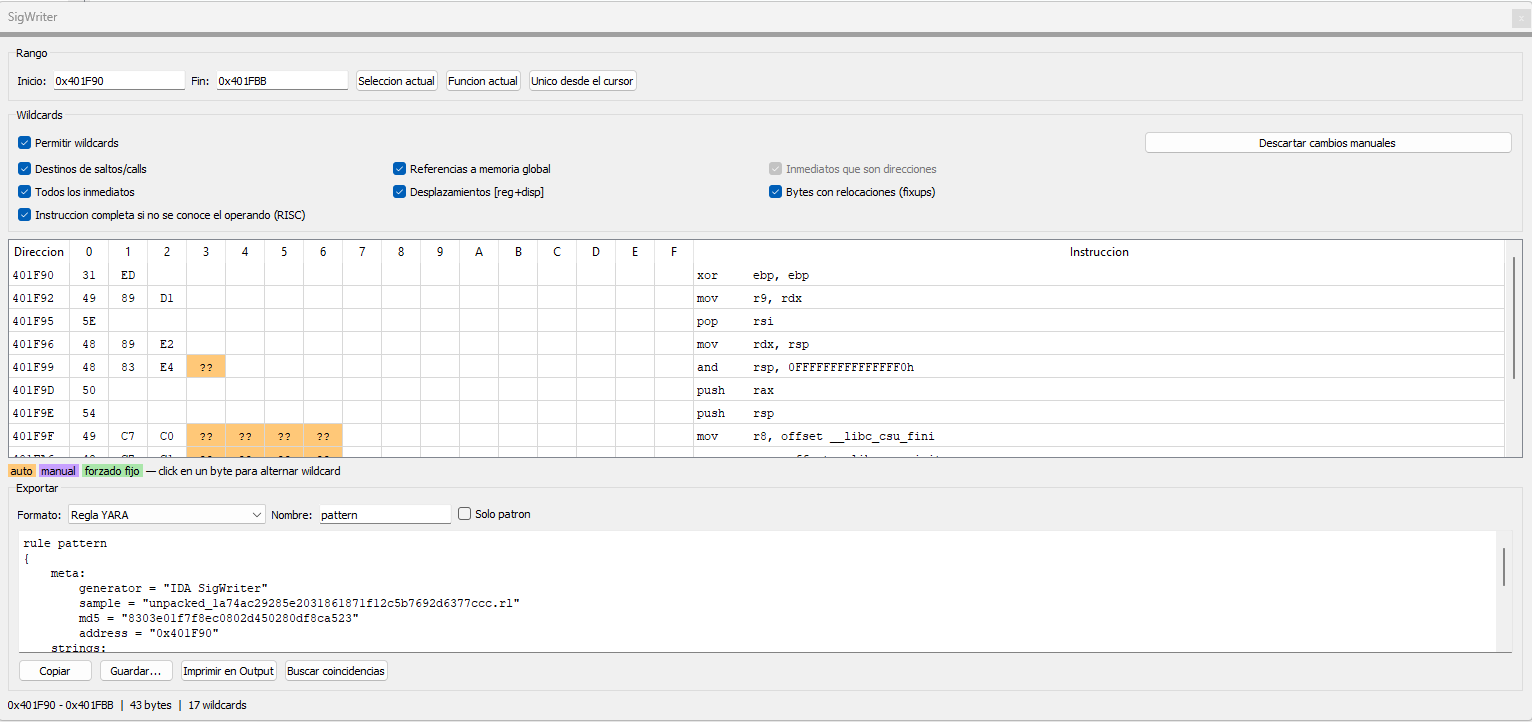 crackinglandia/idasignwriter
IDA Pro plugin that generates byte signatures from disassembly selections, with automatic and manual wildcards, match search, and export to YARA,…
 ryftenius/resx
Specialized Windows Reverse Engineering & Binary Analysis Toolkit | API Deobfuscation, Call Graphs, Kernel Driver & IOCTL Analysis
 drau6/keydra
CLI scanner that detects leaked API keys, tokens, and credentials in source trees and deployed web apps, with Supabase/Firebase misconfiguration…
 ph4ntom-rev/ph4ntom-vitrum
In-vitro static malware dissection pipeline for Telegram, AI agents (Antigravity / Local Ollama / OpenCode), and IDA Pro 9.5 via ph4ntom-ida-bridge
 movray/meles
Malware scanner for container images: daemonless, layer-aware, ClamAV and YARA
 bakhishovism/vyrulix
Open-source, bare-metal desktop malware triage and static threat intelligence workbench for Windows (MapViewOfFile PE parsing, Capstone disassembly,…
 debugactiveprocess/maldoctrace
Defensive Office macro analyzer that extracts VBA and XLM, deobfuscates strings, and emulates macros in a simulated sandbox to recover commands,…