
aegis
 1llu50ry/aegis
Single-header C++20 software protection SDK with polymorphic VM code virtualization, compile-time MBA and string obfuscation, 25+ crypto primitives,…
anti-botbinary-analysiscryptography+6
3
1llu50ry/aegisSingle-header C++20 software protection SDK with polymorphic VM code virtualization, compile-time MBA and string obfuscation, 25+ crypto primitives,…
 ght657/work1-secure-api
HDU IS Work 1 - Secure REST API (Flask) with CI/CD (pytest + bandit + pip-audit) and CVE-2018-17246 analysis
 secprbench/secprbench
Benchmark of 265 real vulnerability-introducing code changes across nine C, C++, and Rust projects, with paired review tasks, Docker sandbox, judge,…
 ntoskernel/deepsecrets
Offline secrets scanner combining regex rules, lexer-based semantic analysis, and hashed-value matching to detect exposed credentials in code with…
 lzh0082-cloud/code-detection
Replication package studying how LLM vulnerability auditors defer to static-analysis evidence, with a tree-sitter C/C++ front end, controlled…
 endrazine/rocq-cve-poc-12155
CVE-2020-37268 — Rocq/Coq Print Assumptions Omits Unsafe Universe Checking via Parameter Inline
 nanashili/rea-rust
Rust port of REA, a local-only reverse-engineering tool with CLI/MCP workflows and a native Ghidra worker
 adam-atlassoftware/kraken
Reverse-engineering workbench built on Ghidra's decompiler with a native Java-free engine, AI-assisted function analysis, byte patching, sandboxed…
 betterleaks/betterleaks
Fast, configurable secrets scanner for filesystems, git history, containers, and cloud sources, with Expr-based filtering, credential validation, and…
 cdxgen/cdxgen
Creates CycloneDX Bill of Materials (BOM) for your projects from source and container images. Supports many languages and package managers. Integrate…

 divyanshukumar0014/shipproof
Automated SOC 2 change management for GitLab CI.
 odomojuli/regextokens
list of regex patterns for oauth / api tokens with provided source
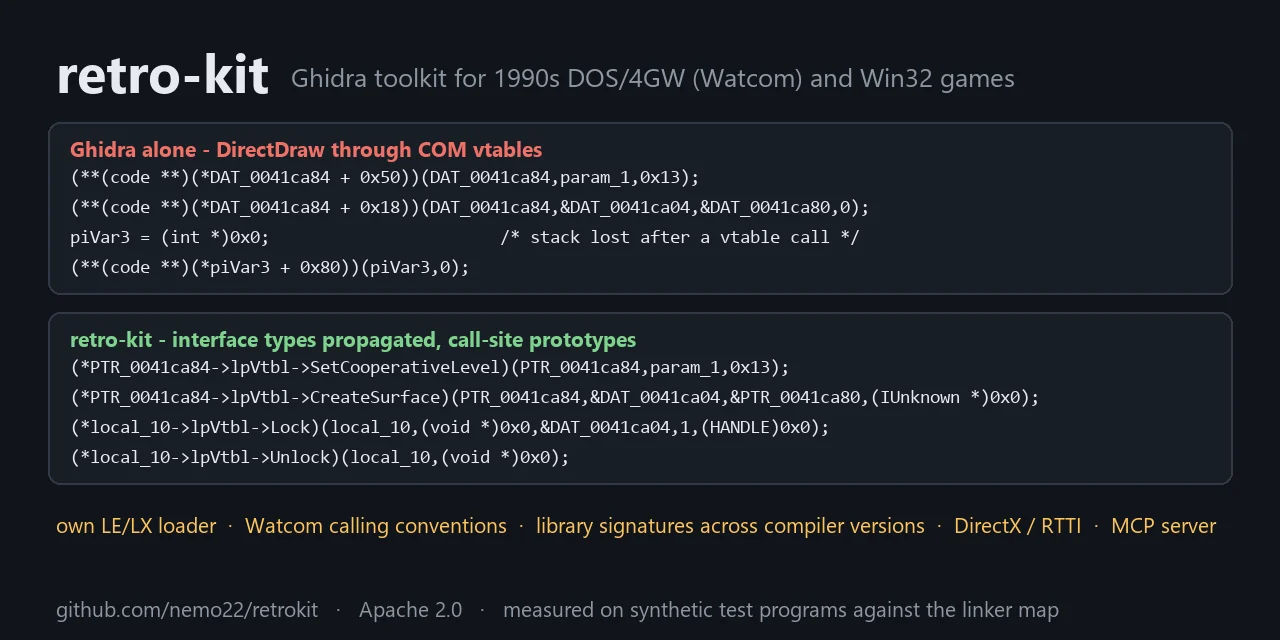 nautilusbits/retrokit
Headless-Ghidra toolkit for reverse engineering 32-bit DOS and Win32 games (1993-2010): own LE/LX loader, Watcom calling conventions, library…
 mr-wolf-is-me/ida-processor-modules
IDA Pro processor modules adding disassembly support for uncommon CPU, DSP, and GPU architectures including XMOS xCORE, TI C7x/PRU, MicroBlaze, and…
 yuatemycat/superghidra
Python toolkit accelerating Ghidra with a cached daemon, ARM64 P-code lifting, Z3 equivalence proofs, GPU-accelerated scanning, binary diffing, and…
 edoardottt/openhands-disclosure
Multiple Command Injection vulnerabilities in openhands <0.62.0 allow an attacker to run arbitrary system commands.
 lsudoko/antibody
GitLab Duo DevSecOps loop where a second AI re-attacks every AI-written fix, saving each successful bypass as a permanent antibody replayed in CI and…
 eliavila10/win32_hash
Password hashing and verification library for Windows, written in Ada/SPARK using the Windows CNG API (bcrypt) and proved with GNATprove.