Mobile-Security-Framework-MobSF

Automated mobile application security testing framework for Android, iOS, and Windows. Performs static and dynamic analysis, malware detection, and…

Automated mobile application security testing framework for Android, iOS, and Windows. Performs static and dynamic analysis, malware detection, and…

0-day malware detection for binaries, source & scripts (that doesn't suck)

The community's most comprehensive, continuously-updated index of research on Large Language Models for software vulnerability detection — papers…

Top-level repository for LFI: Practical, Efficient, and Secure Software-based Sandboxing

Firmware Analysis and Comparison Tool

The reverse-engineering expert agent: plans its own analysis path, derives every fact from raw evidence, and converges under mechanical verification…

AI-powered Docker security scanner that explains vulnerabilities in plain English. An OWASP Lab Project.

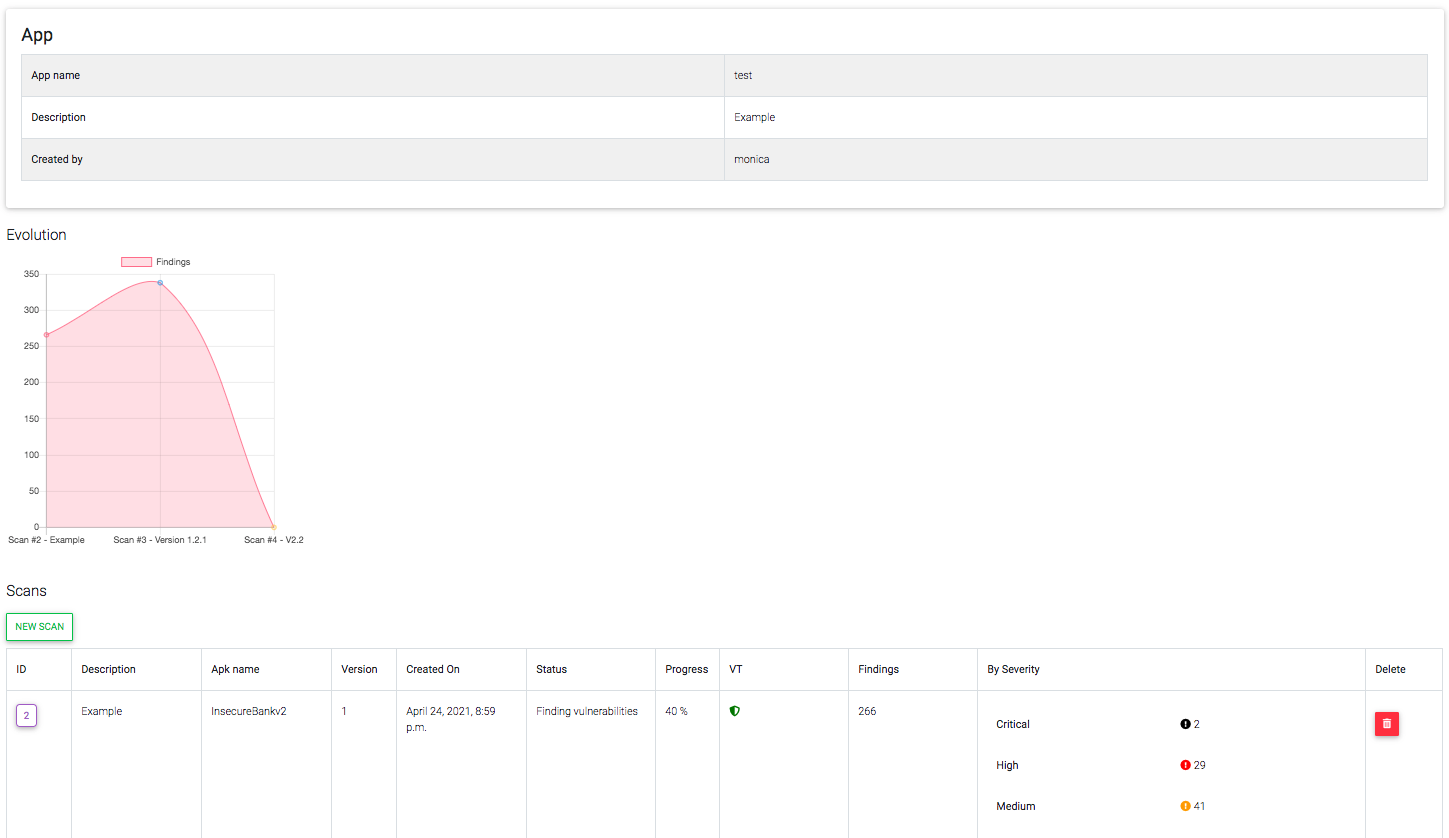
Django application that performs SAST and Malware Analysis for Android APKs

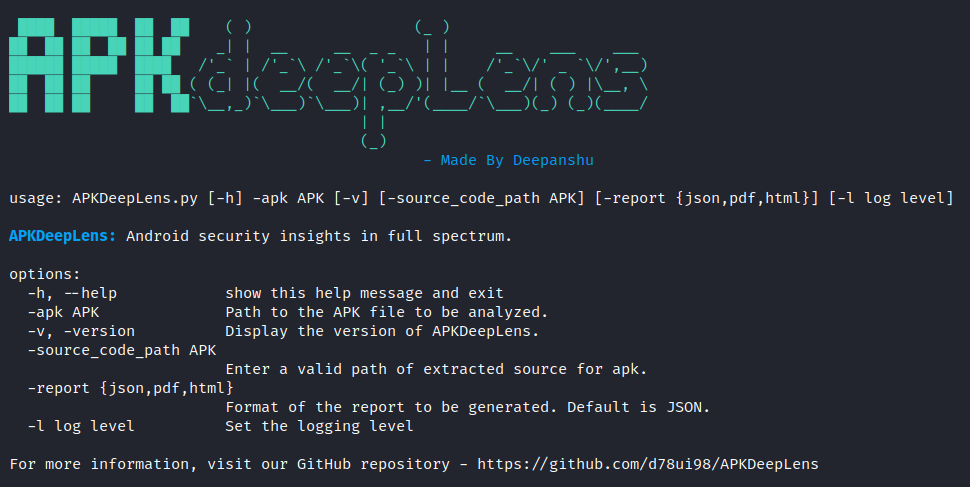
Android security insights in full spectrum.

KubeLinter is a static analysis tool that checks Kubernetes YAML files and Helm charts to ensure the applications represented in them adhere to best…

MCP server for reverse engineering Windows executables and binary formats. Combines static triage, Ghidra-assisted function recovery, plugin-driven…

Client-side PKI toolbox that decodes X.509, CSR, chain, CRL, PKCS#7 and PKCS#12 artifacts, views ASN.1, converts formats, and generates self-signed…

Ghidra is a software reverse engineering (SRE) framework

Workshop on firmware reverse engineering

The independent security agent for AI-written software. Finds issues, investigates whether they are real, and shows you the evidence. Deterministic…

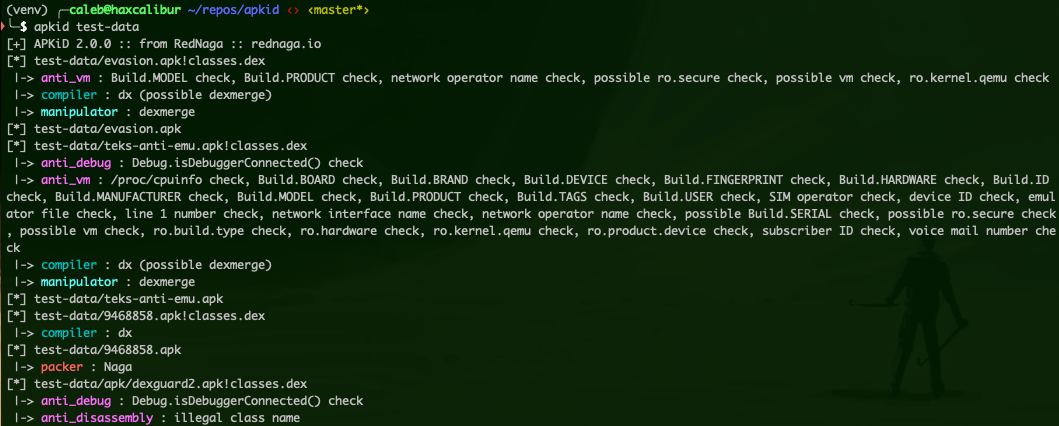
Android Application Identifier for Packers, Protectors, Obfuscators and Oddities - PEiD for Android

Symbolic execution tool

Formal inter-procedural taint analysis engine for application security. Tracks untrusted data across function boundaries, persistence layers, and…