
fish-live-in-trees
 loophole-llc/fish-live-in-trees
Gemini - Production LLM Runtime Alignment Context Injection
adversarial-attackai-securitycurated-resources+3
3
loophole-llc/fish-live-in-treesGemini - Production LLM Runtime Alignment Context Injection
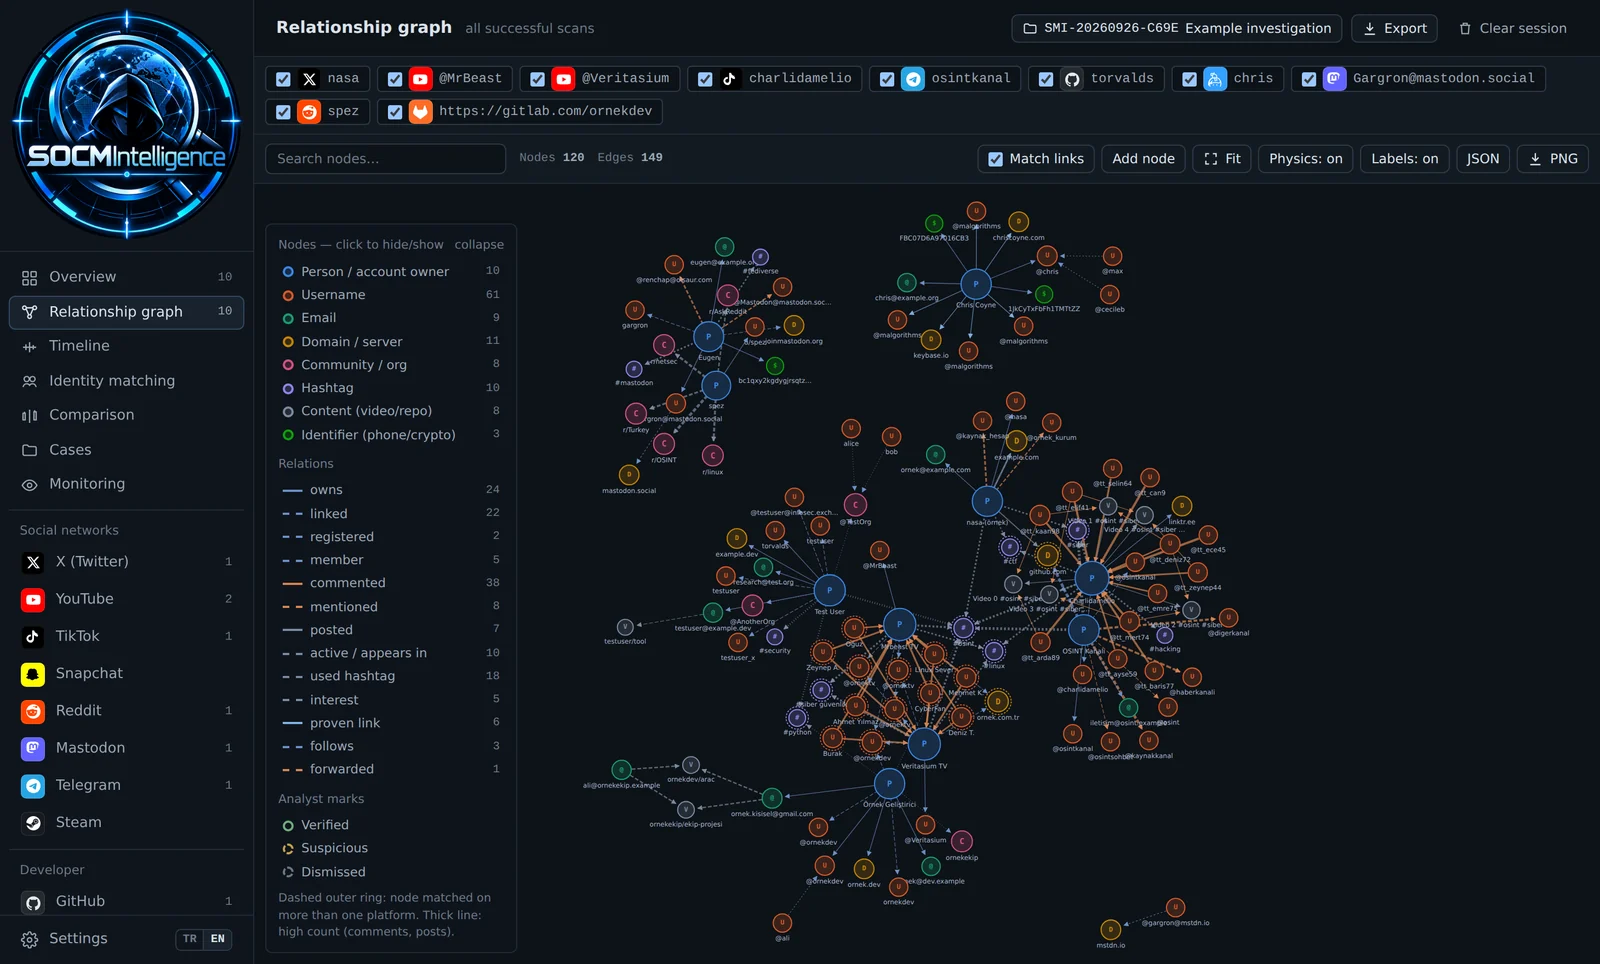 emrekybs/socmintelligence
A modular OSINT & SOCMINT framework for social media intelligence, investigation, and public data analysis.
 shaheeryasirofficial/smugglemypayload
Generates HTML smuggling pages that embed and reconstruct files client-side via JavaScript, with payload encoding, chunking, obfuscation, and…
 gmh5225/fullscreenbrowserphishing
PoC of the phishing through setting browser in the fullscreen mode
 gmh5225/definitelynotphishing
Contains evilginx phislets, gophish templates, burp suite extensions etc.
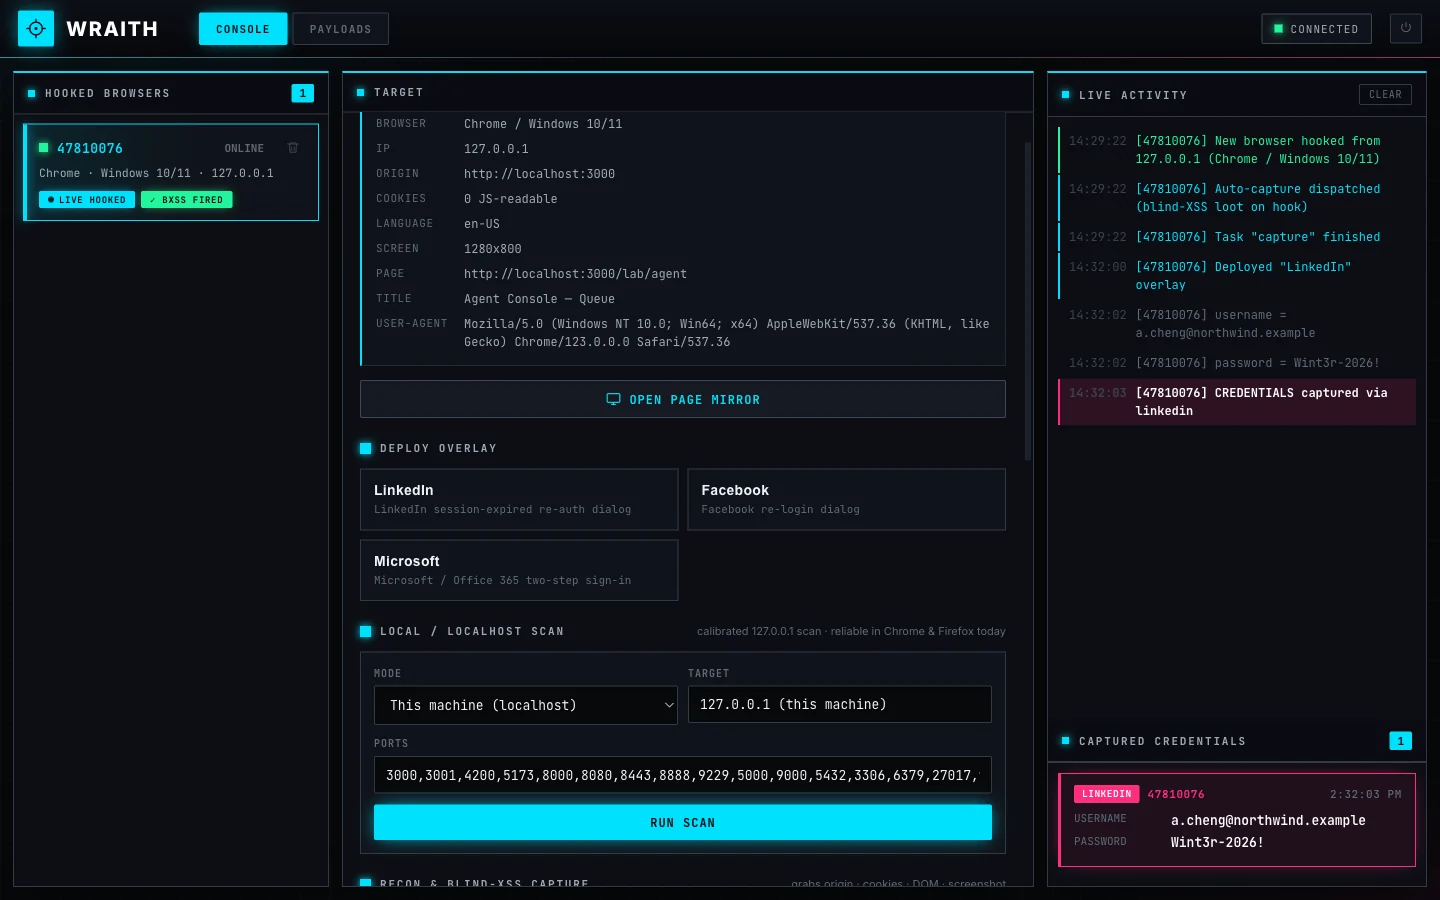 arcanum-sec/wraith
Browser-hooking framework for authorized red teams and educators. Hooks browsers via XSS, provides interactive post-exploitation control, blind-XSS…
 jeet-ganguly/birdy-edwards
Automated AI powered Facebook intelligence tool for target profiling, network analysis and threat reporting. Runs entirely on-device via Ollama.…
 specterops/skills
Reusable offensive security skills and plugins for AI agents, covering reconnaissance, exploitation, C2, payload development, and reporting across…
 exfil0/weaponizing-cve-2024-4367
CVE-2024-4367 is a critical vulnerability (CVSS 9.8) in PDF.js, allowing arbitrary JavaScript code execution due to insufficient type checks on the…
 elenichristopoulou/poc-cve-2026-20841
Proof-of-concept exploit for CVE-2026-20841, a Windows Notepad remote code execution vulnerability, using a crafted .md file and social engineering…
 azhariramadhan/cve-2026-39047
Printer exploitation framework for security testing via raw port 9100, featuring PCL payload delivery, DoS bombing, C2 QR codes, phishing QR codes,…
 keepwannabe/whatsrce
This is a Automated Generate Payload for CVE-2019-11932 (WhatsApp Remote Code Execution)
 toxy4ny/bl00dym4ry
Educational trojan simulator for cybersecurity training, simulating phishing attacks with social engineering, system reconnaissance, anti-sandbox…
 webbreacher/whatsmyname
Community-maintained dataset of 700+ websites for finding accounts by username — powers OSINT and digital footprint tools.
 ransomleak/training-security-awareness
Open-source interactive security awareness training library with 130+ SCORM exercises covering phishing, vishing, BEC, MFA fatigue, and OWASP AI/LLM…
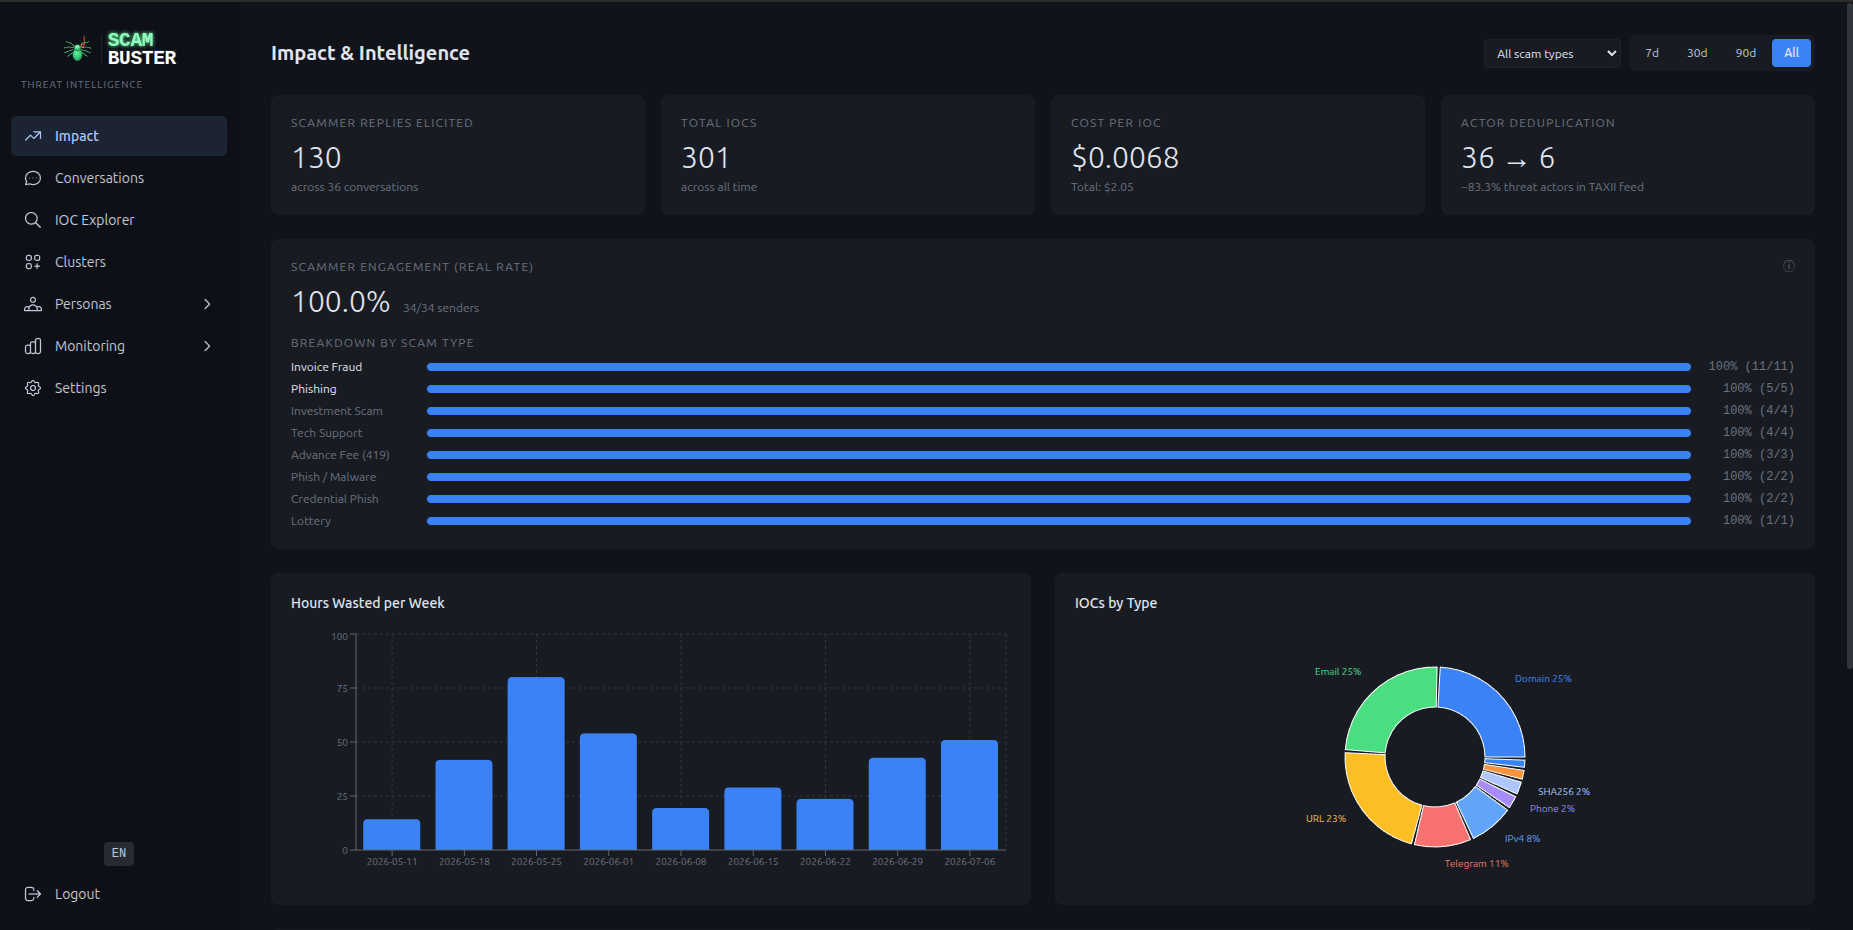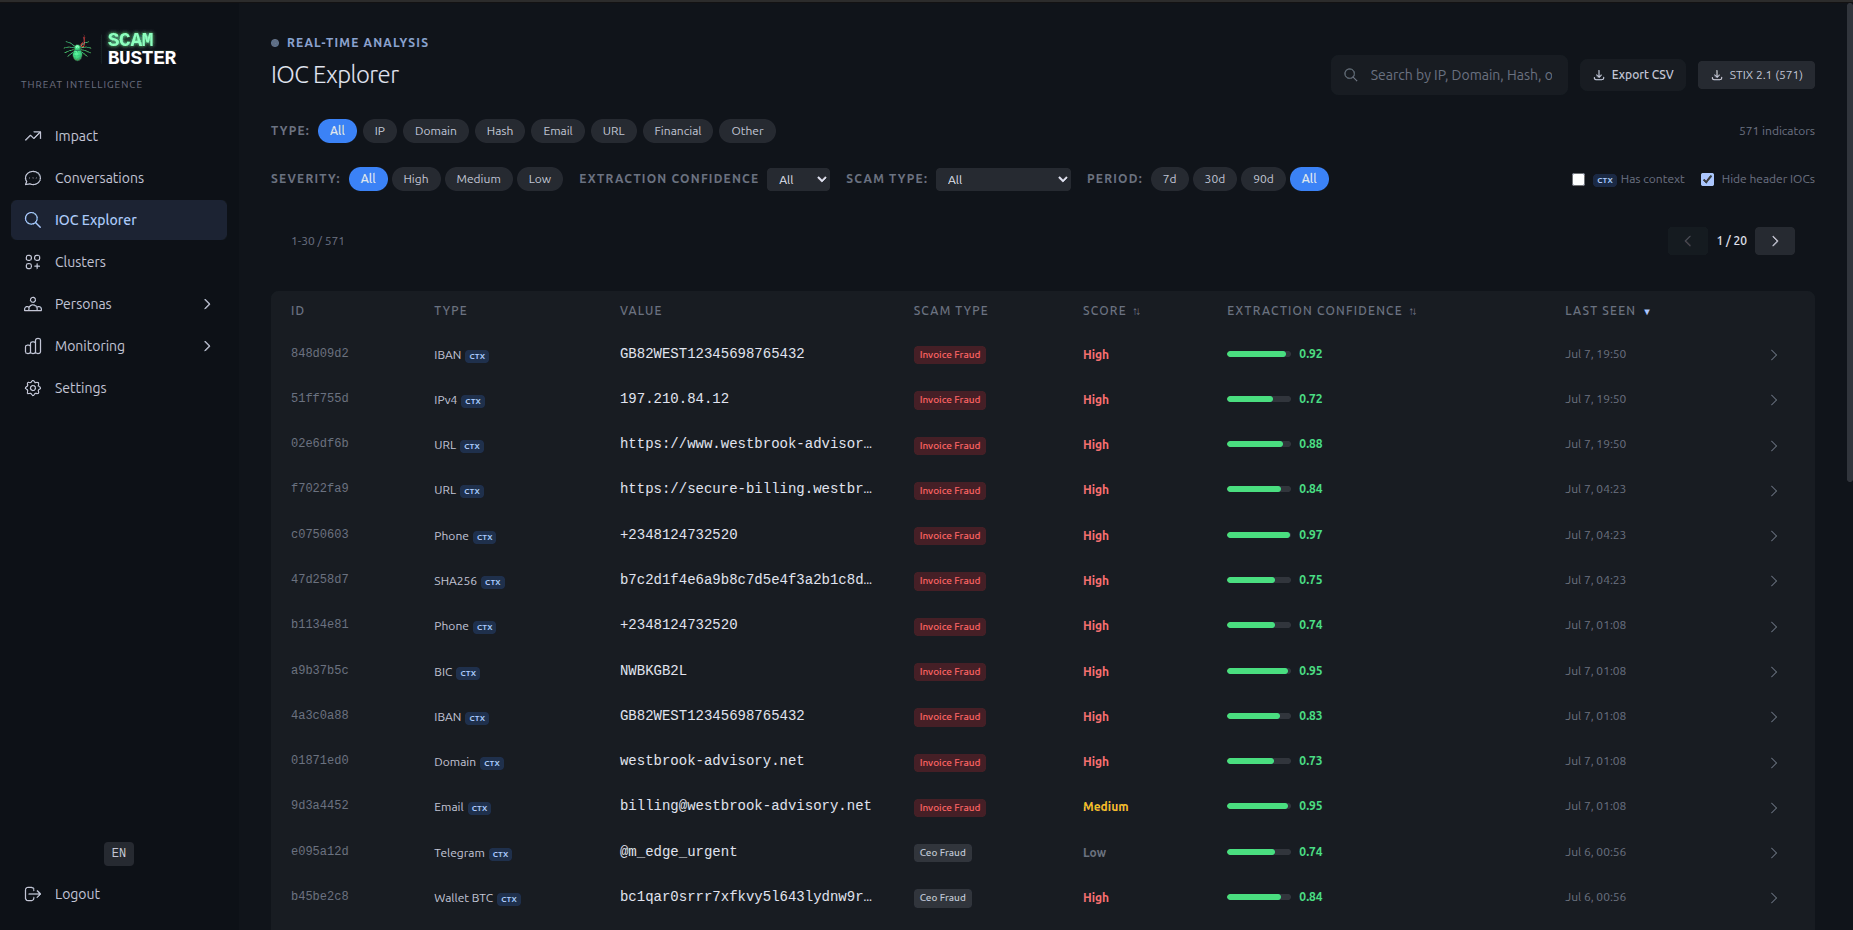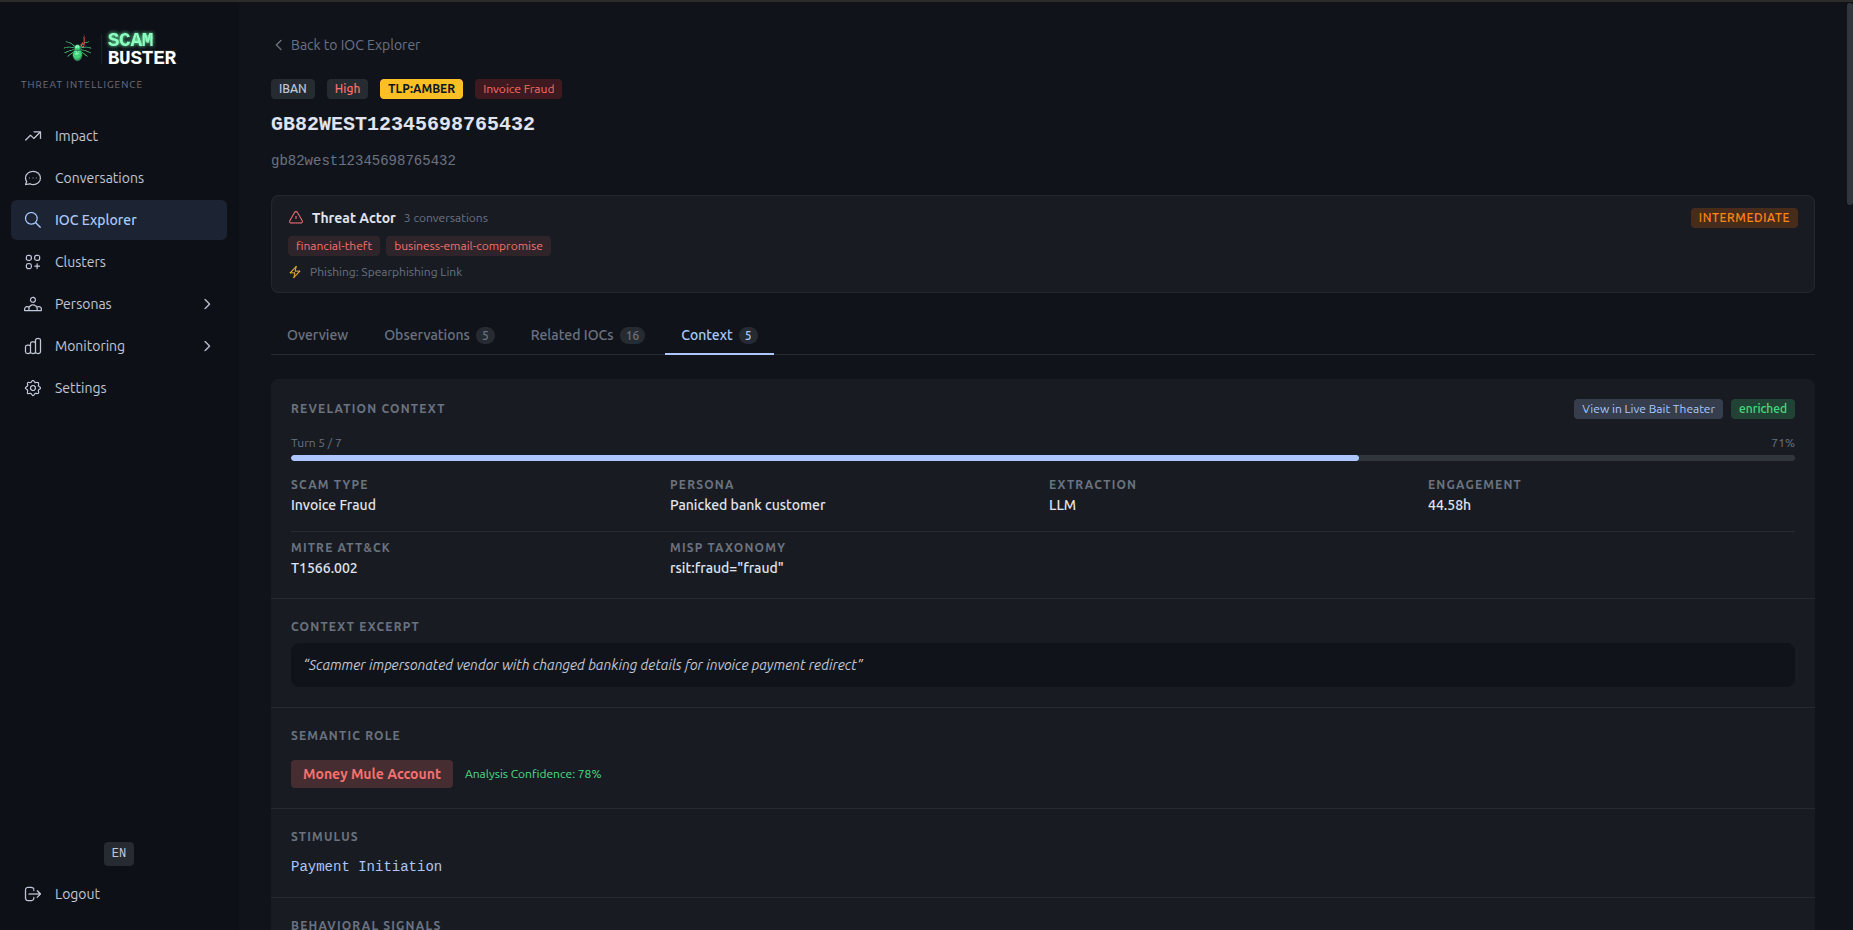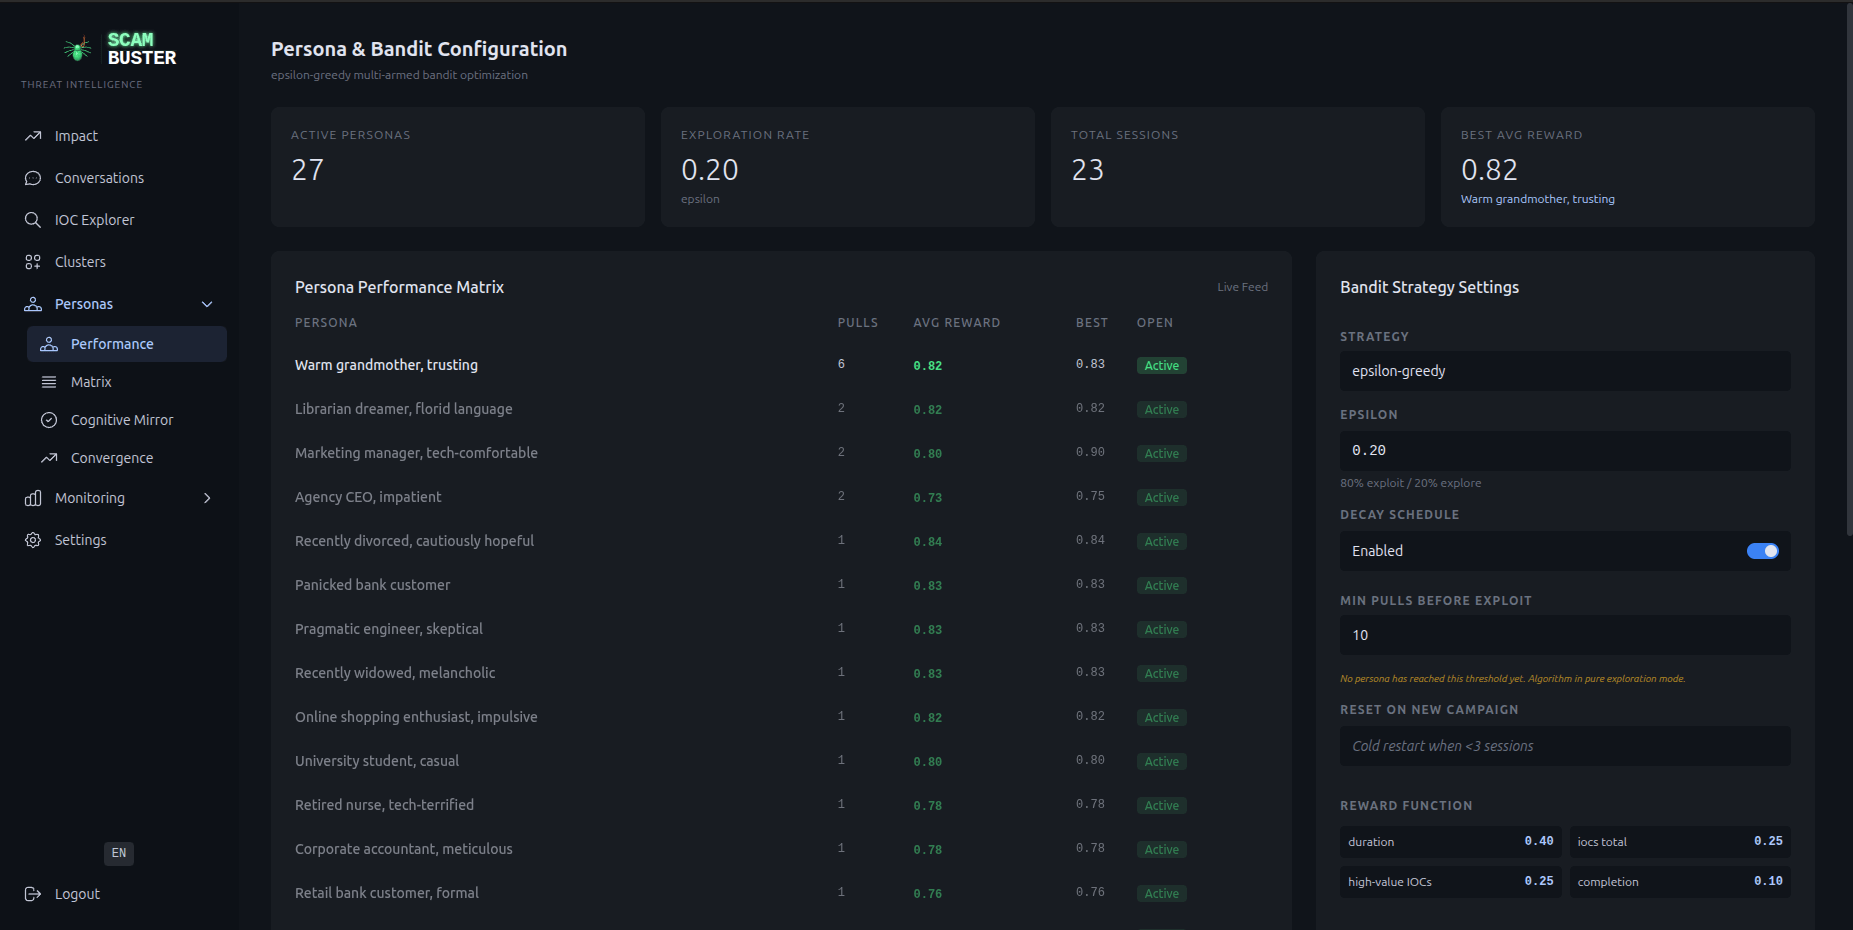 laugiov/scambuster
Defensive engagement & threat intelligence research laboratory. Converts inbound scam emails into actionable IOCs through controlled, policy-driven…
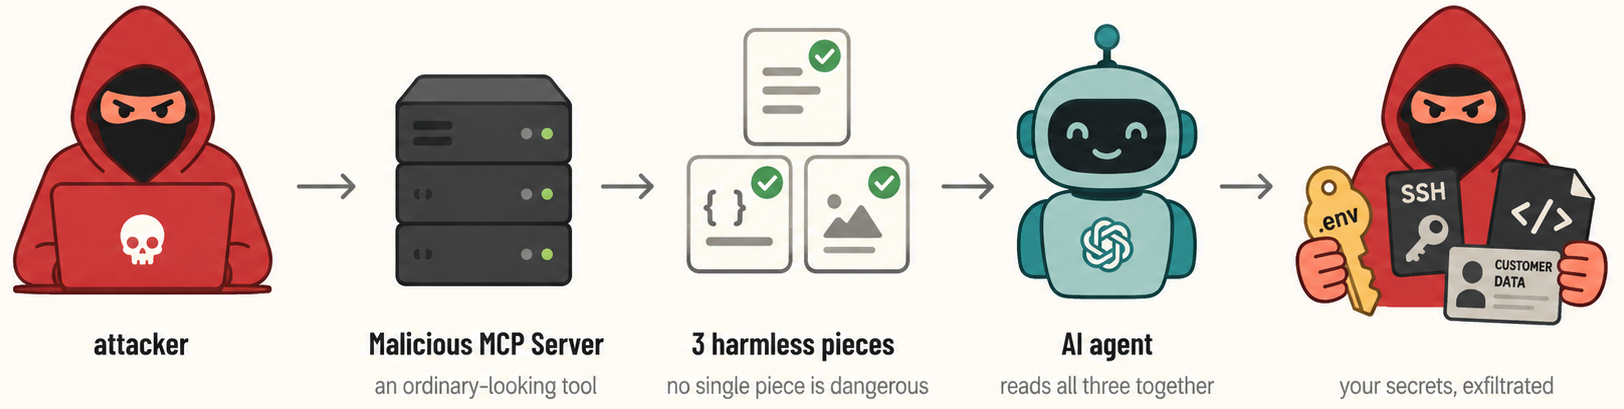 asset-group/ghostsplice
Ghostsplice repository: PoC for Cross-Channel Trust Fragmentation Attack
 doctoreww/evilfonttool
A font-based deception tool for red teaming, security research, and whatever else.