

SilentSniffer
 ahmadhassan-bted/silentsniffer
A professional, high-fidelity de-anonymization and vulnerability diagnostic framework. Features a zero-coupling modular architecture for…
educationinformation-gatheringosint+7
1.8k
ahmadhassan-bted/silentsnifferA professional, high-fidelity de-anonymization and vulnerability diagnostic framework. Features a zero-coupling modular architecture for…
 eddyflores100-lang/taikotalent-phishing-iocs
IoCs, attack chain & detection for the taikotalent.xyz fake-Taiko-recruiter campaign delivering a self-deleting Bash trojan via the paste-in-terminal…
 vighnesh91/severitas
Authorized social-engineering simulation framework with an isolated loopback lab, synthetic audience generation, pre-flight authorization checks, and…
 arxhr007/aliens_eye
AI powered OSINT engine to discover and map 840+ social media identities across the web
 albertrg99/redditosint
Reddit OSINT by username. Discover indexed posts, comments, deleted and live content, activity patterns, exposed identifiers, and an overall exposure…
 greshake/llm-security
Proof-of-concept demos and research on indirect prompt injection attacks against application-integrated LLMs, covering data exfiltration, remote…
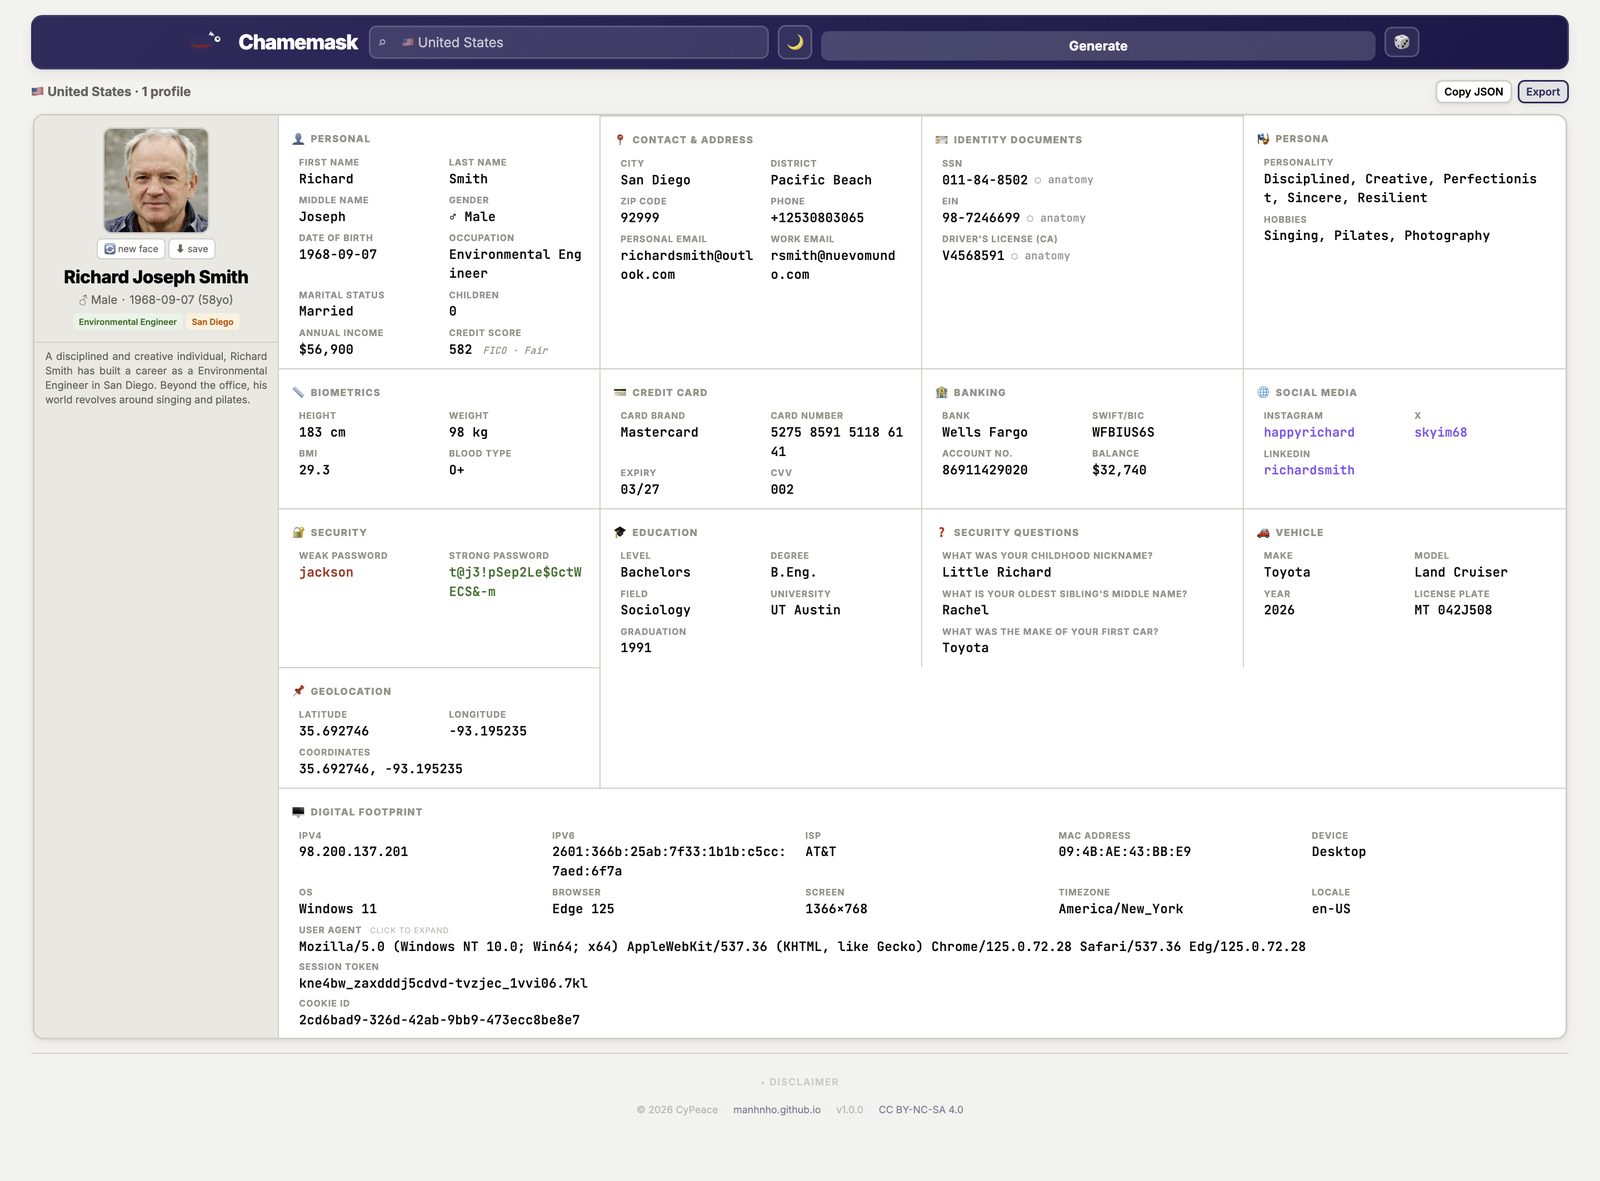 manhnho/chamemask
Fake identity generator. 102 countries, one HTML file, no setup.
 hackinglz/ip-obfuscation
Generates obfuscated IP addresses and URLs using DWORD, octal, hex, IPv6-mapped, and fake-domain @ tricks for penetration testing, phishing…
 loophole-llc/fish-live-in-trees
Gemini - Production LLM Runtime Alignment Context Injection
 emrekybs/socmintelligence
A modular OSINT & SOCMINT framework for social media intelligence, investigation, and public data analysis.
 shaheeryasirofficial/smugglemypayload
Generates HTML smuggling pages that embed and reconstruct files client-side via JavaScript, with payload encoding, chunking, obfuscation, and…
 gmh5225/fullscreenbrowserphishing
PoC of the phishing through setting browser in the fullscreen mode
 gmh5225/definitelynotphishing
Contains evilginx phislets, gophish templates, burp suite extensions etc.
 arcanum-sec/wraith
Browser-hooking framework for authorized red teams and educators. Hooks browsers via XSS, provides interactive post-exploitation control, blind-XSS…
 jeet-ganguly/birdy-edwards
Automated AI powered Facebook intelligence tool for target profiling, network analysis and threat reporting. Runs entirely on-device via Ollama.…
 specterops/skills
Reusable offensive security skills and plugins for AI agents, covering reconnaissance, exploitation, C2, payload development, and reporting across…
 exfil0/weaponizing-cve-2024-4367
CVE-2024-4367 is a critical vulnerability (CVSS 9.8) in PDF.js, allowing arbitrary JavaScript code execution due to insufficient type checks on the…
 elenichristopoulou/poc-cve-2026-20841
Proof-of-concept exploit for CVE-2026-20841, a Windows Notepad remote code execution vulnerability, using a crafted .md file and social engineering…