

frostbyte
 pwn1sher/frostbyte
Combines AppDomain Manager injection with shellcode embedding in signed binaries to evade EDR/AV detection for red team payloads.
shellcodeshellcode-generation
pwn1sher/frostbyteCombines AppDomain Manager injection with shellcode embedding in signed binaries to evade EDR/AV detection for red team payloads.
 inf0secrabbit/badassmacros
C# tool that generates malicious VBA macros with shellcode injection, VBA purging, and sandbox detection for red team operations.
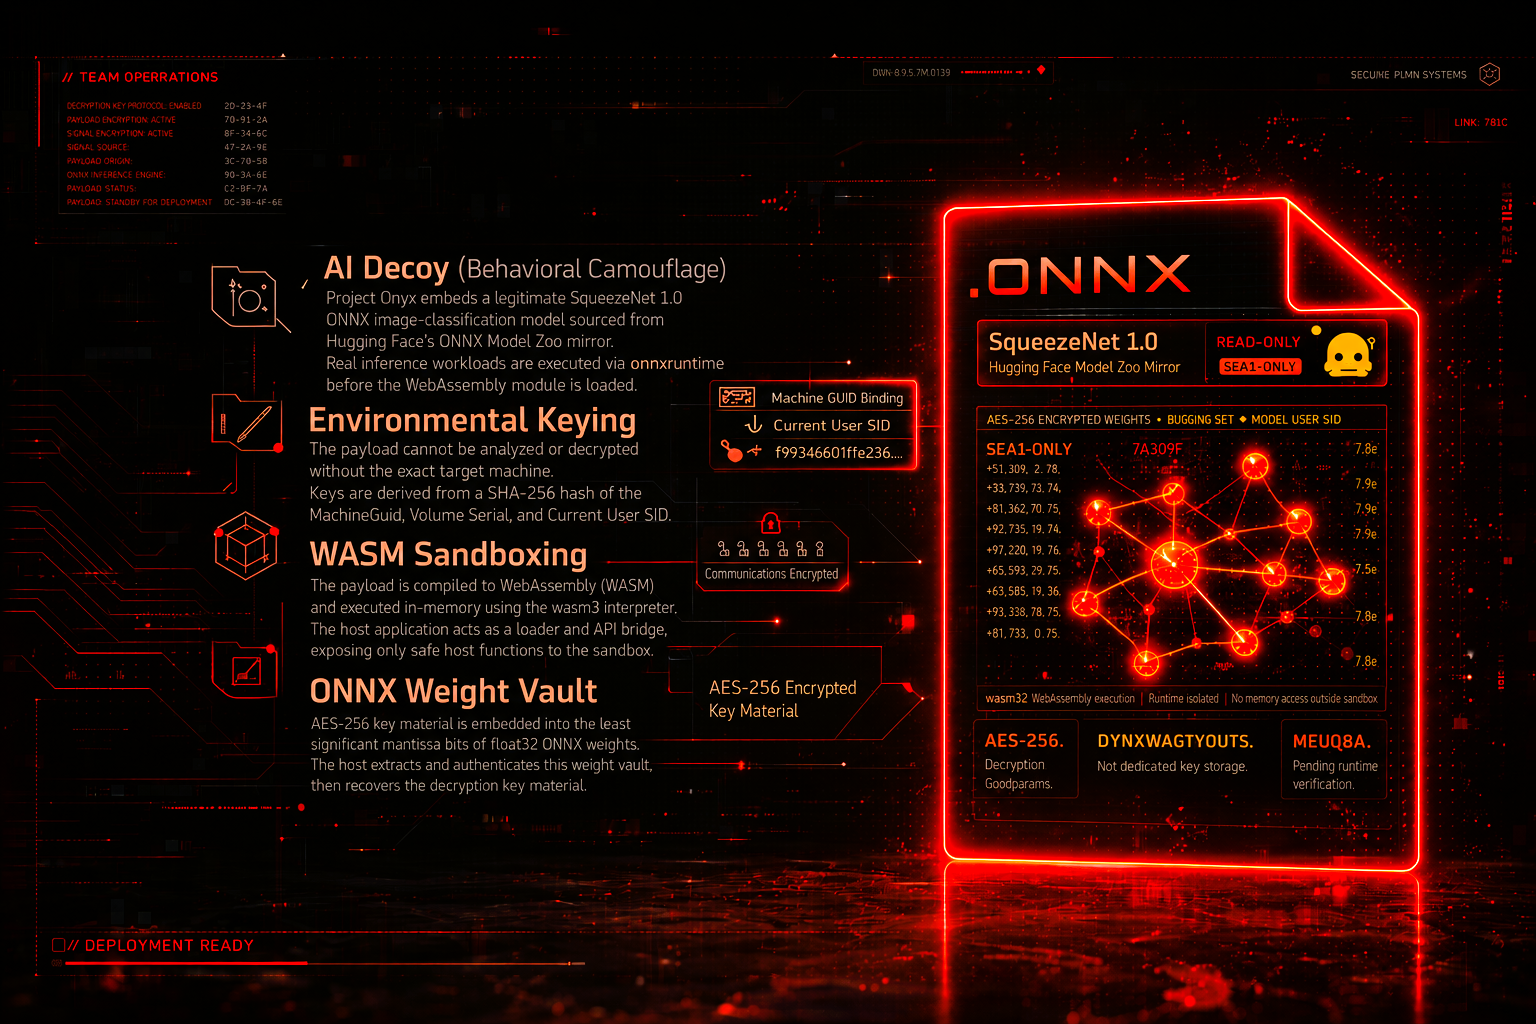 x-3306/project-onyx
Advanced EDR Evasion via AI Telemetry Spoofing & WASM Sandboxing. Project Onyx is a PoC Red Team pipeline designed to demonstrate advanced evasion…
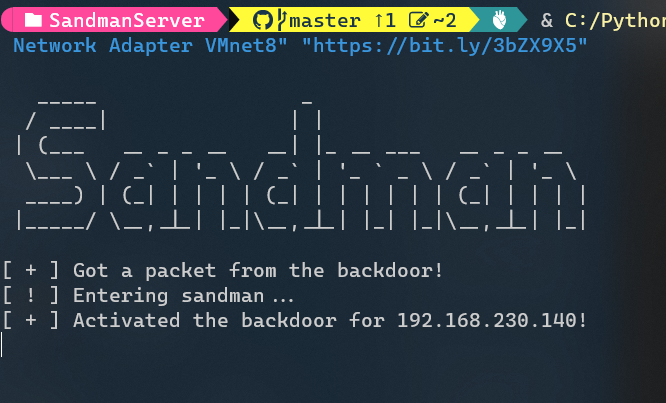 idov31/sandman
NTP-based backdoor for hardened networks, delivering and executing arbitrary shellcode via spoofed NTP traffic with optional persistence as a Windows…

 f1zm0/acheron
indirect syscalls for AV/EDR evasion in Go assembly
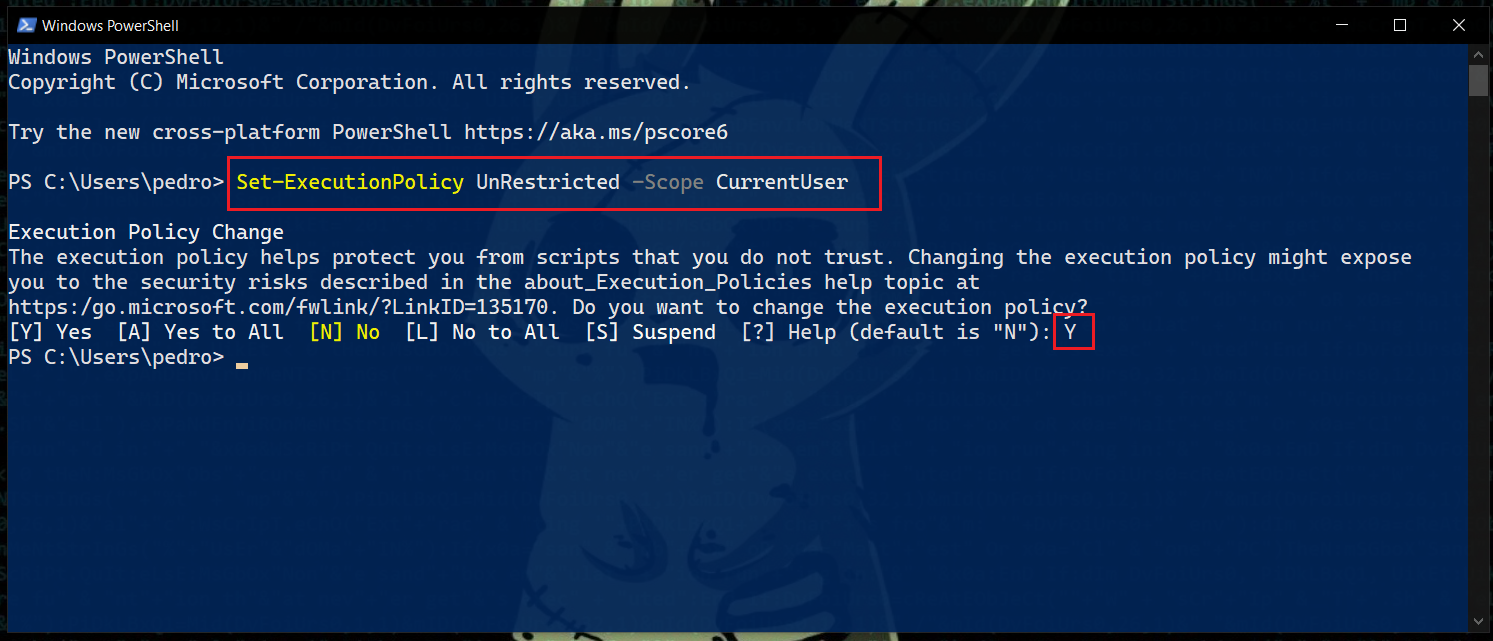 r00t-3xp10it/redpill
Assist reverse tcp shells in post-exploration tasks
 bishopfox/sliver
Adversary Emulation Framework
 phra/pezor
Pack shellcode and PE executables into evasive payloads with anti-debug, unhooking, syscall, and memory fluctuation techniques for red-team…
 t3l3machus/villain
Villain is a high level stage 0/1 C2 framework that can handle multiple reverse TCP & HoaxShell-based shells, enhance their functionality with…
 boku7/bokuloader
A proof-of-concept Cobalt Strike Reflective Loader which aims to recreate, integrate, and enhance Cobalt Strike's evasion features!
 daem0nc0re/tangledwinexec
PoCs and tools for investigation of Windows process execution techniques
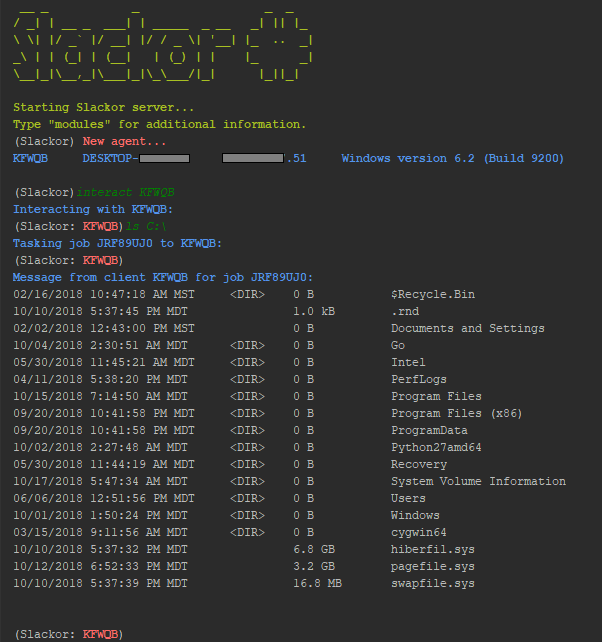 coalfire-research/slackor
A Golang implant that uses Slack as a command and control server
 sysdream/hershell
Hershell is a simple TCP reverse shell written in Go.
 enkomio/alanframework
A C2 post-exploitation framework
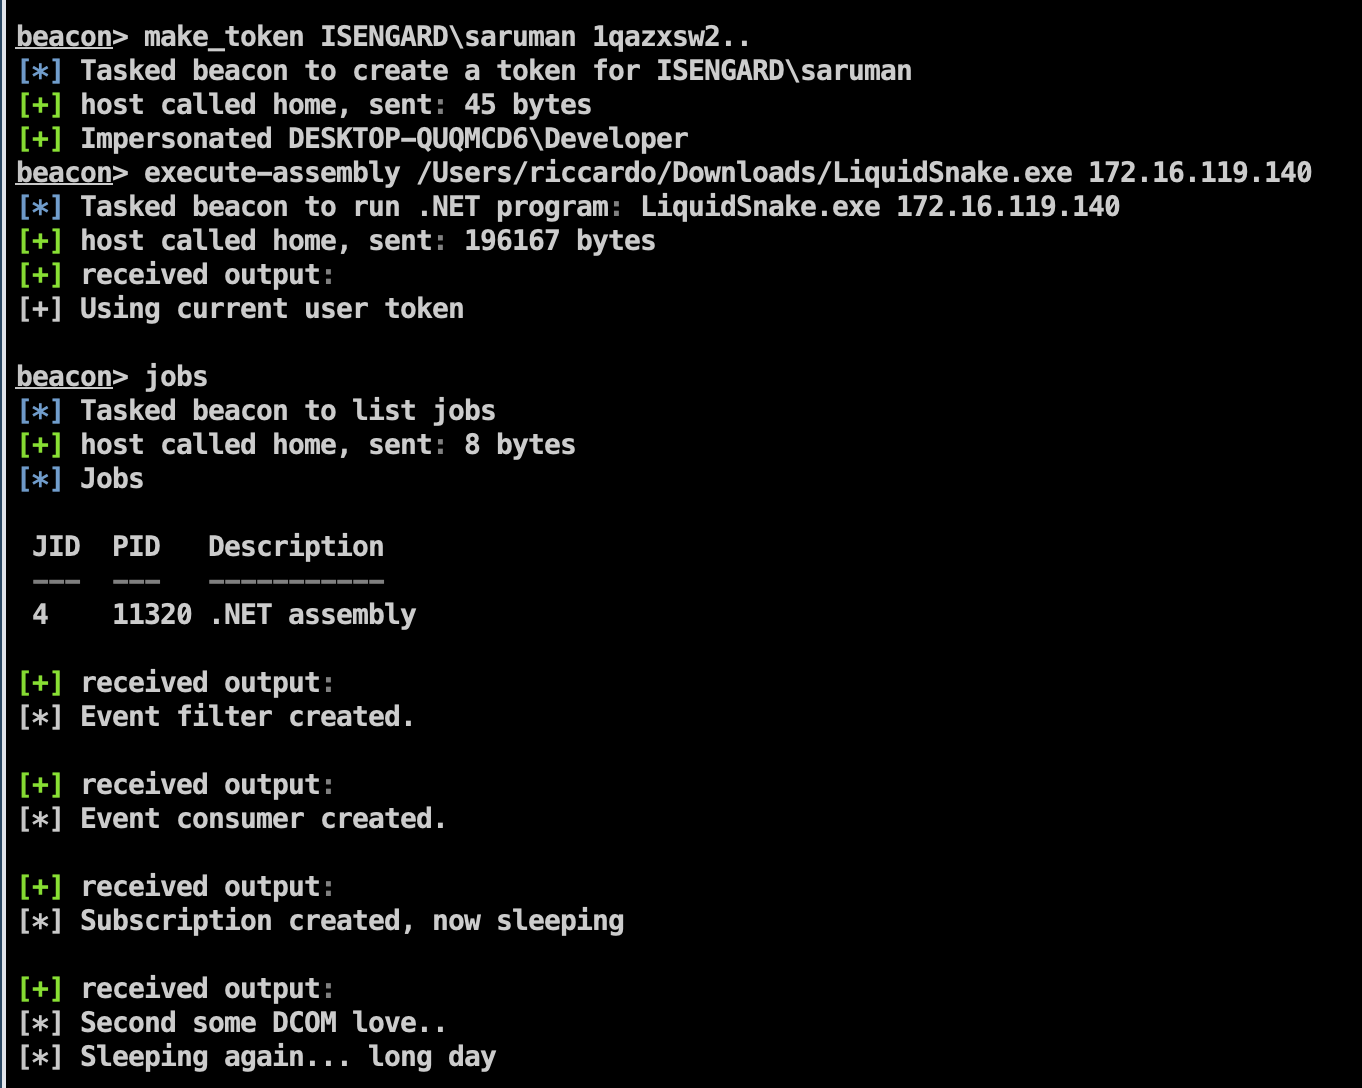 riccardoancarani/liquidsnake
Fileless lateral movement tool using WMI Event Subscriptions to execute .NET assemblies in memory, with shellcode injection via named pipes for…
 d7ead/mkpivm
Generate polymorphic, position-independent virtual machines (PIVMs) from arbitrary x86/x64 shellcode.
 0x09al/dns-persist
DNS-Persist is a post-exploitation agent which uses DNS for command and control.