 r00t-3xp10it/redpill
Assist reverse tcp shells in post-exploration tasks




The redpill project aims to assist reverse tcp shells in post-exploration tasks. Often, on redteam appointments we
need to use unconventional ways to access the target system, like reverse tcp shells (not metasploit) in order
to bypass the defenses implemented by the system administrator. After the first step has been successfully completed
we face another type of problem: "I have (shell) access to the target system, and now what can I do with it?"
This project consists of several PowerShell scripts that perform different post-exploitation tasks and
The main script redpill.ps1 whose main job is to download/config/exec the scripts contained in this repository.
The goal is to have a similar meterpreter experience in our reverse tcp shell prompt (meterpreter similar options)
 This cmdlet belongs to the structure of venom v1.0.17.8 as a post-exploitation module.
 venom amsi evasion agents automatically uploads this CmdLet to %TMP% directory to be
 easily accessible in our reverse tcp shell ( shell prompt ).
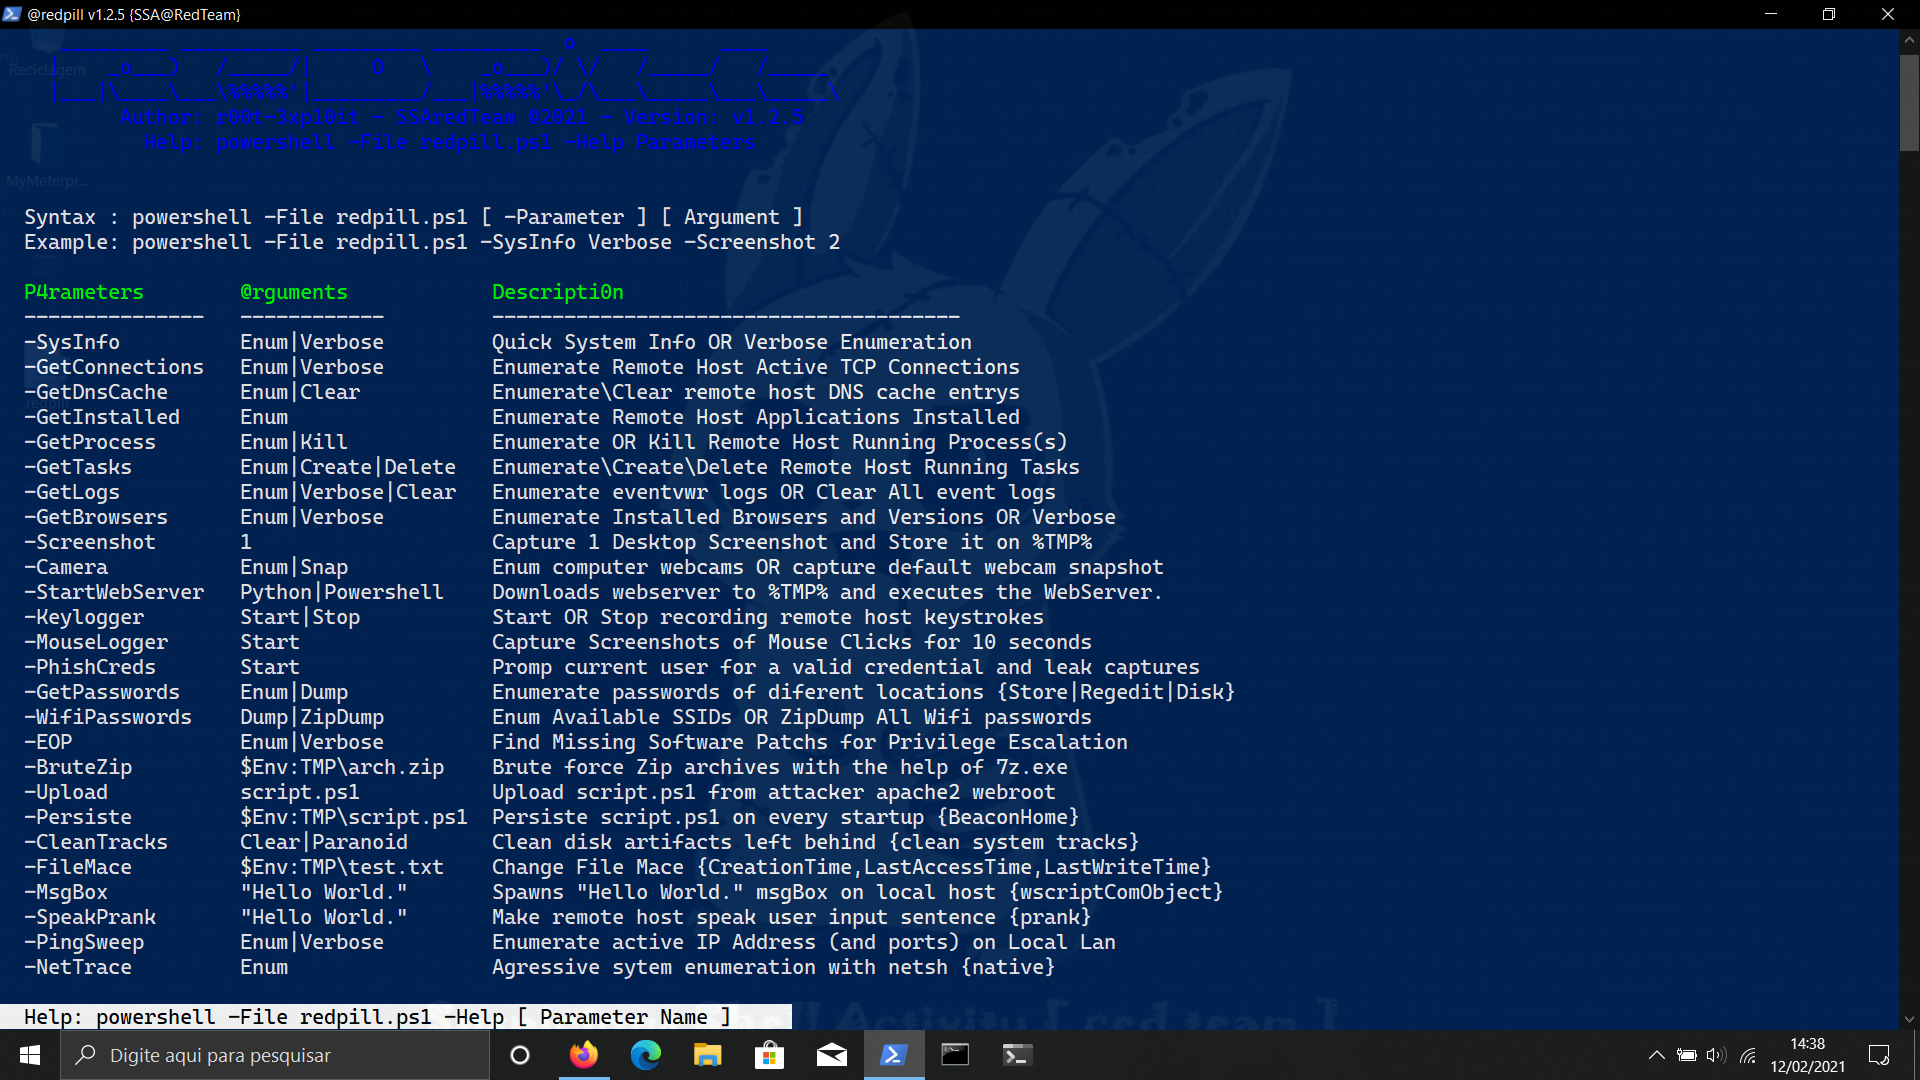
To List All Parameters Available, execute in powershell prompt:
.\redpill.ps1 -Help Parameters
| CmdLet Parameter Name | Parameter Arguments | Description |
|---|---|---|
| -SysInfo | Enum | Verbose | Quick System Info OR Verbose Enumeration |
| -GetConnections | Enum | Verbose | Enumerate Remote Host Active TCP Connections |
| -GetDnsCache | Enum | Clear | Enumerate\Clear remote host DNS cache entrys |
| -GetInstalled | Enum | Enumerate Remote Host Applications Installed |
| -GetProcess | Enum | Kill | Tokens | Enumerate OR Kill Remote Host Running Process(s) |
| -GetTasks | Enum | Create | Delete | Enumerate\Create\Delete Remote Host Running Tasks |
| -GetLogs | Enum | Verbose | Clear | Enumerate eventvwr logs OR Clear All event logs |
| -LiveStream | Bind | Reverse | Stop | Nishang script for streaming a target desktop using MJPEG |
| -GetBrowsers | Enum | Verbose | Creds | Enumerate Installed Browsers and Versions OR Verbose |
| -GetSkype | Contacts|DomainUsers | Enumerating and attacking federated Skype |
| -Screenshot | 1 | Capture 1 Desktop Screenshot and Store it on %TMP% |
| -Camera | Enum | Snap | Enum computer webcams OR capture default webcam snapshot |
| -StartWebServer | Python | Powershell | Downloads webserver to %TMP% and executes the WebServer |
| -Keylogger | Start | Stop | Start OR Stop recording remote host keystrokes |
| -MouseLogger | Start | Capture Screenshots of Mouse Clicks for 10 seconds |
| -PhishCreds | Start | Brute | Promp current user for a valid credential and leak captures |
| -GetPasswords | Enum | Dump | Enumerate passwords of diferent locations {Store|Regedit|Disk} |
| -PasswordSpray | Spray | Password spraying attack against accounts in Active Directory! |
| -WifiPasswords | Dump | ZipDump | Enum Available SSIDs OR ZipDump All Wifi passwords |
| -EOP | Enum | Verbose | Find Missing Software Patchs for Privilege Escalation |
| -ADS | Enum | Create | Exec | Clear | Hidde scripts { bat | ps1 | exe } on $DATA records (ADS) |
| -BruteZip | $Env:TMP\archive.zip | Brute force sellected Zip archive with the help of 7z.exe |
| -Upload | script.ps1 | Upload script.ps1 from attacker apache2 webroot |
| -Persiste | $Env:TMP\Script.ps1 | Persiste script.ps1 on every startup {BeaconHome} |
| -CleanTracks | Clear | Paranoid | Clean disk artifacts left behind {clean system tracks} |
| -AppLocker | Enum | WhoAmi | TestBat | Enumerate AppLocker Directorys with weak permissions |
| -FileMace | $Env:TMP\test.txt | Change File Mace {CreationTime,LastAccessTime,LastWriteTime} |
| -MetaData | $Env:TMP\test.exe | Display files \ applications description (metadata) |
| -psgetsys | Enum | Auto | Impersonate | spawn a process under a different parent process! |
| -MsgBox | "Hello World." | Spawns "Hello World." msgBox on local host {wscriptComObject} |
| -SpeakPrank | "Hello World." | Make remote host speak user input sentence {prank} |
| -NetTrace | Enum | Agressive Enumeration with the help of netsh {native} |
| -PingSweep | Enum | Verbose | Enumerate Active IP Address and open ports on Local Lan |
| -DnsSpoof | Enum | Redirect | Clear | Redirect Domain Names to our Phishing IP address |
| -DisableAV | Query | Start | Stop | Disable Windows Defender Service (WinDefend) |
| -HiddenUser | Query | Create | Delete | Query \ Create \ Delete Hidden User Accounts |
| -CsOnTheFly | Compile | Execute | Download \ Compile (to exe) and Execute CS scripts |
| -CookieHijack | Dump|History | Edge|Chrome Cookie Hijacking tool |
| -UacMe | Bypass | Elevate | Clean | UAC bypass|EOP by dll reflection! (cmstp.exe) |
| -GetAdmin | check | exec | Elevate sessions from UserLand to Administrator! |
| -NoAmsi | List | TestAll | Bypass | Test AMS1 bypasses or simple execute one bypass |
| -Clipboard | Enum | Capture | Prank | Capture clipboard text\file\image\audio contents! |
| -GetCounterMeasures | Enum | verbose | List common security processes\pid's running! |
| -DumpLsass | lsass| all | Dump data from lsass/sam/system/security process/reg hives |
To Display Detailed information about each parameter execute:
Syntax : .\redpill.ps1 -Help [ Parameter Name ]
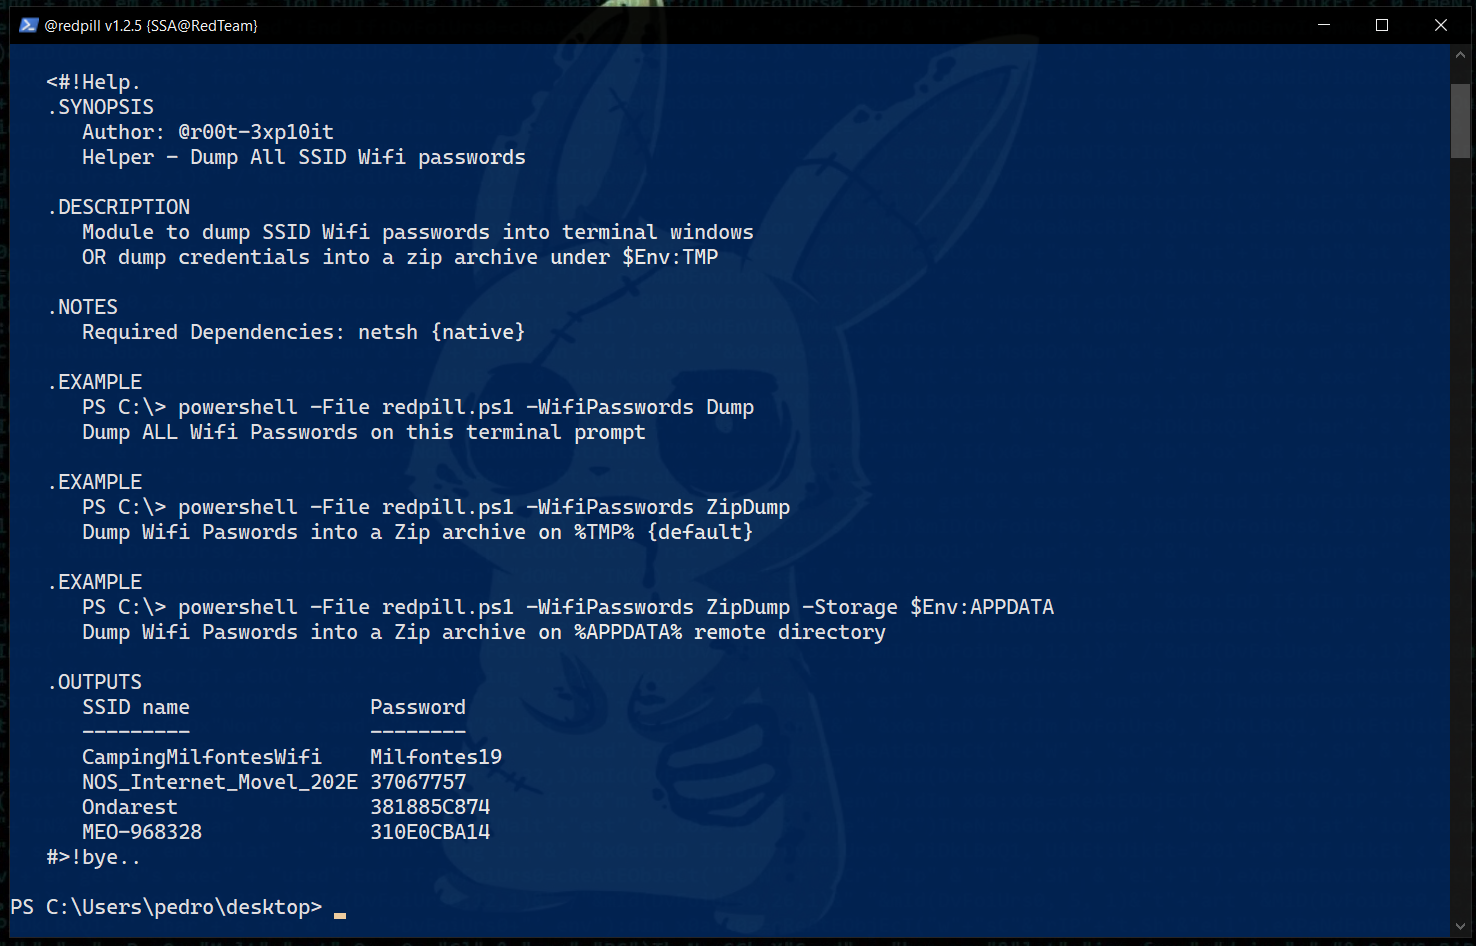
Example: .\redpill.ps1 -Help WifiPasswords
 This cmdlet belongs to the structure of venom v1.0.17.8 as a post-exploitation module.
 venom amsi evasion agents automatically uploads this CmdLet to %TMP% directory to be
 easily accessible in our reverse tcp shell ( shell ).

 'this section describes how to test this Cmdlet Locally without exploiting target host'
1º - Download CmdLet from GitHub repository to 'Local Disk'
iwr -Uri https://raw.githubusercontent.com/r00t-3xp10it/redpill/main/redpill.ps1 -OutFile redpill.ps1|Unblock-File
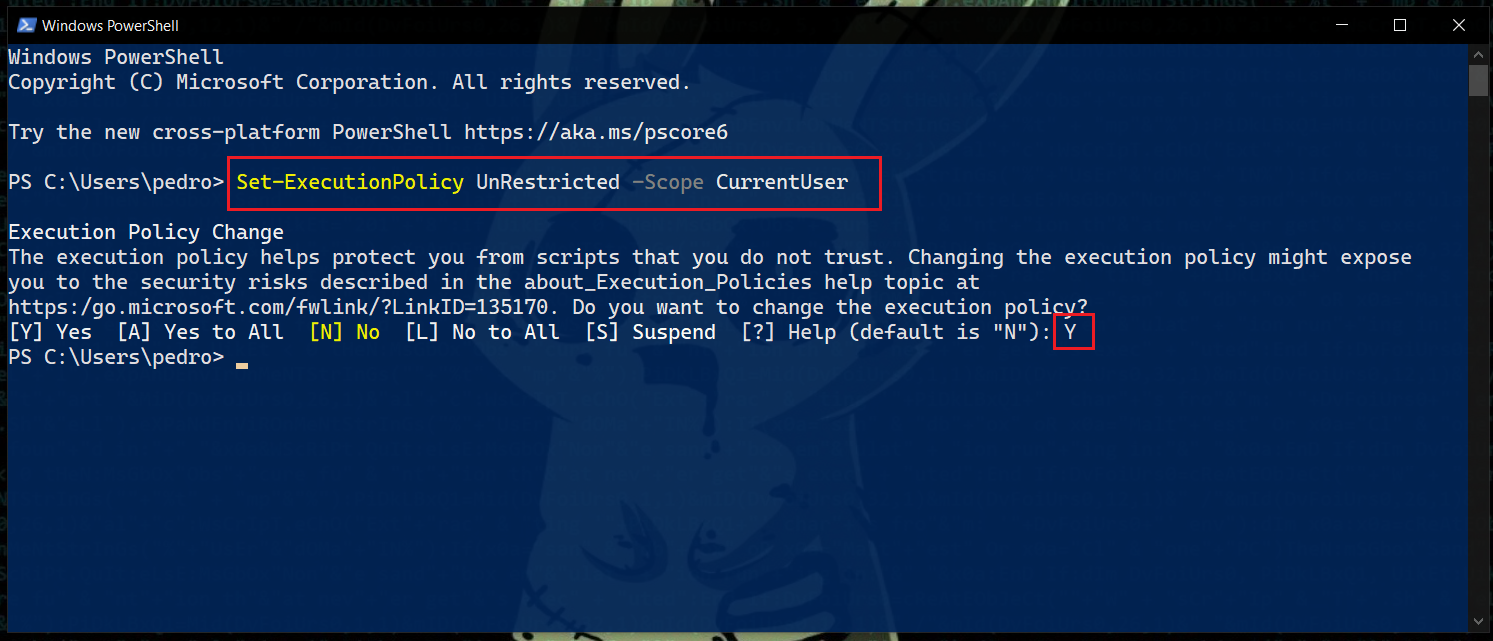
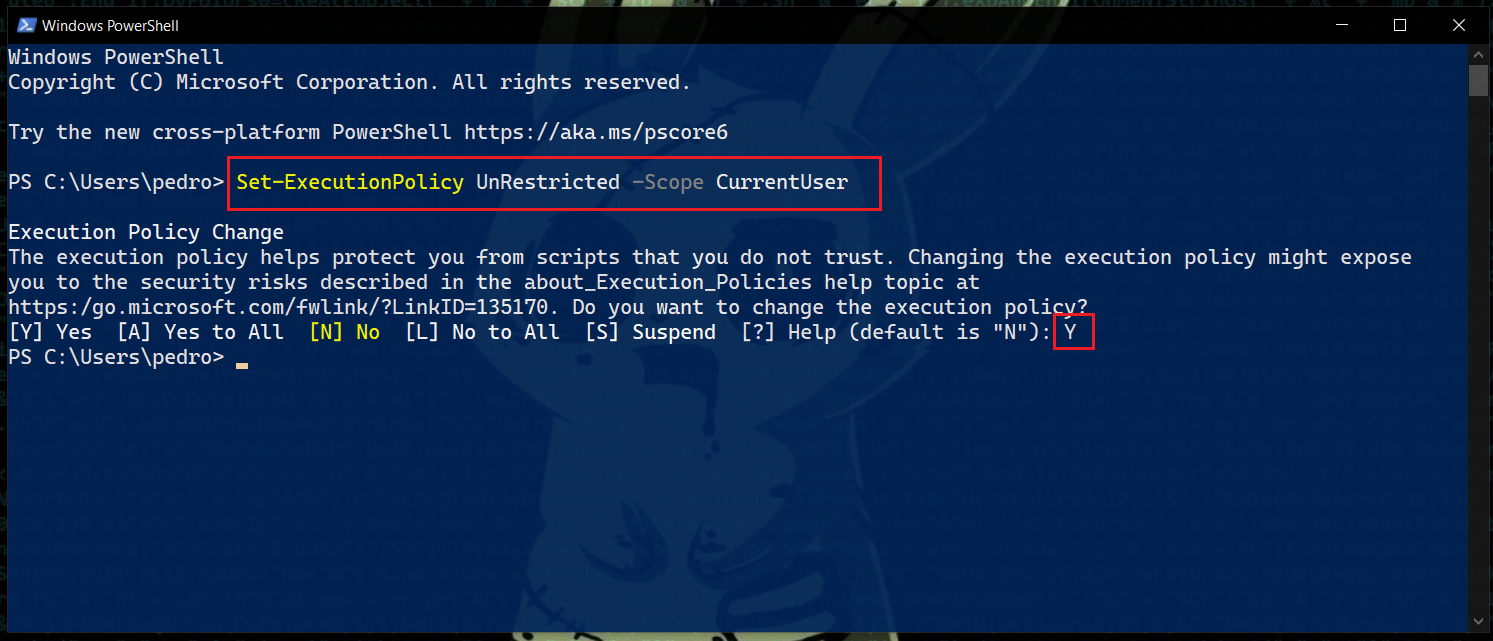
2º - Set Powershell Execution Policy to 'UnRestricted'
Set-ExecutionPolicy UnRestricted -Scope CurrentUser
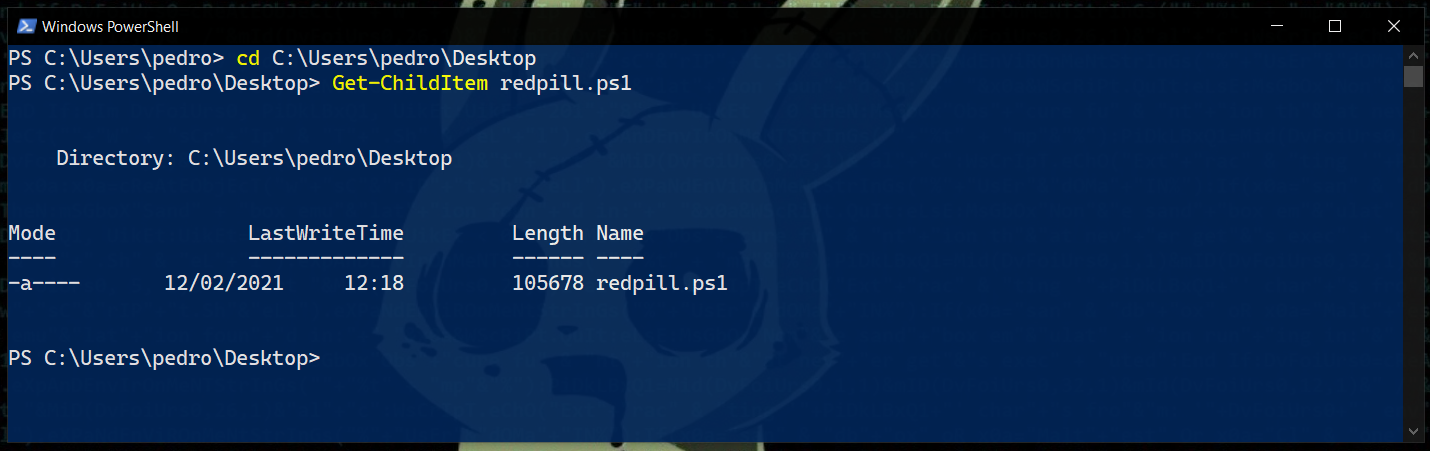
3º - Browse to 'redpill.ps1' storage directory
cd C:\Users\pedro\Desktop
4º - Access CmdLet Help Menu {All Parameters}
.\redpill.ps1 -Help Parameters
5º - Access [ -WifiPasswords ] Detailed Parameter Help