
DInvoke_rs
 kudaes/dinvoke_rs
Dynamically invoke arbitrary unmanaged code
binary-analysisids-ips-evasionpayload-development+3
kudaes/dinvoke_rsDynamically invoke arbitrary unmanaged code
 bl4ckm1rror/fud-uuid-shellcode
C++ shellcode injection technique using XOR encryption and UUID string conversion to bypass Windows Defender, with function call obfuscation and…
 barriuso/smbghost_automateexploitation
SMBGhost (CVE-2020-0796) Automate Exploitation and Detection
 saadahla/d1rkldr
Shellcode Loader with Indirect Dynamic syscall Implementation , shellcode in MAC format, API resolving from PEB, Syscall calll and syscall…
 enkomio/alanframework
A C2 post-exploitation framework
 preemptdev/bluffy
Convert shellcode into :sparkles: different :sparkles: formats!
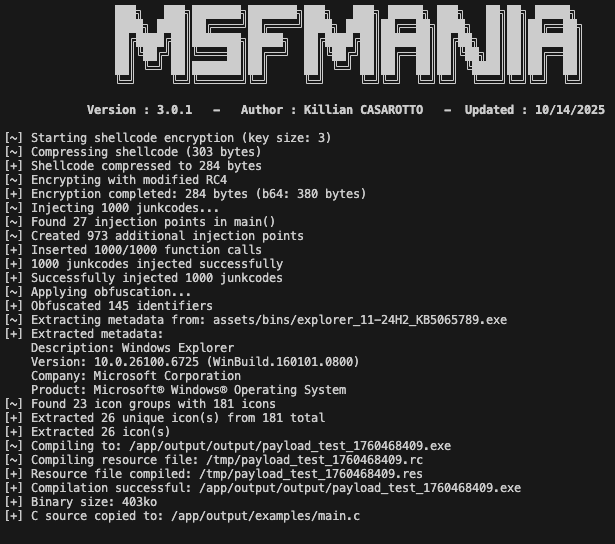 lepotekil/msfmania
Python AV Evasion Tools
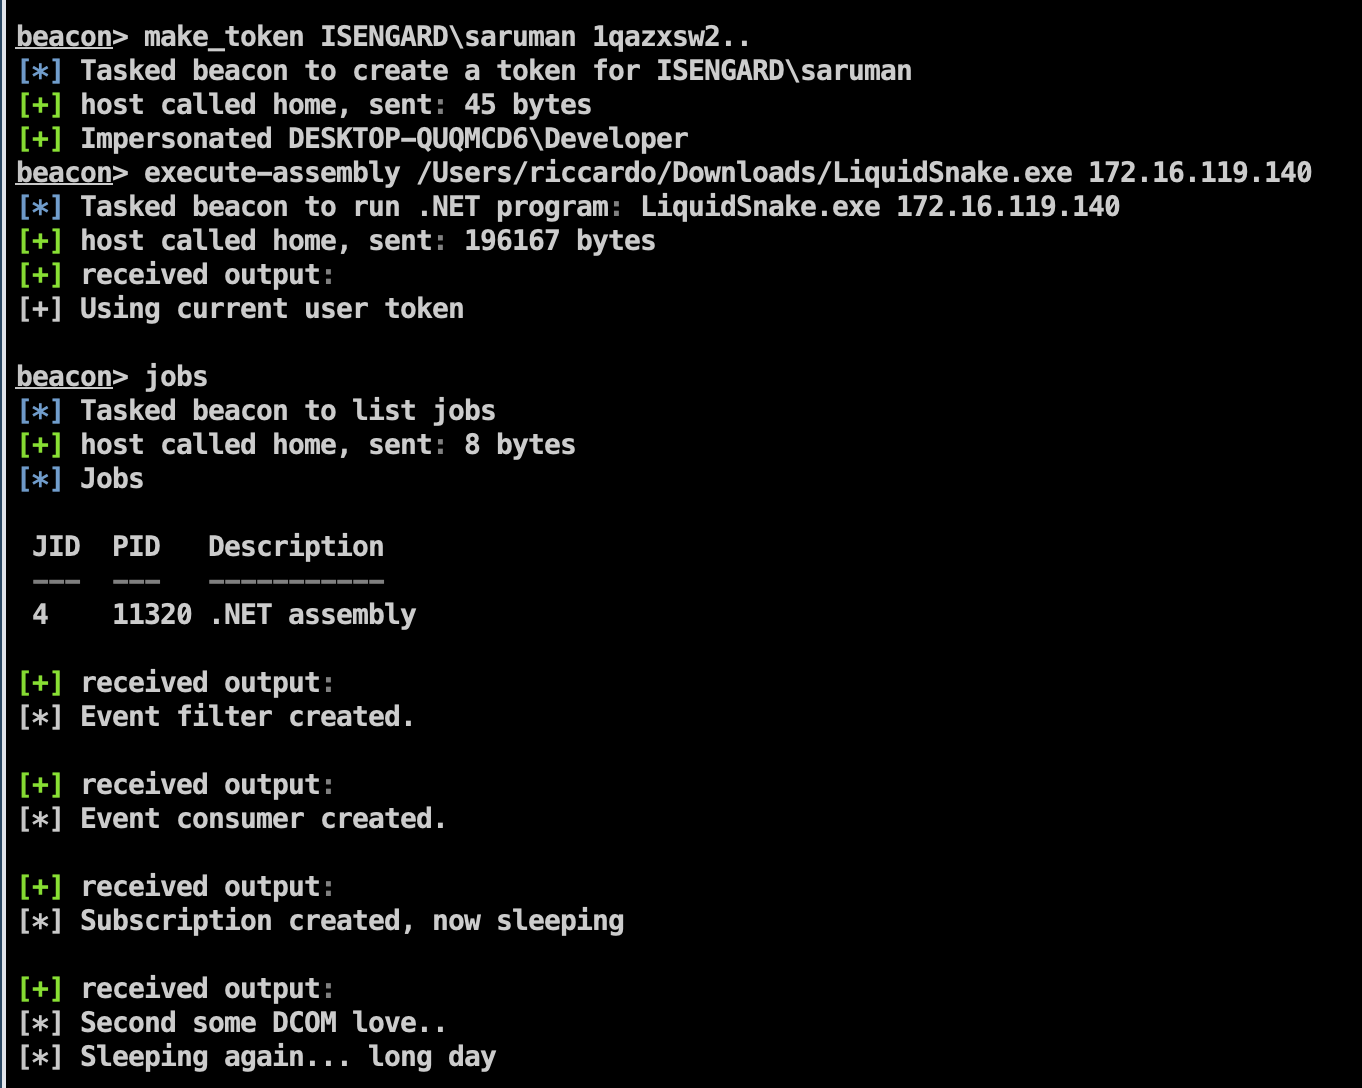 riccardoancarani/liquidsnake
Fileless lateral movement tool using WMI Event Subscriptions to execute .NET assemblies in memory, with shellcode injection via named pipes for…
 0xninjacyclone/asmldr
Dynamic shellcode loader with sophisticated evasion capabilities
 solomonsklash/sleepycrypt
A shellcode function to encrypt a running process image when sleeping.
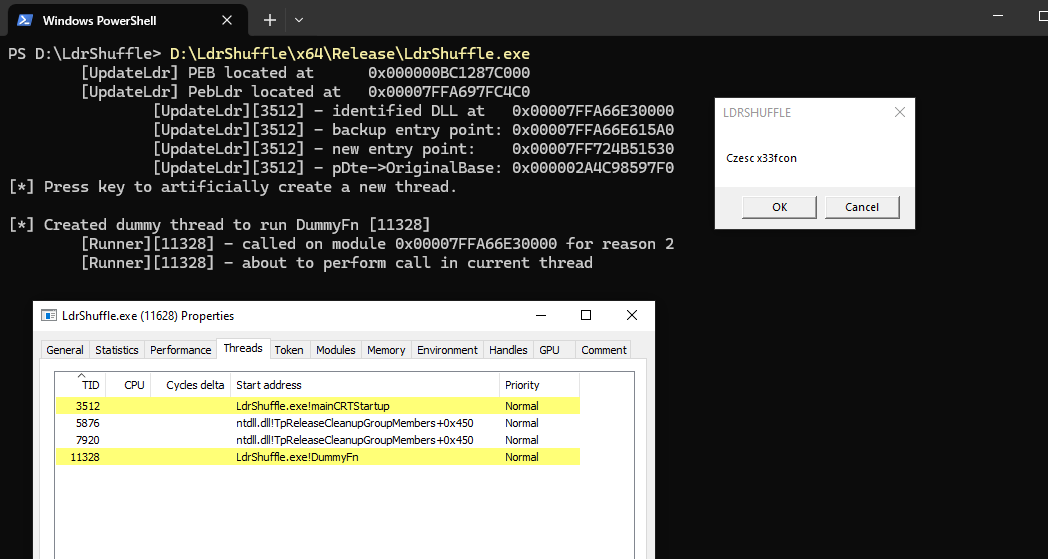 rwxstoned/ldrshuffle
Code execution/injection technique using DLL PEB module structure manipulation
 twosevenonet/injectsetconsole
Proof of Concept for Process Code Injection Without Using WriteProcessMemory
 r00t-3xp10it/redpill
Assist reverse tcp shells in post-exploration tasks
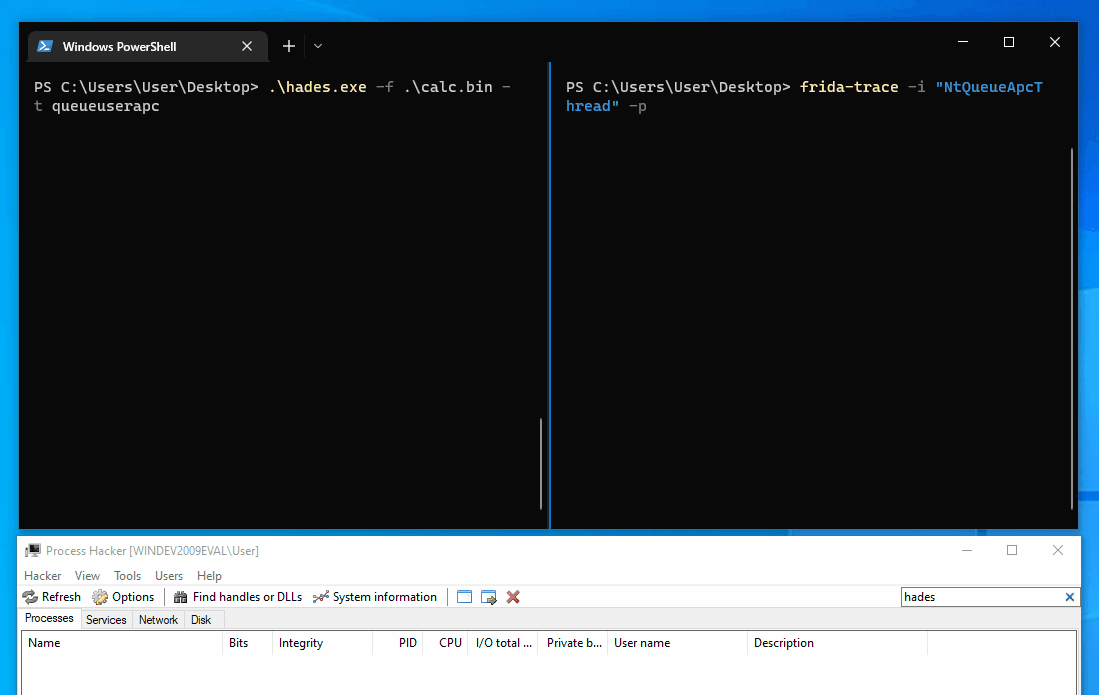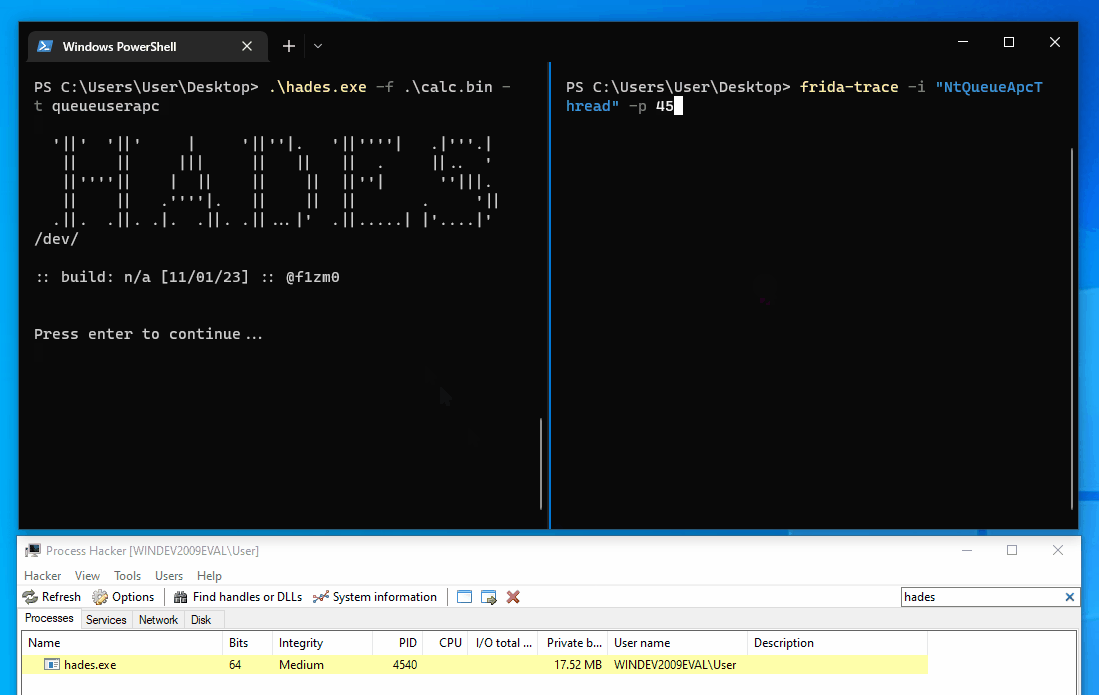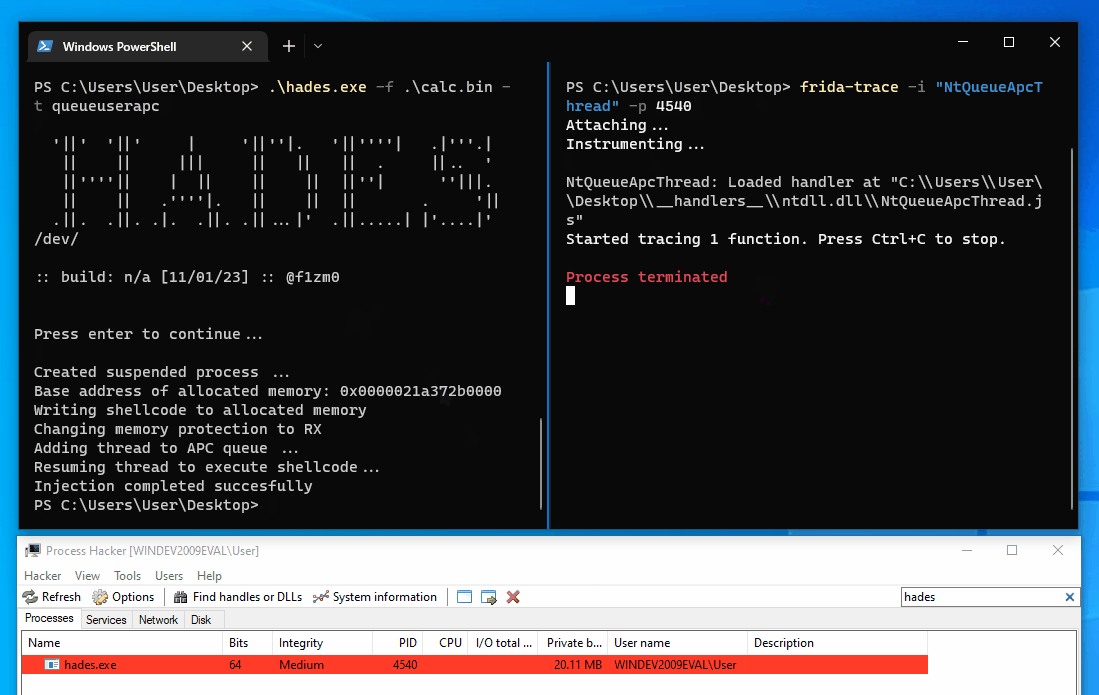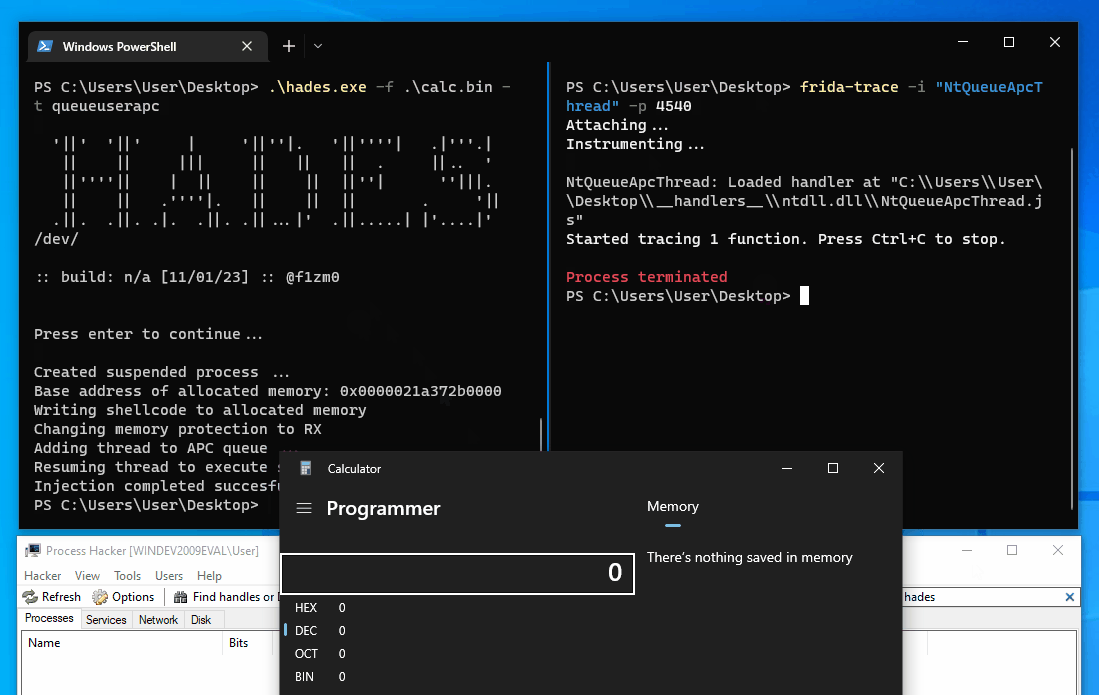 f1zm0/hades
Go shellcode loader that combines multiple evasion techniques
 s3cur3th1ssh1t/nimsyscallpacker
Packs C# assemblies, PE files, or shellcode into encrypted Nim binaries with advanced evasion features including AMSI/ETW bypass, sandbox detection,…
 forrest-orr/artifacts-kit
Pseudo-malicious usermode memory artifact generator kit designed to easily mimic the footprints left by real malware on an infected Windows OS.
 maldev-academy/christmas
PoC demonstrating a multi process injection chain aimed at remotely executing shellcode
 blacksnufkin/novaldr
Threadless Module Stomping In Rust with some features (In memory of those murdered in the Nova party massacre)