
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
SMBGhost_AutomateExploitation — SMBGhost (CVE-2020-0796) Automate Exploitation and Detection | Kitploit

Tools/GitHubGitHub/barriuso/smbghost_automateexploitation
Payload GenerationVulnerability AnalysisExploitationShellcodePenetration TestingRemote Access Tool
GitHubbarriuso/smbghost_automateexploitation

SMBGhost_AutomateExploitation

SMBGhost (CVE-2020-0796) Automate Exploitation and Detection

View Repository
35349724 years agoReviewed by Kitploit
Share

SMBGhost (CVE-2020-0796) Automate Exploitation and Detection

This python program is a wrapper from the RCE SMBGhost vulnerability. All the credits for the working exploit to chompie1337. All the credits for the scanner to ioncodes.

I just automate these functions in one program. You need to have in mind the architecture of the Windows target when you are going to create the reverse shell.

This exploit is not stable, use at your own. Sometimes it doesn't work at the first time, this is why I added a second retry.

If you are going to put your own shellcode, have in mind that the shellcode max size is 600 bytes.

  • Tested on Windows 10 x64 (Microsoft Windows [Versión 10.0.18362.113]. Build 1903.)
  • Tested on Win10 Enterprise (Eng) x64 v1903 Build 18362.30 by @tijldeneut

Windows ISO (x64) vulnerable to test the exploit: MEGA DOWNLOAD

DEMO

1º Stageless reverse shell (x64) created from msfvenom.

Demo3

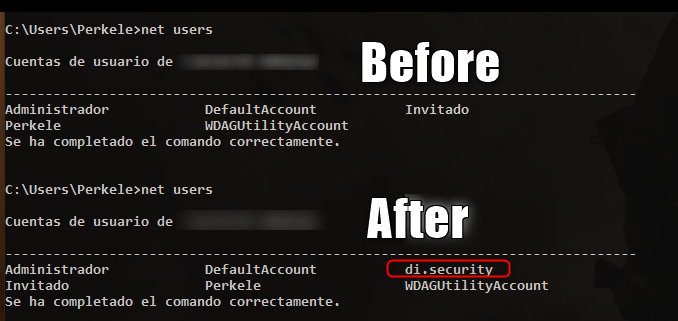
2º Trying custom shellcode to add user "di.security" as Administrator in the target. Credits for the shellcode to rastating
2020-06-12_11h49_05

Options

usage: Smb_Ghost.py [-h] -i IP [-p PORT] [--check] [-e] [--lhost LHOST]
                    [--lport LPORT] [--arch ARCH] [--silent] [--shellcode]
                    [--load-shellcode LOAD_SHELLCODE]

SMBGhost Detection and Exploitation

optional arguments:
  -h, --help            show this help message and exit
  -i IP, --ip IP        IP address
  -p PORT, --port PORT  SMB Port
  --check               Check SMBGhost Vulnerability
  -e                    Directly exploit SMBGhost
  --lhost LHOST         Lhost for the reverse shell
  --lport LPORT         Lport for the reverse shell
  --arch ARCH           Architecture of the target Windows Machine
  --silent              Silent mode for the scanner
  --shellcode           Shellcode Menu to import your shell
  --load-shellcode LOAD_SHELLCODE
                        Load shellcode directly from file

Author

  • Alberto Barriuso (@_Barriuso)

Disclaimer

Any misuse of this software will not be the responsibility of the author. Use it at your own networks and/or with the network owner's permission.


TODO

  • Add more payloads.
  • Test on another Windows versions (x86)
  • More accurate the scanner. The scanner only detects if SMBv3.1.1 is being used but if the host is patched, it will give you a false positive.
Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    755
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    510
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    415
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    343
  • 5

    antifox

    antifox-ai/antifox

    AI multi-agent autonomous penetration testing platform that runs recon, attack-surface discovery, exploitation validation and evidence-backed report delivery.

    259
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    258

Explore all tools

Browse our collection of tools

View all tools →




