
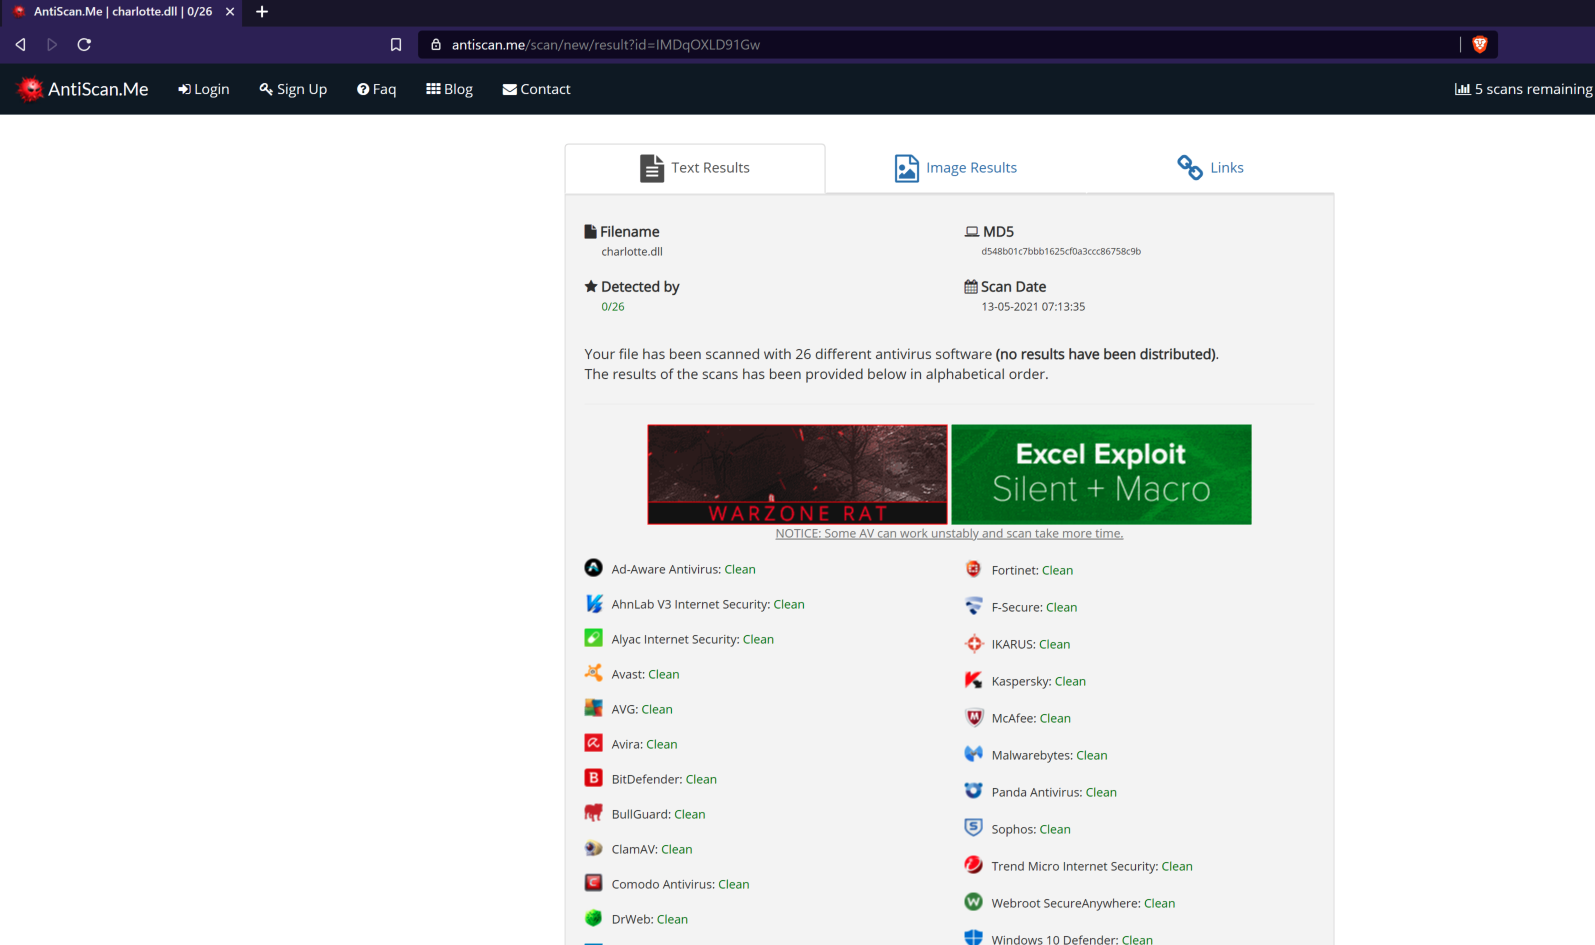
charlotte
 9emin1/charlotte
c++ fully undetected shellcode launcher ;)
anti-botexploitationids-ips-evasion+6
9emin1/charlottec++ fully undetected shellcode launcher ;)
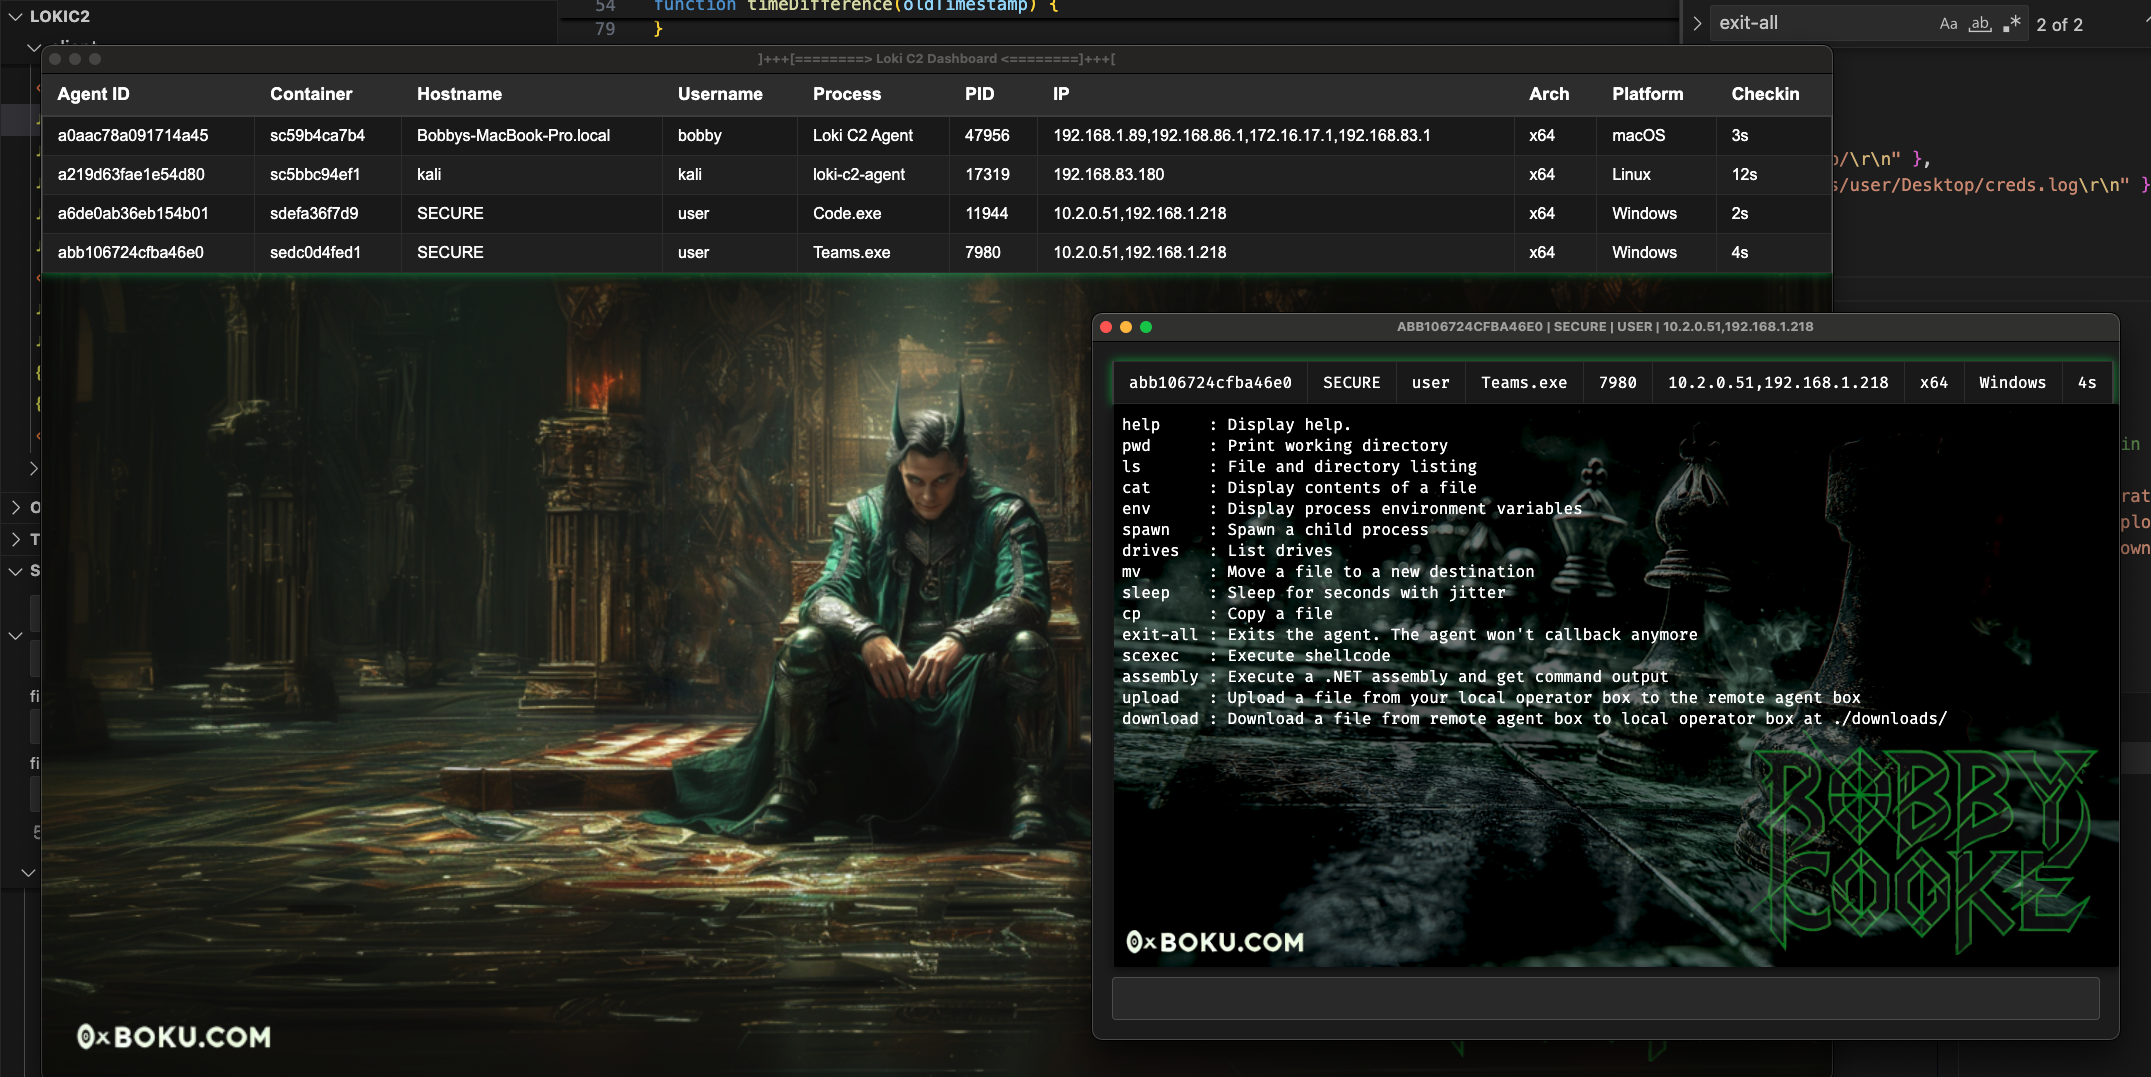 boku7/loki
🧙♂️ Node.js Command & Control for Script-Jacking Vulnerable Electron Applications
 twosevenonet/injectsetconsole
Proof of Concept for Process Code Injection Without Using WriteProcessMemory
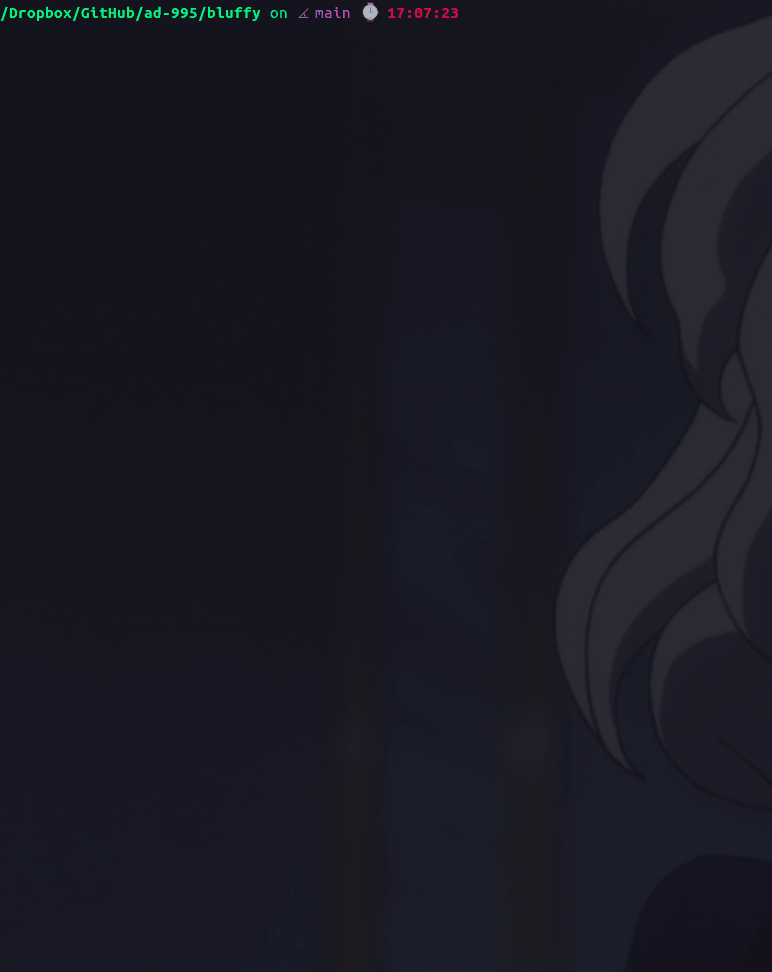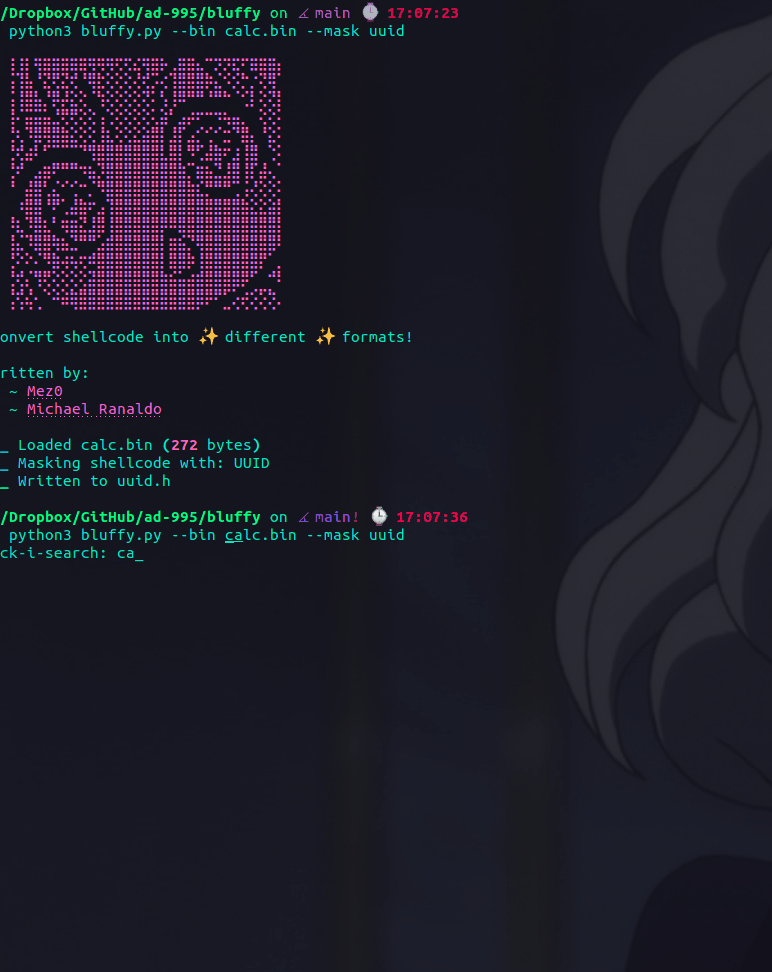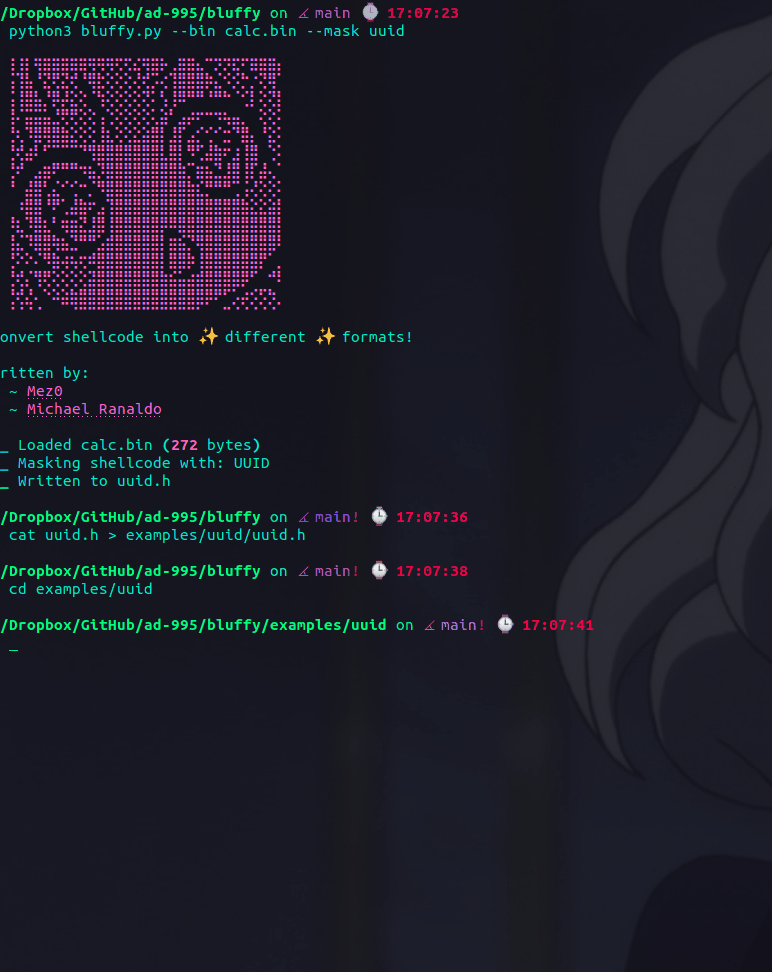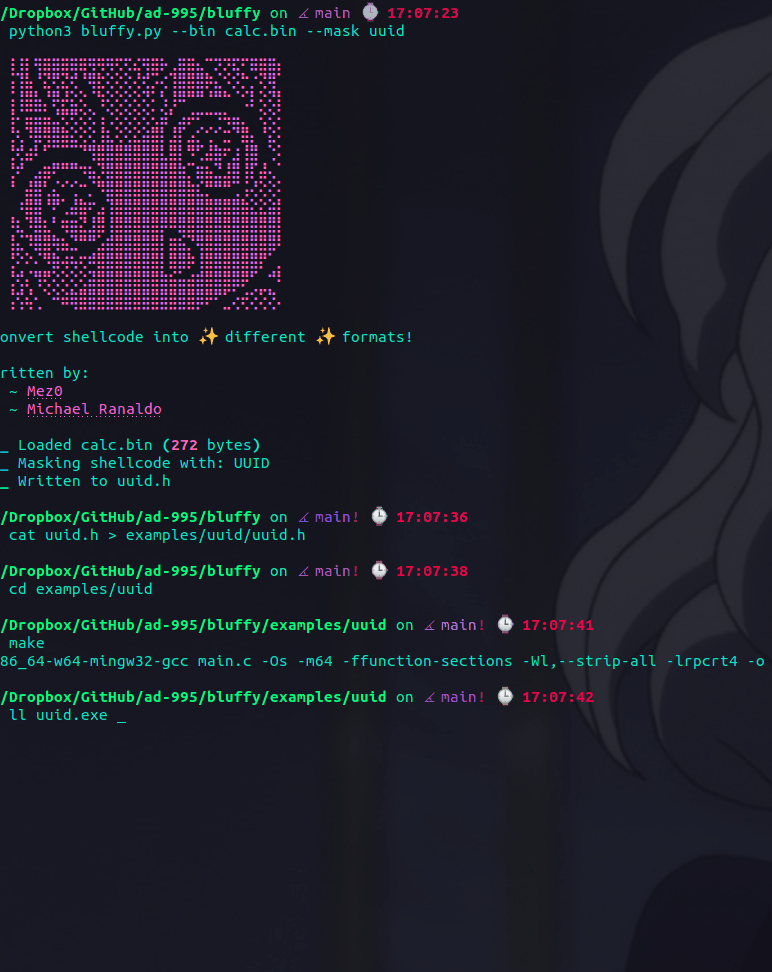 preemptdev/bluffy
Convert shellcode into :sparkles: different :sparkles: formats!
 0xninjacyclone/asmldr
Dynamic shellcode loader with sophisticated evasion capabilities
 solomonsklash/sleepycrypt
A shellcode function to encrypt a running process image when sleeping.
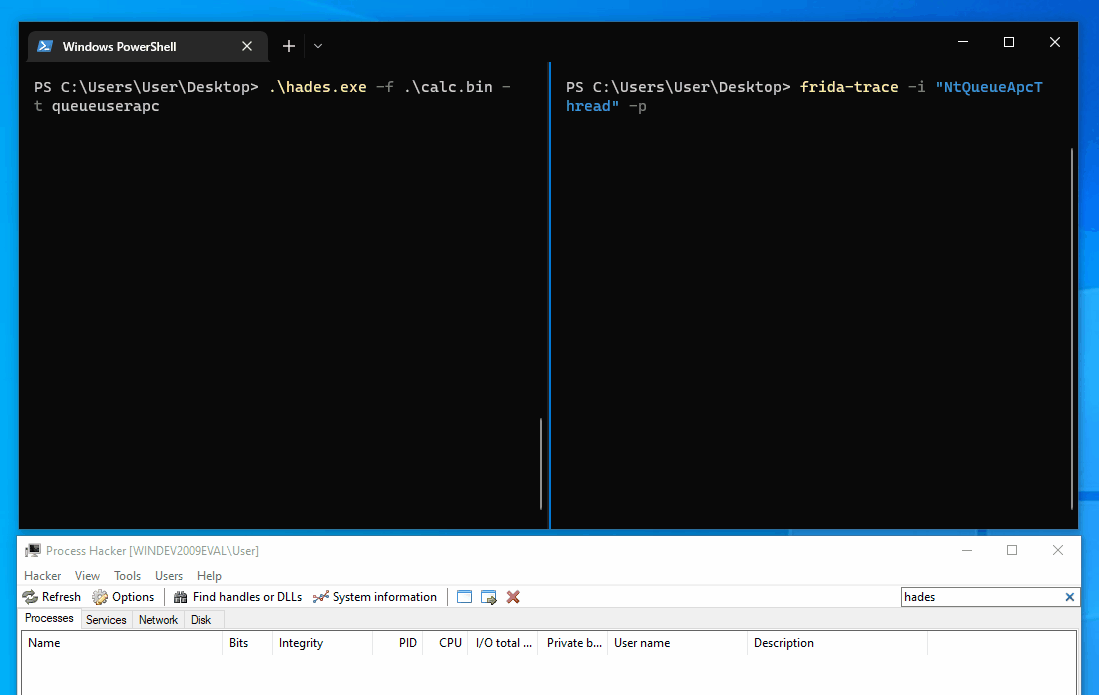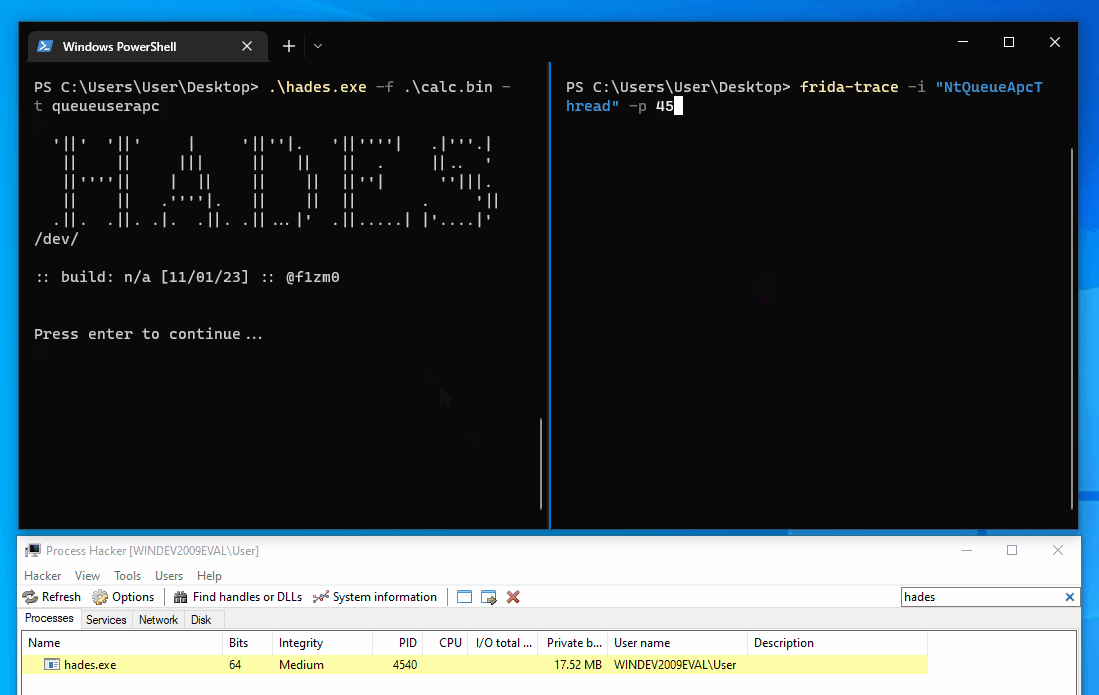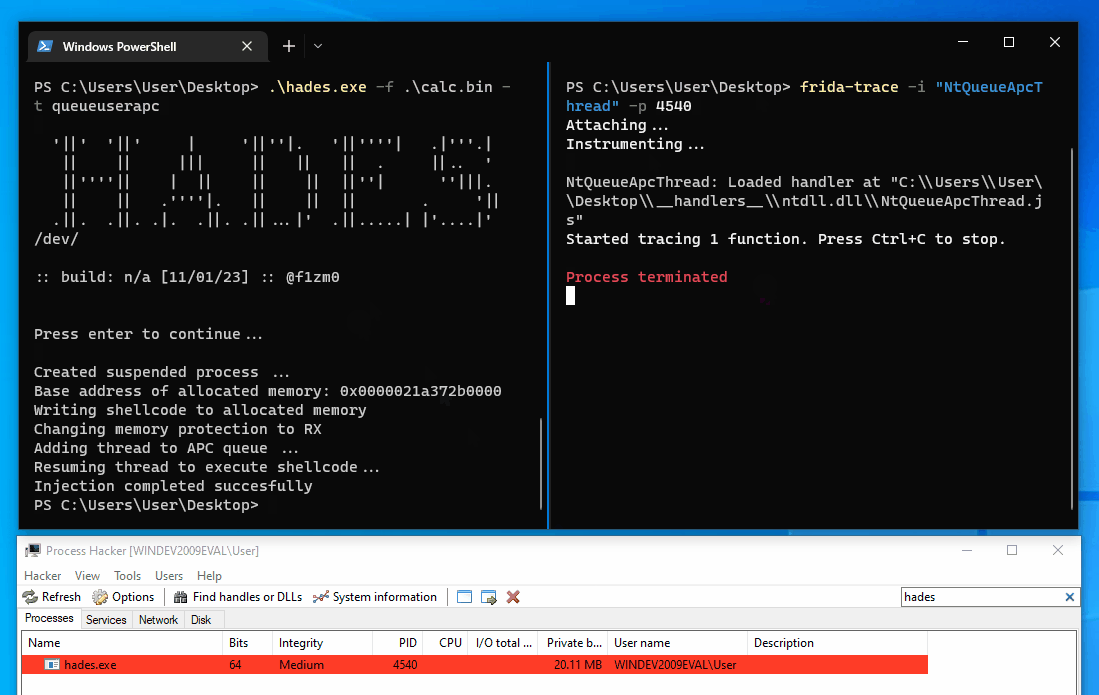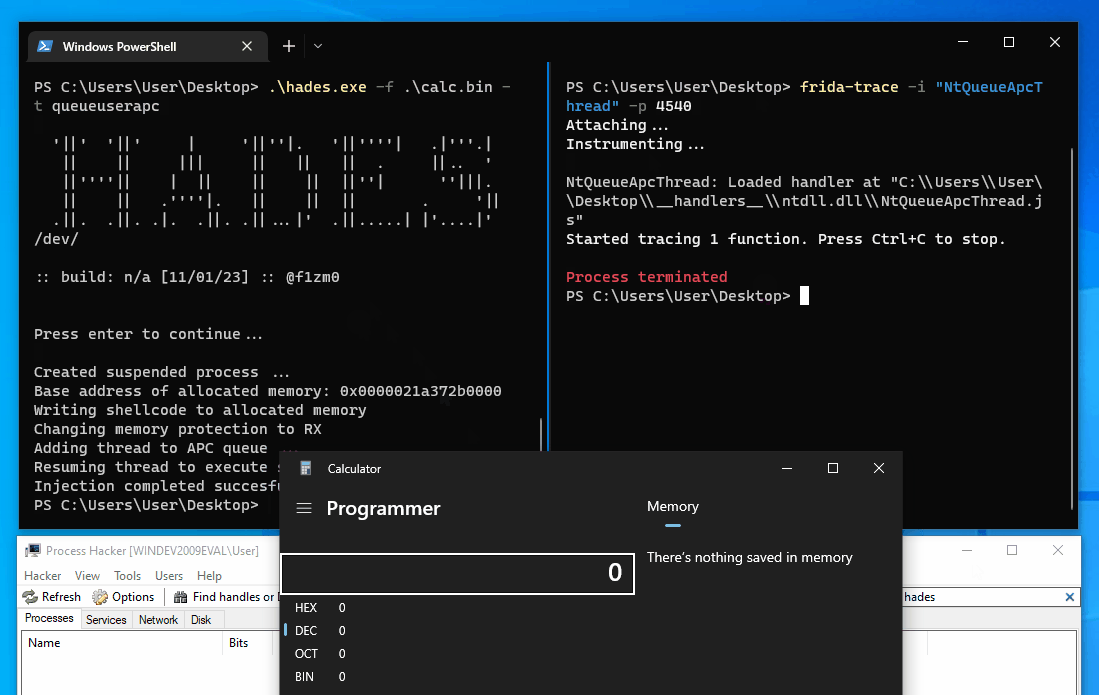 f1zm0/hades
Go shellcode loader that combines multiple evasion techniques
 maldev-academy/christmas
PoC demonstrating a multi process injection chain aimed at remotely executing shellcode
 zimawhit3/bitmancer
Nim Library for Offensive Security Development
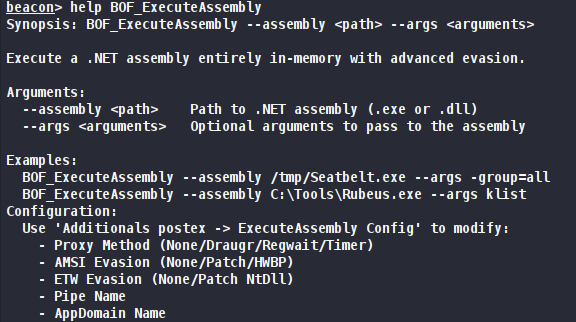 ntdallas/bof_executeassembly
Beacon Object File for Cobalt Strike that executes .NET assemblies in beacon with evasion techniques.
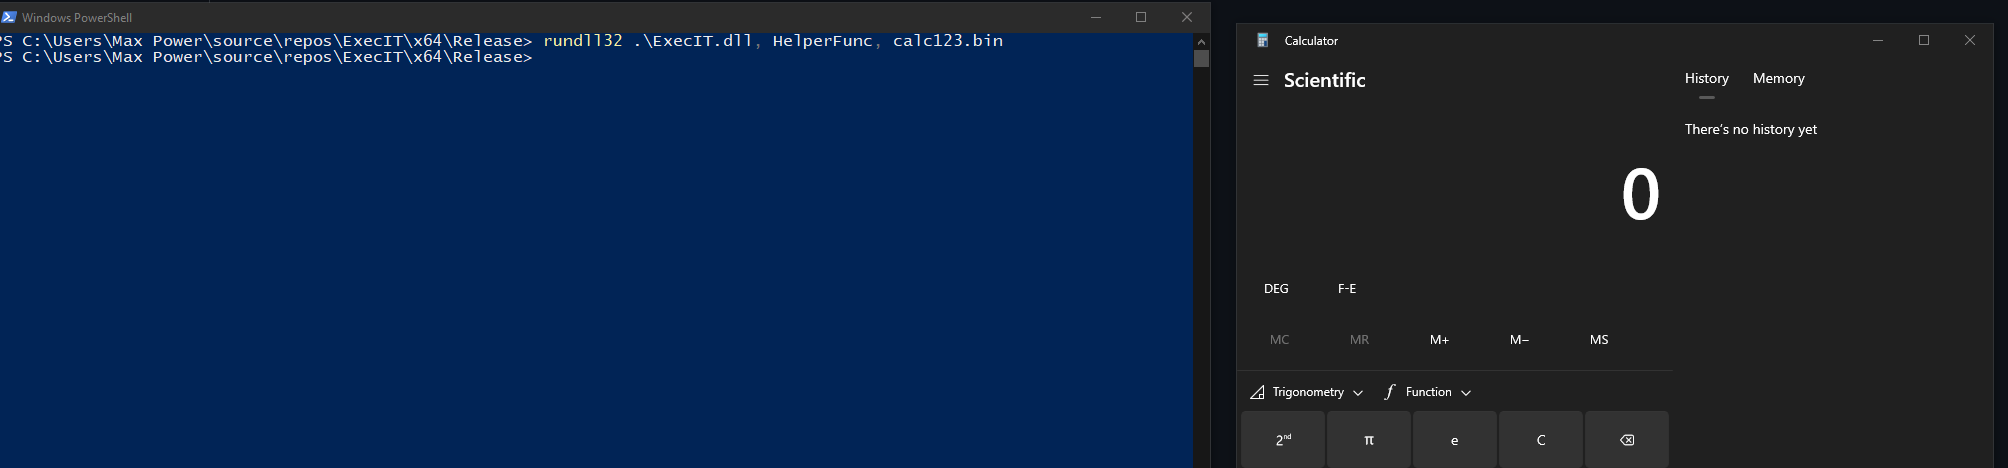 florylsk/execit
Execute shellcode files with rundll32
 secforce/sharpwhispers
C# porting of SysWhispers2. It uses SharpASM to find the code caves for executing the system call stub.
 ariary/volana
🌒 Shell command obfuscation to avoid detection systems
 silentisvox/syscallrevenant
Clean Indirect Syscalls with Syscall Tampering.
 gmh5225/icall-gadget
Exploit for redirecting control flow of a legit kernel module to your own illegitimate kernel module to evade anti-cheats stack walking
 xaff-xaff/black-angel-rootkit
Black Angel is a Windows 11/10 x64 kernel mode rootkit. Rootkit can be loaded with enabled DSE while maintaining its full functionality.
 nydubh3/cuiri
一款红队专用免杀木马生成器,基于shellcode生成绕过所有杀软的木马。