
CVE-2003-0264
 adenkiewicz/cve-2003-0264
Exploit for CVE-2003-0264 based on pwntools and metasploit's windows/reverse_tcp
binary-exploitationexploitationexploit-frameworks+3
adenkiewicz/cve-2003-0264Exploit for CVE-2003-0264 based on pwntools and metasploit's windows/reverse_tcp
 chris1sflaggin/lcsajdump
An ML powered Graph-Based Multi-Architecture Approach for ROP Gadget Detection
 boku7/venom
Venom C2 is a dependency‑free Python3 Command & Control framework for redteam persistence
 pard0p/remote-bof-runner
Remote BOF Runner is a Havoc extension framework for remote execution of Beacon Object Files (BOFs) using a PIC loader made with Crystal Palace.
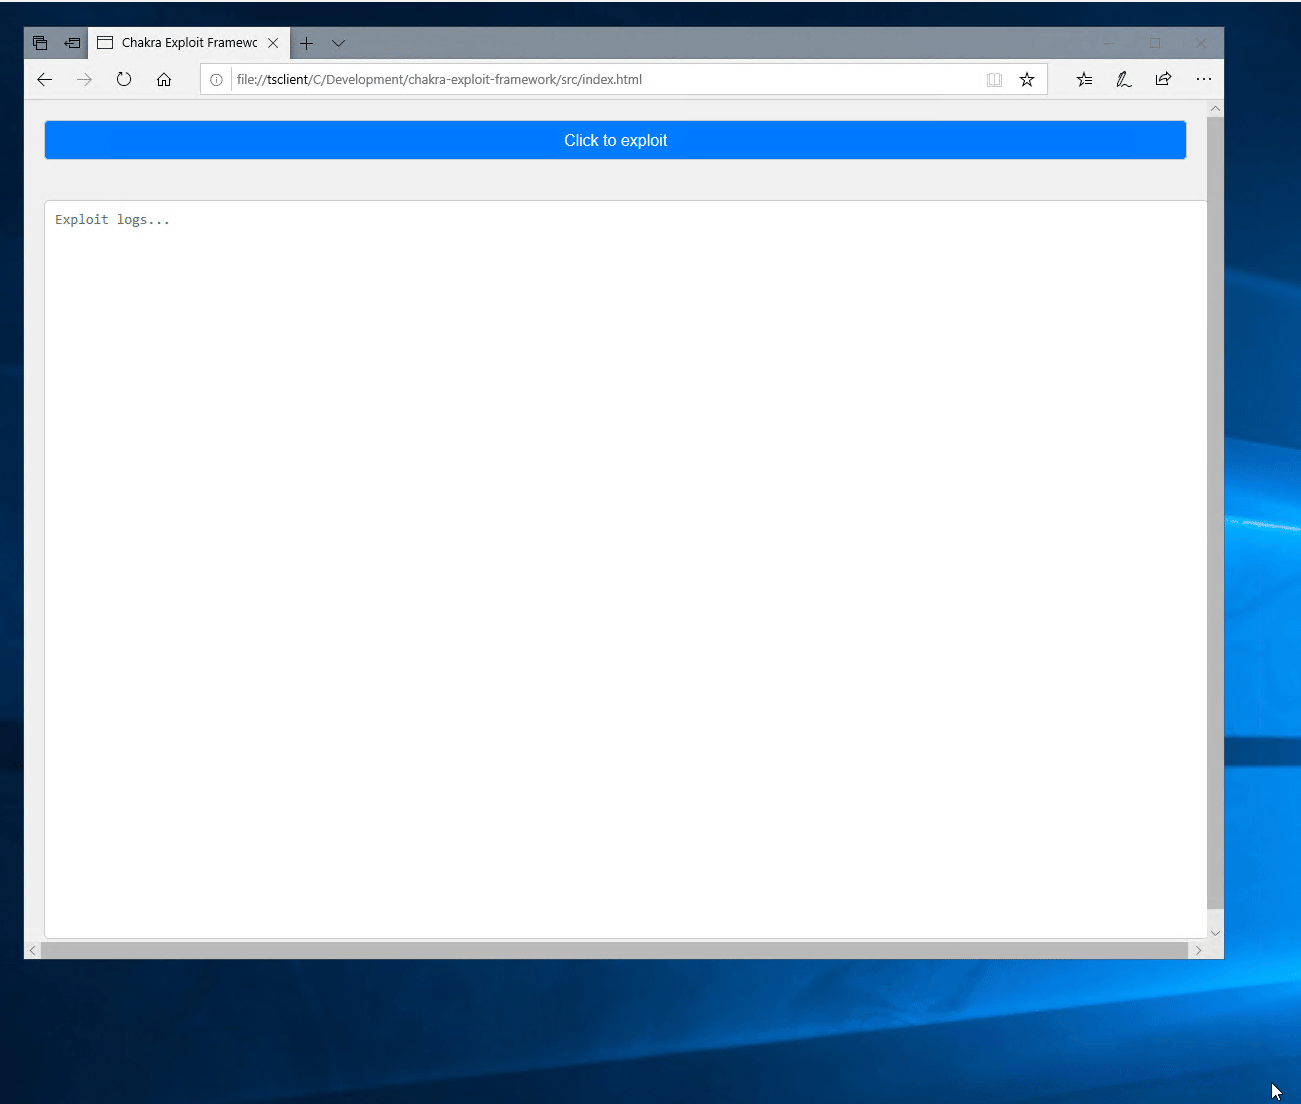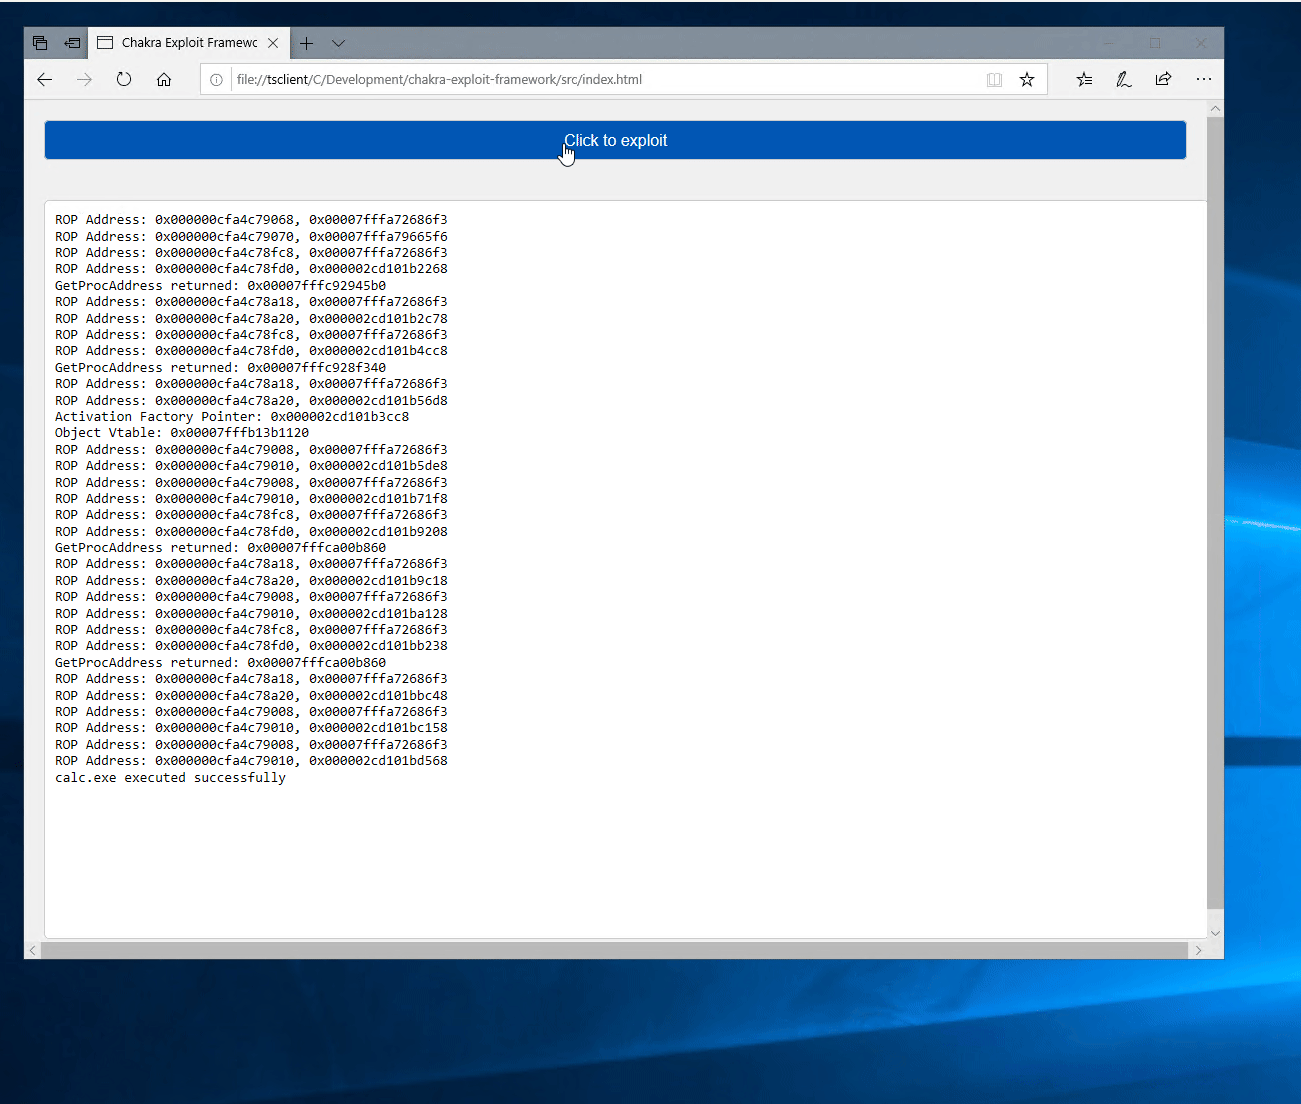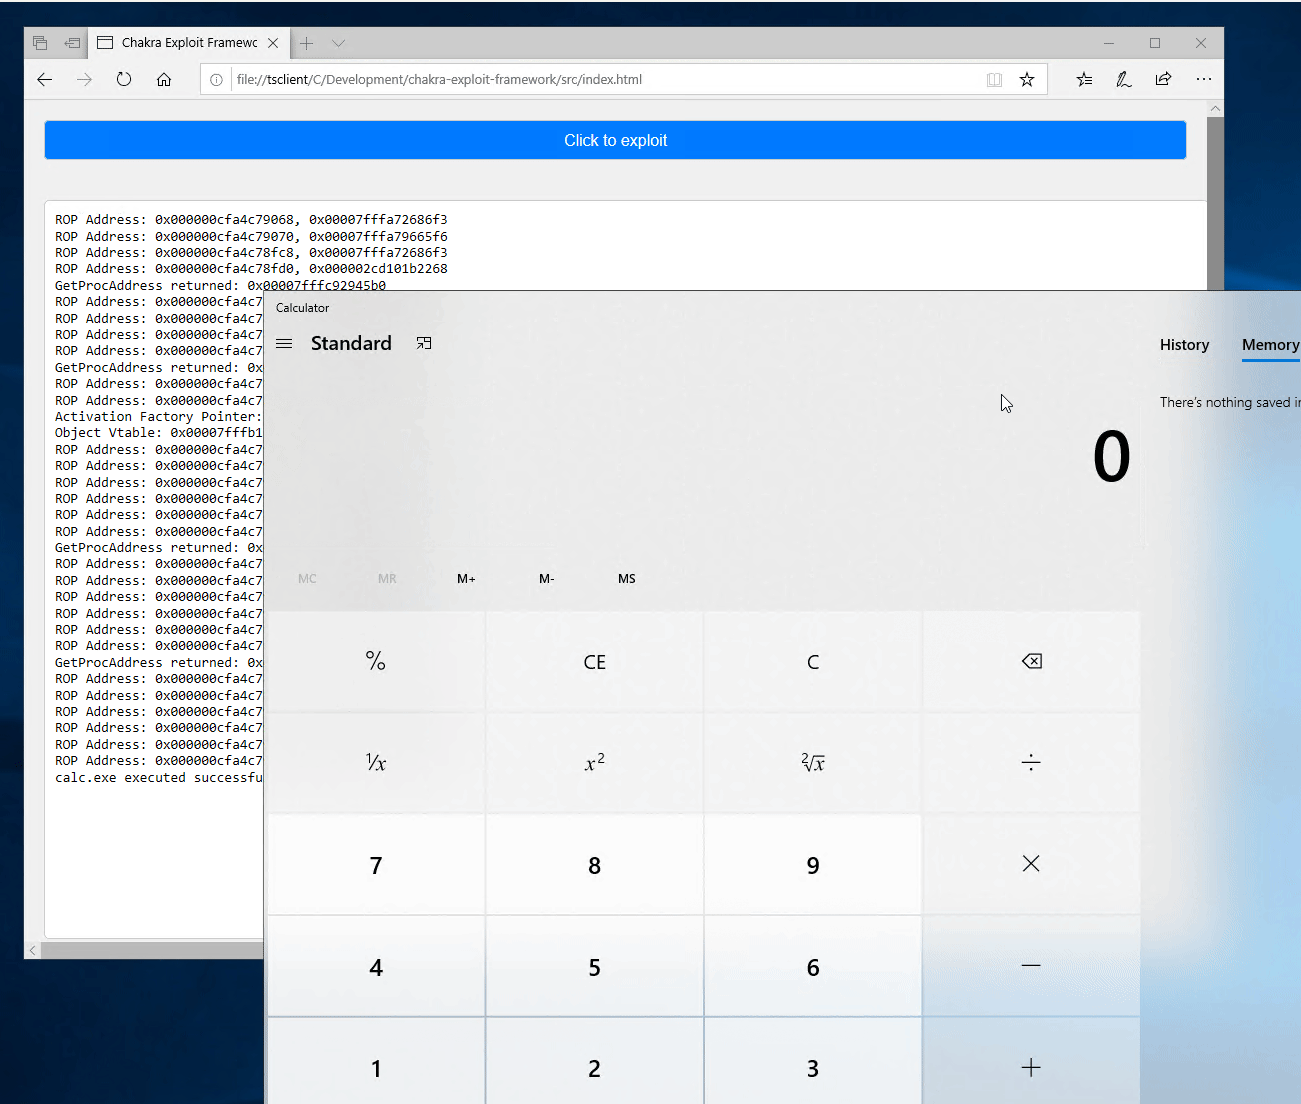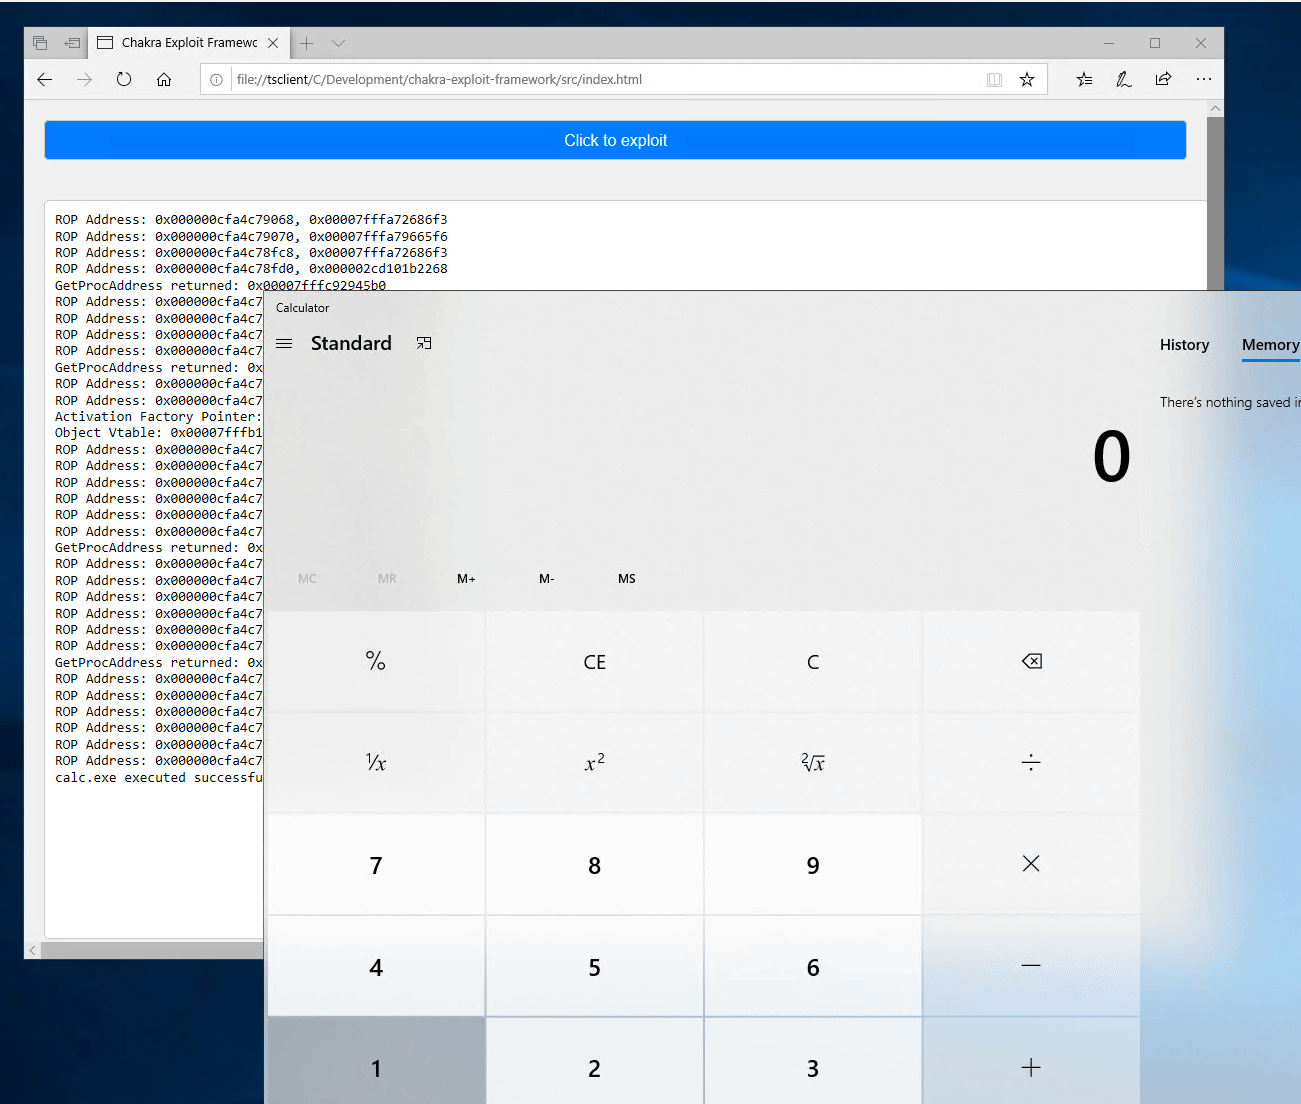 ntdelta/chakra-exploit-framework
Browser exploitation framework for Chakra (Edge). Written as part of OSEE preparation. Demo bug: CVE-2019-0567
 optiv/dent
A framework for creating COM-based bypasses utilizing vulnerabilities in Microsoft's WDAPT sensors.
 ekomssavior/airborne-poc
poc for CVE-2025-24252 & CVE-2025-24132
 optiv/scarecrow
ScareCrow - Payload creation framework designed around EDR bypass.
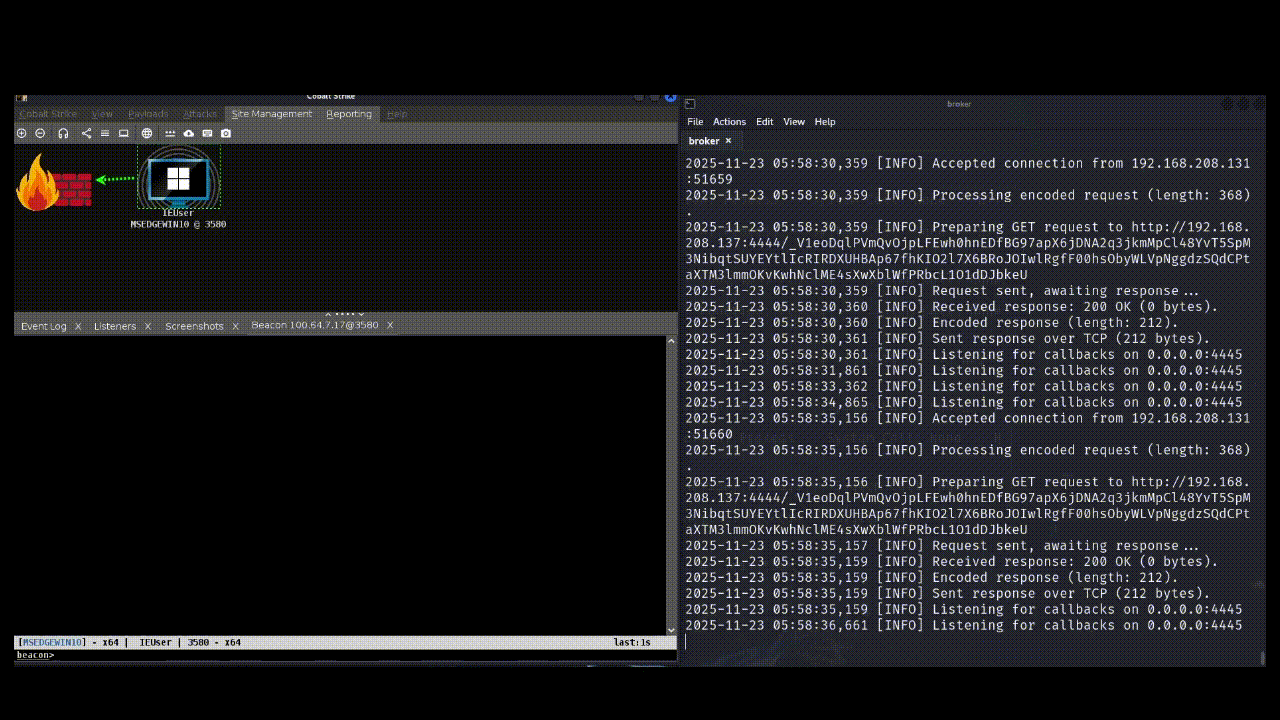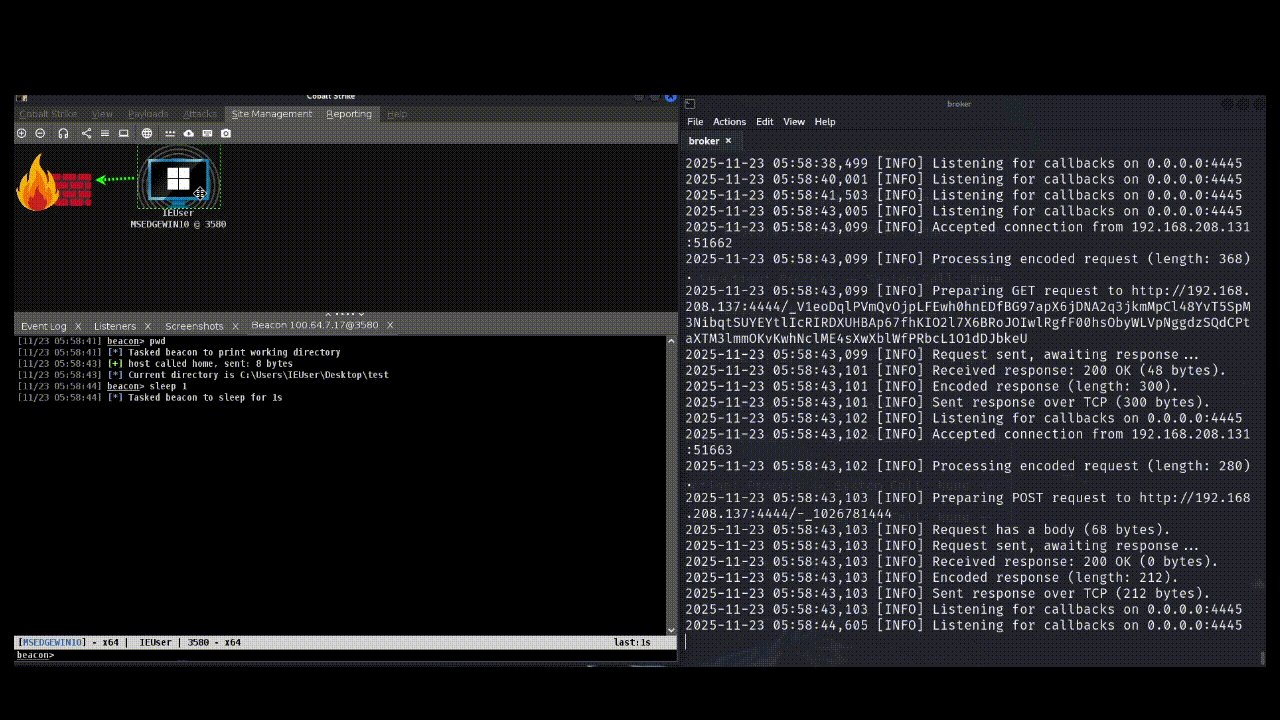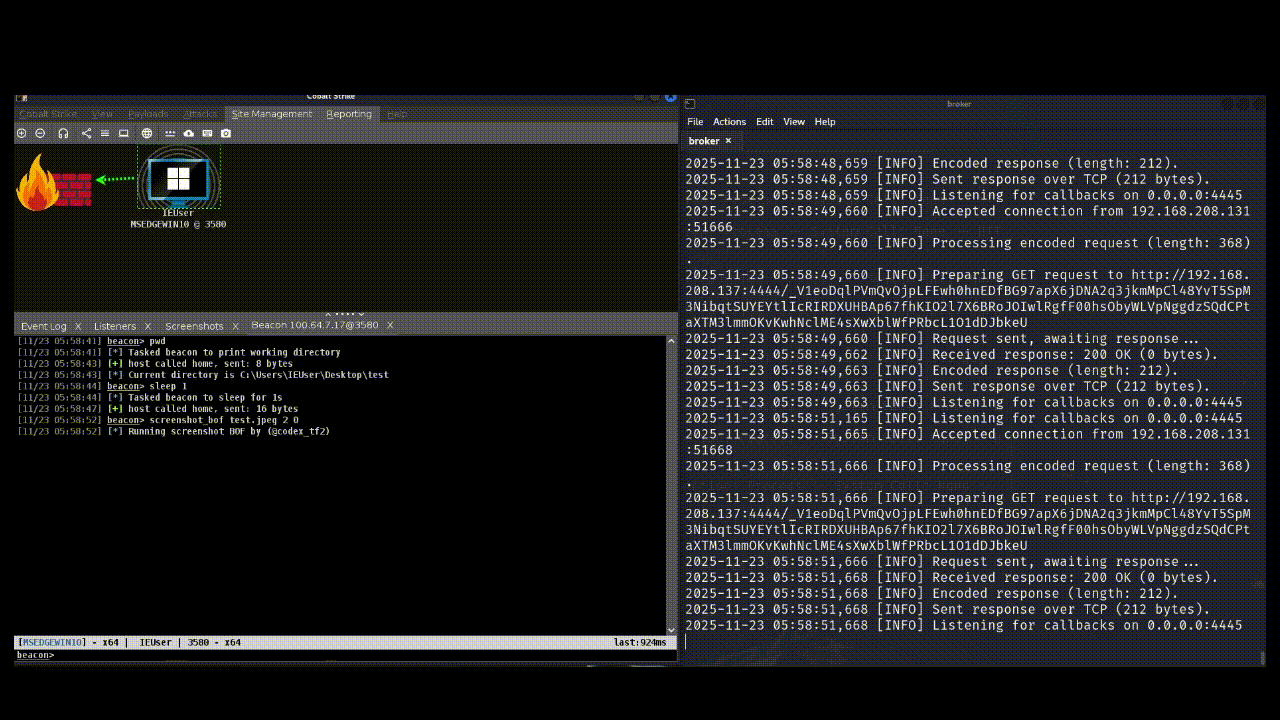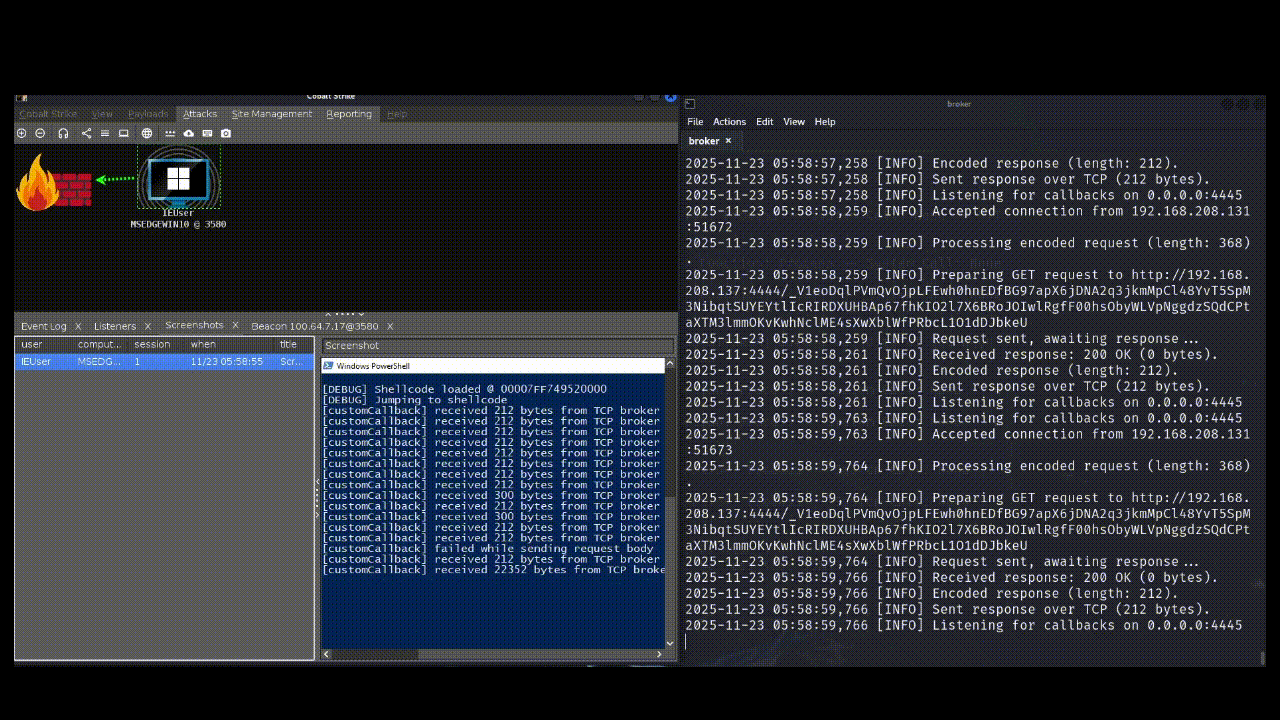 codextf2/customc2channeltemplate
template for developing custom C2 channels for Cobalt Strike using IAT hooks applied by a reflective loader.
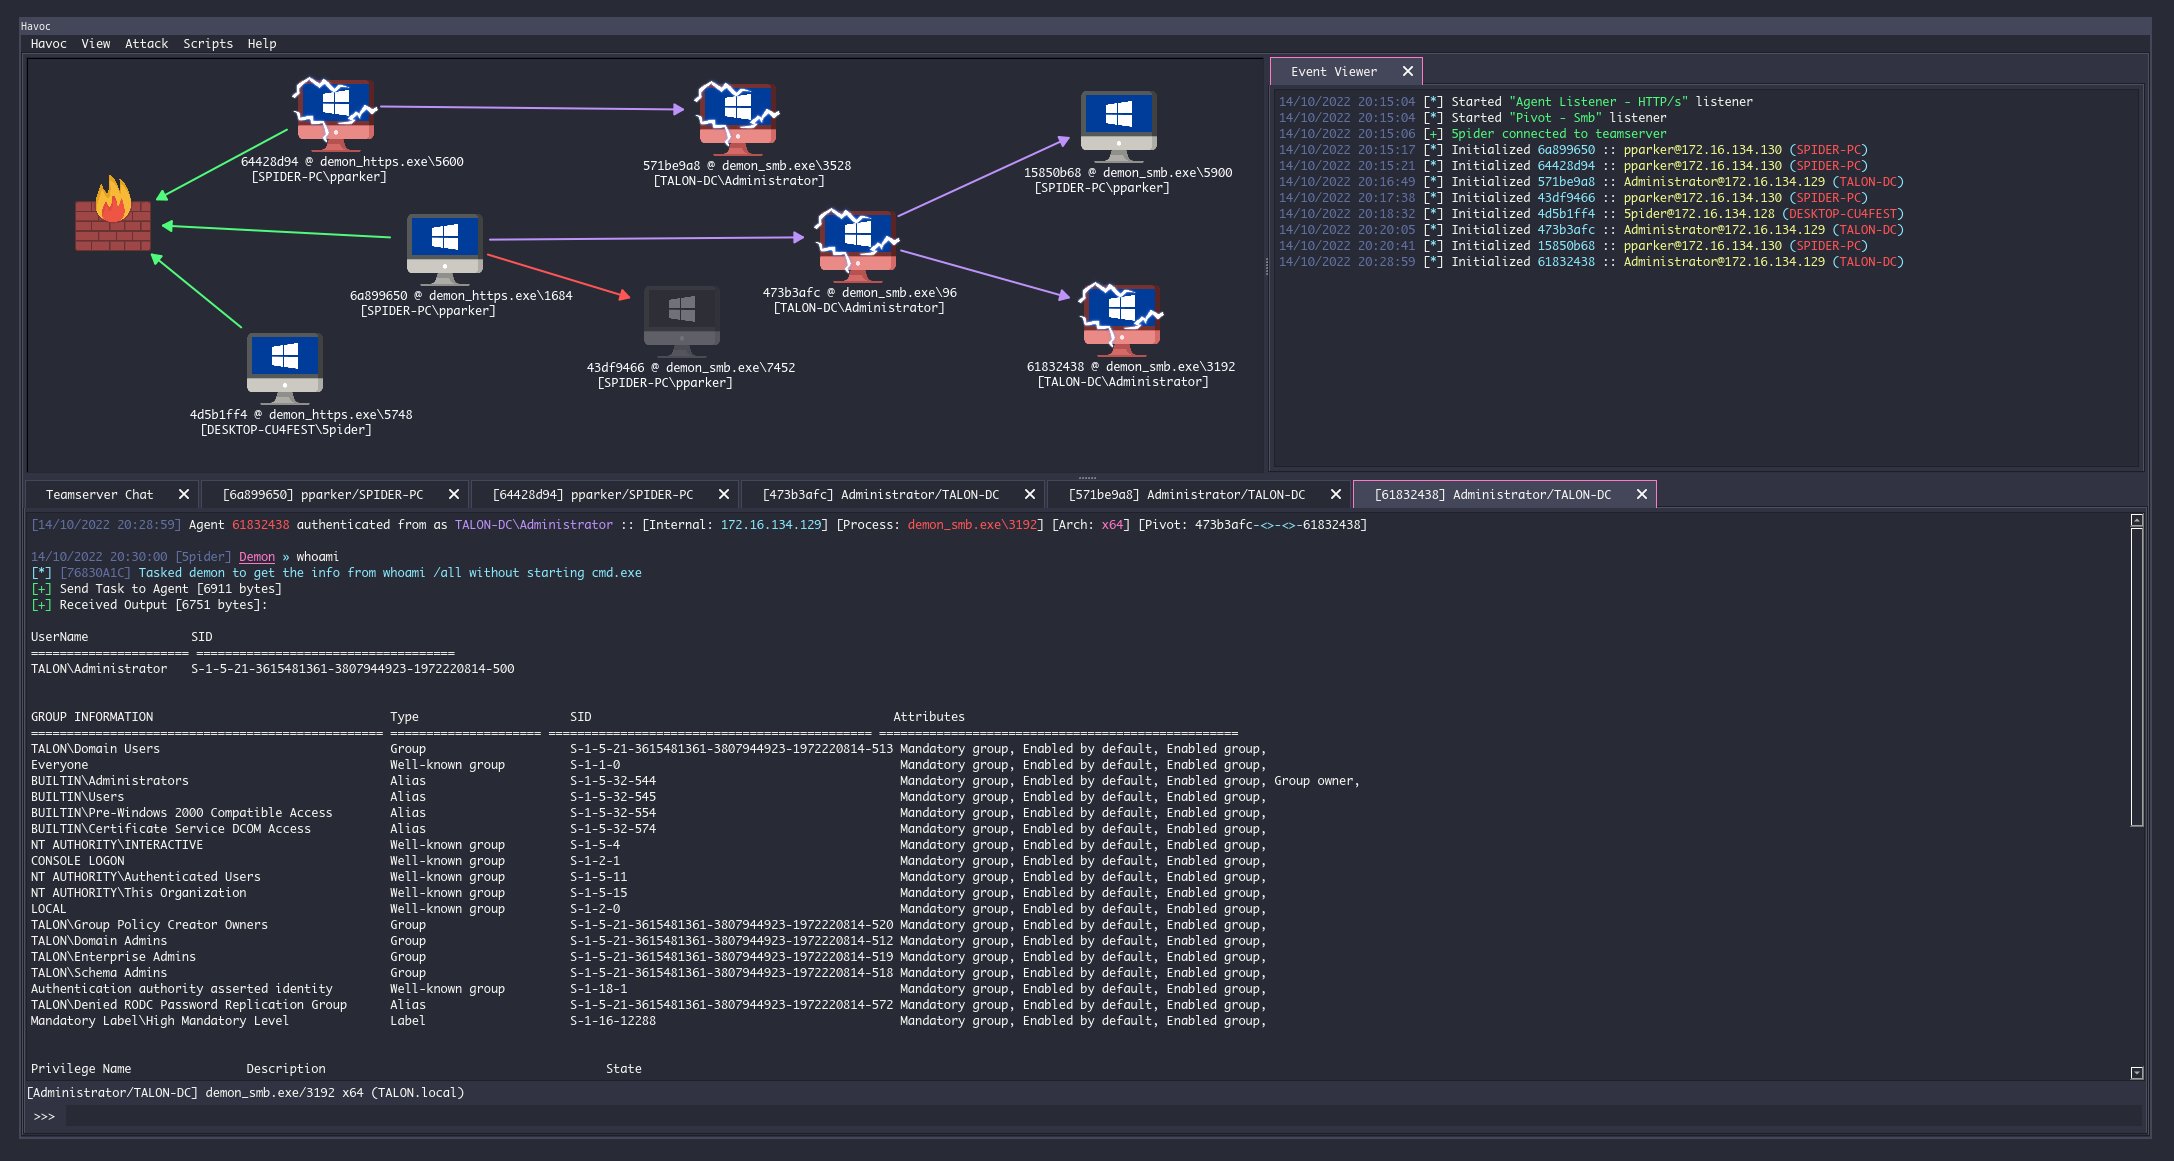 havocframework/havoc
The Havoc Framework
 winterknife/silverpick
Windows User-Mode Shellcode Development Framework (WUMSDF)
 rew-sploit/rew-sploit
Emulate and Dissect MSF and *other* attacks
 powershellmafia/powersploit
PowerSploit - A PowerShell Post-Exploitation Framework
 funnydog896/cve-2024-36401-woodpeckerplugin
CVE-2024-36401-GeoServer Property 表达式注入 Rce woodpecker-framework 插件
 bc-security/empire
Empire is a post-exploitation and adversary emulation framework that is used to aid Red Teams and Penetration Testers.
 chvancooten/nimpackt-v1
Nim-based assembly packer and shellcode loader for opsec & profit
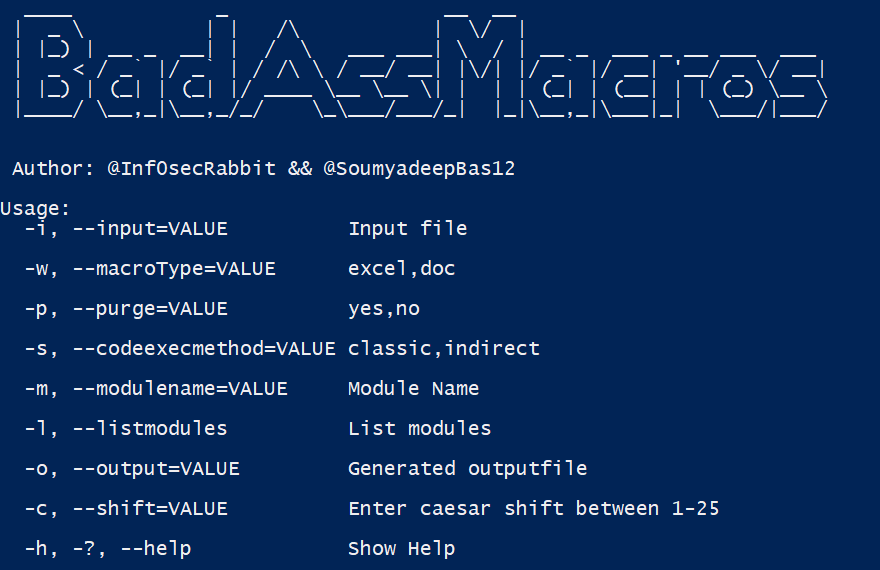 inf0secrabbit/badassmacros
C# tool that generates malicious VBA macros with shellcode injection, VBA purging, and sandbox detection for red team operations.
 rsmudge/cve-2020-0796-bof
Cobalt Strike Beacon Object File implementing CVE-2020-0796 SMBGhost local privilege escalation with dual weaponization paths for token theft and…