
dicerosbicornis
 maldevel/dicerosbicornis
A fully featured Windows backdoor that uses email as a C&C server
command-and-controldata-exfiltrationencryption-decryption-tools+5
16
maldevel/dicerosbicornisA fully featured Windows backdoor that uses email as a C&C server
 havocframework/havoc
The Havoc Framework
 sneakynachos/cve-2026-2766-but-with-wasm
CVE-2026-2766, but with wasm
 greycat-amc/cve-2025-5548
Analisis de CVE relacionada con stack overflow
 rapid7/metasploit-framework
Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…
 bishopfox/sliver
Adversary Emulation Framework
 k8gege/k8tools
K8工具合集(内网渗透/提权工具/远程溢出/漏洞利用/扫描工具/密码破解/免杀工具/Exploit/APT/0day/Shellcode/Payload/priviledge/BypassUAC/OverFlow/WebShell/PenTest) Web GetShell…
 bc-security/empire
Empire is a post-exploitation and adversary emulation framework that is used to aid Red Teams and Penetration Testers.
 trustedsec/unicorn
Unicorn is a simple tool for using a PowerShell downgrade attack and inject shellcode straight into memory. Based on Matthew Graeber's powershell…
 byt3bl33d3r/offensivenim
My experiments in weaponizing Nim (https://nim-lang.org/)
 trickster0/offensiverust
Rust Weaponization for Red Team Engagements.
 t3l3machus/villain
Villain is a high level stage 0/1 C2 framework that can handle multiple reverse TCP & HoaxShell-based shells, enhance their functionality with…
 bytecode77/r77-rootkit
Fileless ring 3 rootkit with installer and persistence that hides processes, files, network connections, etc.
 mdsecactivebreach/sharpshooter
Payload Generation Framework
 nccgroup/winpayloads
Undetectable Windows Payload Generation
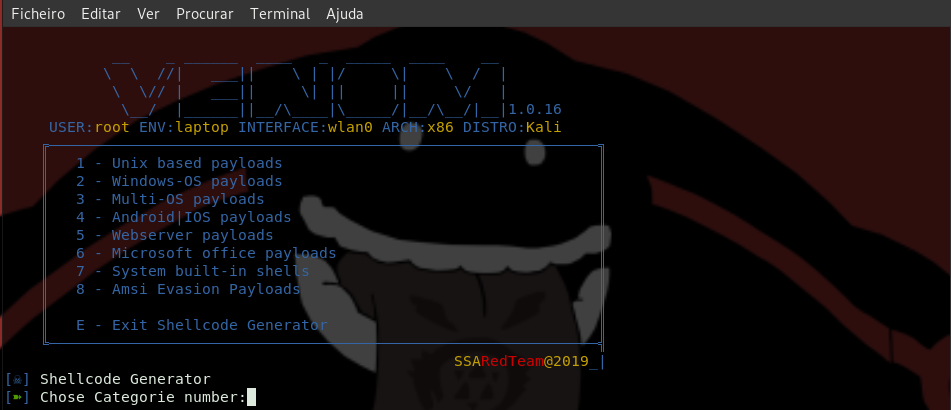 r00t-3xp10it/venom
venom - C2 shellcode generator/compiler/handler
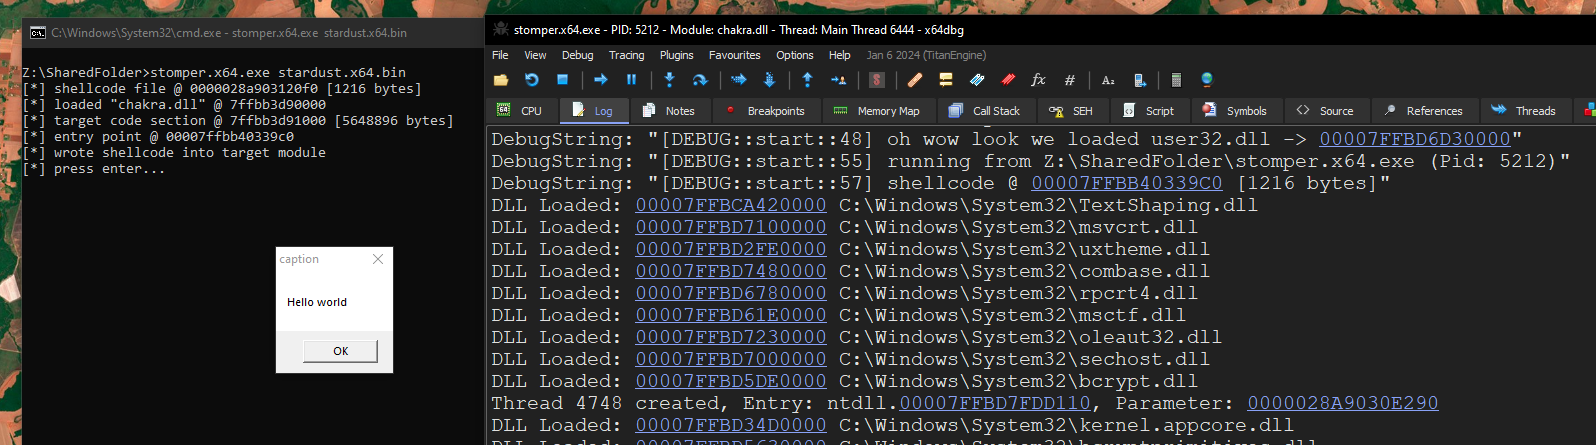 cracked5pider/stardust
A modern 32/64-bit position independent implant template