Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
32 results
NTDLL-reconstruction preview

NTDLL-reconstruction

GitHubsk4r4b/ntdll-reconstruction

A technique that mixes NTDLL unhooking and hellsgate gate varients

binary-exploitationdefensive-toolsids-ips-evasion+6
33
1 day ago
PngLoader preview

PngLoader

GitHubi014n/pngloader

Hides arbitrary payloads in PNG images using nibble-to-ASCII encoding and Fibonacci LSB steganography, with a C++ loader that extracts and executes…
defensive-toolseducationexploitation+6
33 days ago
ReflectivePluginLoader preview

ReflectivePluginLoader

GitHubracoten/reflectivepluginloader

Minimal Windows x64 reflective PE mapper that loads DLLs from memory without LoadLibrary, resolves exports, and dispatches calls through a…

binary-exploitationdefensive-toolseducation+7
511 days ago
KDU preview

KDU

GitHubhfiref0x/kdu

Windows kernel driver utility that abuses vulnerable signed drivers (BYOVD) to bypass DSE, load unsigned drivers, hijack protected processes, and…
binary-exploitationdefensive-toolsexploitation+8
2.8k1 month ago
polychrome-rs preview

polychrome-rs

GitHubdovelus/polychrome-rs

A PoC on how to use a Compute Shader as Payload

defensive-toolsencryption-decryption-toolsexploitation+5
101 month ago
TinyLoad preview

TinyLoad

GitHubiamsopotatoe-coder/tinyload

Open source Windows x64 PE packer and crypter. Compresses and encrypts executables with a custom virtual machine into a self extracting stub.

binary-analysisencryption-decryption-toolsexploitation+5
2022 months ago
r77-rootkit preview

r77-rootkit

GitHubbytecode77/r77-rootkit

Fileless ring 3 rootkit with installer and persistence that hides processes, files, network connections, etc.
command-and-controldefensive-toolsids-ips-evasion+6
2.2k3 months ago
p3-loader preview

p3-loader

GitHuborange-cyberdefense/p3-loader

P³-Shellcode Loader is a loader that implements a code injection technique which leverages the Process Parameters structure as an execution and…
binary-exploitationdefensive-toolseducation+8
2463 months ago
Obfusk8 preview

Obfusk8

GitHubx86byte/obfusk8

Obfusk8: lightweight Obfuscation library based on C++17 / Header Only for windows binaries
cryptographyexploit-frameworkspayload-development+4
8384 months ago
QuasarNix preview

QuasarNix

GitHubdtrizna/quasarnix

Reverse Shell Detection with Machine Learning
adversarial-attackanomaly-detectiondefensive-tools+6
84 months ago
CustomLoadImage preview

CustomLoadImage

GitHubbackdoorskid/customloadimage

Stealthy .NET assembly loading using AssemblyNative::LoadFromBuffer
defensive-toolsexploitationpenetration-testing+3
597 months ago
watcher preview

watcher

GitHubthemoonsir/watcher

Detection reverse shell and kill it before trying shell.
binary-analysisdefensive-toolsincident-response+5
28 months ago
redpill preview

redpill

GitHubr00t-3xp10it/redpill

Assist reverse tcp shells in post-exploration tasks
defensive-toolsinformation-gatheringlateral-movement+6
2181 year ago
LazySign preview

LazySign

GitHubjfmaes/lazysign

Create fake certs for binaries using windows binaries and the power of bat files

binary-analysisdefensive-toolsimpersonation-tools+6
5692 years ago
SysWhispers3 preview

SysWhispers3

GitHubklezvirus/syswhispers3

SysWhispers on Steroids - AV/EDR evasion via direct system calls.
defensive-toolsexploitationids-ips-evasion+5
1.7k2 years ago
FunctionStomping preview
Archived

FunctionStomping

GitHubidov31/functionstomping

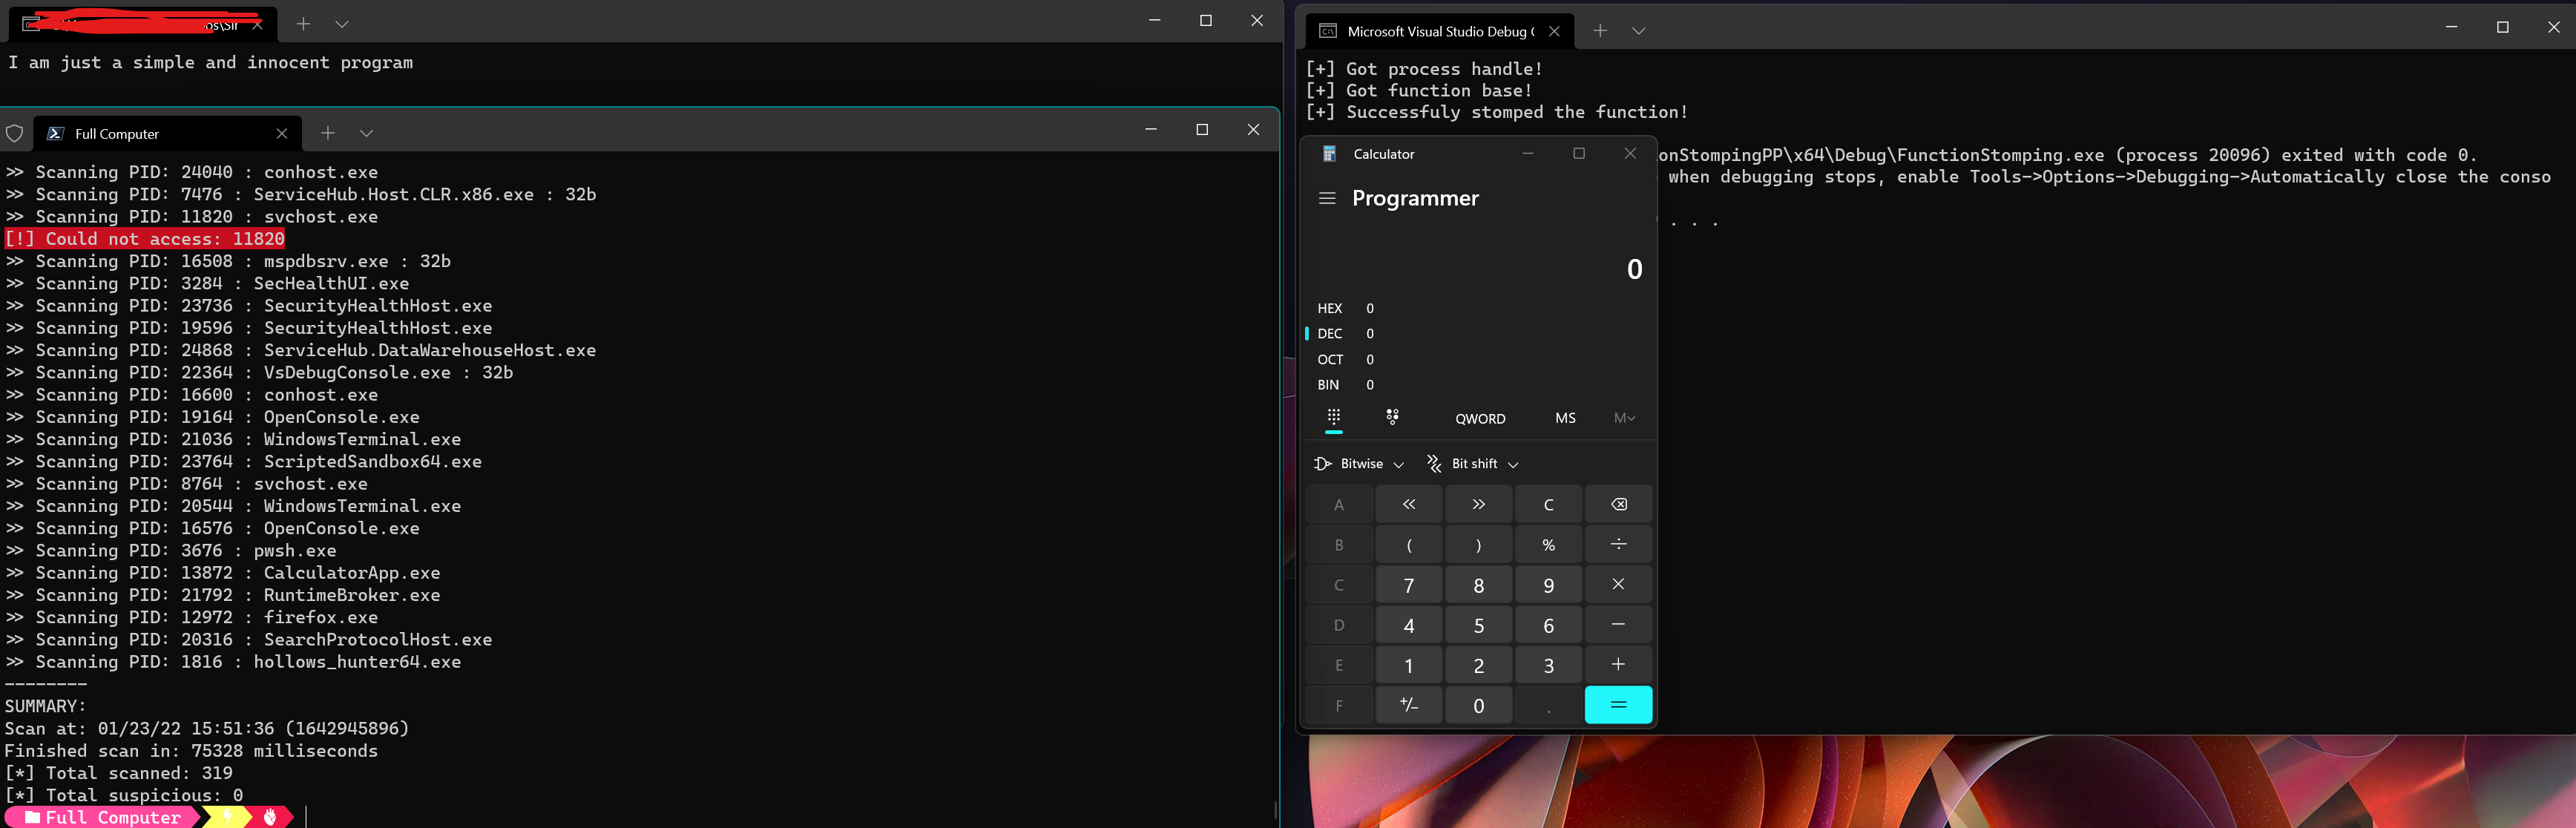
Shellcode injection technique. Given as C++ header, standalone Rust program or library.
binary-exploitationdefensive-toolsexploitation+7
7073 years ago
Mangle preview
Archived

Mangle

GitHuboptiv/mangle

Mangle is a tool that manipulates aspects of compiled executables (.exe or DLL) to avoid detection from EDRs

binary-analysisdefensive-toolsexploitation+6
1.2k3 years ago
Dent preview
Archived

Dent

GitHuboptiv/dent

A framework for creating COM-based bypasses utilizing vulnerabilities in Microsoft's WDAPT sensors.

defensive-toolsexploit-frameworksids-ips-evasion+2
2963 years ago
Previous12Next