metasploit-framework

Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…

Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…

A collection of initial access loaders to use inside enterprise hardened enviroments

K8工具集(内网渗透/提权工具/远程溢出/漏洞利用/端口扫描/密码破解/免杀/Exploit/RCE/LPE/0day/Shellcode/Payload/BypassUAC/OverFlow/WebShell/PenTest/hacking(Struts2/Zimbra/Weblogic/Tomc…

Empire is a post-exploitation and adversary emulation framework that is used to aid Red Teams and Penetration Testers.

Adversary Emulation Framework

A Windows implant development framework for offensive engineering and C2 research.

Linux C2 beacon with native in-memory ELF BOF loader, AES-256-CFB encrypted polling, and a Python C2 server for fileless post-exploitation modules.

Unified repository for different Metasploit Framework payloads


Unicorn is a simple tool for using a PowerShell downgrade attack and inject shellcode straight into memory. Based on Matthew Graeber's powershell…

Cross-platform C2 agent for Mythic with dynamic function loading, SOCKS5 proxy, file operations, shellcode injection, and macOS/Windows…

This is a project aimed to make every other Saas product a C2, confluence is just the beginning.

CVE-2026-96652 CVE-2026-96654 CVE-2026-96655 CVE-2026-96656

Merlin is a cross-platform post-exploitation HTTP/2 Command & Control server and agent written in golang.

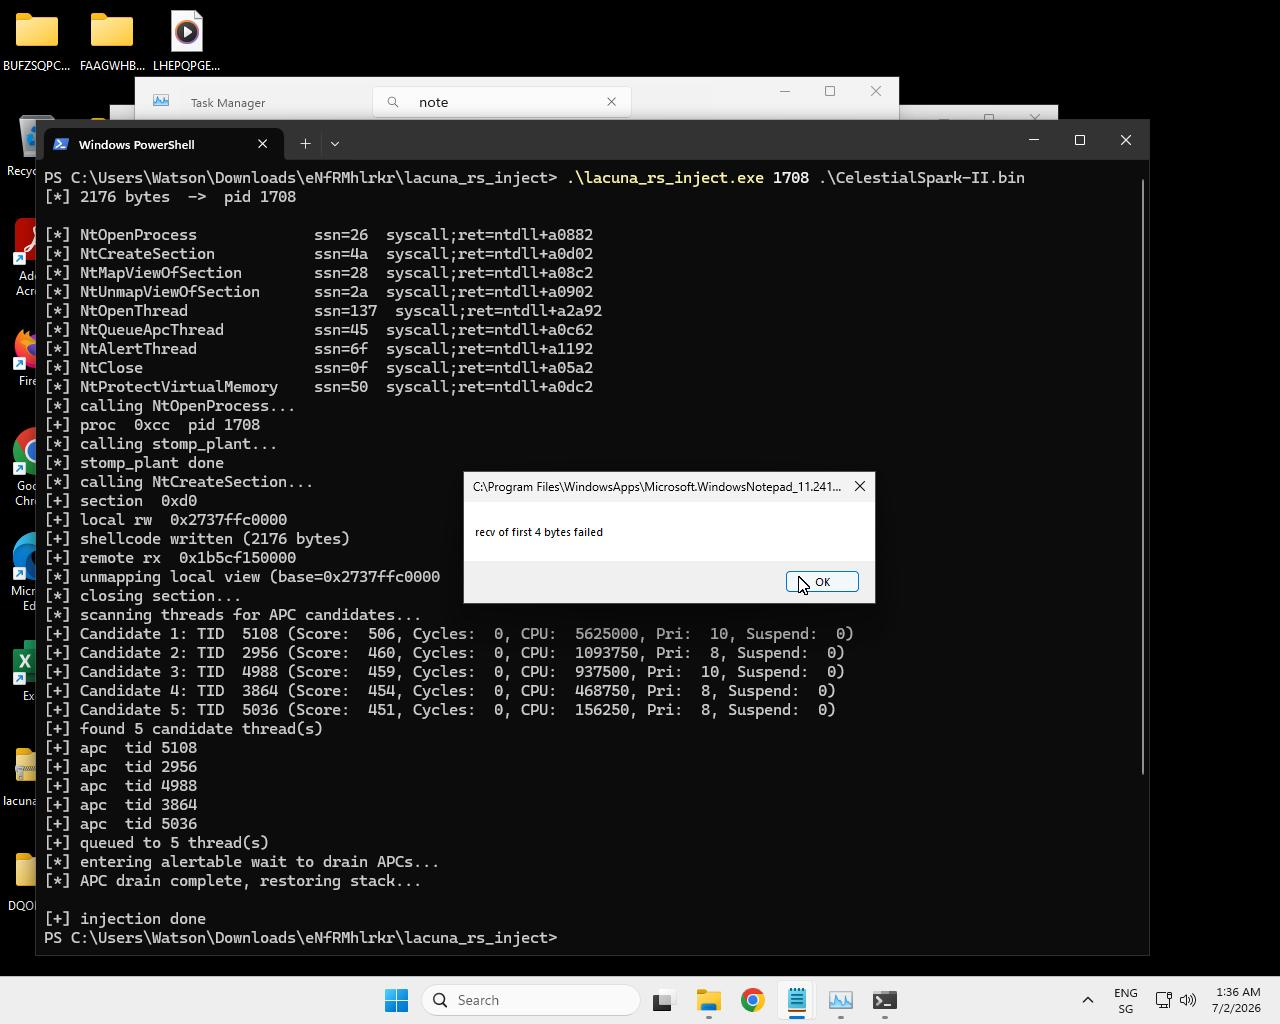
Rust crate for ghost-frame call-stack spoofing, runtime indirect syscalls, and APC injection on Windows x64. Provides SSN resolution, JIT stub…

Fileless x64 Assembly C2 framework with dual-channel ICMP/DNS protocol pivoting, direct syscall execution, and ptrace-based process injection for…


Proof of Concept for Process Code Injection Without Using WriteProcessMemory