
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
219 results
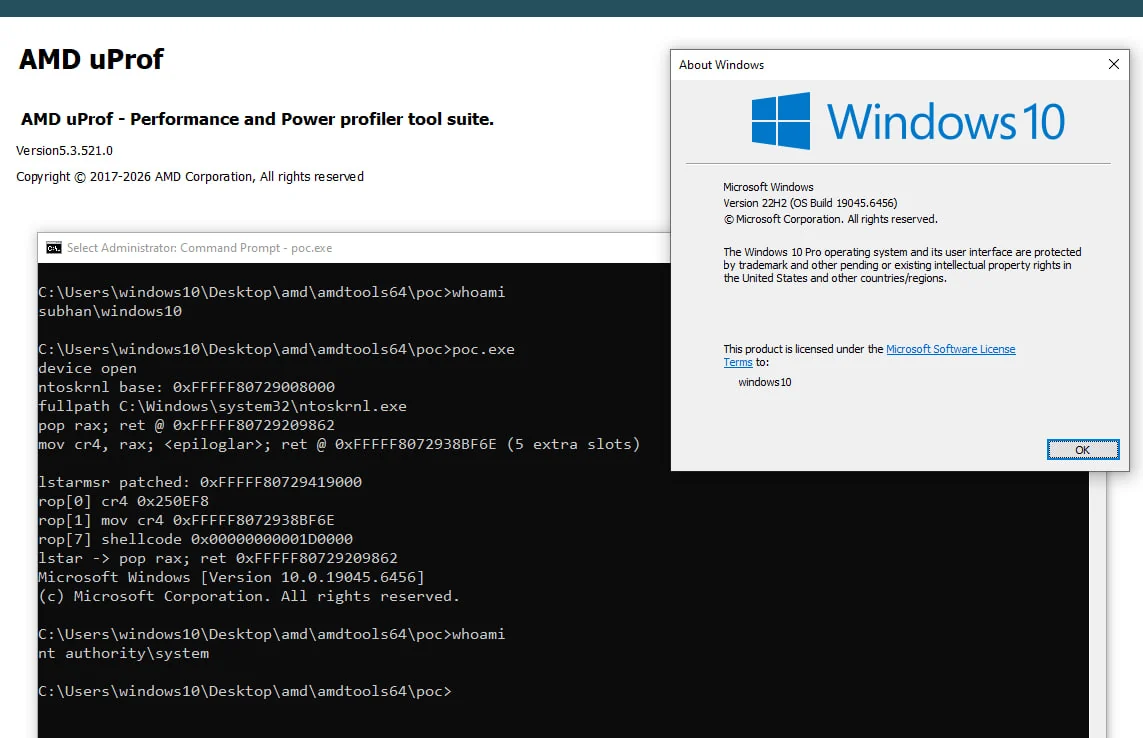
MercilessAmd preview

MercilessAmd

GitHubmein-0/mercilessamd

Proof-of-concept exploiting AMD AmdTools64.sys MSR read/write IOCTLs to overwrite IA32_LSTAR, bypass SMEP and escalate from administrator to SYSTEM…
binary-exploitationexploitationprivilege-escalation+4
4 days ago
OffensiveReverseShellCheatSheet preview

OffensiveReverseShellCheatSheet

GitHubd4t4s3c/offensivereverseshellcheatsheet

Curated cheat sheet of reverse shell payloads in Bash, Netcat, PHP, PowerShell, Python, Perl, Ruby, and msfvenom, plus webshells, log poisoning, and…
command-and-controlcurated-resourceseducation+8
5461 year ago
blacksandbeacon preview

blacksandbeacon

GitHubgrisuno/blacksandbeacon

Linux C2 beacon with native in-memory ELF BOF loader, AES-256-CFB encrypted polling, and a Python C2 server for fileless post-exploitation modules.
binary-exploitationcommand-and-controlencryption-decryption-tools+9
1514 days ago
ReflectiveDLLRefresher preview

ReflectiveDLLRefresher

GitHubcylancevulnresearch/reflectivedllrefresher

Reflective DLL that scans process memory and unhooks loaded libraries to evade security software, with UPX, TLS injector, and Meterpreter integration.
ids-ips-evasionmalware-analysispayload-development+6
3248 years ago
GhostStrike preview

GhostStrike

GitHubstivenhacker/ghoststrike

C++ process hollowing injector that encrypts and obfuscates shellcode with XOR, Base64, and dynamic API resolution to deploy stealthy reverse shells…
command-and-controlencryption-decryption-toolsmalware-analysis+4
8282 years ago
Packer-payload-EntropyReducer preview

Packer-payload-EntropyReducer

GitHubgmh5225/packer-payload-entropyreducer

Reduce Entropy And Obfuscate Youre Payload With Serialized Linked Lists
encryption-decryption-toolsmalware-analysispayload-development+3
53 years ago
PngLoader preview

PngLoader

GitHubi014n/pngloader

Hides arbitrary payloads in PNG images using nibble-to-ASCII encoding and Fibonacci LSB steganography, with a C++ loader that extracts and executes…
defensive-toolseducationexploitation+6
236 days ago
mcp-gamehacking preview

mcp-gamehacking

GitHub1llu50ry/mcp-gamehacking

MCP server exposing a 4,100+ skill game-hacking and reverse-engineering knowledge base with source archives, specialized agents, subagents, plugins…
ai-assisted-reversingbinary-analysiscurated-resources+6
5284 days ago
ConfluenceC2 preview

ConfluenceC2

GitHubdagowda/confluencec2

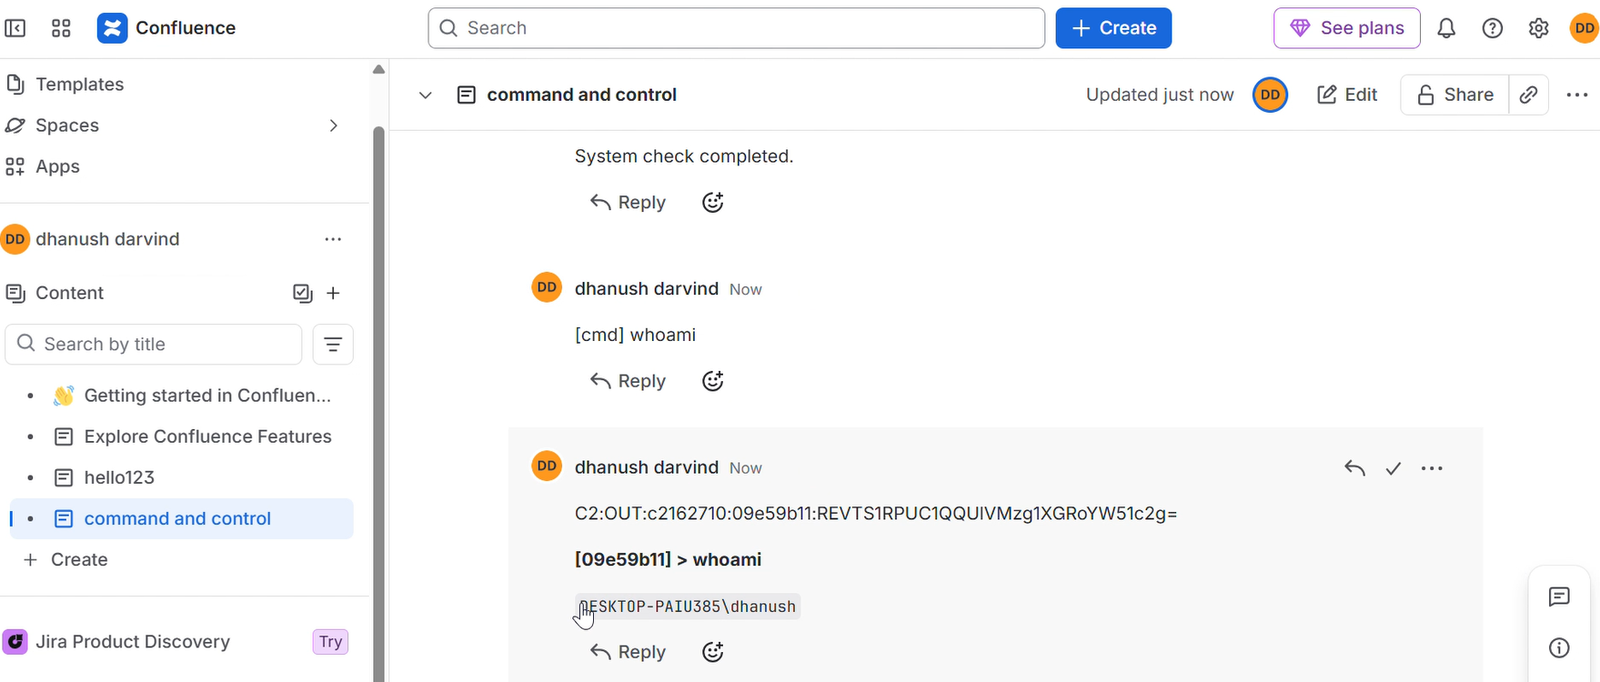
This is a project aimed to make every other Saas product a C2, confluence is just the beginning.
command-and-controldata-exfiltrationlateral-movement+9
2112 days ago
SyscallRevenant preview

SyscallRevenant

GitHubsilentisvox/syscallrevenant

Clean Indirect Syscalls with Syscall Tampering.
binary-exploitationexploitationids-ips-evasion+6
518 days ago
Relapse-Exploit preview

Relapse-Exploit

GitHubntfargo/relapse-exploit

PS5 exploit chain for firmware 7.00-13.60 combining a WebKit JSC info leak and typedarray corruption with an aio_multi_wait UAF race for kernel…
binary-exploitationeducationexploitation+5
2.6k1 month ago
house_of_apple_2 preview

house_of_apple_2

GitHubjazho76/house_of_apple_2

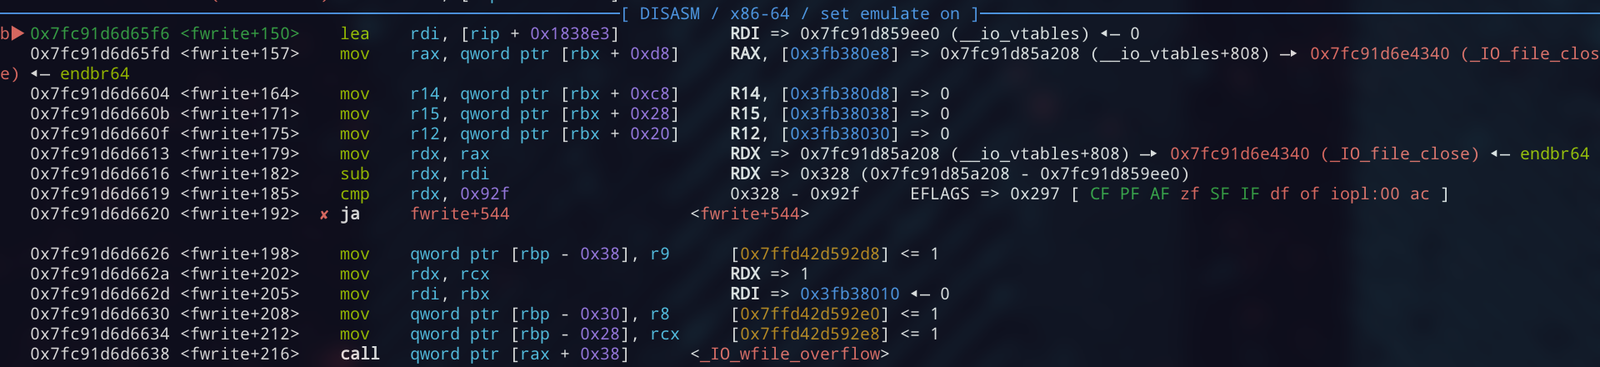
Interactive GDB walkthrough of the House of Apple 2 FSOP technique on glibc 2.43, with a reproducible sandbox covering vtable bypass, stack pivoting,…
binary-exploitationdebuggerseducation+7
52 months ago
CVE-2025-22457-vulnserver-lab preview

CVE-2025-22457-vulnserver-lab

GitHubdonofly/cve-2025-22457-vulnserver-lab

Hands-on lab reproducing CVE-2025-22457: sets up Docker attacker/victim containers, finds stack addresses with GDB, and delivers a msfvenom reverse…
binary-exploitationctfeducation+6
1 month ago
EvilVM preview

EvilVM

GitHubjephthai/evilvm

Forth-based compiler deployed as position-independent x86_64 shellcode, providing a remote code execution agent with interactive REPL over TCP, HTTP,…
command-and-controlexploit-frameworkspayload-development+7
2095 years ago
MSRKit preview

MSRKit

GitHubrurixis/msrkit

A concept of using a ROP chain paired with a WRMSR primitive to call kernel functions and map unsigned drivers through BYOVD (AmdTools64.sys)
binary-exploitationexploitationpayload-development+5
671 month ago
MS09-050 preview

MS09-050

GitHubbytejmp/ms09-050

Python exploit for MS09-050 (CVE-2009-3103) SMBv2 srv2.sys buffer overflow, with vulnerability scanner, arch auto-detection, and x86/x64 reverse…

exploitationinformation-gatheringnetwork-security+7
1 month ago
CVE-2026-43499-S26 preview

CVE-2026-43499-S26

GitHubsammyenigma/cve-2026-43499-s26

Android GKI 6.12 kernel exploit for CVE-2026-43499, chaining an rt_mutex rollback bug with pselect stack overwrite to gain root on Samsung and Pixel…

android-securitybinary-exploitationexploitation+8
2 months ago
radare2-scripts preview

radare2-scripts

GitHubwithsecurelabs/radare2-scripts

Collection of radare2 scripts for malware analysis: carve binaries from memory dumps, patch PE headers, and decode hashed function imports in…

binary-analysisdigital-forensicsmalware-analysis+3
328 years ago
Previous12…13Next