
kAFL
 intellabs/kafl
A fuzzer for full VM kernel/driver targets
dynamic-analysis-sandboxingembedded-systems-securityfirmware-analysis+4
intellabs/kaflA fuzzer for full VM kernel/driver targets
 aarif450/zapscape
Guest-to-host KVM/x86 escape exploiting CVE-2026-64561, delivering a full PoC chain and analysis for security researchers.
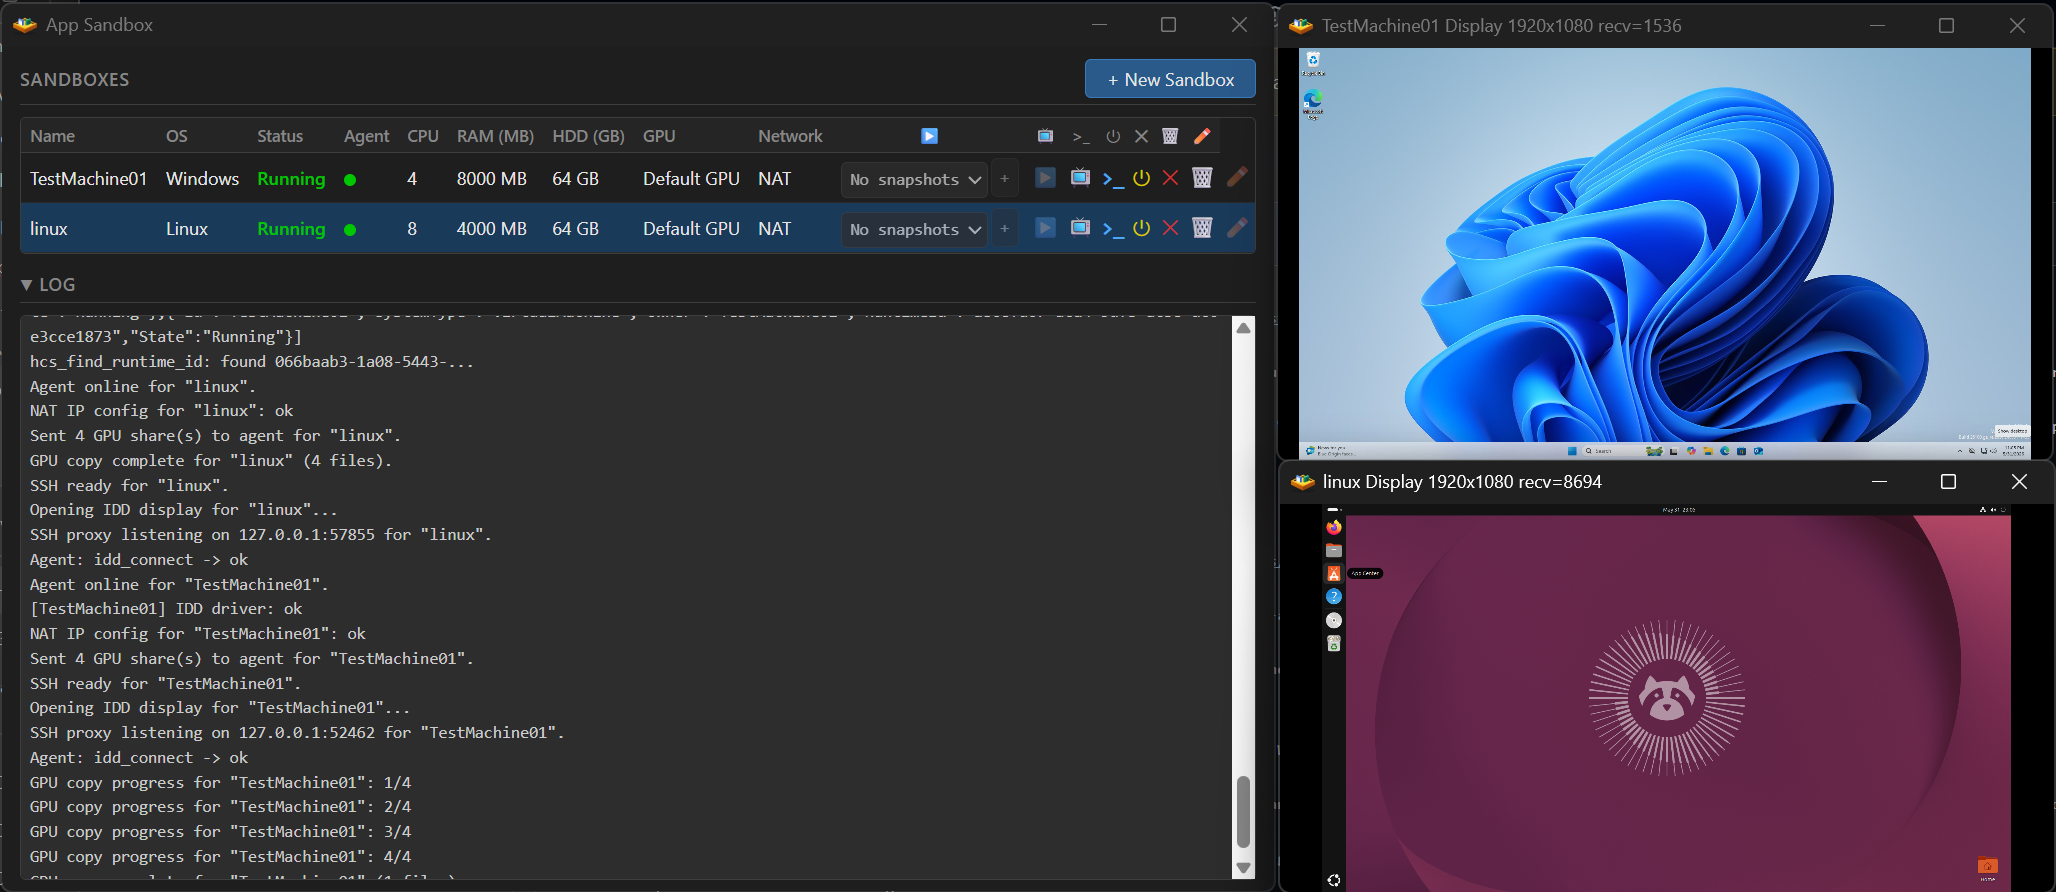 jamesstringer90/appsandbox
Easily create full virtual machines that are sandboxed for development or computer use models.
 security-onion-solutions/securityonion
Open-source security monitoring platform for threat hunting, intrusion detection, log management, incident response, and endpoint visibility with…
 xyrem/hyperdeceit
HyperDeceit is the ultimate all-in-one library that emulates Hyper-V for Windows, giving you the ability to intercept and manipulate operating system…
 cisagov/vulnrichment
A repo to conduct vulnerability enrichment.
 finbarr/yolobox
Let your AI go full send. Your home directory stays home.
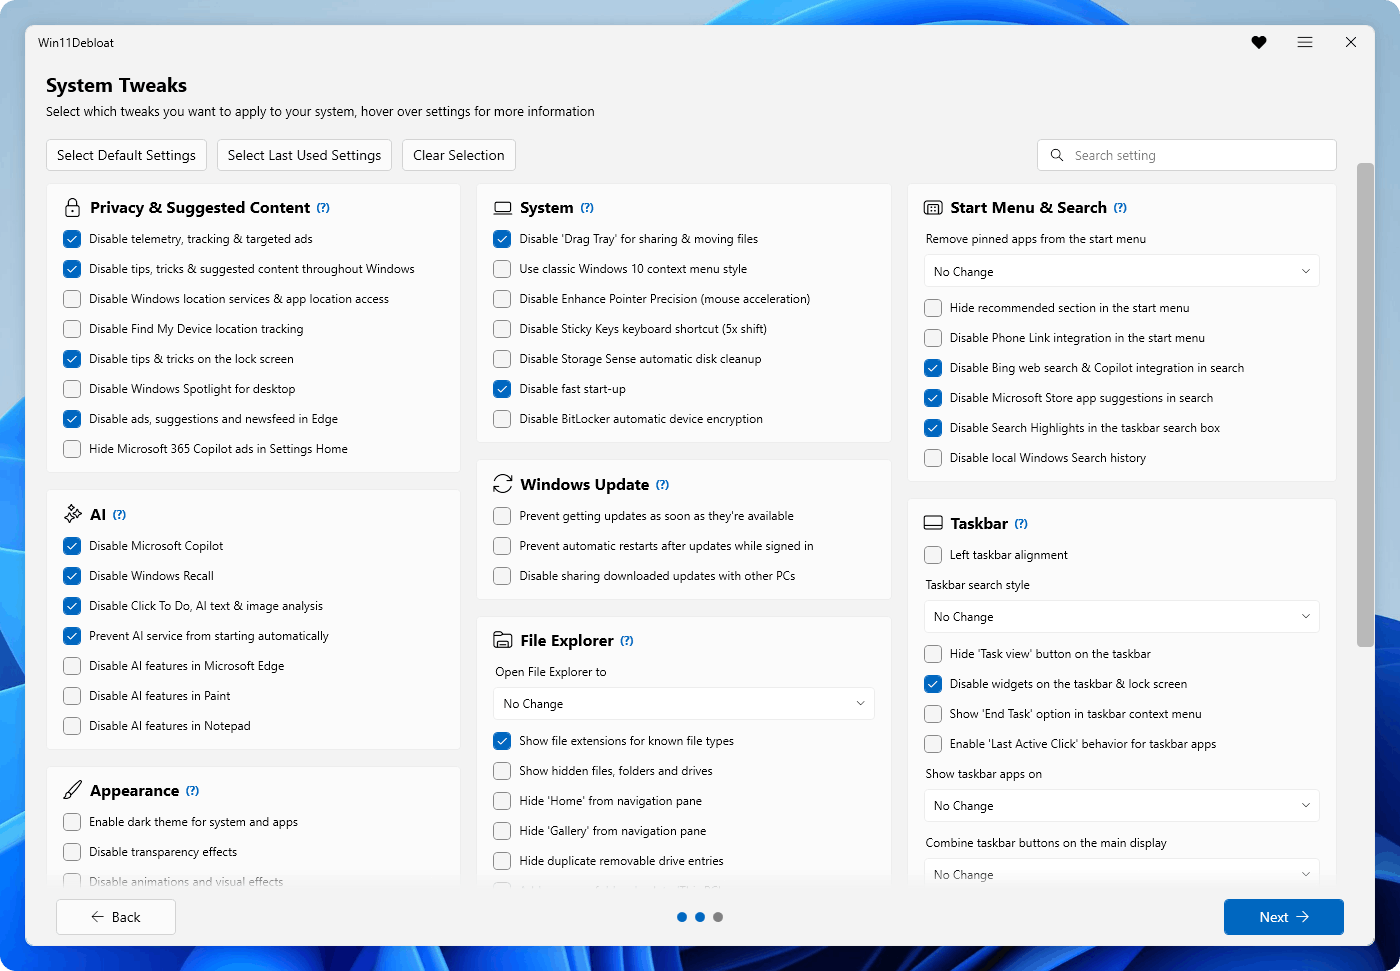 raphire/win11debloat
A simple, lightweight PowerShell script that allows you to remove pre-installed apps, disable telemetry, as well as perform various other changes to…
 firecracker-microvm/firecracker
Secure and fast microVMs for serverless computing.
 qemu/qemu
Official QEMU mirror. Please see https://www.qemu.org/contribute/ for how to submit changes to QEMU. Pull Requests are disabled. Please only use…
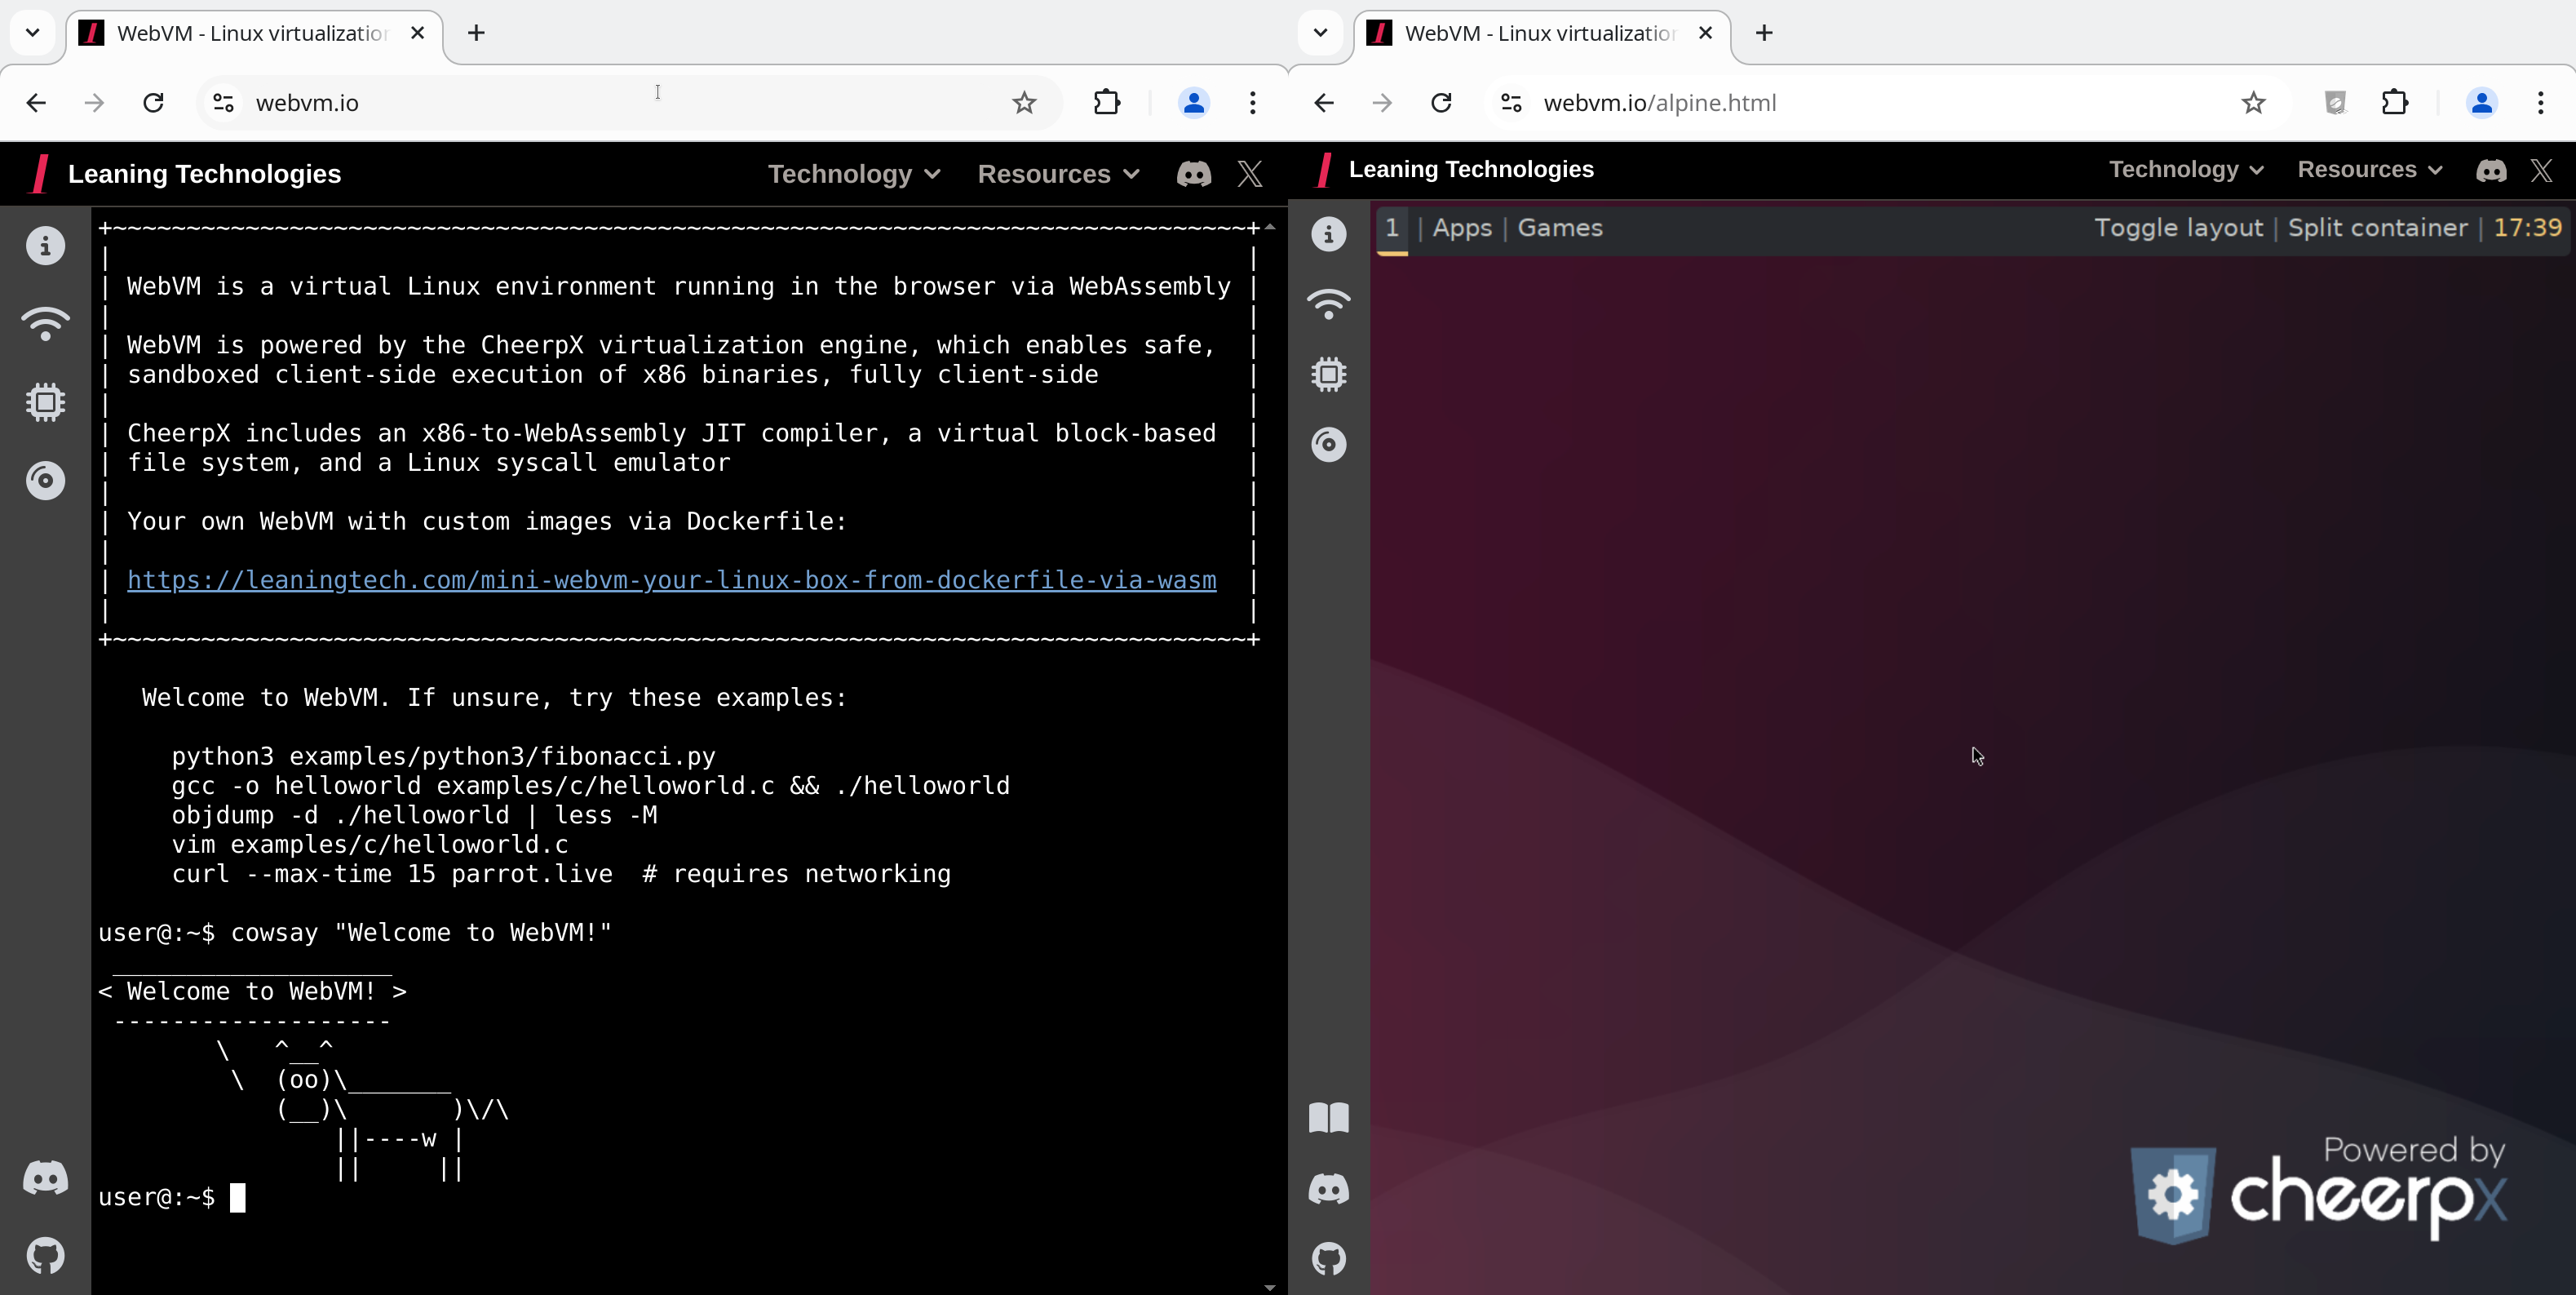 leaningtech/webvm
Client-side Linux virtual machine running in the browser via WebAssembly, with Tailscale networking, Dockerfile-based custom images, and CTF…
 nvidia/openshell
Sandboxed runtime for autonomous AI agents with declarative YAML policies enforcing filesystem, network, and process constraints, plus endpoint-bound…
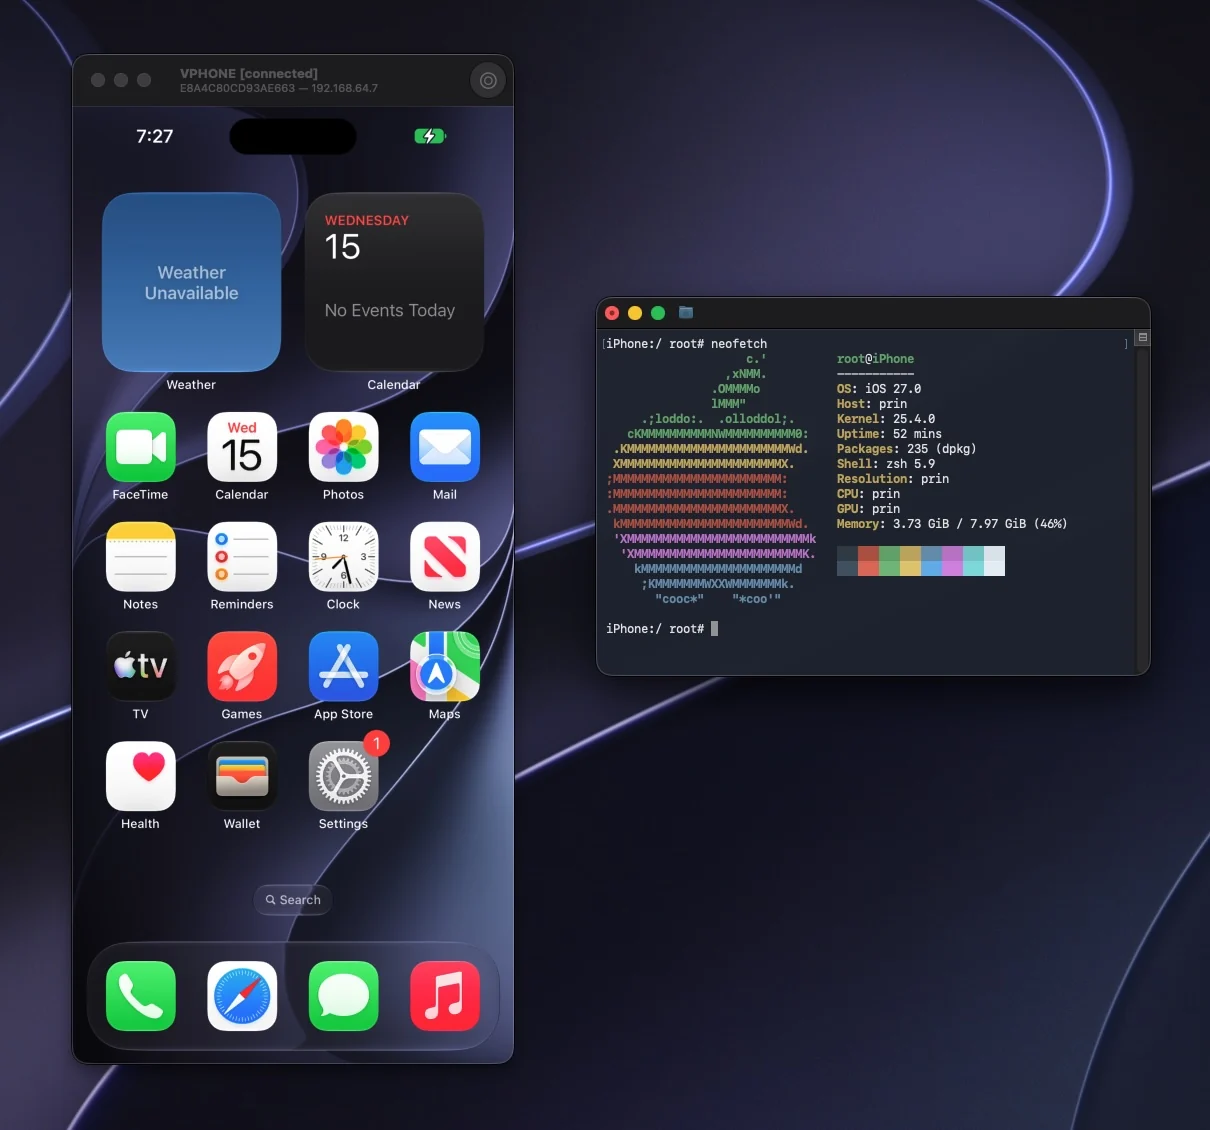 lakr233/vphone-cli
Boot and manage virtual iPhones on Apple Silicon with firmware patching, jailbreak variants, and security research features for iOS testing and…
 mandiant/flare-vm
A collection of software installations scripts for Windows systems that allows you to easily setup and maintain a reverse engineering environment on…
 mandiant/commando-vm
Customizable Windows-based virtual machine distribution pre-packaged with offensive security tools for penetration testing and red teaming operations.
 anthropic-experimental/sandbox-runtime
A lightweight sandboxing tool for enforcing filesystem and network restrictions on arbitrary processes at the OS level, without requiring a container.
 boltgolt/howdy
🛡️ Windows Hello™ style facial authentication for Linux
 dosx-dev/obfus.h
Macro-header for compile-time C polymorphic obfuscation (tcc, win x86/x64)