redStackPRO
A canvas for red team infrastructure and cyber ranges. Compose a topology, export runnable Terraform and Ansible, and deploy it yourself. Your cloud…

A canvas for red team infrastructure and cyber ranges. Compose a topology, export runnable Terraform and Ansible, and deploy it yourself. Your cloud…

A simple, lightweight PowerShell script that allows you to remove pre-installed apps, disable telemetry, as well as perform various other changes to…

Linux namespaces and seccomp-bpf sandbox

Offline and security-first tool for syncing and managing agent skills

Rootless container runtime and sandbox that launches kernel-enforced OCI images in milliseconds with no daemon, featuring resource profiles, seccomp…

Sandboxes containers via a userspace application kernel that intercepts system calls, limits host kernel access, and integrates with…

Azure workbook dashboard that visualizes and explores detection performance metrics, helping security teams measure and proactively maintain their…

Manage OpenClaw in your team (Enterprise) by providing it compute infrastructure, tool integration, Authentication and security primitives

Pre-Built Vulnerable Environments Based on Docker-Compose

A PS5 hypervisor exploit for 1.xx-2xx firmwares.

Deliberately vulnerable Docker lab with a routable DNS estate and machine-readable answer keys per target, scoring scanner precision, recall and…

Low-level unprivileged sandboxing tool used by Flatpak and similar projects

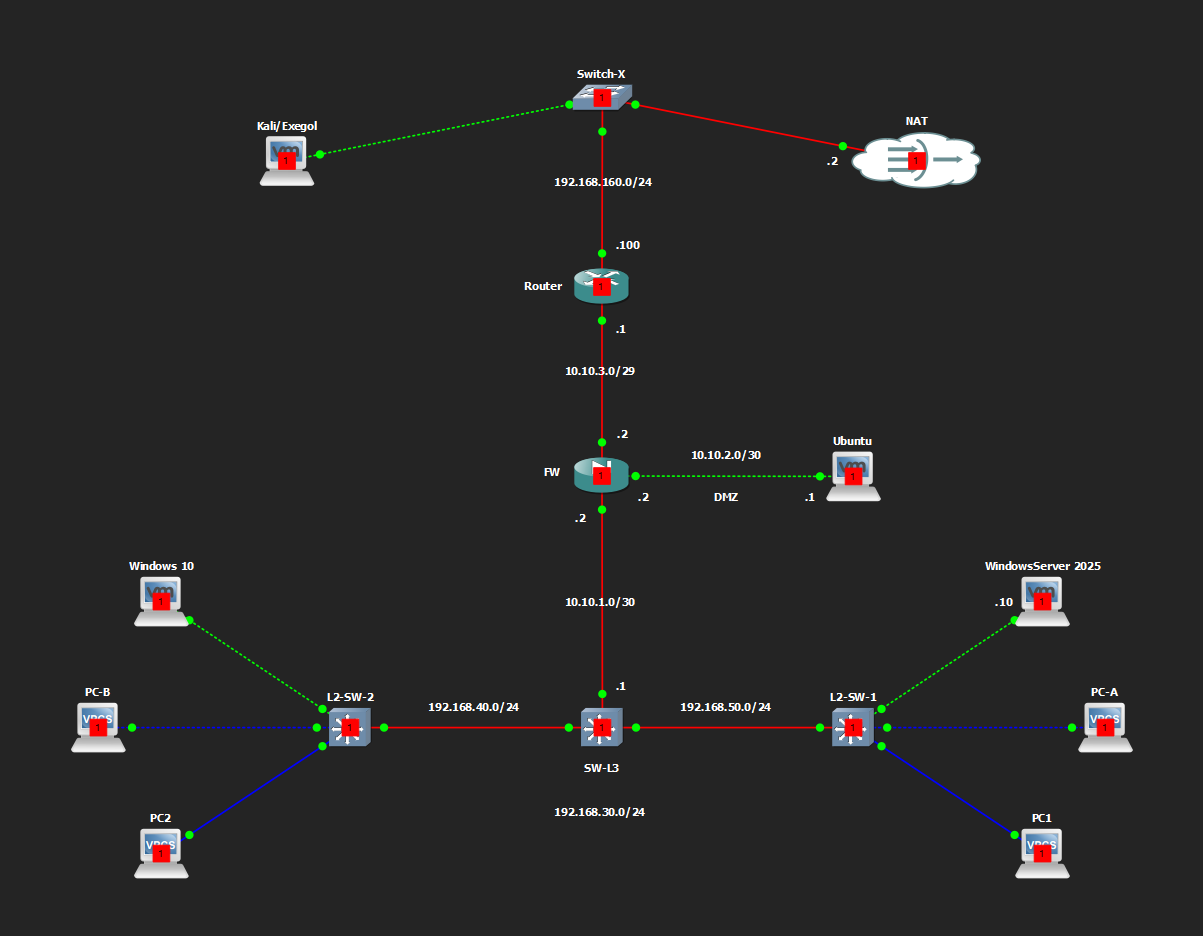
GNS3 home lab documenting a segmented network with Cisco ASAv firewall, L3 core, DMZ, and an Active Directory domain for practicing networking,…

Sandboxed Execution Environment

Kernel-level eBPF sandbox for securing LLM agent tool calls made through the Model Context Protocol (MCP)

Sandbox untrusted code with safe access to the host.

The research UEFI hypervisor that supports booting an operating system.

Multi-cloud security auditing tool that leverages cloud provider APIs to gather configuration data, assess security posture, and generate HTML…