
rusty-hog
 newrelic/rusty-hog
Multi-source secret scanner detecting API keys, passwords, and PII across Git repos, S3 buckets, filesystems, Confluence, JIRA, Slack, and Google…
cloud-securitycode-analysisdevsecops+1
555
newrelic/rusty-hogMulti-source secret scanner detecting API keys, passwords, and PII across Git repos, S3 buckets, filesystems, Confluence, JIRA, Slack, and Google…
 corgea/sighthound
Tree-sitter based static vulnerability scanner with pattern matching and taint-flow analysis for multi-language source code. Outputs findings as…
 sourcecode-ai/aura
Python source code auditing and static analysis on a large scale
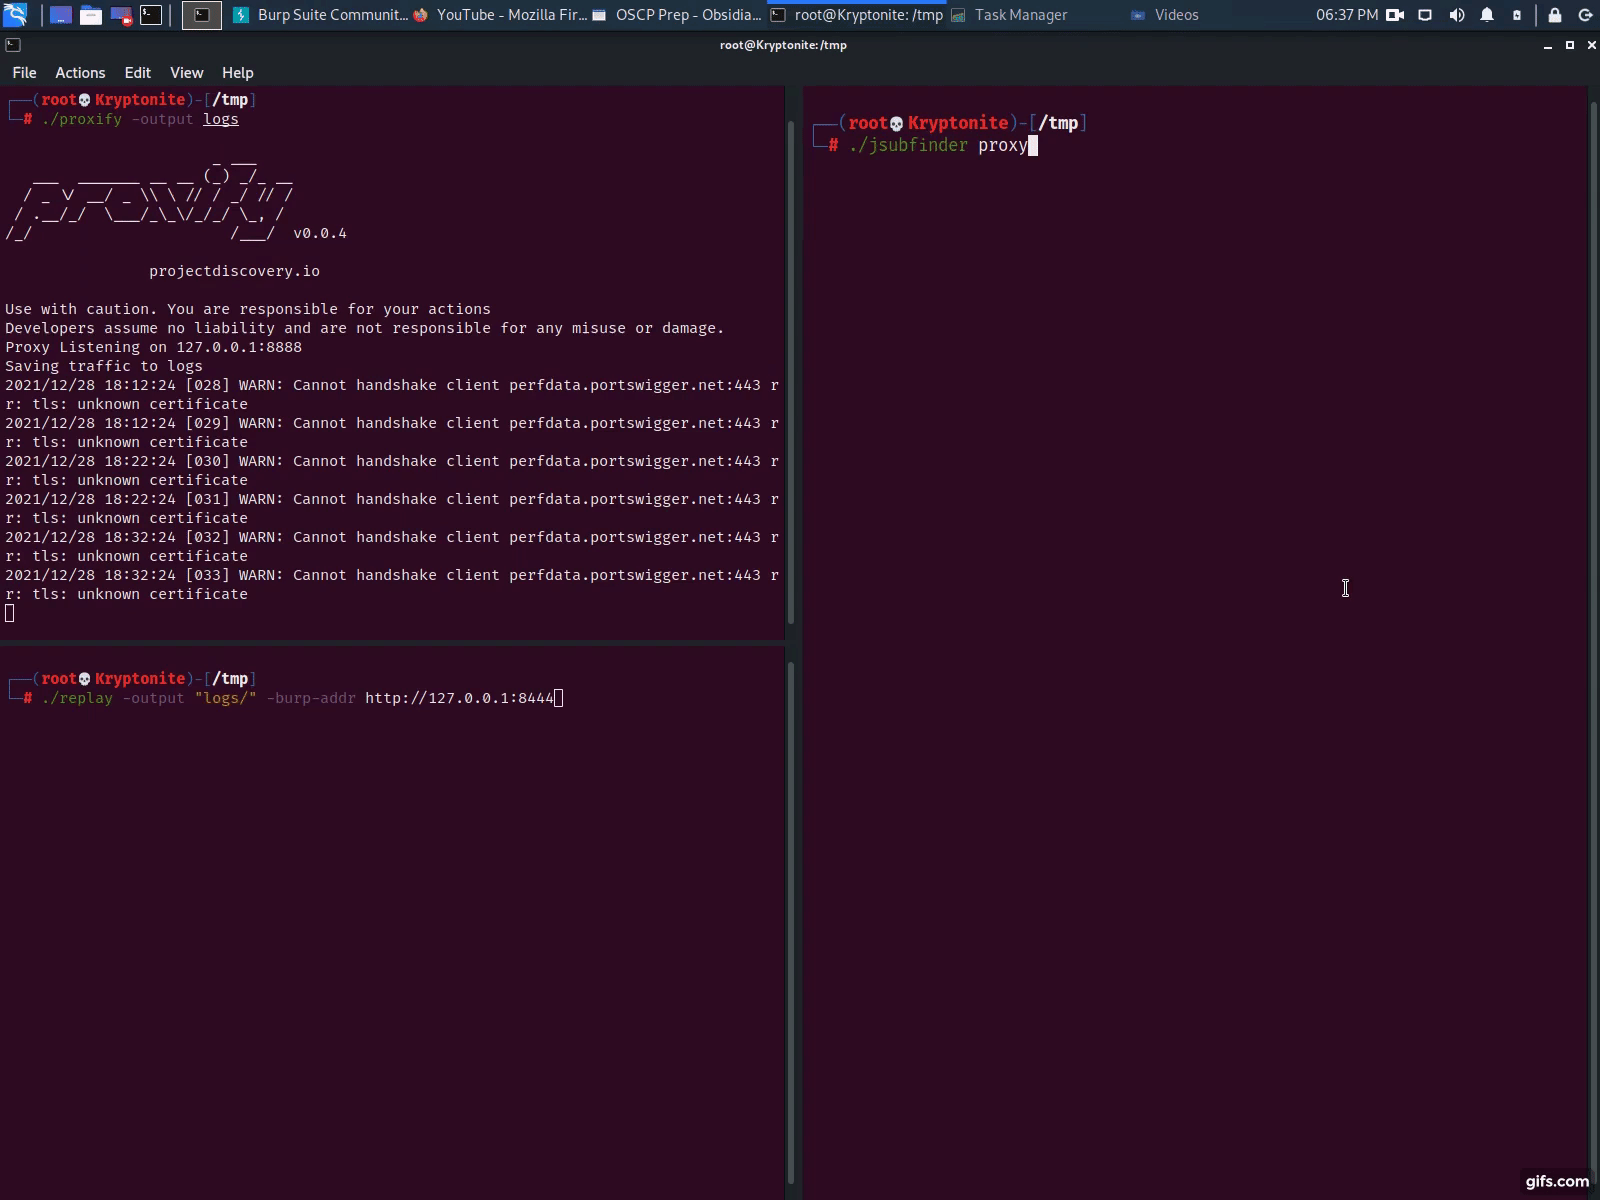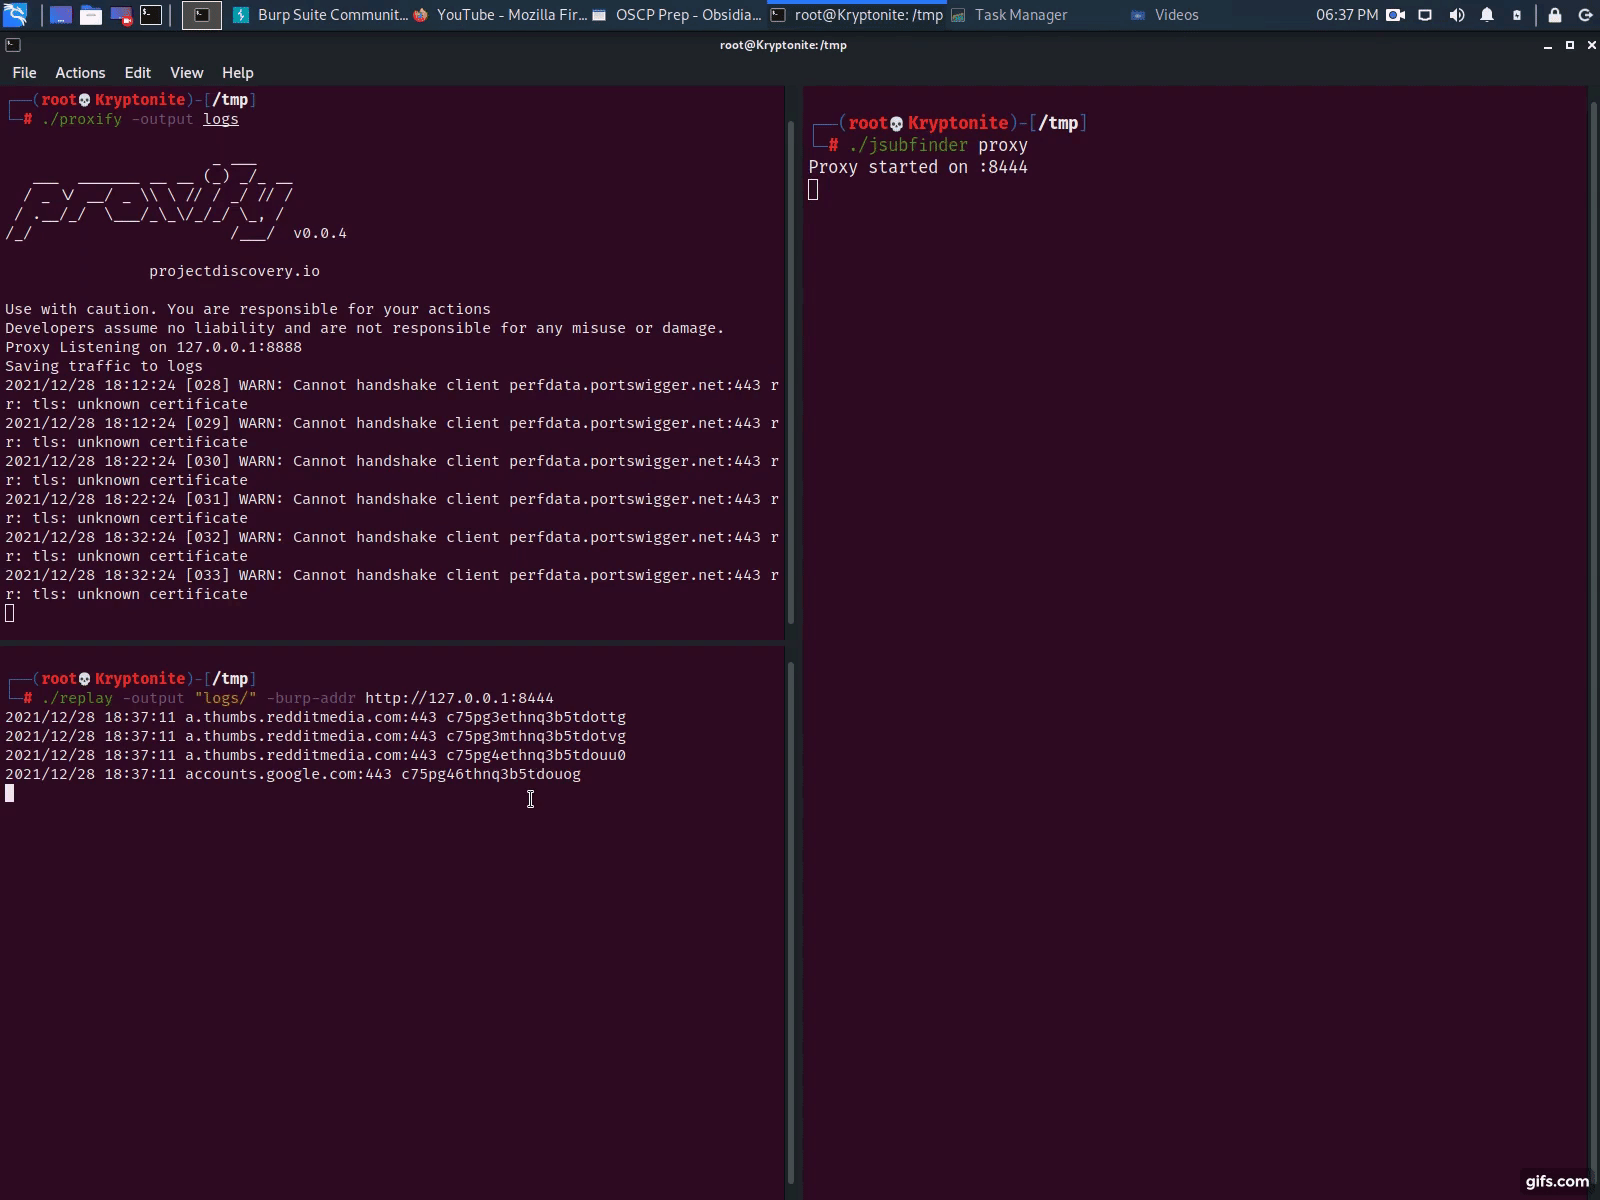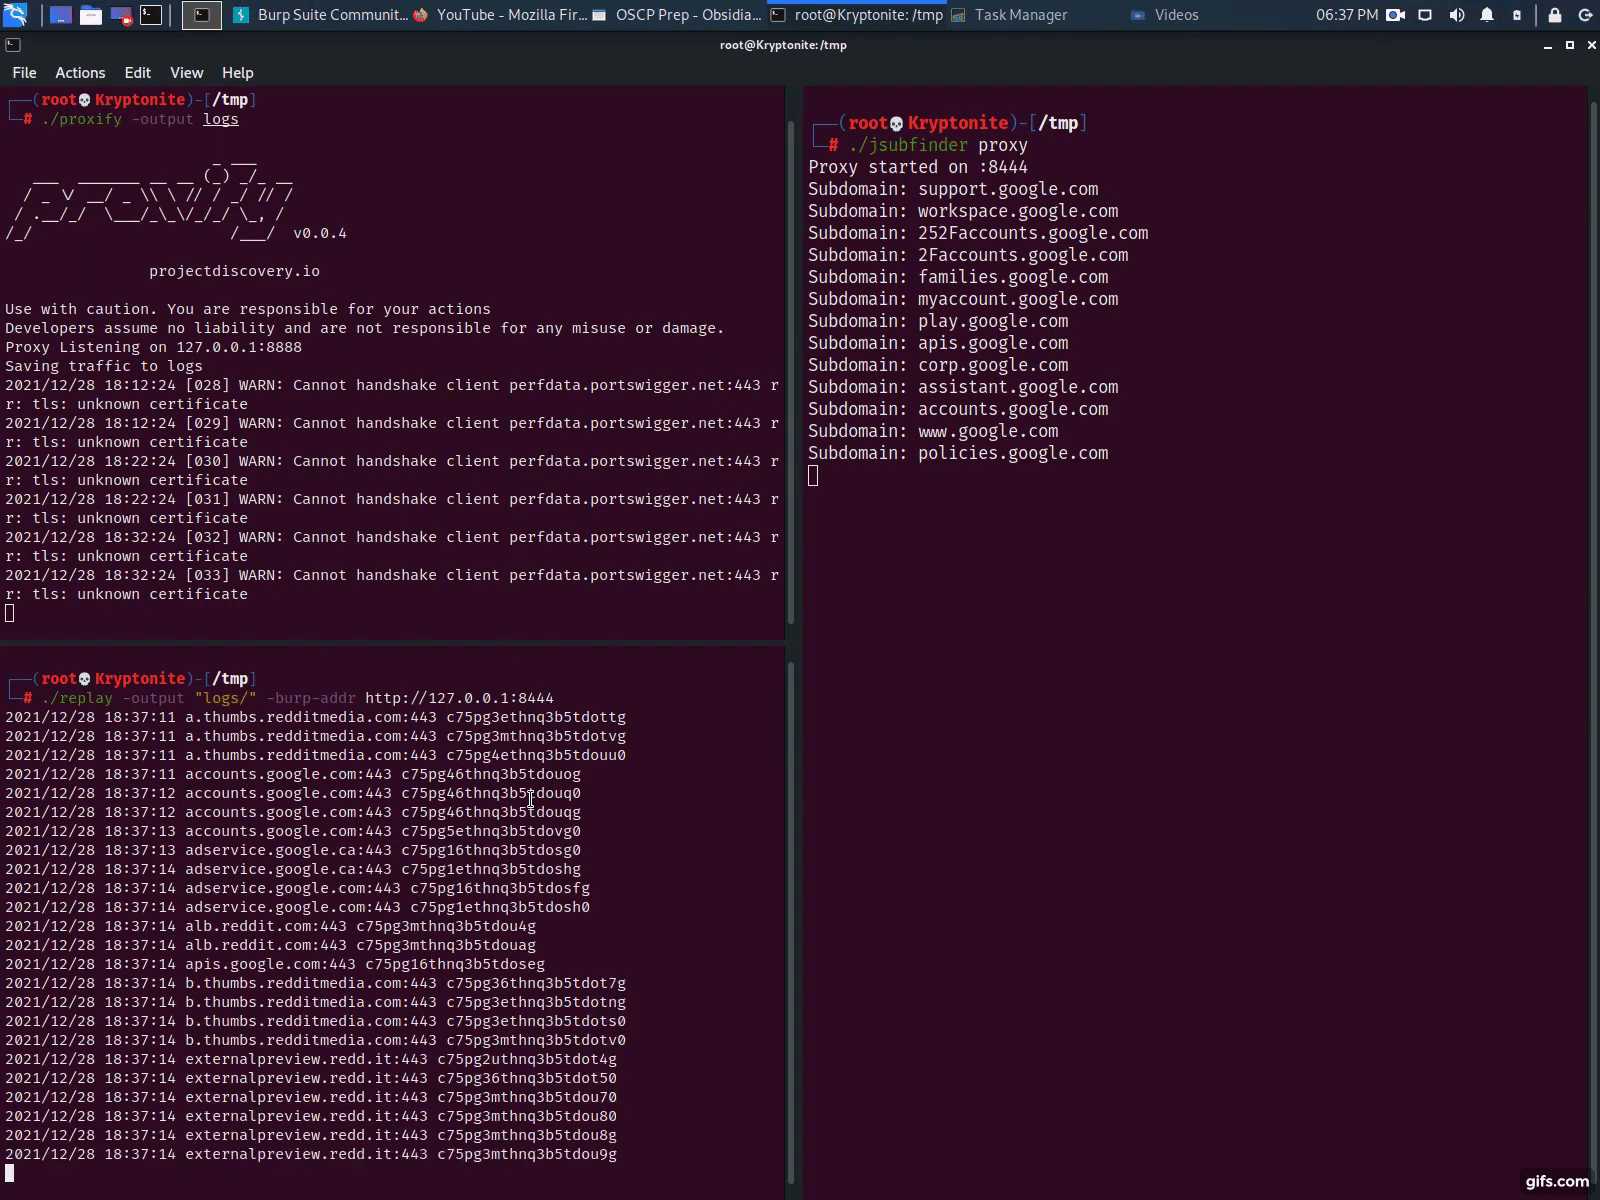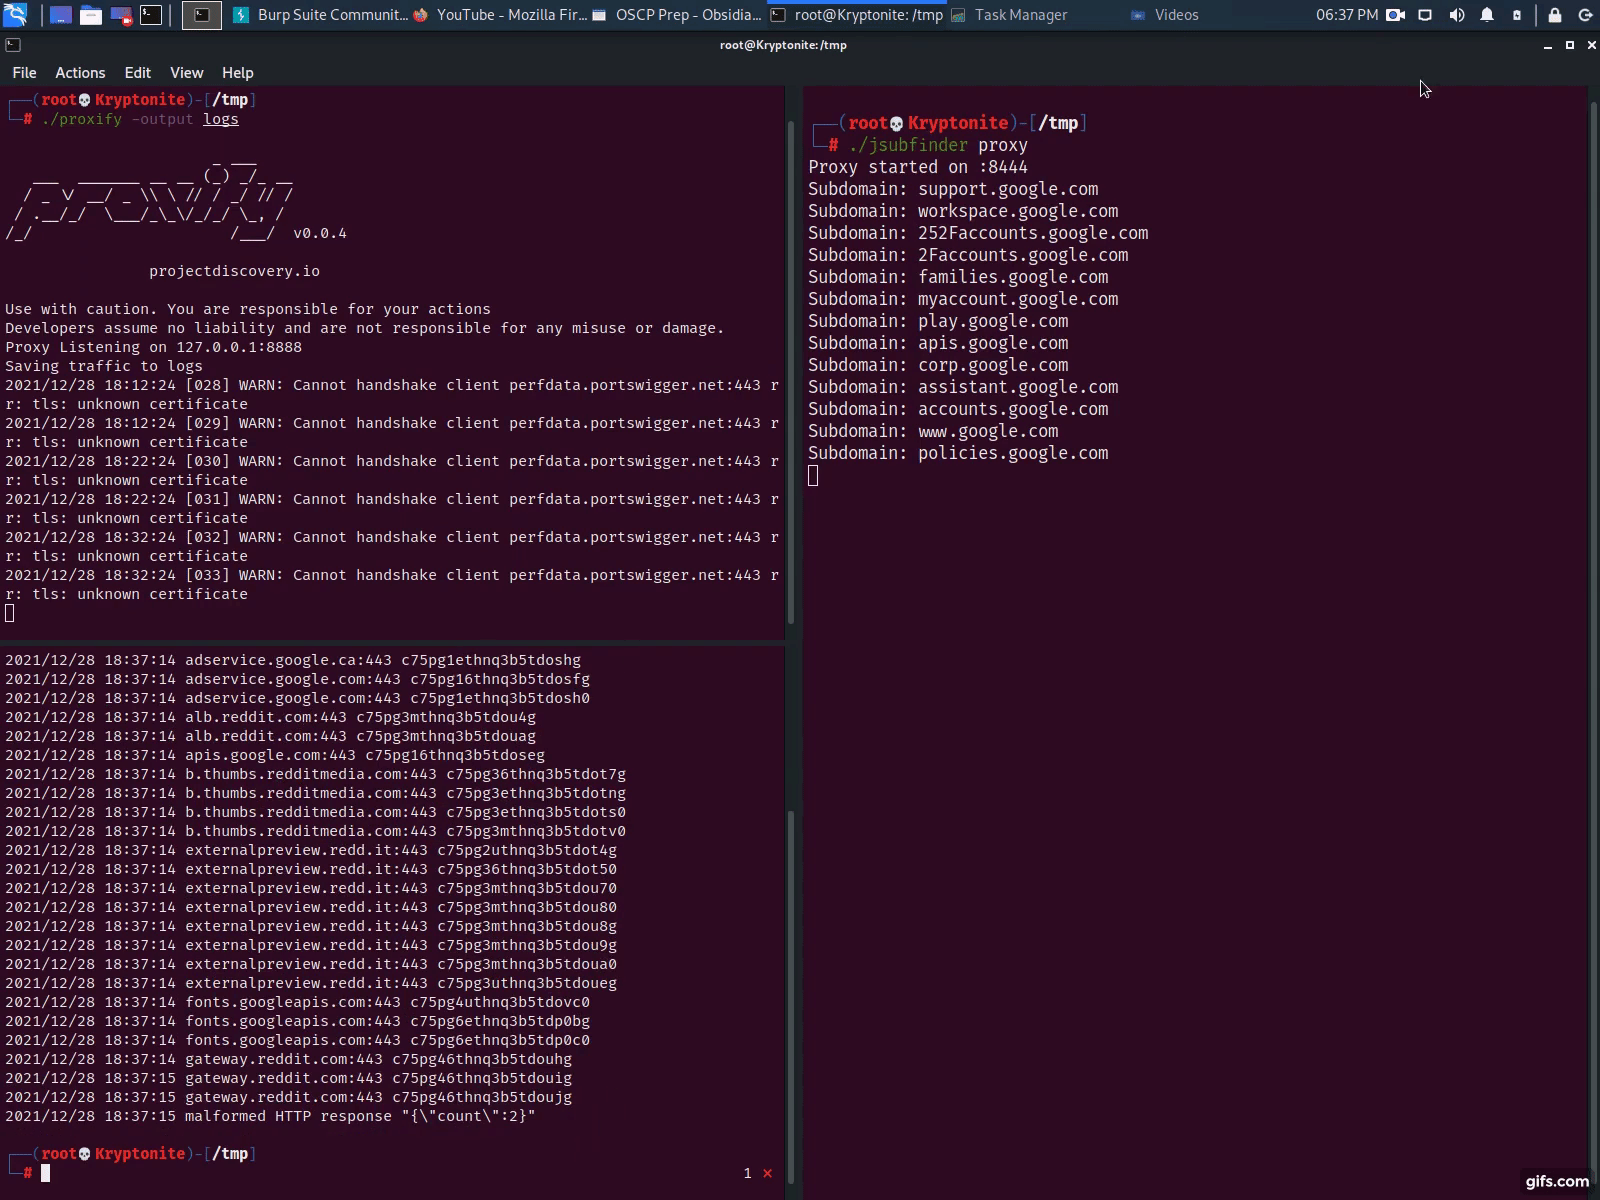 threatunknown/jsubfinder
Go-based tool that scans webpages and JavaScript files to discover hidden subdomains and secrets, with optional crawling and real-time proxy analysis…
 jayu/rev-dep
Dependency analysis and optimization toolkit for modern JavaScript and TypeScript codebases. Enforce dependency graph hygiene and remove unused code…
 pii-shield/pii-shield
Zero-code K8s sidecar for log sanitization. Detects secrets via Entropy Analysis, preserves JSON integrity, and redacts PII deterministically. 🛡️
 ntoskernel/deepsecrets
Offline secrets scanner combining regex rules, lexer-based semantic analysis, and hashed-value matching to detect exposed credentials in code with…
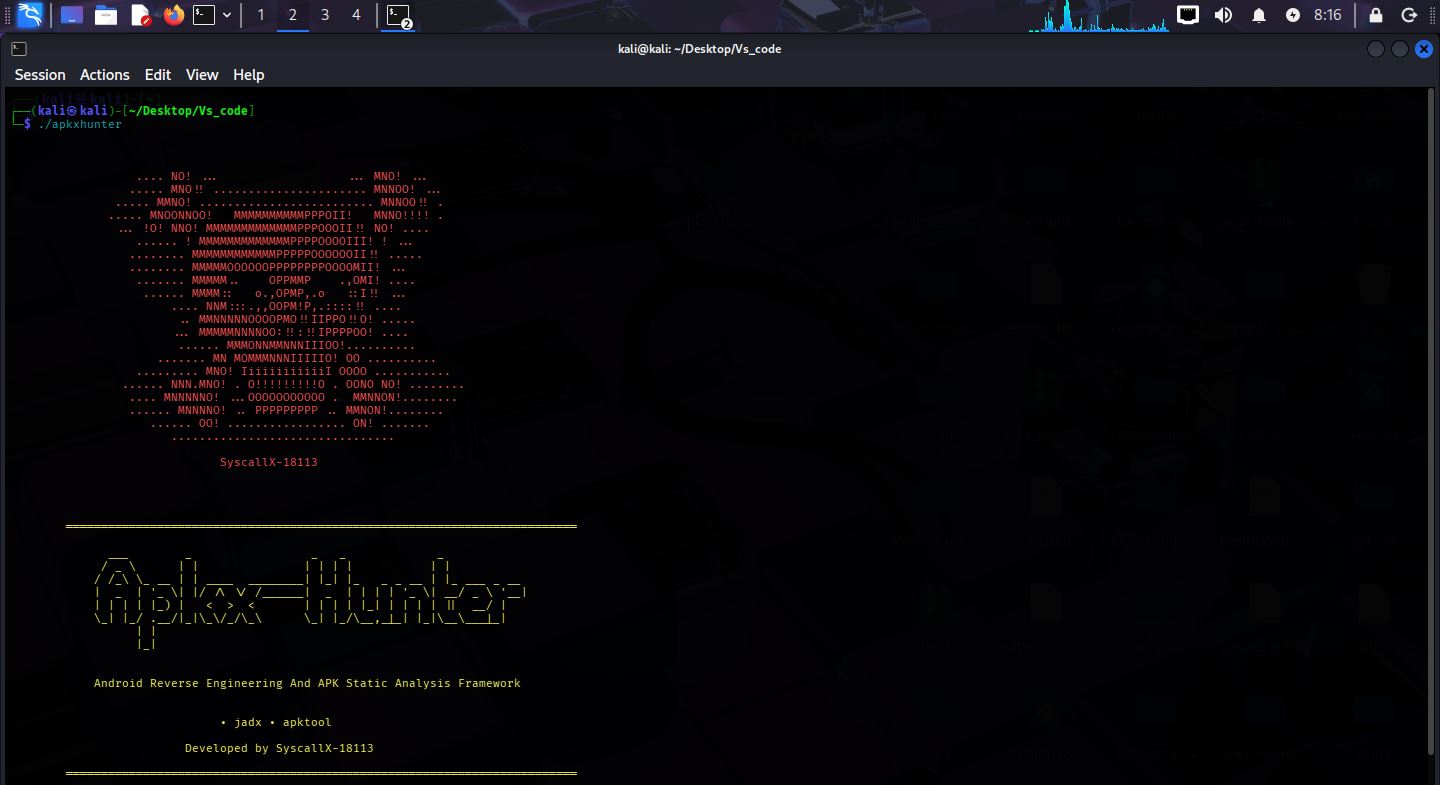 syscallx-18113/apkx-hunter
C-based Android static analysis framework for decompilation, secret detection, endpoint discovery, permission analysis, and native library scanning…
 nuguardai/nuguard
opensource repo for validating agentic AI applications: redteam, behavior, supply-chain, static analysis
 avito-tech/deepsecrets
Static analysis tool that scans source code for hardcoded secrets, API keys, and credentials using semantic understanding of code context.
 mcp-shark/mcp-shark
Wireshark-like forensic analysis for Model Context Protocol communications Capture, inspect, and investigate all HTTP requests and responses between…
 arsbr/veritensor
The Anti-Virus for AI Artifacts & RAG Firewall. A static analysis tool scanning Models and Notebooks for RCE, Datasets and RAG docs for Data…
 adamsjack711-ux/pkgxray
Pre-install security for AI agents, npm packages, and MCP servers. Zero-dep local static analysis; normal scans never execute package code.
 dnszlsk/muad-dib
Real-time npm/PyPI supply-chain threat detection. Behavioral chain analysis, AST scanning, IOC feeds, and compound scoring engine.
 otsmane-ahmed/ci-supplychain-guard
Static analysis tool that detects malicious dependencies in CI/CD pipelines using pattern matching and AST analysis, with a traffic-light risk…
 ny1024/clawguard
Modular security toolkit for autonomous agents providing static analysis, configuration auditing, runtime monitoring, and supply chain verification…
 stuxctf/slythestx
Mobile app security auditing tool focused on automating SAST analysis, identifying underlying technologies (React Native, Flutter, Xamarin, native),…
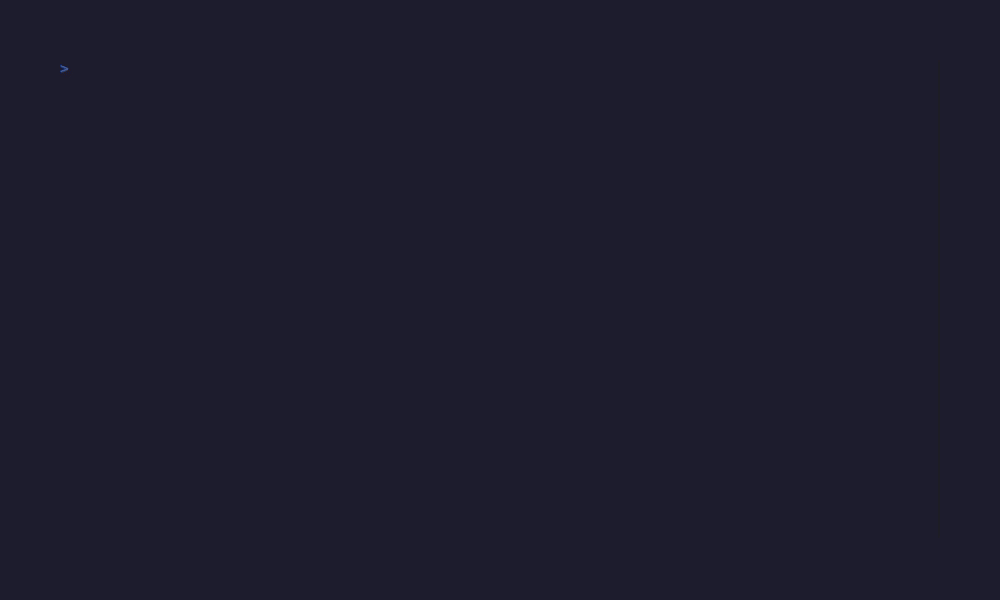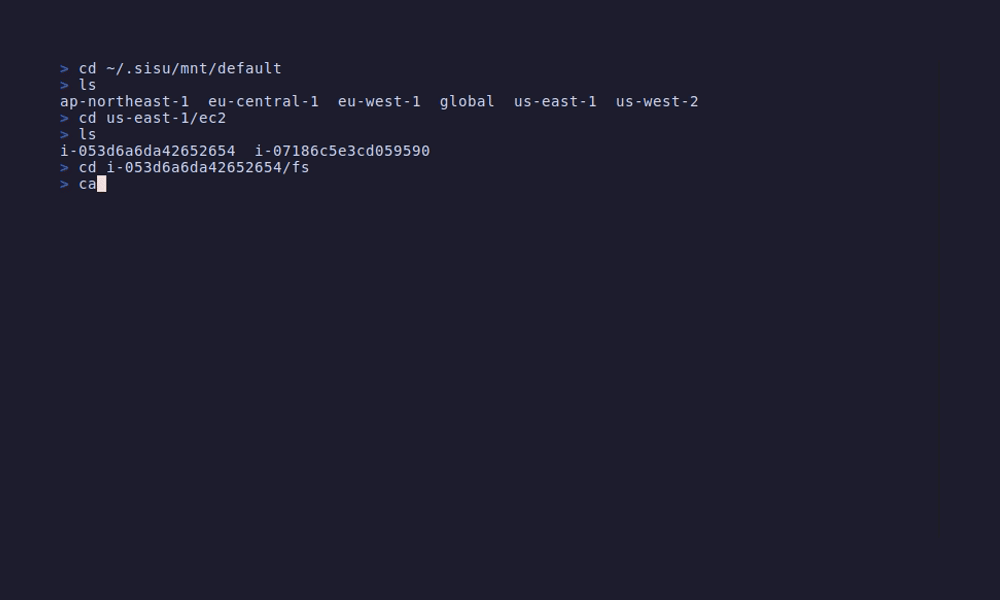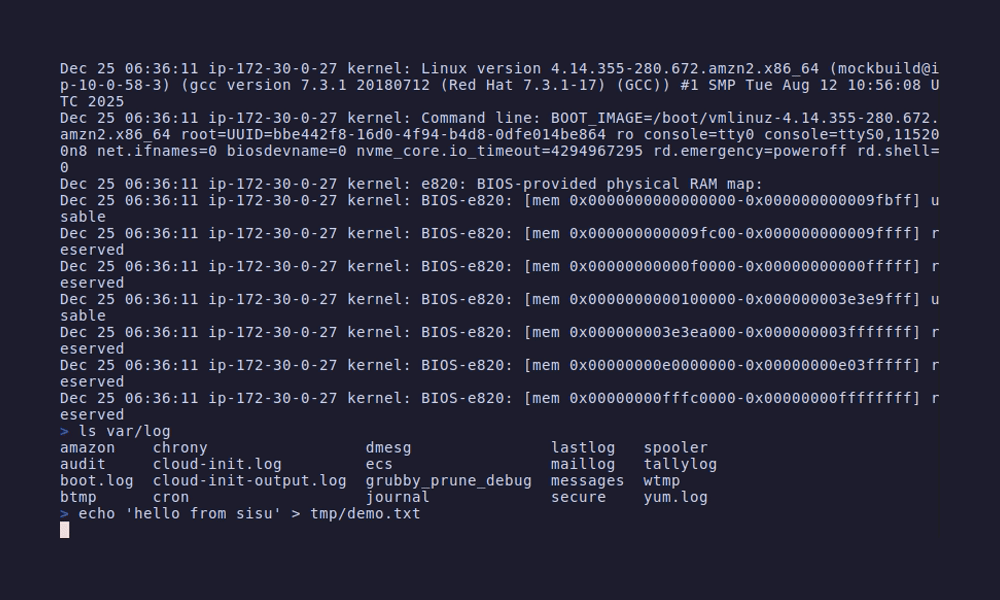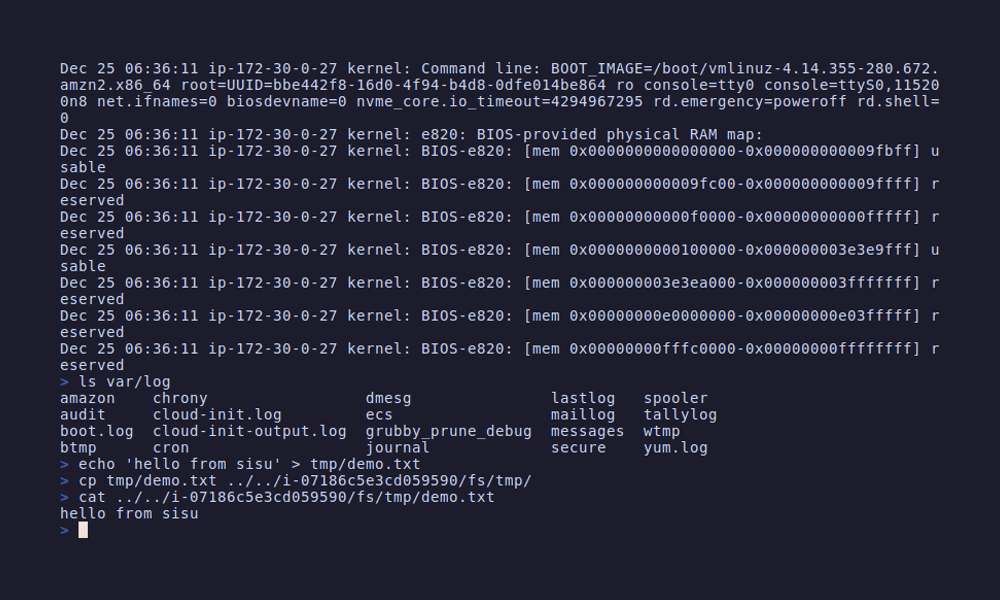 semonte/sisu
Mounts AWS resources as a local filesystem for infrastructure exploration, security auditing, and configuration analysis using standard Unix tools…