

bromure
 rderaison/bromure
Proper sandboxing for agentic coding and web browsing
ai-securitycontainer-securitydynamic-analysis-sandboxing+6
rderaison/bromureProper sandboxing for agentic coding and web browsing
 trufflesecurity/trufflehog
Find, verify, and analyze leaked credentials
 hashgraph-online/hol-guard
Open-source antivirus for AI agents: block risky tools, secret access, prompt injection, malicious packages, MCP servers, plugins, and skills at…
 navikt/cplt
Sandbox for AI coding agents. Runs Copilot CLI, Claude Code, OpenCode, Gemini CLI, Antigravity, Pi, goose or a plain shell inside a kernel-level…
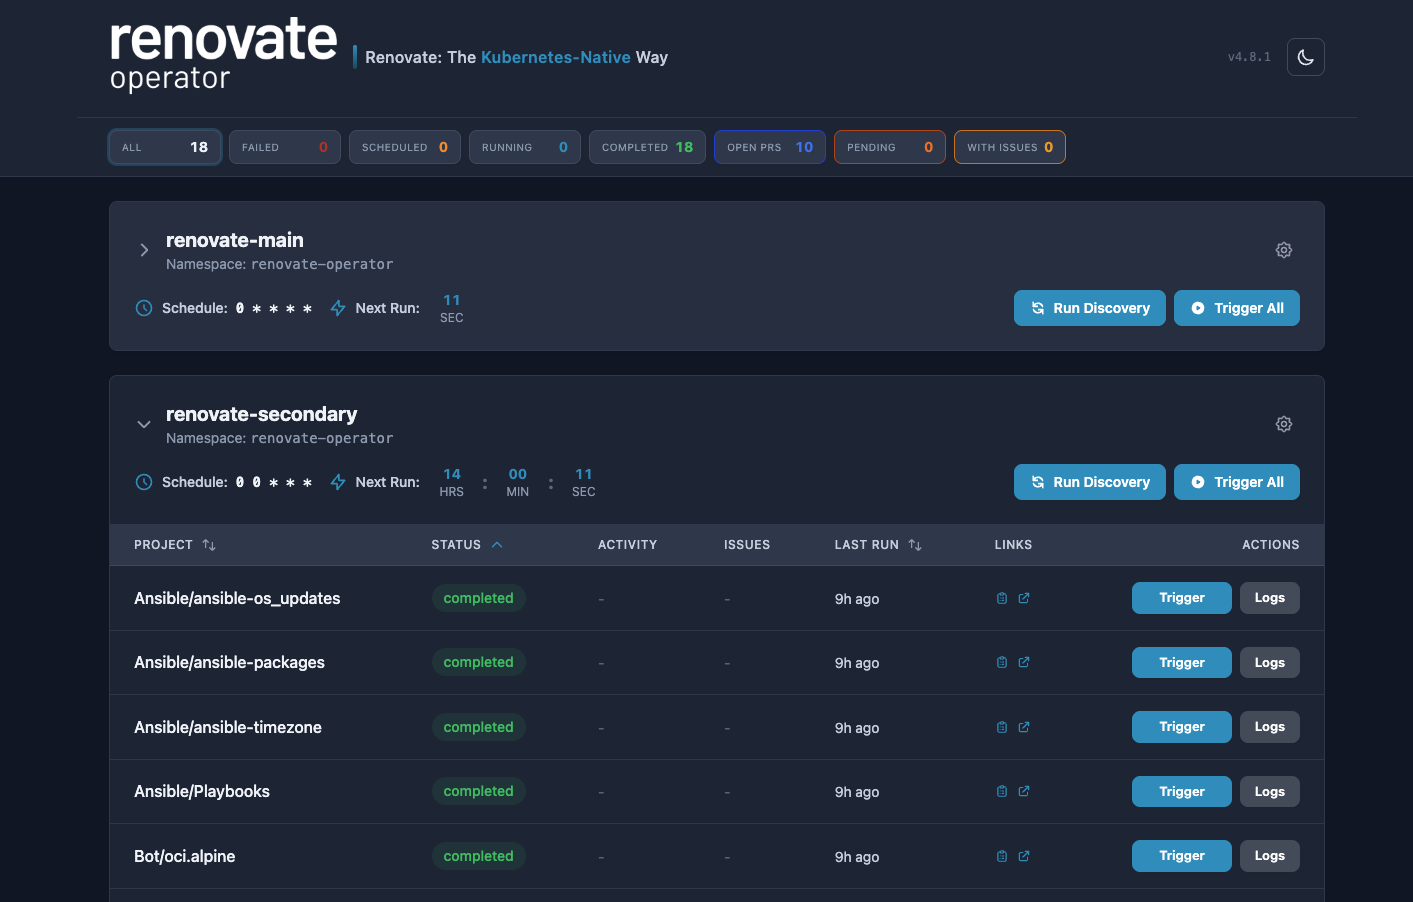 mogenius/renovate-operator
Operator to streamline renovate executions in Kubernetes
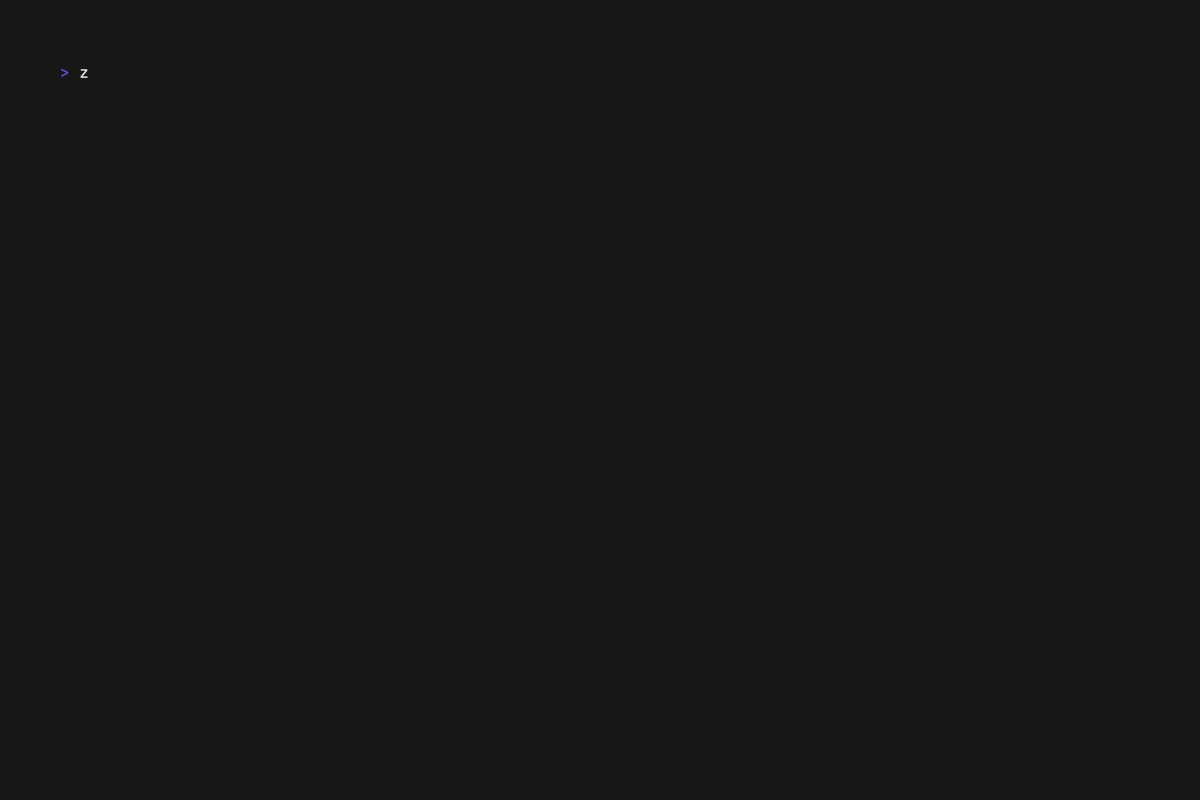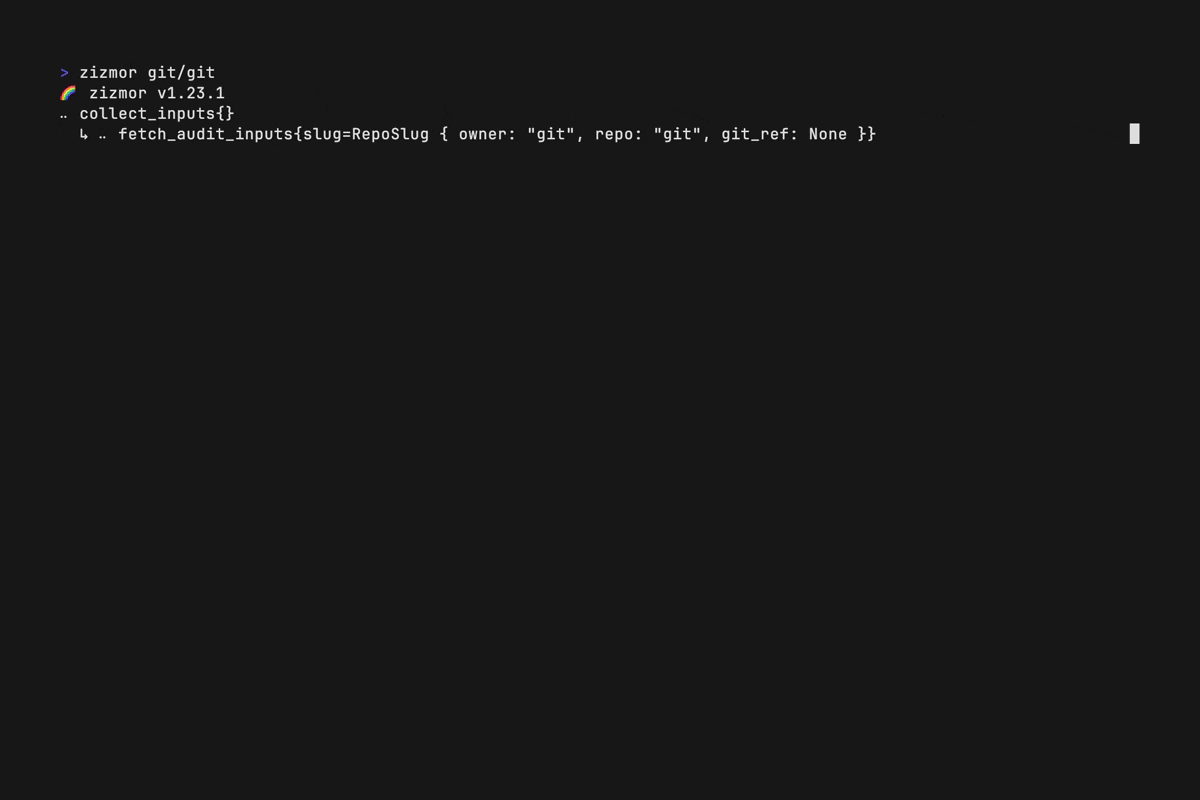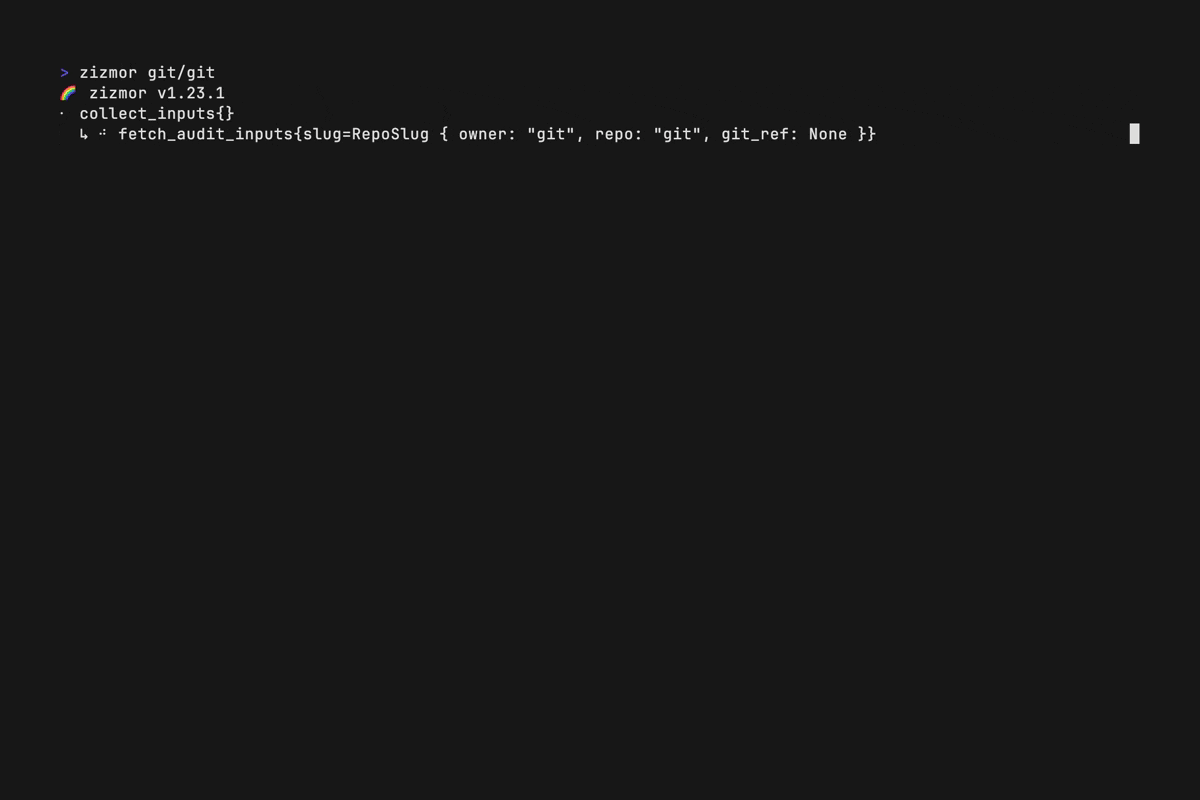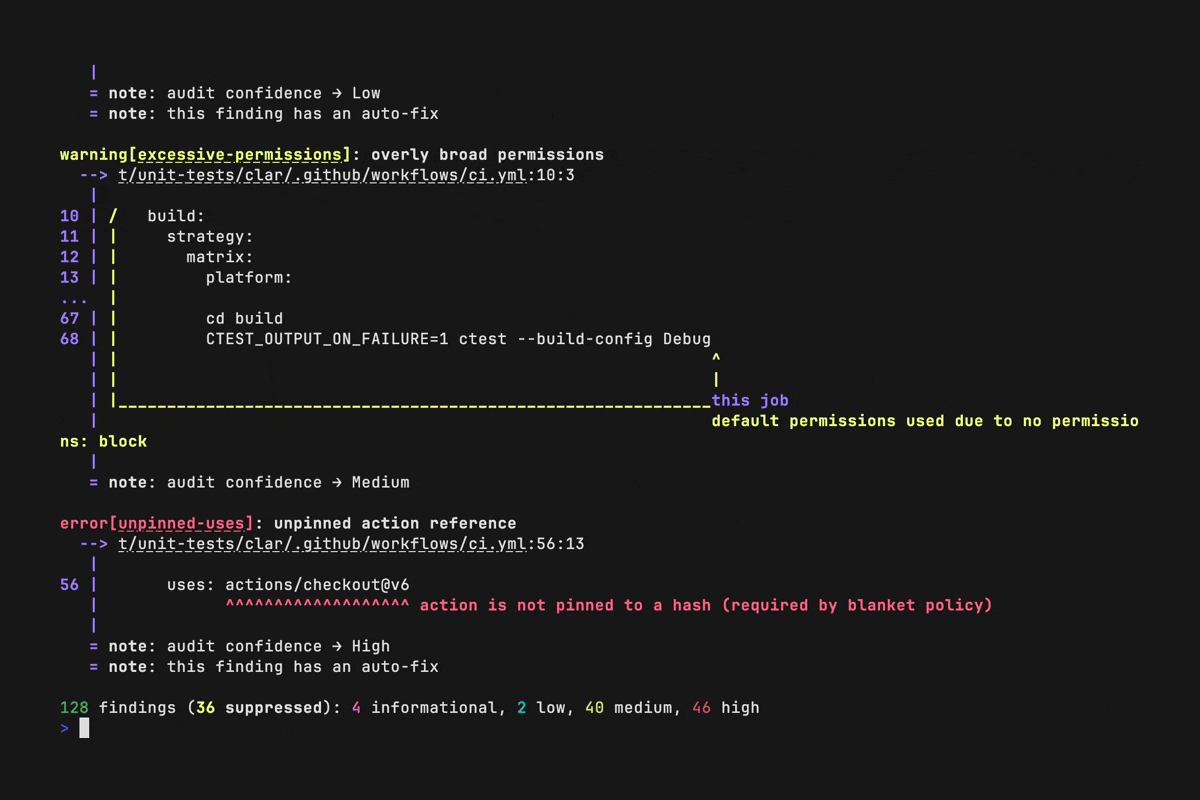 zizmorcore/zizmor
Static analysis tool for CI/CD systems that detects and fixes security issues in GitHub Actions, Dependabot, and pre-commit configurations, including…
 msaad00/agent-bom
AI supply-chain BOM: every agent, MCP server and AI package, and what each one can reach. Open-source scanner and self-hosted control plane for code,…
 prismorsec/prismor
Self-hosted runtime control plane for AI agents. Observe or HITL approve or Block rogue tool calls before it executes: secret leaks, prompt…
 preflightsh/preflight
Go-based CLI tool that scans codebases for launch readiness, detecting missing configuration, security hygiene issues, secret leaks, and integration…
 mindersec/minder
Software Supply Chain Security Platform
 secretlint/secretlint
Pluggable linting tool to prevent committing credential.
 google/osv-scanner
Vulnerability scanner written in Go which uses the data provided by https://osv.dev
 ariesq/gh-safe-repo
Python CLI that creates GitHub repos with safe defaults — branch protection, Dependabot, secret scanning, and pre-flight security scanning — applied…
 praetorian-inc/titus
High-performance secrets scanner. CLI, Go library, Burp Suite extension, and Chrome extension. 487 detection rules with live credential validation.
 ossf/scorecard
OpenSSF Scorecard - Security health metrics for Open Source
 9pings/fad-checker
Buildless dependency auditor that scans 10 ecosystems offline, reporting CVEs prioritized by CISA KEV and EPSS, EOL packages, licenses, committed…
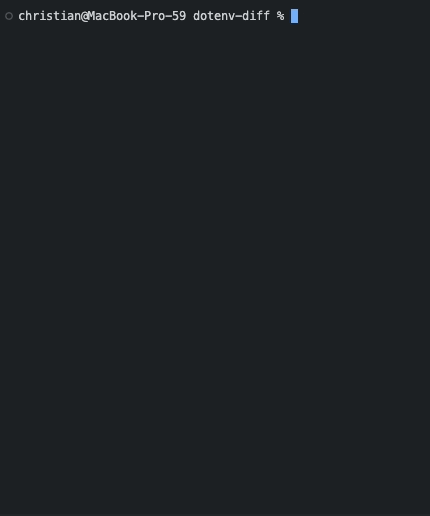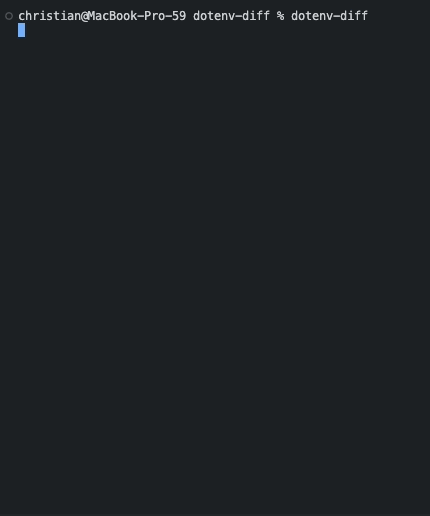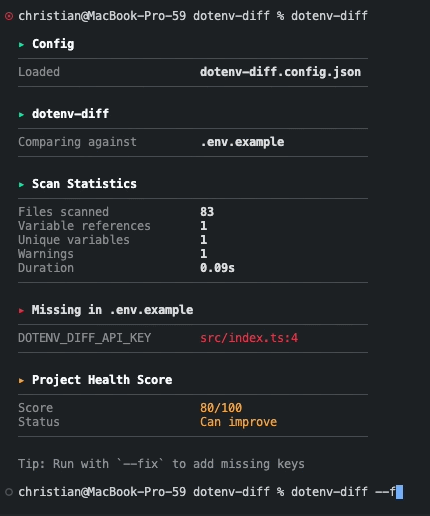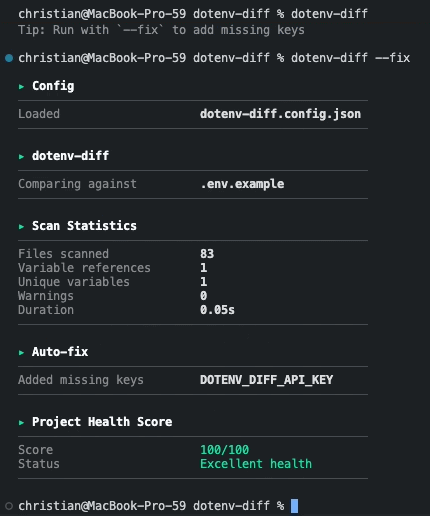 chrilleweb/dotenv-diff
Validate environment variable usage in codebase
 gitguardian/ggshield
Detect and validate 500+ types of hardcoded secrets with advanced checks. Use it as a pre-commit hook, GitHub Action, or CLI for proactive secret…