TriSuElla-AIDLCA-Framework

Policy-governed LLMSecOps framework providing AST-based SAST, secret scanning, supply-chain and multi-cloud CSPM checks, AI-BoM generation, and CI/CD…

Policy-governed LLMSecOps framework providing AST-based SAST, secret scanning, supply-chain and multi-cloud CSPM checks, AI-BoM generation, and CI/CD…

Interactive secure coding training with hands-on SCORM exercises covering OWASP Top 10 web and API vulnerabilities, Git/secrets exposure, and…

jsluice++ is a Burp Suite extension designed for passive and active scanning of JavaScript traffic using the CLI tool jsluice

The independent security agent for AI-written software. Finds issues, investigates whether they are real, and shows you the evidence. Deterministic…

Scans public code repositories and code snippet platforms to extract and validate AI service API keys with real-time dashboard and multi-format…

Vulnerability Assessment Scanner with Report Generation

SEDATED® Project (Sensitive Enterprise Data Analyzer To Eliminate Disclosure)

Source code for the Binaries of OWASP WrongSecrets

OWASP Secure Agent Playbook Project

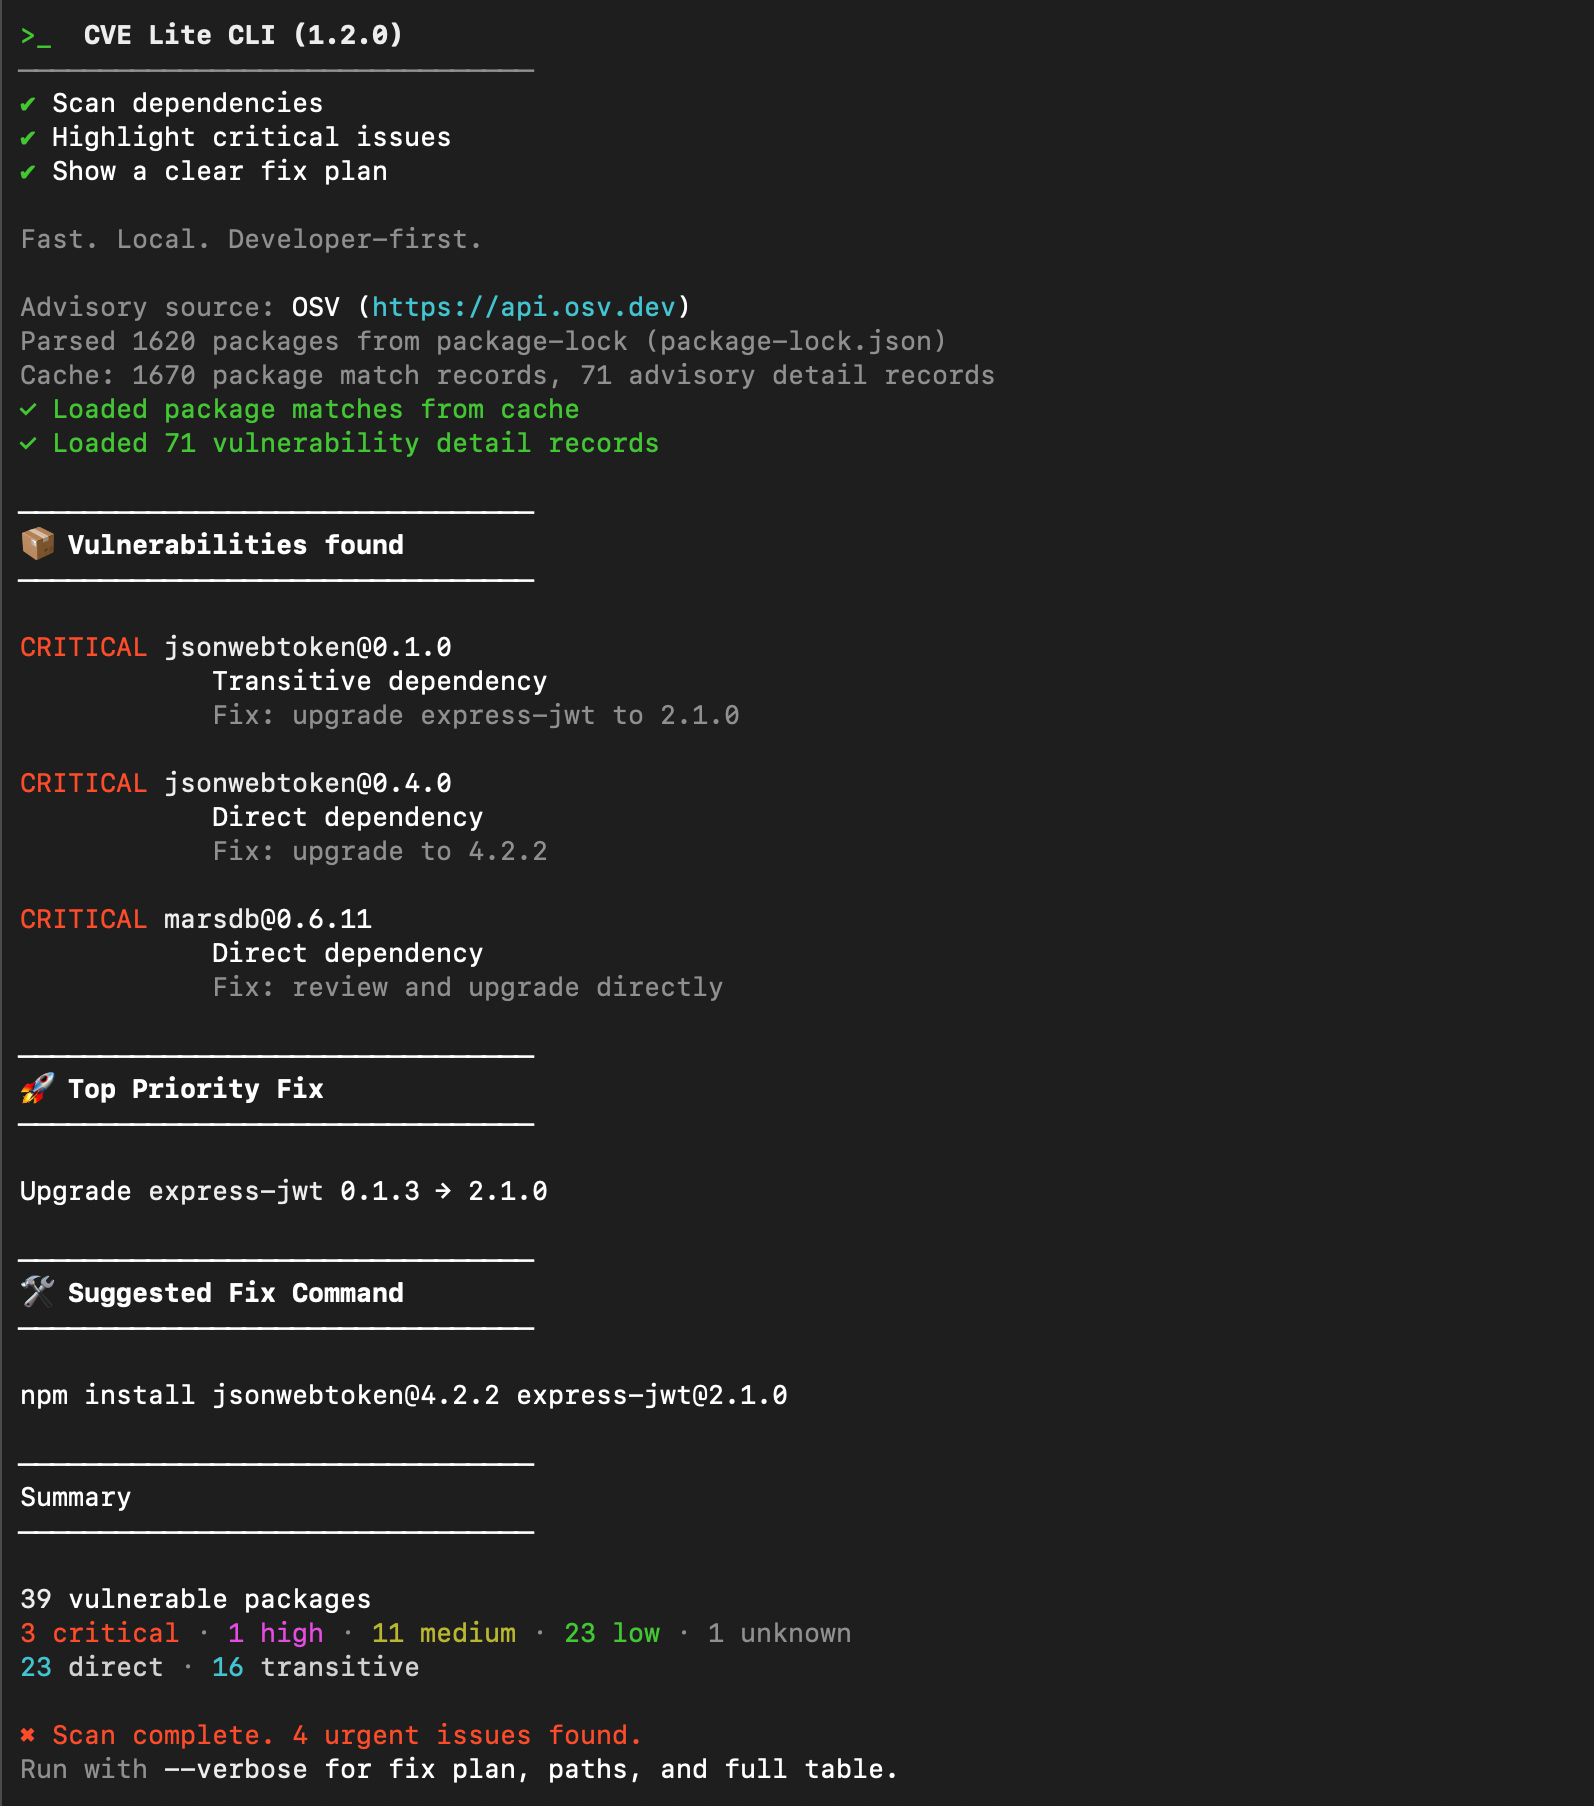
Fast, developer-friendly JS/TS dependency vulnerability scanner with local lockfile scanning, OSV matching, direct vs transitive visibility, --fix,…

opensource repo for validating agentic AI applications: redteam, behavior, supply-chain, static analysis

Running OWASP cve-lite-cli against the pi monorepo: scan journey and key finding (vitest CVE-2026-47429).

Unified security scanner for MCP servers with config, pentest, and repo-scan modes. Generates SARIF reports for CI/CD integration, detects secrets,…

Advanced recon engine that finds real secrets, validates them live, and builds exploit paths from client-side intelligence.

AI-powered SAST scanner that finds auth bypass, IDOR, and logic bugs Semgrep/CodeQL miss. Free GitHub Action. Supports Python, JS/TS, Go, PHP, Ruby.

Self-hosted runtime control plane for AI agents. Observe or HITL approve or Block rogue tool calls before it executes: secret leaks, prompt…

C-based Android static analysis framework for decompilation, secret detection, endpoint discovery, permission analysis, and native library scanning…

Code security scanning tool (SAST) to discover, filter and prioritize security and privacy risks.