
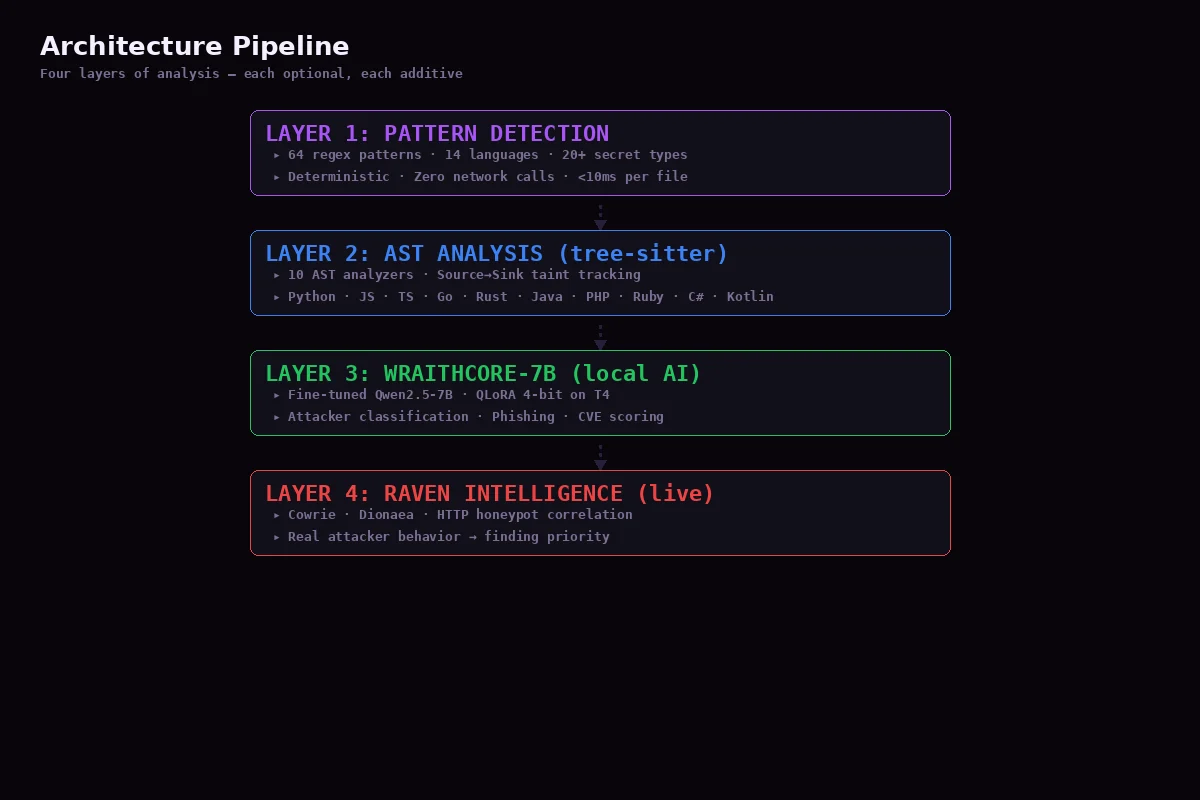
Codeguard-copilot
 niffyhunt/codeguard-copilot
AI-powered security co-pilot that catches vulnerabilities as you code. Real-time security scanning, educational explanations, and auto fixes for…
ai-securitycode-analysisdefensive-tools+8
niffyhunt/codeguard-copilotAI-powered security co-pilot that catches vulnerabilities as you code. Real-time security scanning, educational explanations, and auto fixes for…
 dmdhrumilmistry/security-harness
Multi-agent static application-security review harness for AI coding agents: maps codebases, hunts vulnerability classes, chains and verifies…
 akha-security/akca
Evidence-oriented DAST scanner in Go that crawls web apps and APIs, then runs adaptive SQLi, XSS, RCE, SSRF, and auth checks with replayable proof.
 9pings/fad-checker
Buildless dependency auditor that scans 10 ecosystems offline, reporting CVEs prioritized by CISA KEV and EPSS, EOL packages, licenses, committed…
 openbreach/canop
Static analysis CLI that scans AI-generated code for vulnerabilities like SQL injection, unsafe reflection, and hardcoded secrets, with SARIF export…
 tomnomnom/gf
A wrapper around grep, to help you grep for things
 zaydmulani09/sentrymcp
A static + runtime security scanner for MCP (Model Context Protocol) servers
 pantheon-security/medusa
AI-first security scanner. NEW in v2026.7: Claude Code compromise detection — vet .claude/ hooks, permissions & skills before you clone — plus an…
 synacktiv/octoscan
Octoscan is a static vulnerability scanner for GitHub action workflows.
 adamsjack711-ux/pkgxray
Pre-install security for AI agents, npm packages, and MCP servers. Zero-dep local static analysis; normal scans never execute package code.
 owasp/sedated
SEDATED® Project (Sensitive Enterprise Data Analyzer To Eliminate Disclosure)
 cisco-ai-defense/skill-scanner
Security Scanner for Agent Skills
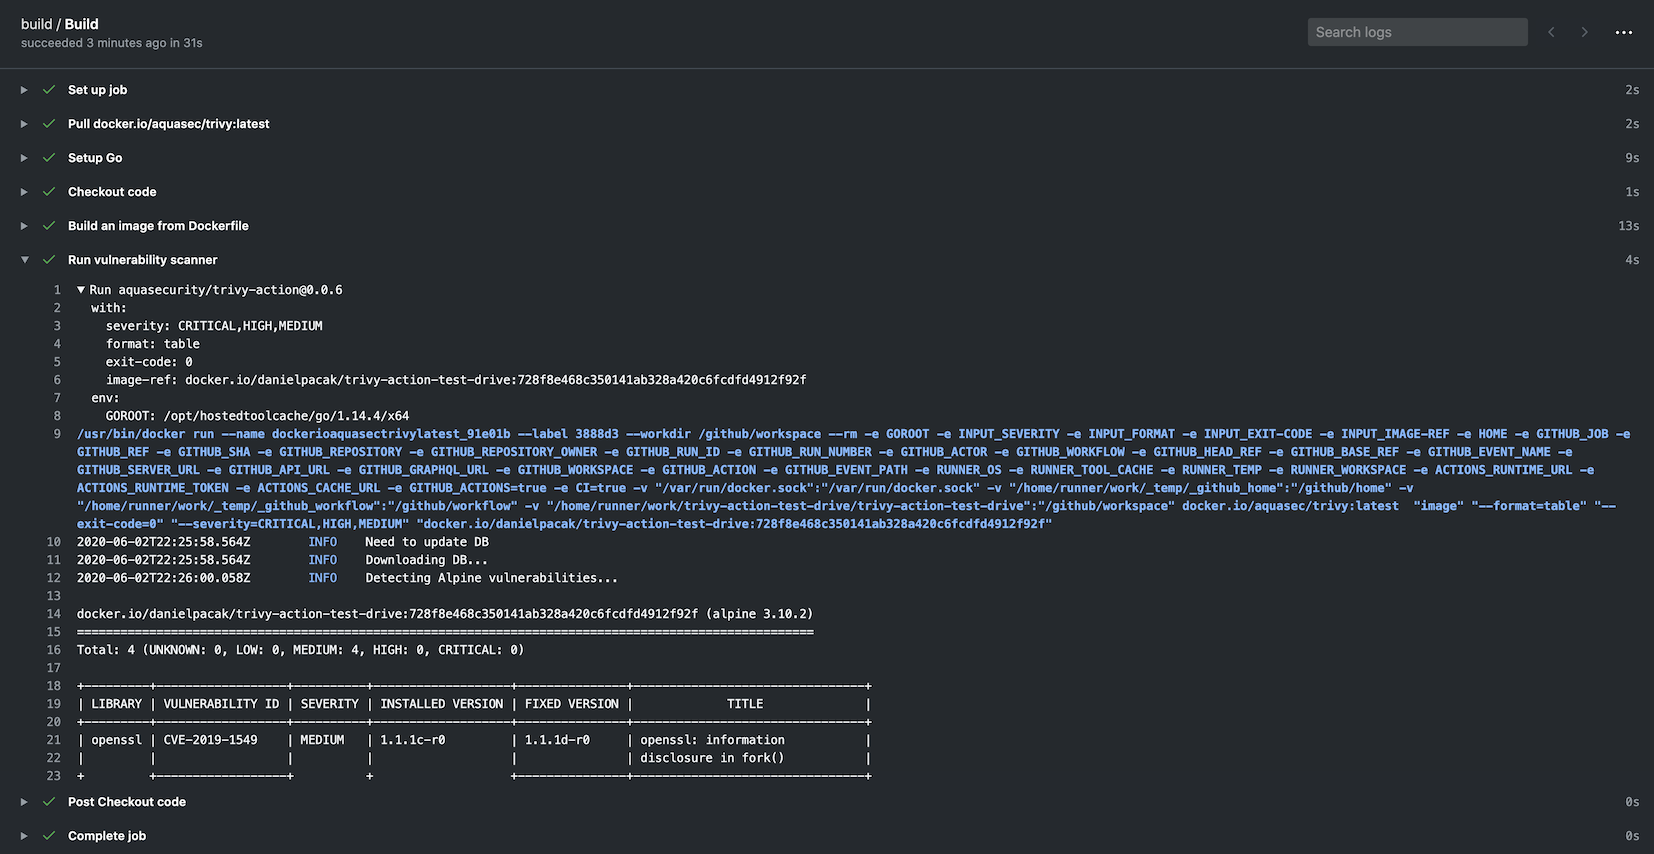 aquasecurity/trivy-action
Runs Trivy as GitHub action to scan your Docker container image for vulnerabilities
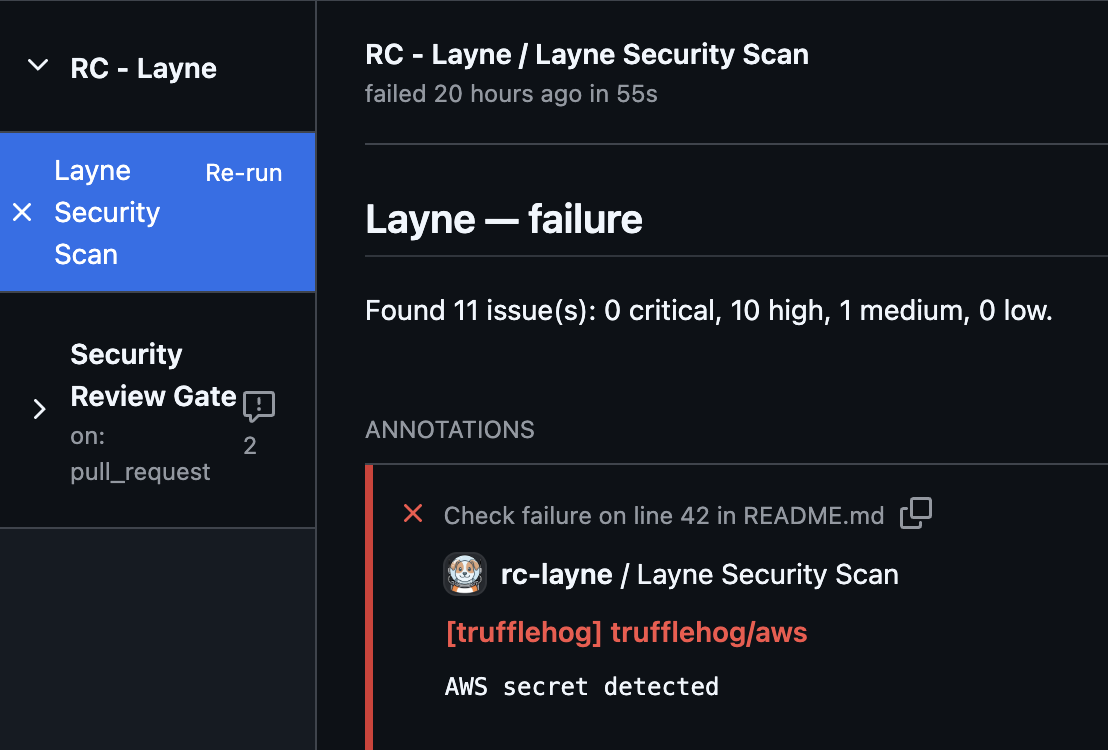 rocketchat/layne
A doggo that helps look for security issues in your repositories.
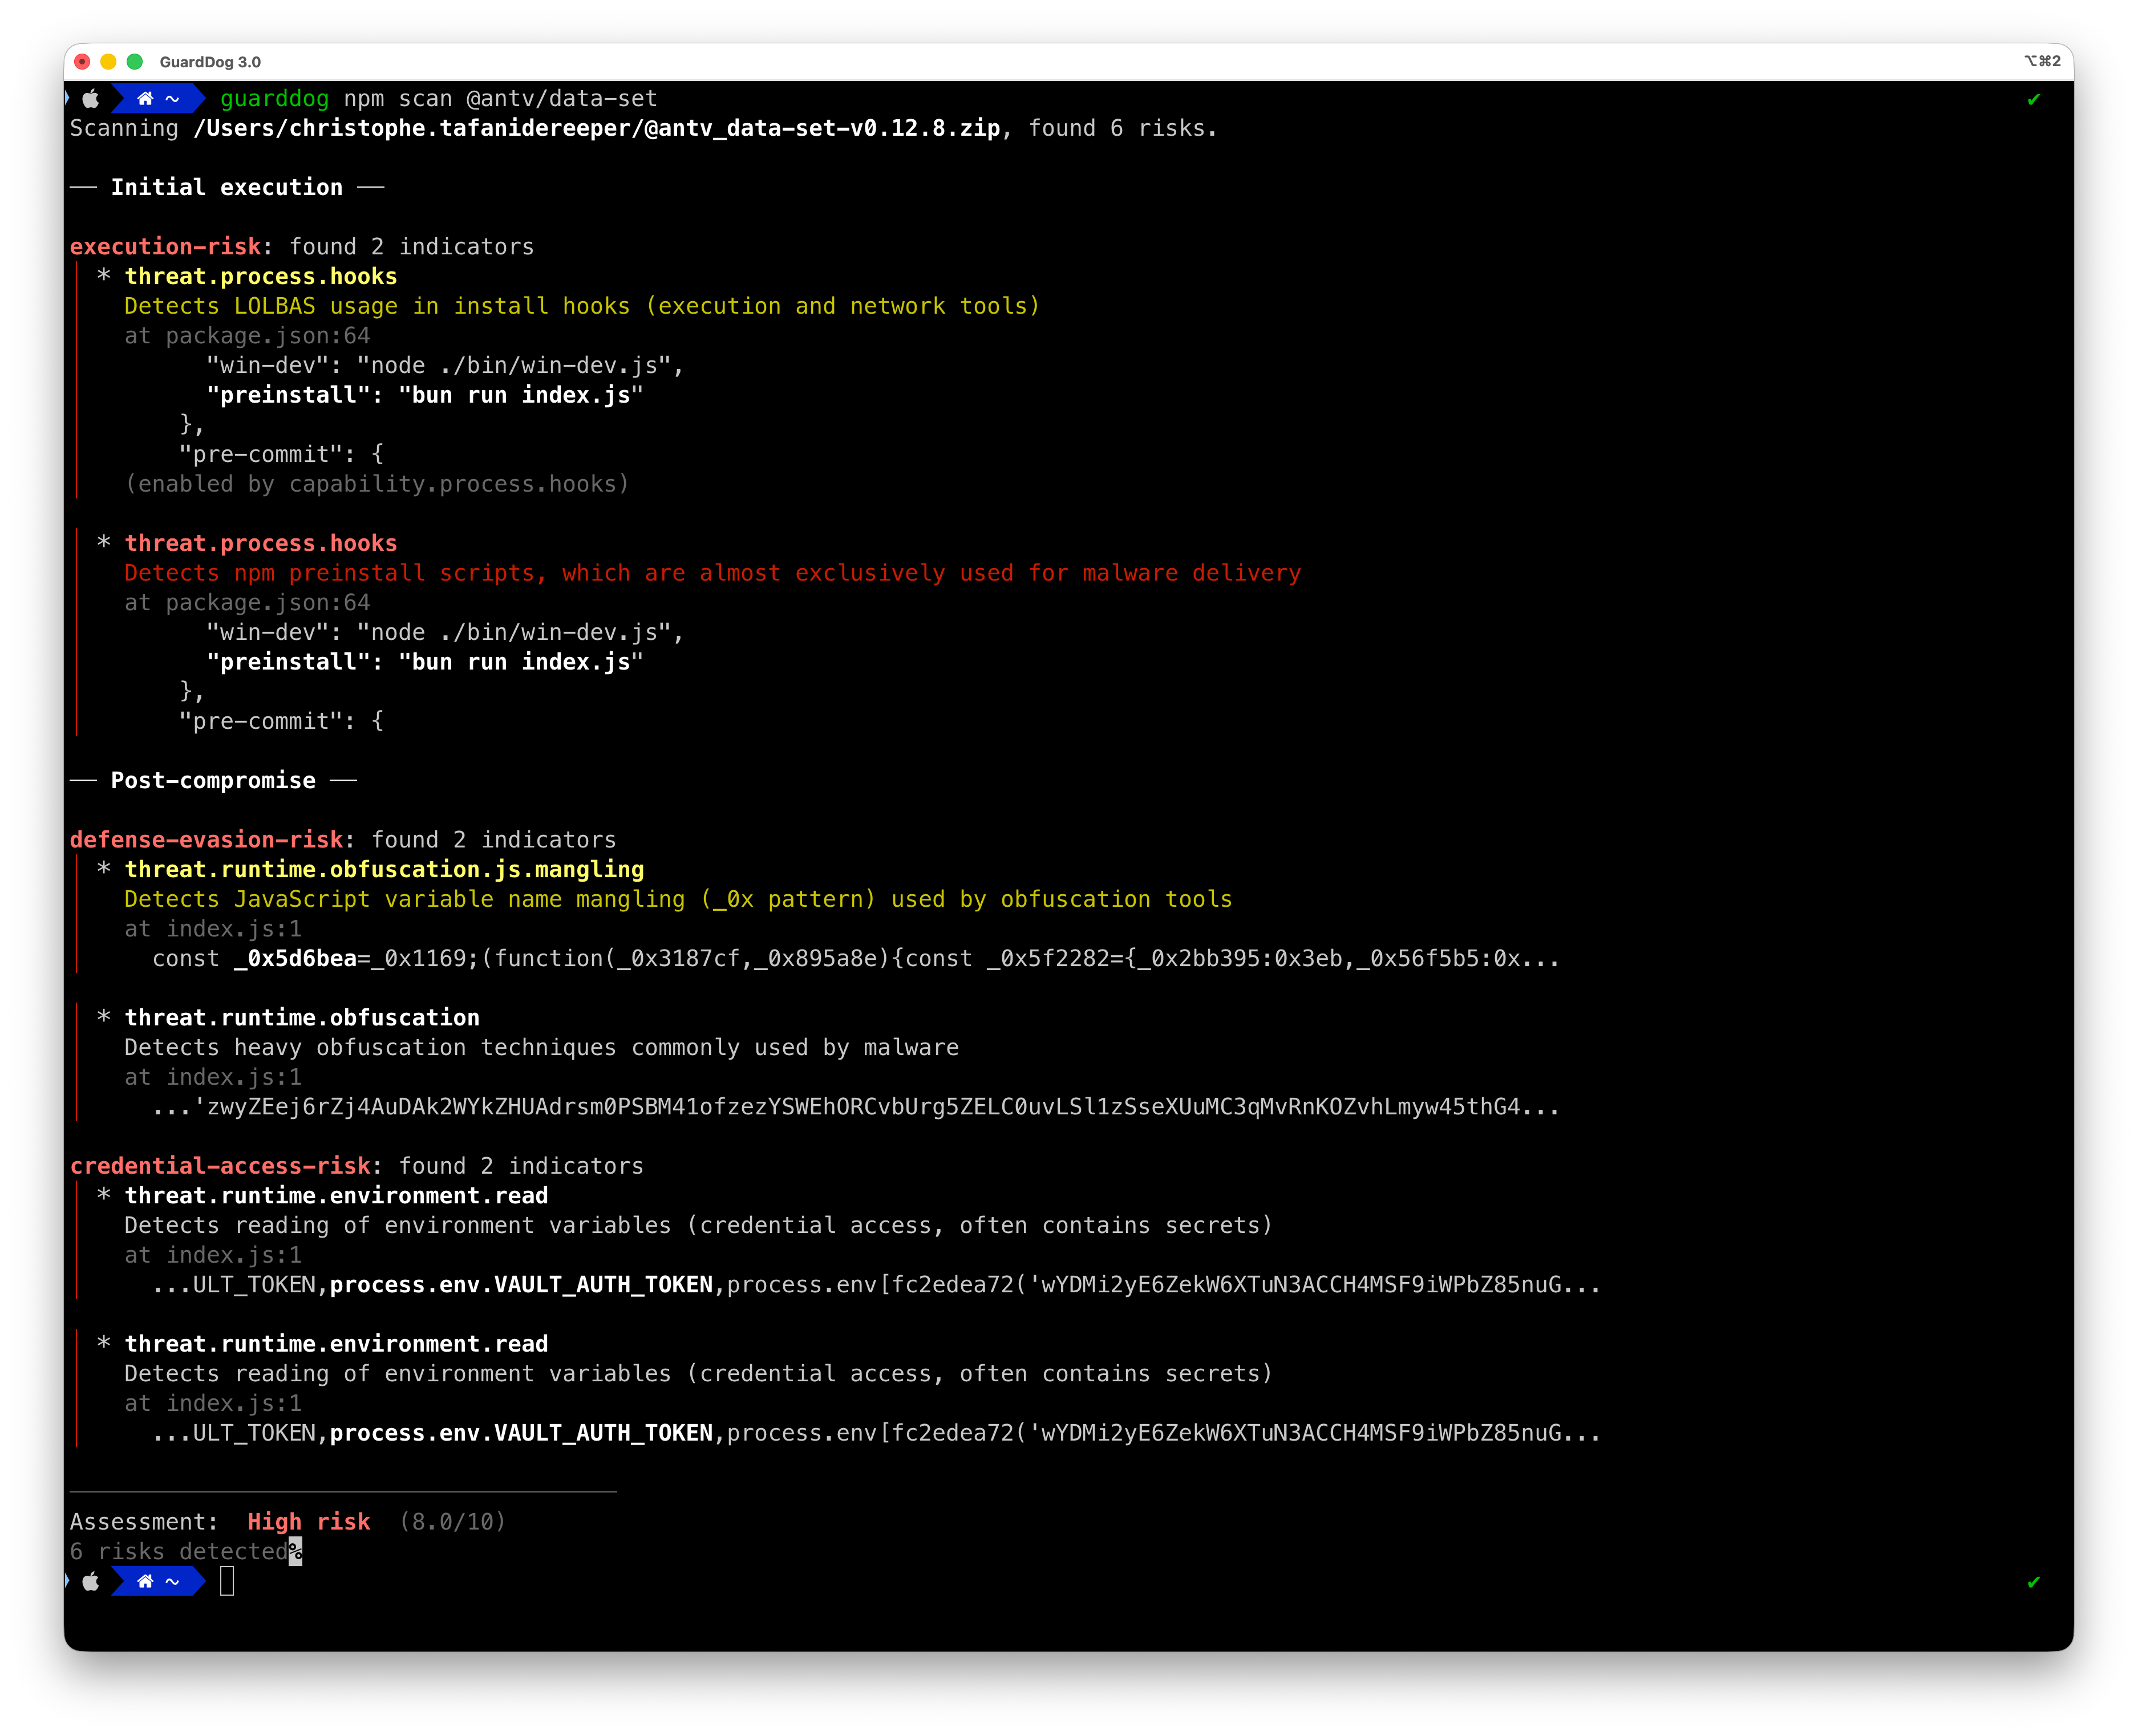 datadog/guarddog
🐍 🔍 GuardDog is a CLI tool to Identify malicious PyPI and npm packages
 qi-scape/scan-shai-hulud
Detect CVE-2026-45321 Mini Shai-Hulud supply chain compromise — scans for 170 npm + 2 PyPI poisoned packages across TanStack, Mistral AI, UiPath,…
 shakilkhatri/scanner-for-cve-2025-55182-vulnerability
CVE-2025-55182 Detector. Find which of your GitHub repositories are exposed to the critical React/Next.js RCE vulnerability and generate a clean…
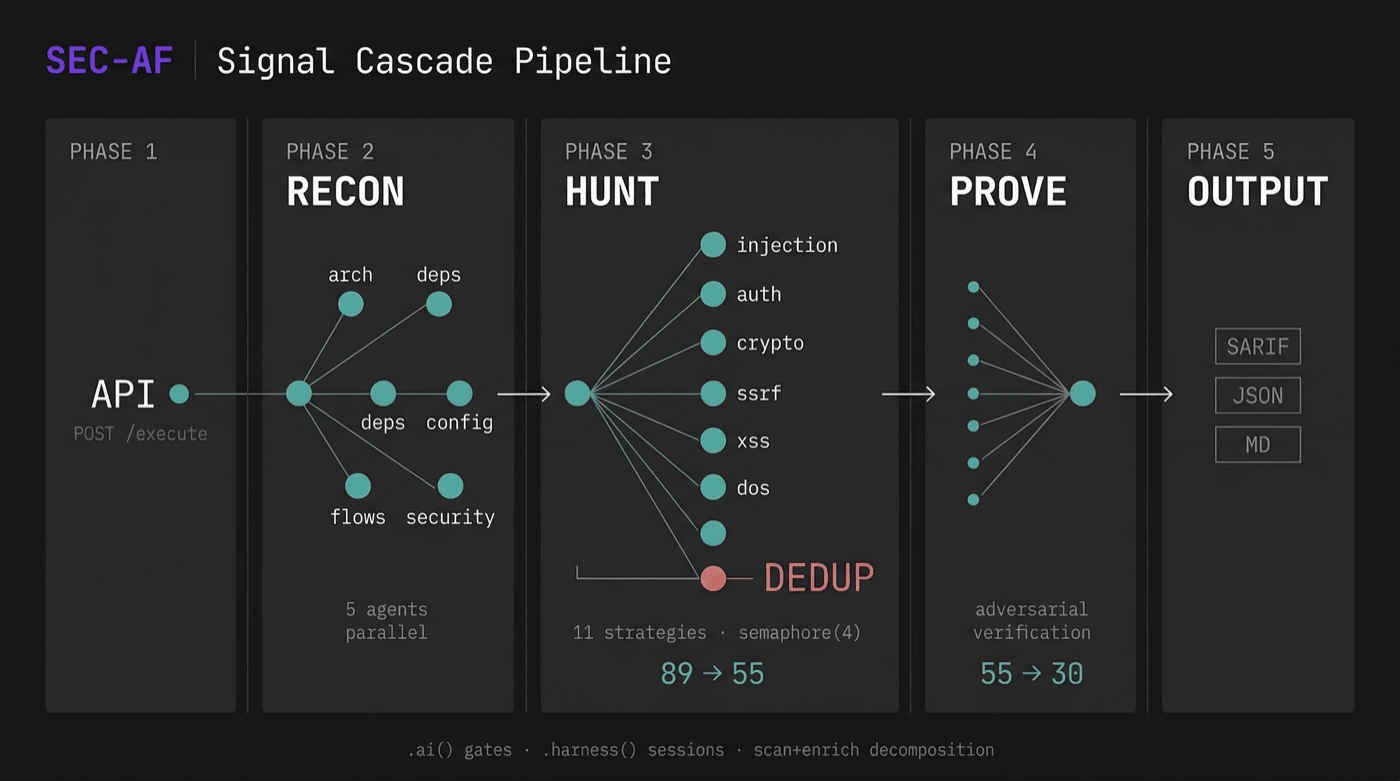 agent-field/sec-af
AI-native code security auditor on AgentField that proves exploitability with verdicts, traces, and actionable evidence.