

nuclei
 projectdiscovery/nuclei
Fast YAML-based vulnerability scanner with template-driven detection engine for automated security testing across web apps, APIs, networks, DNS, and…
anti-botapi-securityapi-security-testing+21
32.5k
projectdiscovery/nucleiFast YAML-based vulnerability scanner with template-driven detection engine for automated security testing across web apps, APIs, networks, DNS, and…
 dmdhrumilmistry/security-harness
Multi-agent static application-security review harness for AI coding agents: maps codebases, hunts vulnerability classes, chains and verifies…
 m14r41/scan4secrets
Find credentials and secret with 170+ rules covering across source code, Web URL, and CI/CD, verifies them against vendor APIs, and generates SARIF,…
 awarexone/agentic-bug-hunter
AI-powered bug bounty hunting toolkit that works with or without subscription.
 akha-security/akca
Evidence-oriented DAST scanner in Go that crawls web apps and APIs, then runs adaptive SQLi, XSS, RCE, SSRF, and auth checks with replayable proof.
 karim852/kumo-domain-recon-tool
Domain OSINT and security reconnaissance framework running 26 parallel modules for DNS, ports, subdomains, leaked credentials, exposed endpoints,…
 piratesshield/apiharvester
The one shot API attacker tool - finds the API url from the given root simulate the automated attacks
 mongodb/kingfisher
Detect secrets + live validation. Map blast radius. Revoke fast. Use the CLI or embed in Rust and Python.
 proviesec/google-dorks
Useful Google Dorks for WebSecurity and Bug Bounty

 unkl4b/gitminer3
Tool for advanced mining for content on Github
 owasp/secretsifter
OWASP Incubator project: detects credentials exposed in browser-delivered content (JavaScript, config responses, live traffic).
 owasp/piihunter
Scans PostgreSQL databases and Jira issues for PII using regex, NER/ML, and optional self-hosted LLM detection, with redacted reports and audit…
 syscallx-18113/apkx-hunter
C-based Android static analysis framework for decompilation, secret detection, endpoint discovery, permission analysis, and native library scanning…
 praetorian-inc/caeruleus
Single Go binary for Bluetooth Low Energy security testing on Linux/BlueZ: scan, enumerate GATT, read/write/notify, fuzz characteristics, and run…
 wadingporque/apkprobe
APK decompiler & secrets scanner for Android security research! Extract leaked API keys, hardcoded credentials, endpoints from APK files. apk2url,…
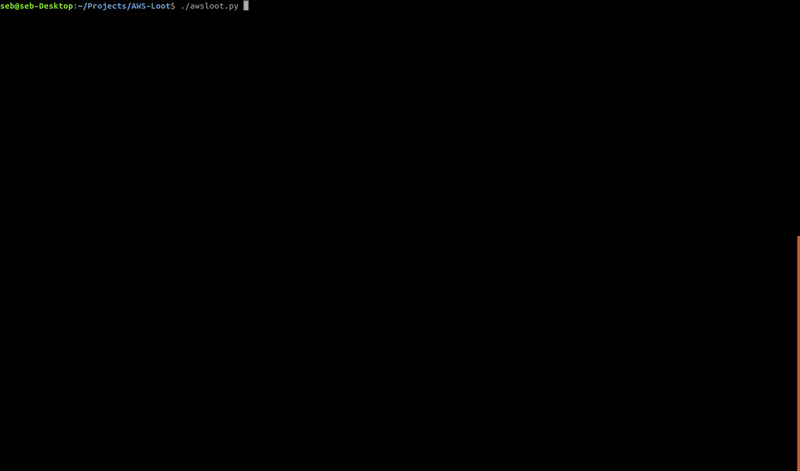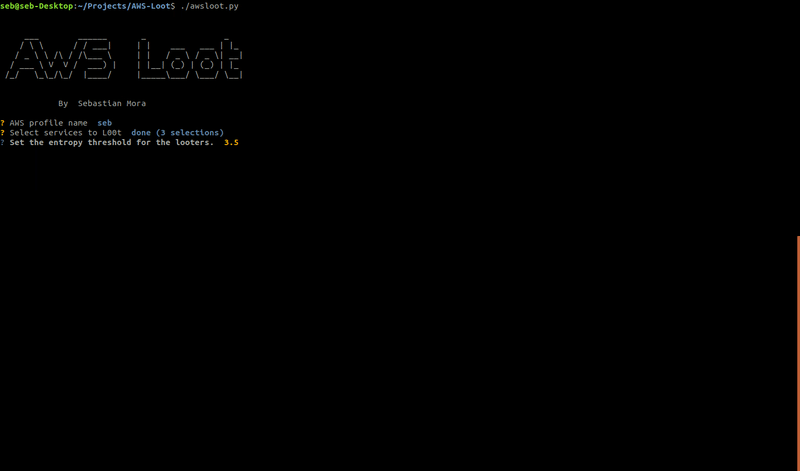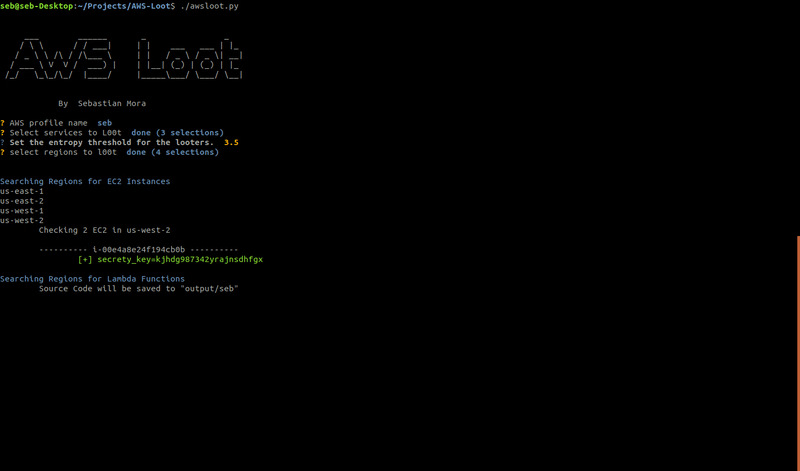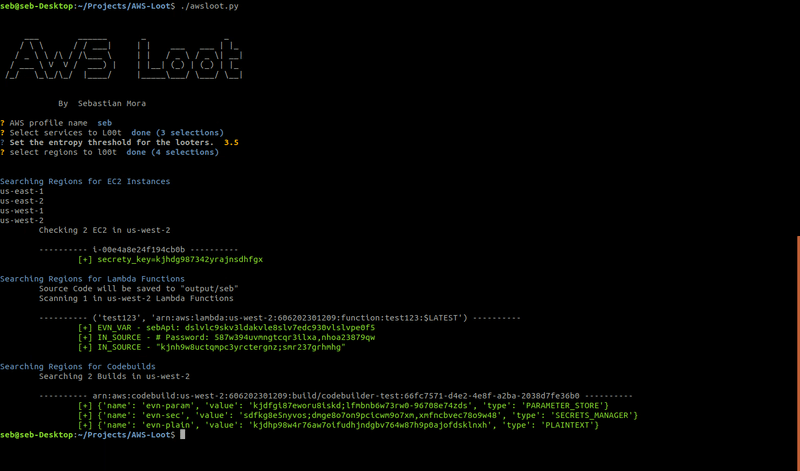 sebastian-mora/aws-loot
Enumerates AWS environments for secrets by scanning EC2 userdata, Lambda environment variables and source code, and CodeBuild instances for…
 hilmiazizi/oorecon
Terminal UI for attack surface discovery: DNS recon, subdomain enumeration, port scanning, reverse IP, leaked login URLs, and JavaScript secret…