

TangledWinExec
 daem0nc0re/tangledwinexec
PoCs and tools for investigation of Windows process execution techniques
adversarial-attackdebuggersids-ips-evasion+6
958
daem0nc0re/tangledwinexecPoCs and tools for investigation of Windows process execution techniques
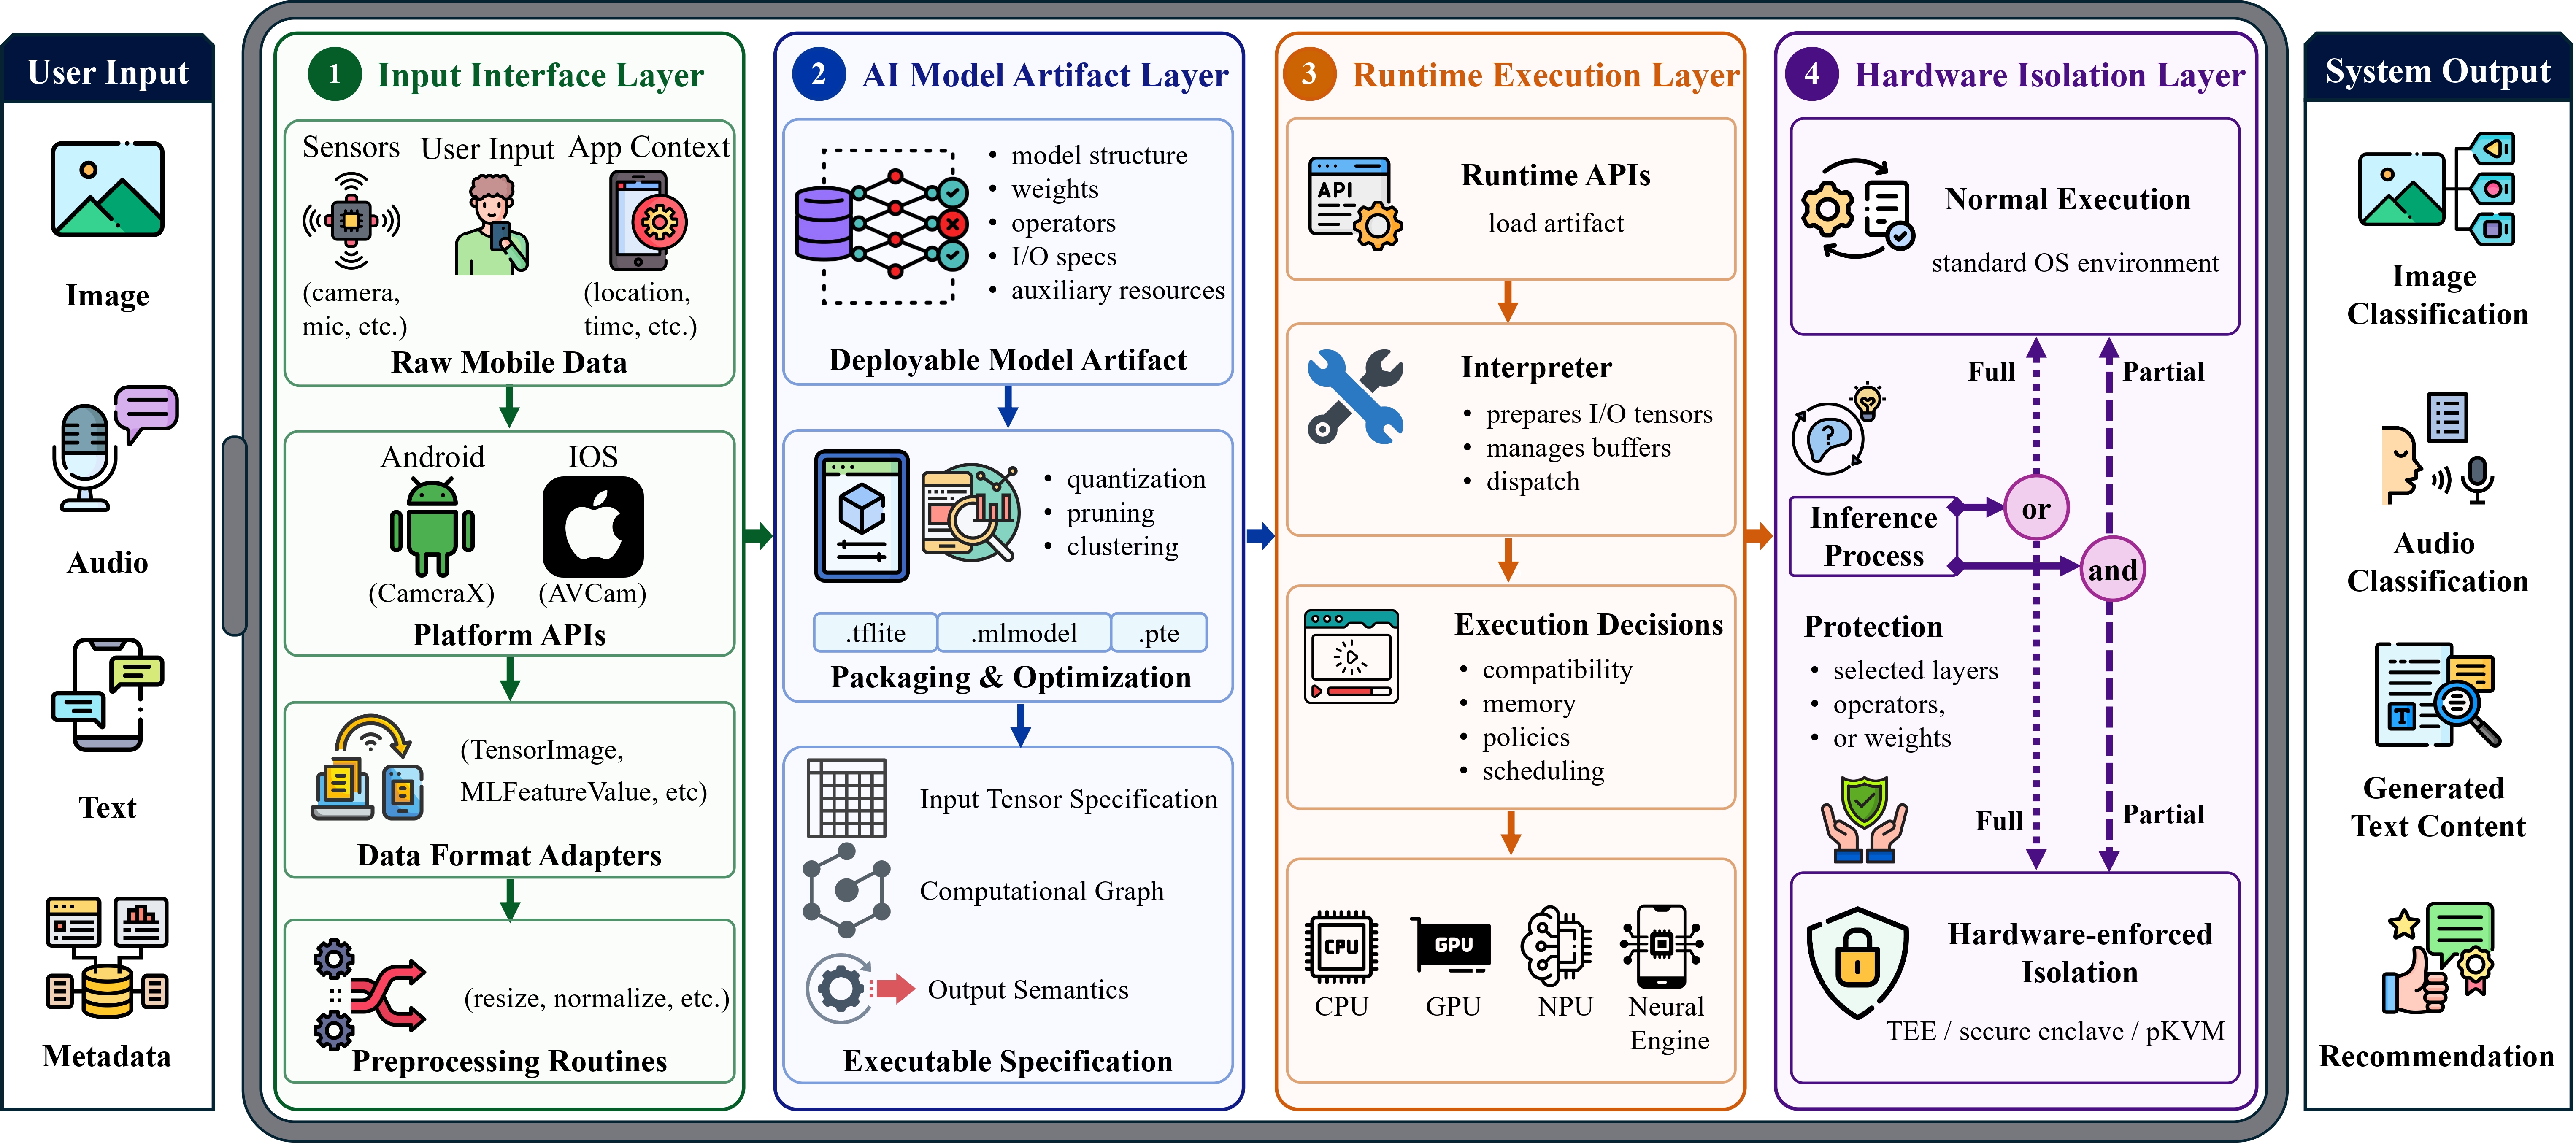 jinxhy/awesome-moai-security
Curated reading list and taxonomy of attack and defense research for mobile on-device AI systems, covering adversarial, backdoor, model stealing, and…
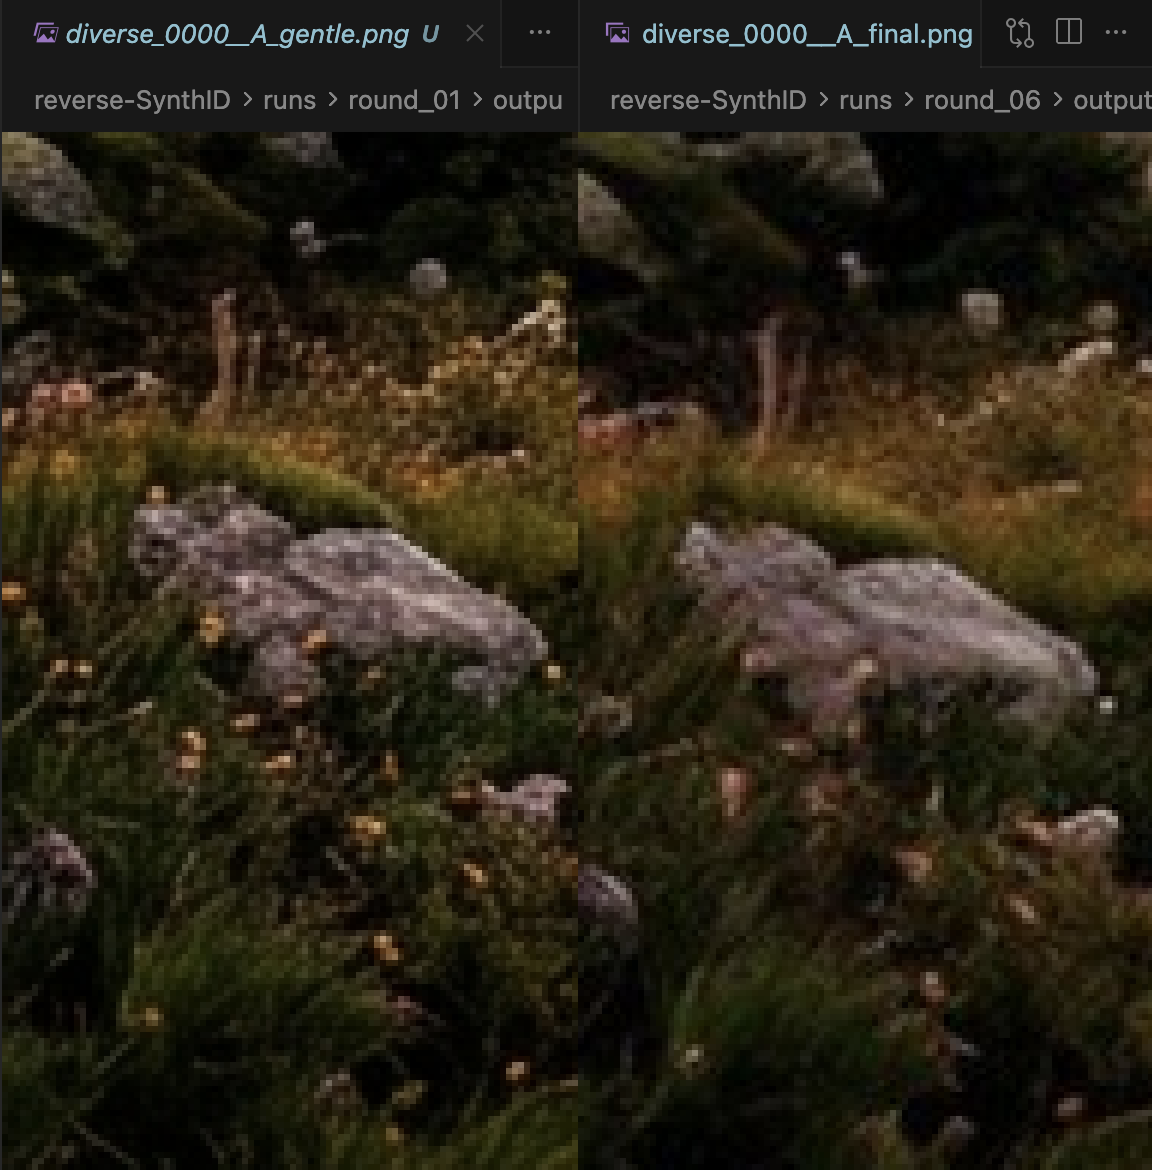 aloshdenny/reverse-synthid
reverse engineering Gemini's SynthID detection
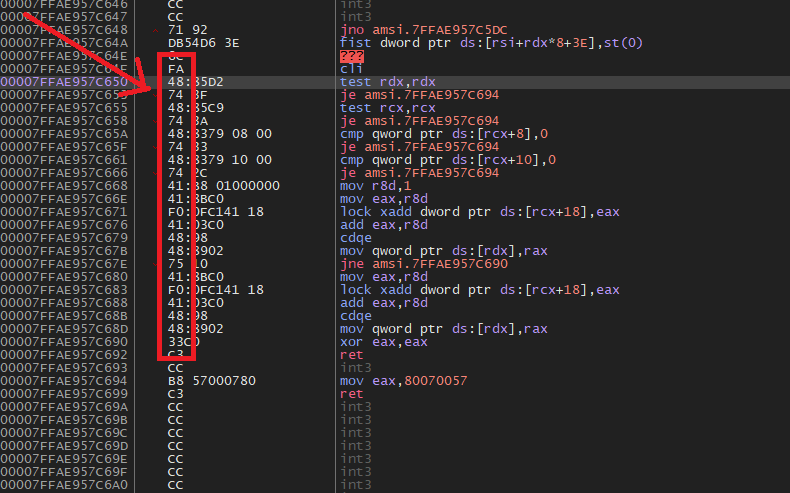 zeromemoryex/amsi-killer
Lifetime AMSI bypass
 xyrem/hyperdeceit
HyperDeceit is the ultimate all-in-one library that emulates Hyper-V for Windows, giving you the ability to intercept and manipulate operating system…
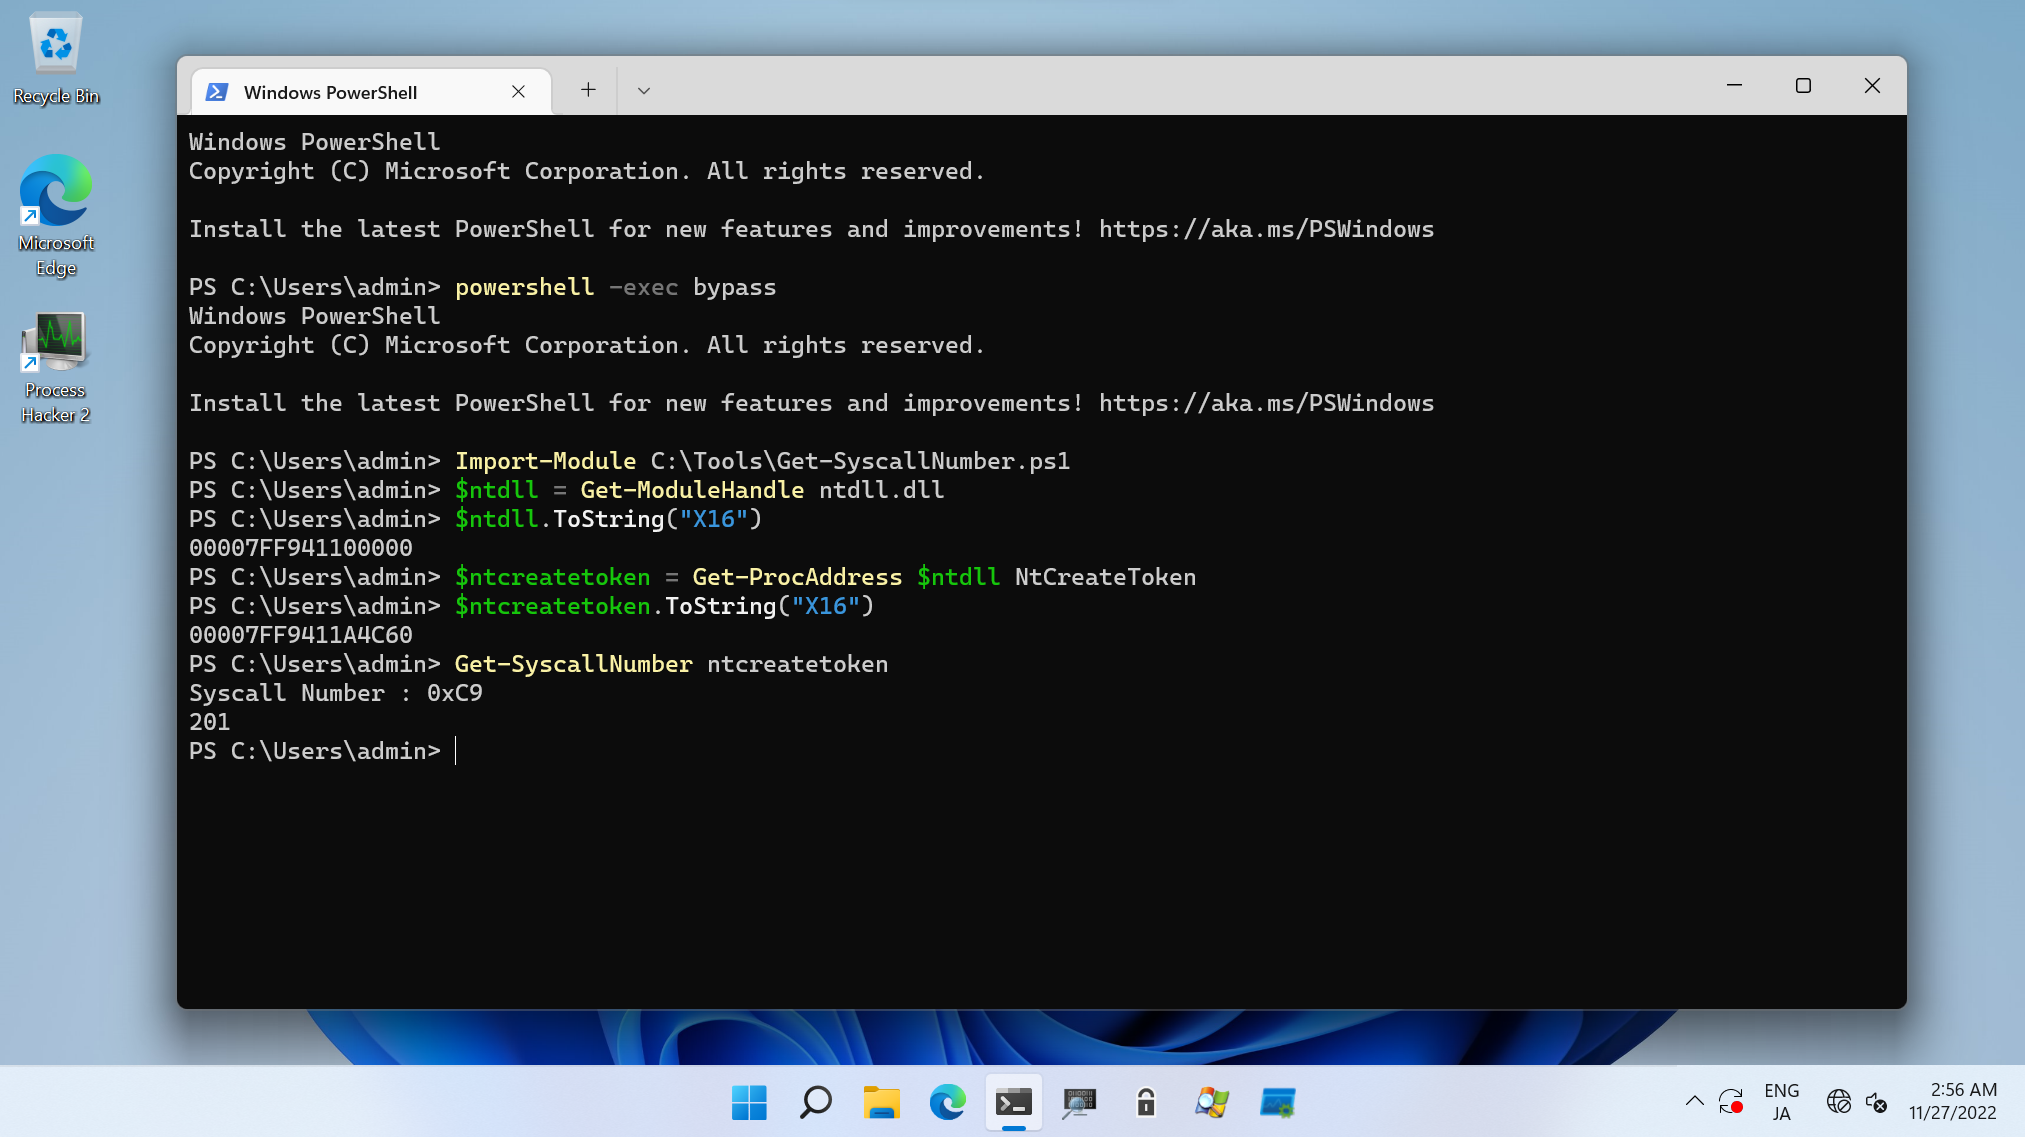 daem0nc0re/atomicsyscall
Tools and PoCs for Windows syscall investigation.
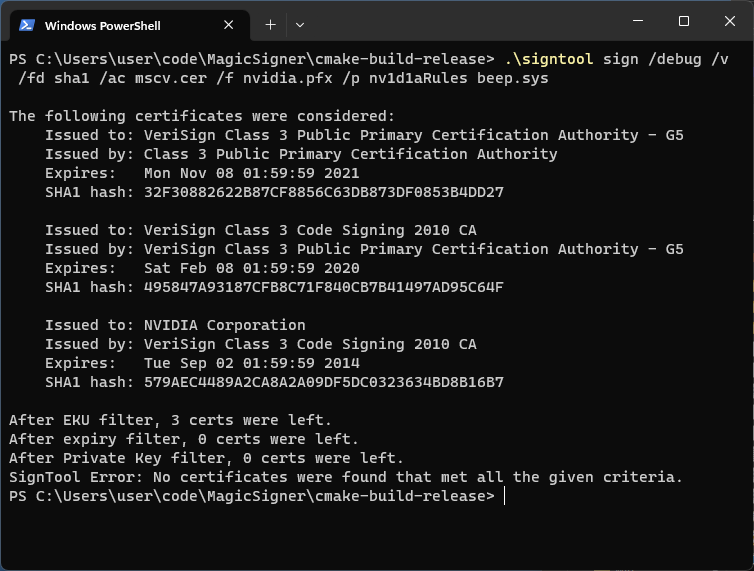 namazso/magicsigner
Signtool for expired certificates
 arosenmund/defcon33_silence_kill_edr
Hands-on DEFCON workshop materials for killing and silencing EDR agents: lab setup, BYOVD, custom C/C++ evasion tooling, and reverse engineering.
 neomaster831/kurasagi
Windows 11 24H2-25H2 Runtime PatchGuard Bypass
 mr-un1k0d3r/windows-signedbinary
Mutates signed Windows binaries to retain valid catalog signatures while changing file hashes, bypassing hash-based endpoint blocks and exposing…
 thebabush/llvm-jutsu
Anti-LLM obfuscation via finger counting
 aloshdenny/reverse-synthid-text
reverse engineering SynthID for text
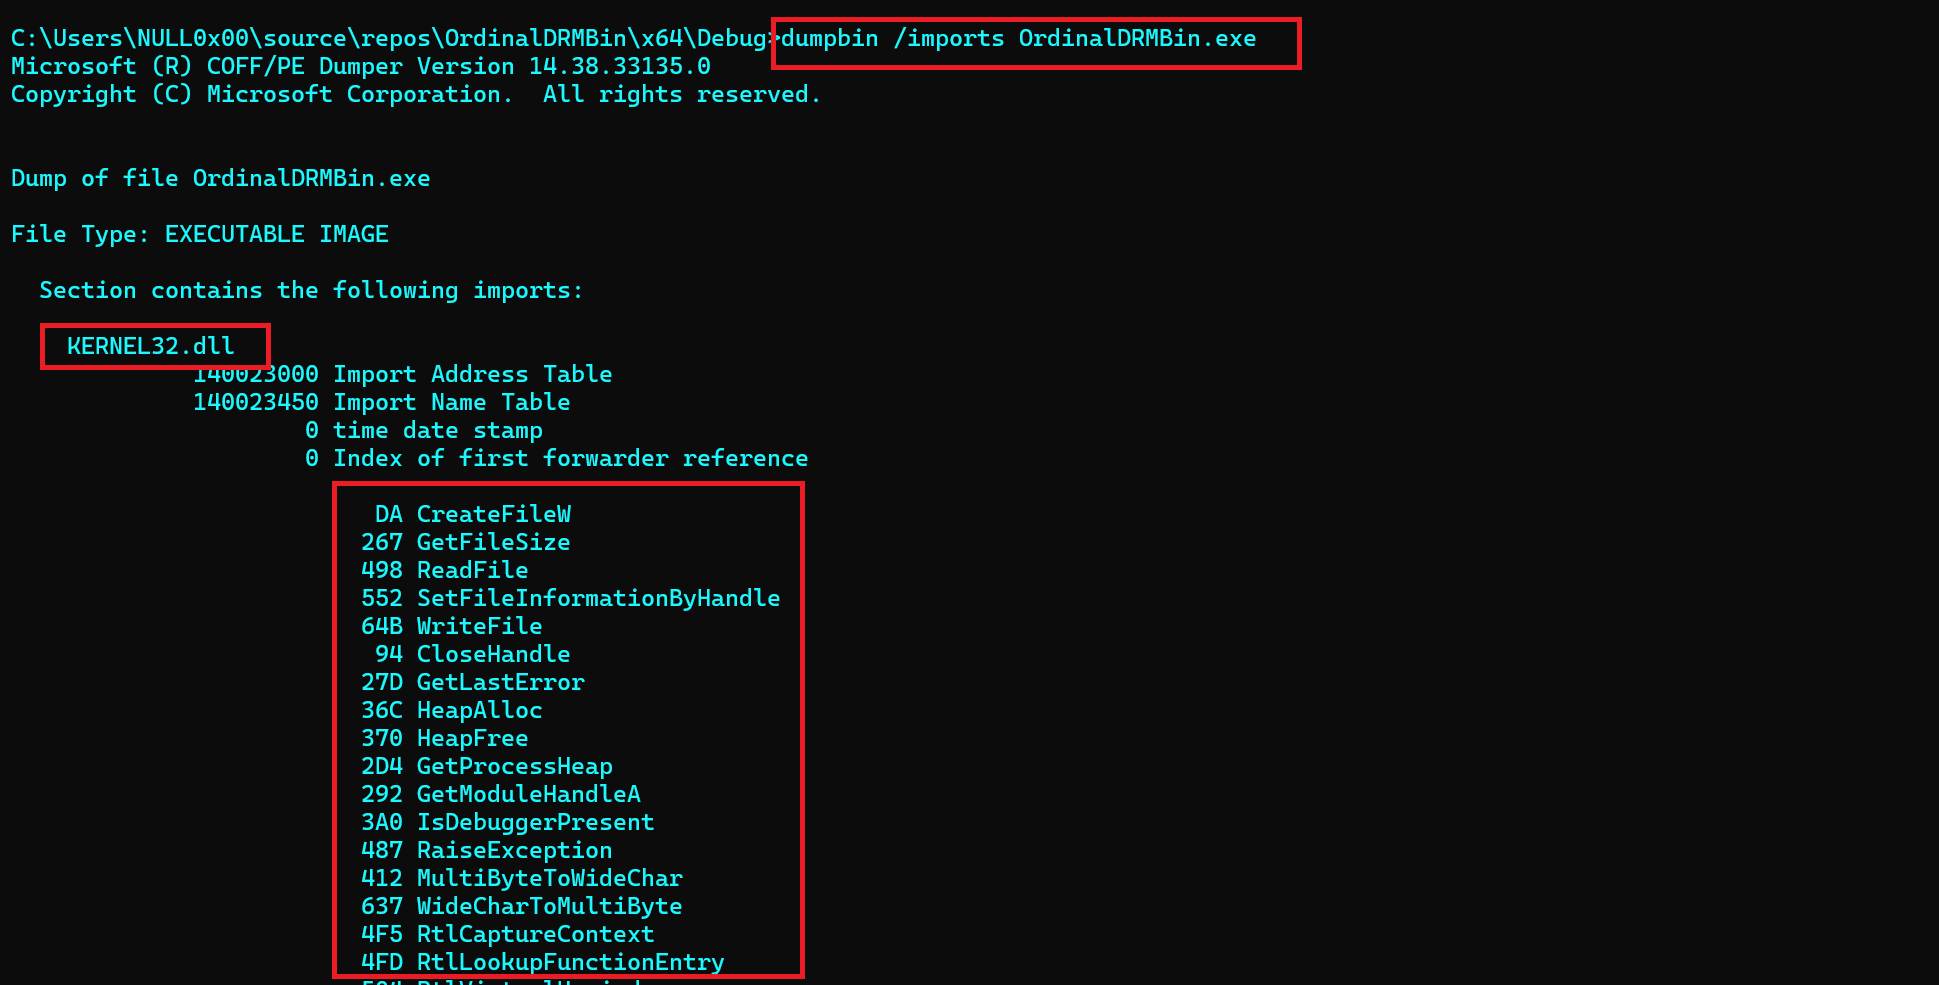 maldev-academy/drmbinviaordinalimports
Create Anti-Copy DRM Malware
 gmh5225/antidebug-antivm
Different methods to detect a virtualized environment or potential debugging
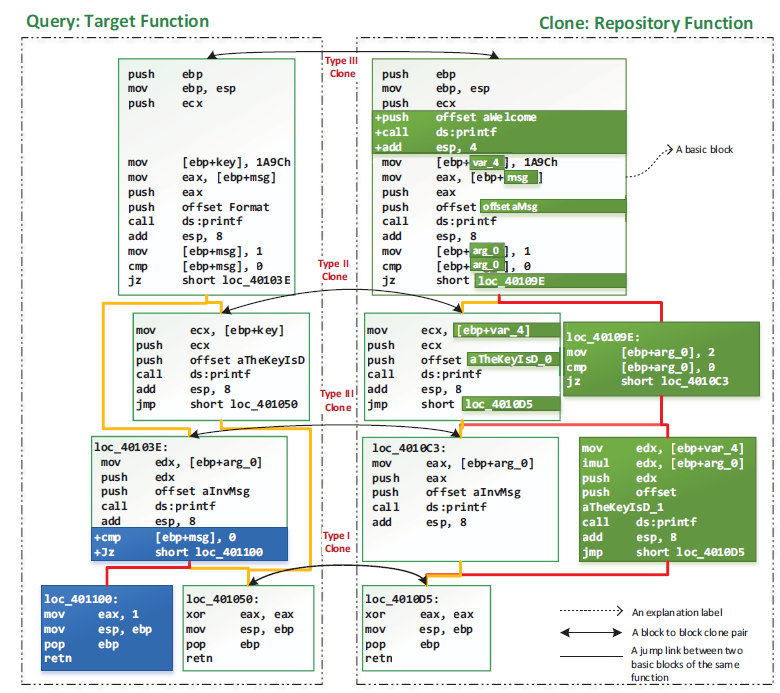 mcgill-dmas/kam1n0-community
Scalable assembly analysis platform for indexing, clone search, and executable classification using static, dynamic, and machine-learning techniques…
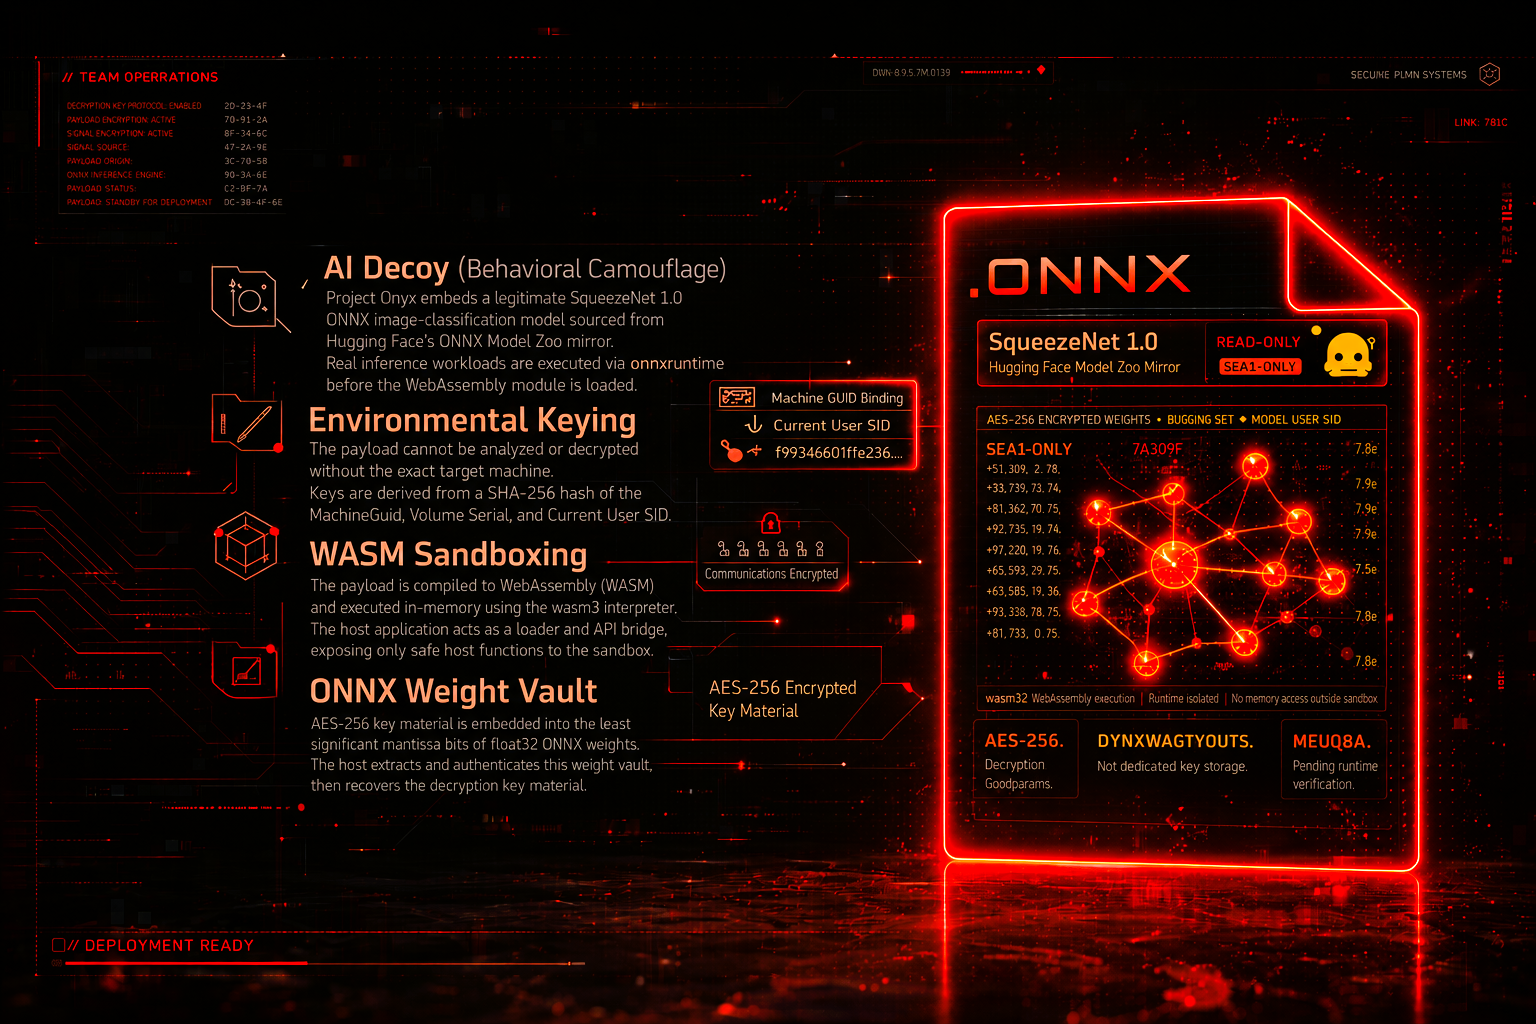 x-3306/project-onyx
Advanced EDR Evasion via AI Telemetry Spoofing & WASM Sandboxing. Project Onyx is a PoC Red Team pipeline designed to demonstrate advanced evasion…
 seanheelan/anamnesis-release
Evaluation framework for studying LLM agents that automatically generate working exploits from vulnerability reports, bypassing modern security…
 mrphrazer/binary-cartography
Technical webinars on reverse engineering, malware analysis, and software protection.