

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
51 results
yakit preview

yakit

GitHubyaklang/yakit

All-in-one penetration testing platform with MITM proxy, web fuzzer, reverse connection handler, and plugin system for automated security testing and…
command-and-controlexploit-frameworksfuzzing+9
7.8k
6h 29m ago
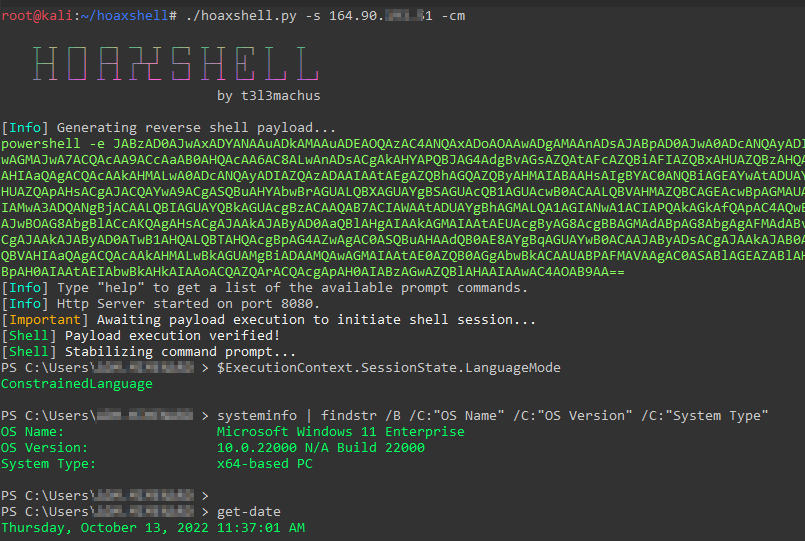
hoaxshell preview

hoaxshell

GitHubt3l3machus/hoaxshell

A Windows reverse shell payload generator and handler that abuses the http(s) protocol to establish a beacon-like reverse shell.

command-and-controlexploitationpayload-generation+5
3.5k1 year ago
skills preview

skills

GitHubspecterops/skills

Reusable offensive security skills and plugins for AI agents, covering reconnaissance, exploitation, C2, payload development, and reporting across…
command-and-controleducationexploitation+9
7154 days ago
CobaltStrikeParser preview

CobaltStrikeParser

GitHubsentinel-one/cobaltstrikeparser

Python parser for extracting CobaltStrike Beacon configurations from PE files, memory dumps, and C2 URLs using heuristic XOR decryption and…
binary-analysiscommand-and-controlmalware-analysis+1
1.1k3 years ago
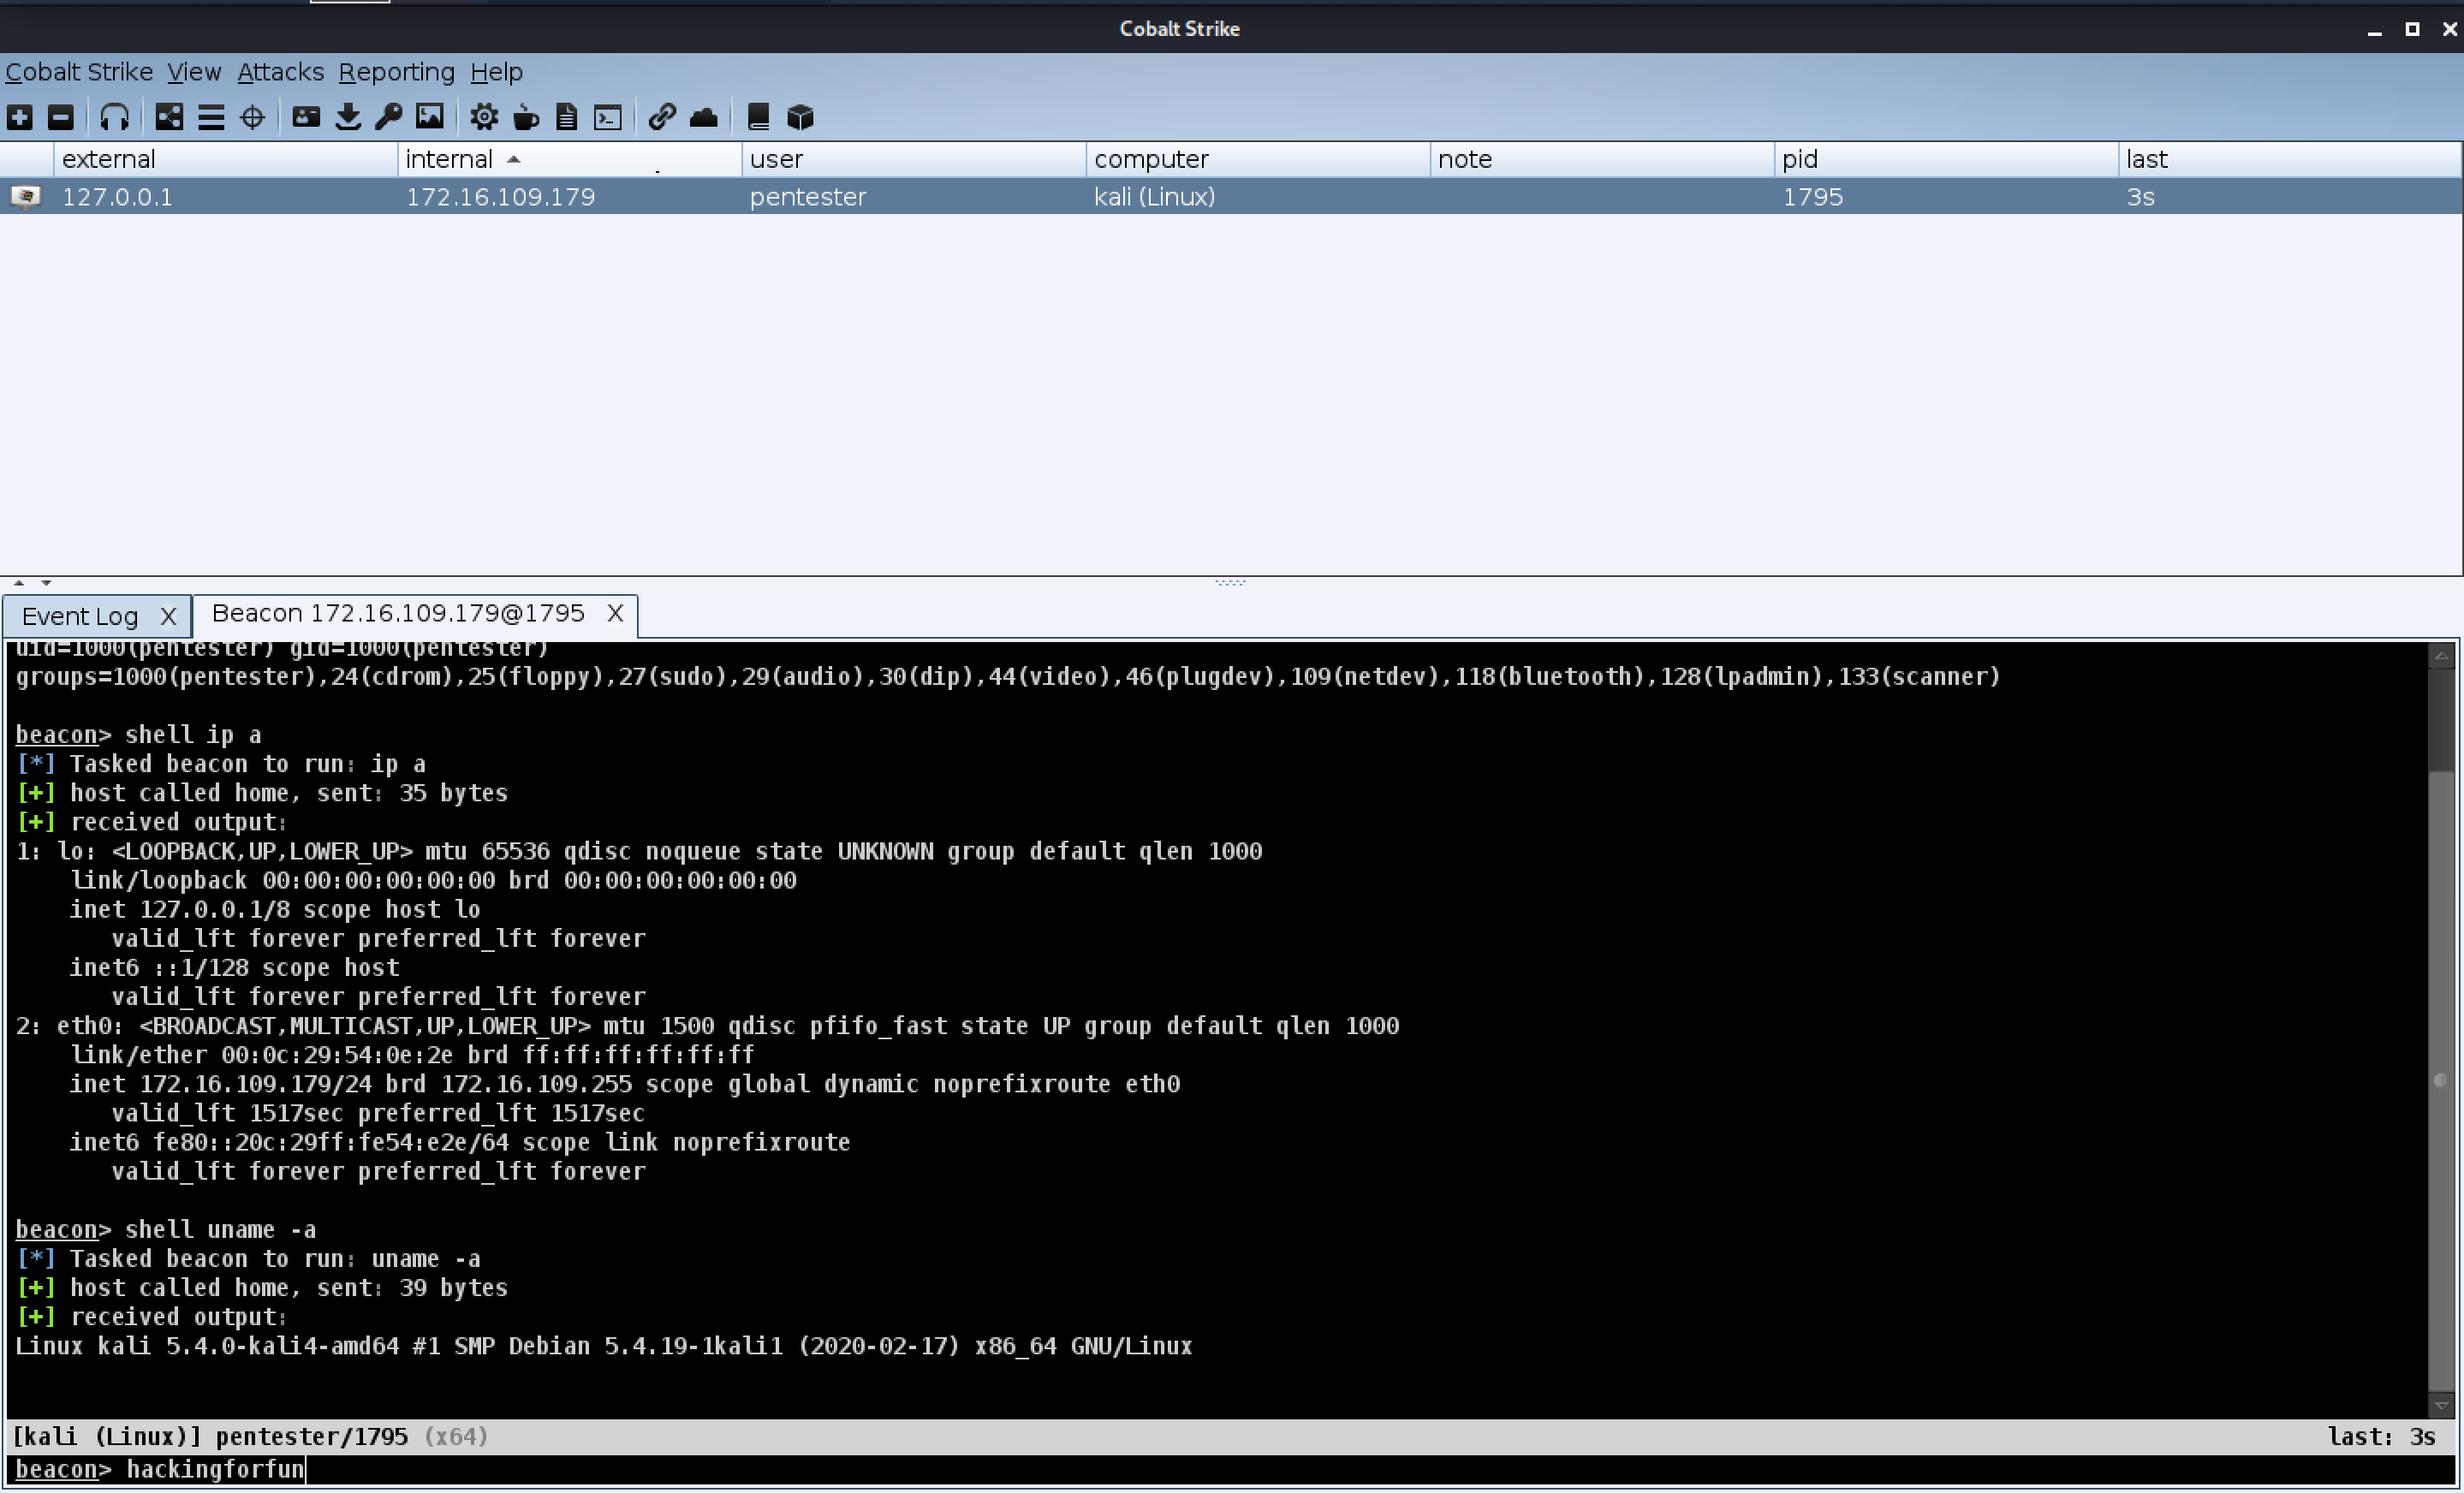
geacon preview

geacon

GitHubdarkr4y/geacon

Practice Go programming and implement CobaltStrike's Beacon in Go

command-and-controlexploit-frameworkspayload-development+2
1.3k6 years ago
hackEmbedded preview

hackEmbedded

GitHubdoudoudedi/hackembedded

This tool is used for encrypt backdoor,shellcode,socks5 proxy generation,Information retrieval and POC arrangement for various architecture devices

command-and-controlembedded-systems-securityencryption-decryption-tools+8
2062 months ago
EvilVM preview

EvilVM

GitHubjephthai/evilvm

Forth-based compiler deployed as position-independent x86_64 shellcode, providing a remote code execution agent with interactive REPL over TCP, HTTP,…
command-and-controlexploit-frameworkspayload-development+7
2094 years ago
PixelCode-Attack preview

PixelCode-Attack

GitHubs3n4t0r-0x0/pixelcode-attack

Malicious PixelCode is a security research project that demonstrates a covert technique for encoding executable files into pixel data and storing…

command-and-controldata-exfiltrationeducation+8
1768 months ago
Project-Onyx preview

Project-Onyx

GitHubx-3306/project-onyx

Advanced EDR Evasion via AI Telemetry Spoofing & WASM Sandboxing. Project Onyx is a PoC Red Team pipeline designed to demonstrate advanced evasion…
ai-securitycommand-and-controlcryptography+6
1191 month ago
notionterm preview

notionterm

GitHubariary/notionterm

Embed a reverse shell in Notion pages using the Notion API as a proxy, enabling stealthy remote shell sessions with encrypted and authenticated…

command-and-controlexploitationpayload-generation+3
1383 years ago
DarkTortilla-RAT-Telegram-Exfiltration-Payload-Extraction-Analysis preview

DarkTortilla-RAT-Telegram-Exfiltration-Payload-Extraction-Analysis

GitHubkaandemir993/darktortilla-rat-telegram-exfiltration-payload-extraction-analysis

Reverse engineering analysis of DarkTortilla RAT, a sophisticated malware that steals credit card data, decrypts browser passwords, and exfiltrates…

command-and-controldata-exfiltrationdigital-forensics+4
491 month ago
PureRAT-msbuild.exe--C2-Extraction--Net-Evasion-Analysis preview

PureRAT-msbuild.exe--C2-Extraction--Net-Evasion-Analysis

GitHubkaandemir993/purerat-msbuild.exe--c2-extraction--net-evasion-analysis

Reverse engineering analysis of PureRAT RAT abusing msbuild.exe, extracting C2 infrastructure, .NET evasion APIs, file system manipulation, and…
binary-analysiscommand-and-controldefensive-tools+6
1727 days ago
PHPStudy-Backdoor preview

PHPStudy-Backdoor

GitHubjas502n/phpstudy-backdoor

phpstudy dll backdoor for v2016 and v2018

command-and-controlmalware-analysispayload-development+4
197 years ago
Overlord-RAT-Reverse-Engineering-a-Go-Based-RAT-Injection-Keylogging-C2-Exfiltration-Analysis preview

Overlord-RAT-Reverse-Engineering-a-Go-Based-RAT-Injection-Keylogging-C2-Exfiltration-Analysis

GitHubkaandemir993/overlord-rat-reverse-engineering-a-go-based-rat-injection-keylogging-c2-exfiltration-analysis

Full static & memory analysis of Overlord RAT: Go agent architecture, HTTP/2 + WebSocket C2, reflective DLL injection, browser keylogging, and IOCs.…
command-and-controldata-exfiltrationdigital-forensics+6
98 days ago
OpenShell preview

OpenShell

GitHubiss4cf0ng/openshell

Lightweight Go-based reverse shell management server with a web GUI for interactive shell sessions, session management, and multi-tab terminal…
command-and-controlpenetration-testingred-teaming+3
267 months ago
Salat-Stealer-Telegram-Proxy-Decoy-C2-Analysis preview

Salat-Stealer-Telegram-Proxy-Decoy-C2-Analysis

GitHubkaandemir993/salat-stealer-telegram-proxy-decoy-c2-analysis

"Reverse engineering analysis of Salat Stealer, a Go-based info-stealer that uses a Telegram proxy decoy, C2 communication, and encrypted memory…

binary-analysiscommand-and-controleducation+6
53 months ago
Lumma-Stealer-dllhost-Hollowing-C2-Domains-Payload-Extraction-Analysis preview

Lumma-Stealer-dllhost-Hollowing-C2-Domains-Payload-Extraction-Analysis

GitHubkaandemir993/lumma-stealer-dllhost-hollowing-c2-domains-payload-extraction-analysis

In-depth reverse engineering analysis of Lumma Stealer, an info-stealer using process hollowing, Native API calls, and C2 communication. Includes…

binary-analysiscommand-and-controldata-exfiltration+4
111 month ago
Tourmaline preview

Tourmaline

GitHubv-pun215/tourmaline

Reverse engineering notes, deobfuscated source, IOCs, and YARA rules for the Tourmaline ClickFix Python RAT, covering its DNS tunnel and blockchain…

command-and-controlcryptographydigital-forensics+7
111 month ago
Previous123Next