Agent-Tesla-APC-Injection-Token-Manipulation-Registry-Persistence-Analysis

"Reverse engineering analysis of Agent Tesla, a .NET-based info-stealer that uses APC injection, token manipulation, and registry persistence.…

"Reverse engineering analysis of Agent Tesla, a .NET-based info-stealer that uses APC injection, token manipulation, and registry persistence.…

7-Zip XZ Decoder Heap Buffer Overflow - Full analysis, root cause, PoC, and RCE exploitation roadmap

From Solder to Shell: Full Hardware Exploitation of the Linksys WRT54GL Router (CVE-2022-43973)

Master's Thesis research on CVE-2024-51324 (BYOVD). Advanced exploit with 4 operational modes (SCANNER, LOADER, KILLER, CLEANUP), SHA-256 driver…

CVE-2025-14611 CentreStack and Triofox full Poc/Exploit

Educational lab demonstrating a stack buffer overflow (CVE-2025-5548) in FreeFloat FTP Server. Covers full exploit development: vulnerability…

Stack-based buffer overflow in R 3.4.4. Full exploitation on x86, but only RIP control with gadget analysis on x64 due to program constraints. The…

Python Command-Line Ghidra MCP

Headless Binary Ninja MCP server — giving AI agents deep reverse-engineering capabilities via 180 tools.

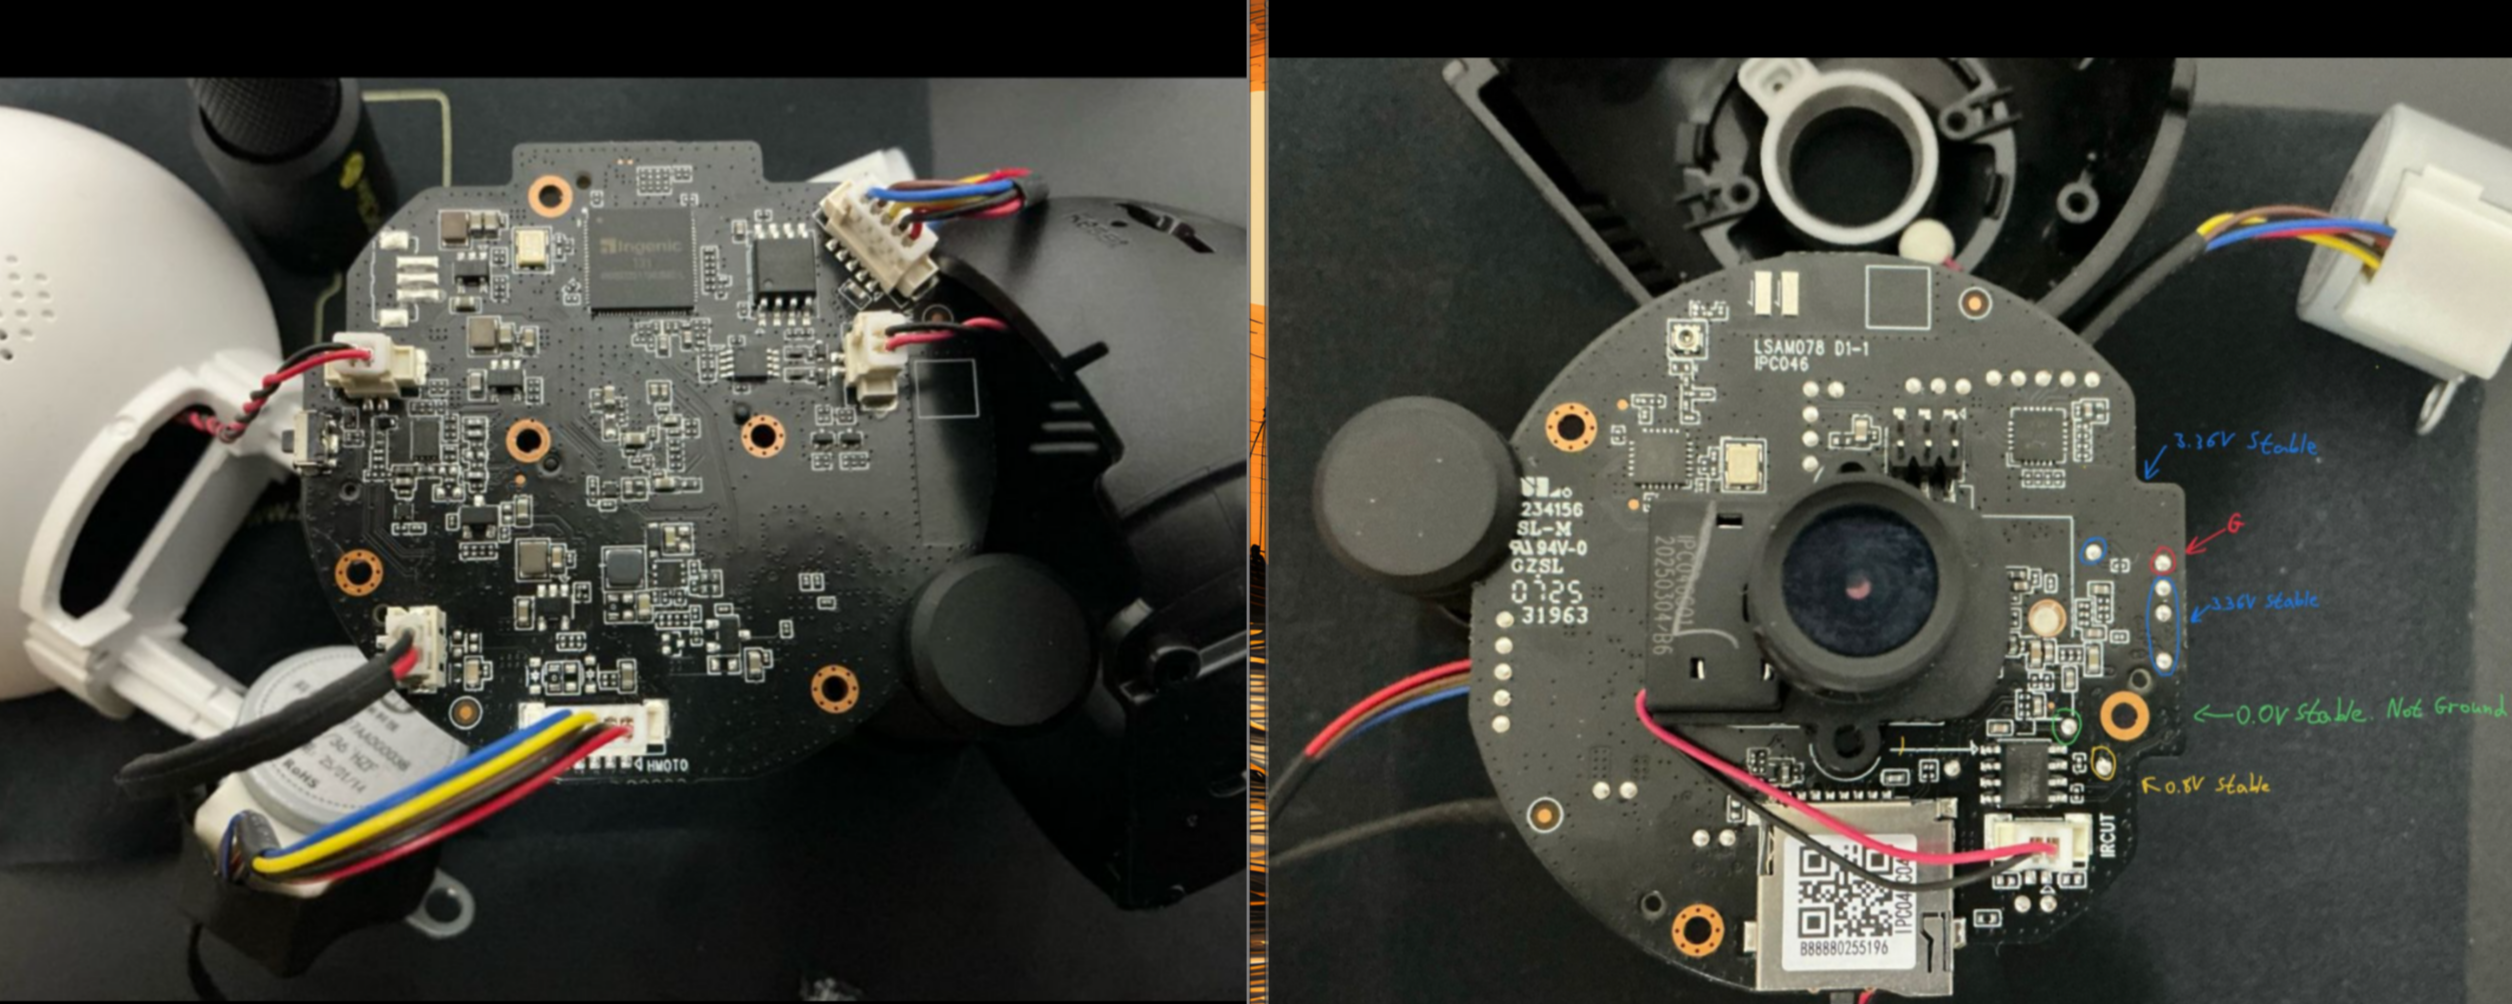
From UART to Root: Breaking Into the Xiaomi C200 via U-Boot

.NET Decompiler with support for PDB generation, ReadyToRun, Metadata (&more) - cross-platform!

MCP server enabling AI agents to autonomously execute 150+ cybersecurity tools for automated penetration testing, vulnerability discovery, bug bounty…

🐬 A collection of awesome resources for the Flipper Zero device.

Some setup scripts for security research tools.

UPX - the Ultimate Packer for eXecutables

Multi-architecture disassembly framework providing a lightweight, thread-safe API for binary analysis, reverse engineering, and malware research…

Program for determining types of files for Windows, Linux and MacOS.

MCP Server for Ghidra