

radare2
 radareorg/radare2
UNIX-like reverse engineering framework and command-line toolset
ai-assisted-reversingandroid-securitybinary-analysis+16
radareorg/radare2UNIX-like reverse engineering framework and command-line toolset
 b2r2-org/b2r2
B2R2 is a fully managed binary analysis framework written in F#. It provides a rich set of algorithms, functions, and tools for reverse engineering,…
 theopolis/uefi-firmware-parser
Parse BIOS/Intel ME/UEFI firmware related structures: Volumes, FileSystems, Files, etc
 kaandemir993/overlord-rat-reverse-engineering-a-go-based-rat-injection-keylogging-c2-exfiltration-analysis
Full static & memory analysis of Overlord RAT: Go agent architecture, HTTP/2 + WebSocket C2, reflective DLL injection, browser keylogging, and IOCs.…
 hugsy/gef
GEF (GDB Enhanced Features) - a modern experience for GDB with advanced debugging capabilities for exploit devs & reverse engineers on Linux
 theqmaks/phantom-frida
Build anti-detection Frida server from source. ~90 patches covering 16 detection vectors, weekly auto-builds with random names.
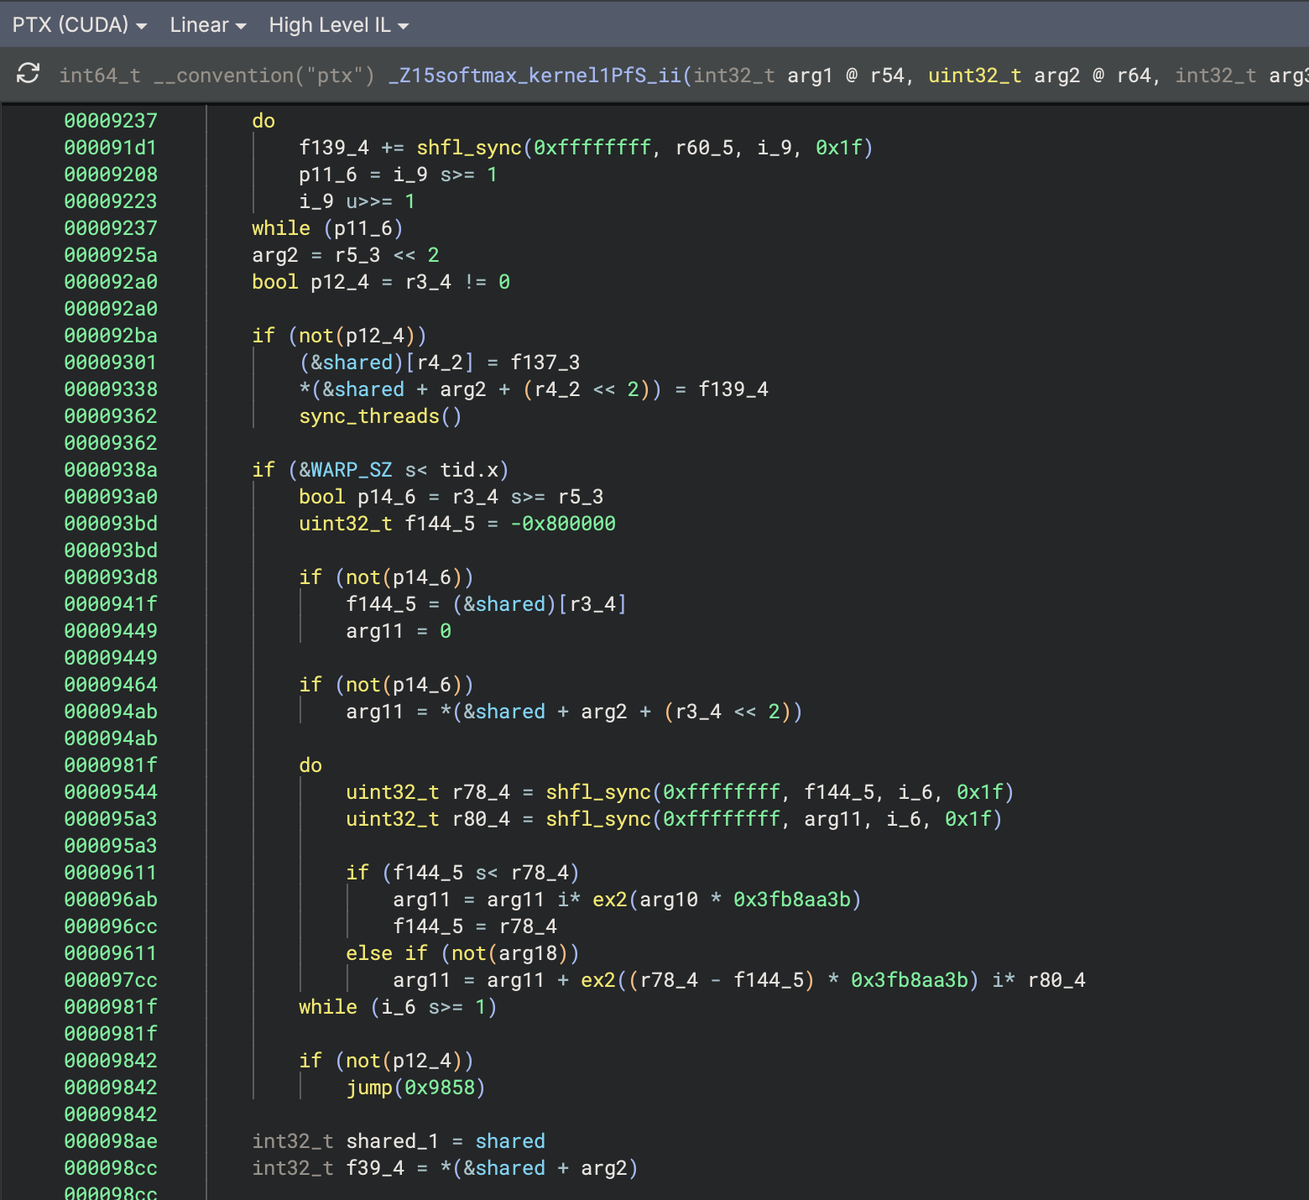 seekbytes/ptxninja
Binary Ninja plugin for reverse engineering PTX -- the virtual instruction set architecture of CUDA-based GPUs.
 bootleg/ret-sync
ret-sync is a set of plugins that helps to synchronize a debugging session (WinDbg/GDB/LLDB/OllyDbg2/x64dbg) with IDA/Ghidra/Binary Ninja…
 h3xdum/xiaomi-c200-firmware-analysis
From UART to Root: Breaking Into the Xiaomi C200 via U-Boot
 nccgroup/blackboxprotobuf
Blackbox Protobuf is a set of tools for working with encoded Protocol Buffers (protobuf) without the matching protobuf definition.
 nmantani/fileinsight-plugins
FileInsight-plugins: decoding toolbox of McAfee FileInsight hex editor for malware analysis
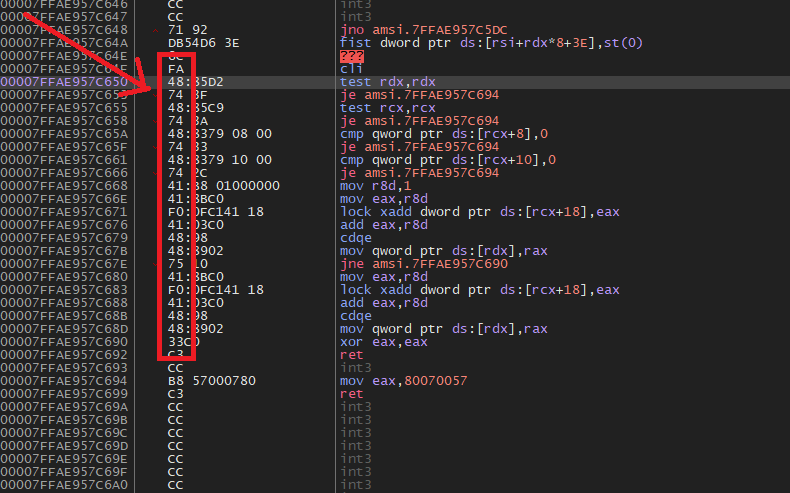 zeromemoryex/amsi-killer
Lifetime AMSI bypass
 duality084/cve-2023-33381-mitrastar-gpt-2741gnac
Proof-of-concept exploit for OS command injection (CVE-2023-33381) in MitraStar GPT-2741GNAC routers. Demonstrates bypass of restricted shell via…
 withsecurelabs/garbageman
GarbageMan is a set of tools for analyzing .NET binaries through heap analysis.
 gmh5225/no-access-protection-x86
It encrypts the text section and set the protection to NO_ACCESS.
 denuvosoftwaresolutions/simba
Efficient Deobfuscation of Linear Mixed Boolean-Arithmetic Expressions
 nccgroup/asafw
Set of scripts to deal with Cisco ASA firmware [pack/unpack etc.]
 k3vinlusec/r7000_httpd_bof_cve-2020-15416
Walkthrough of CVE-2020-15416 buffer overflow exploit for Netgear R7000 router, including QEMU user-mode debugging environment setup and detailed…