

pwndbg
 pwndbg/pwndbg
Exploit Development and Reverse Engineering with GDB & LLDB Made Easy
ai-assisted-reversingbinary-analysisbinary-exploitation+12
pwndbg/pwndbgExploit Development and Reverse Engineering with GDB & LLDB Made Easy
 radareorg/r2ai
Radare2 AI plugin using local or remote LLMs for decompilation, function explanation, vulnerability detection, renaming, and scripted reverse…
 nationalsecurityagency/ghidra
Ghidra is a software reverse engineering (SRE) framework
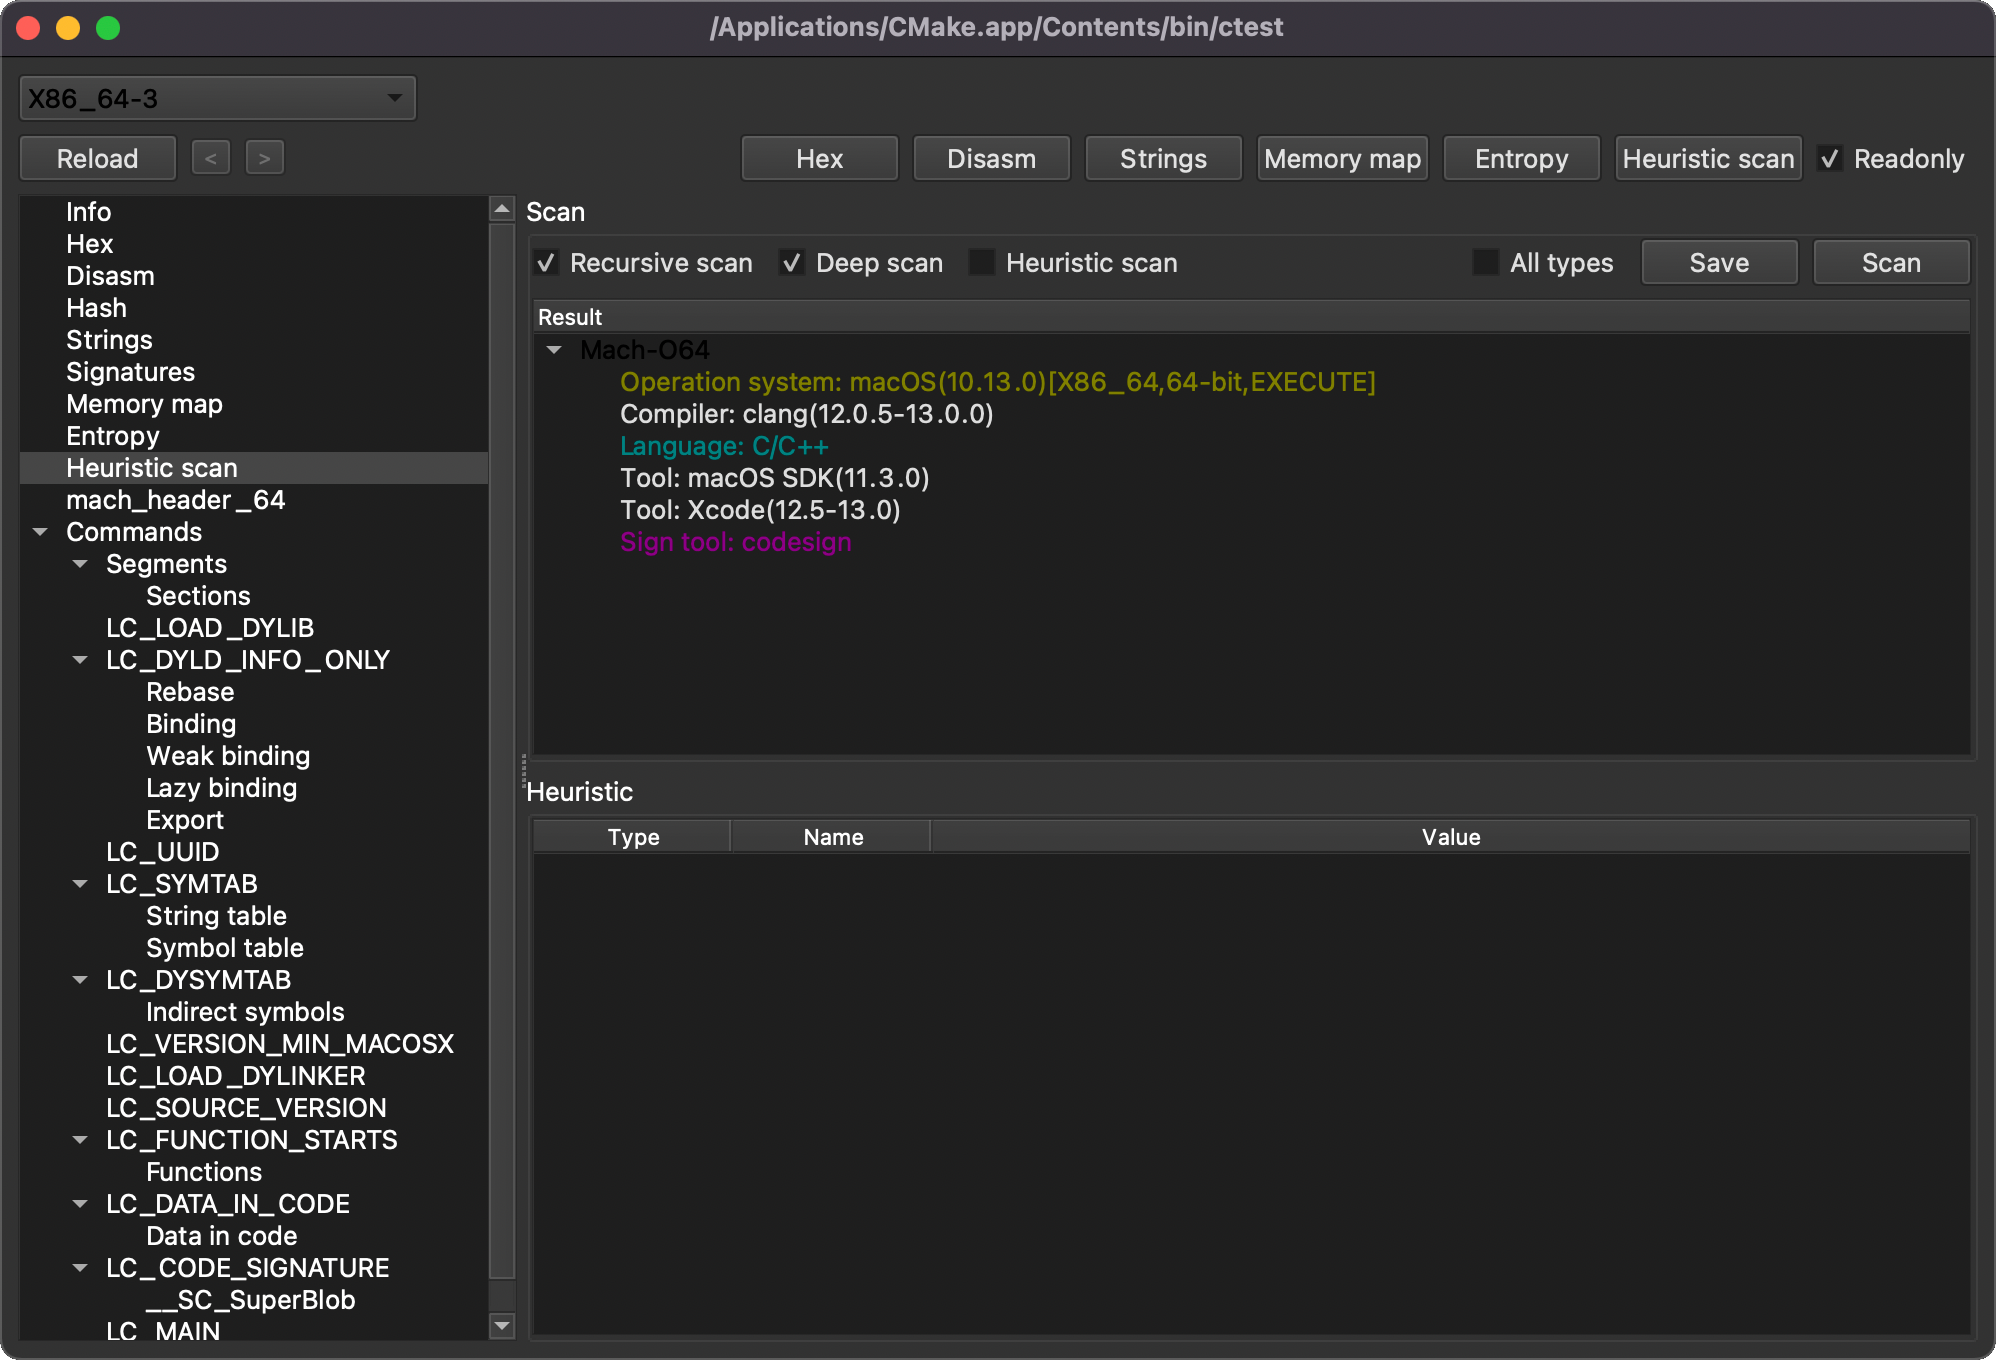 horsicq/xmachoviewer
XMachOViewer is a Mach-O viewer for Windows, Linux and MacOS
 cristianzsh/freki
Open-source malware analysis platform with static PE analysis, YARA pattern matching, VirusTotal integration, REST API, and Docker deployment for…
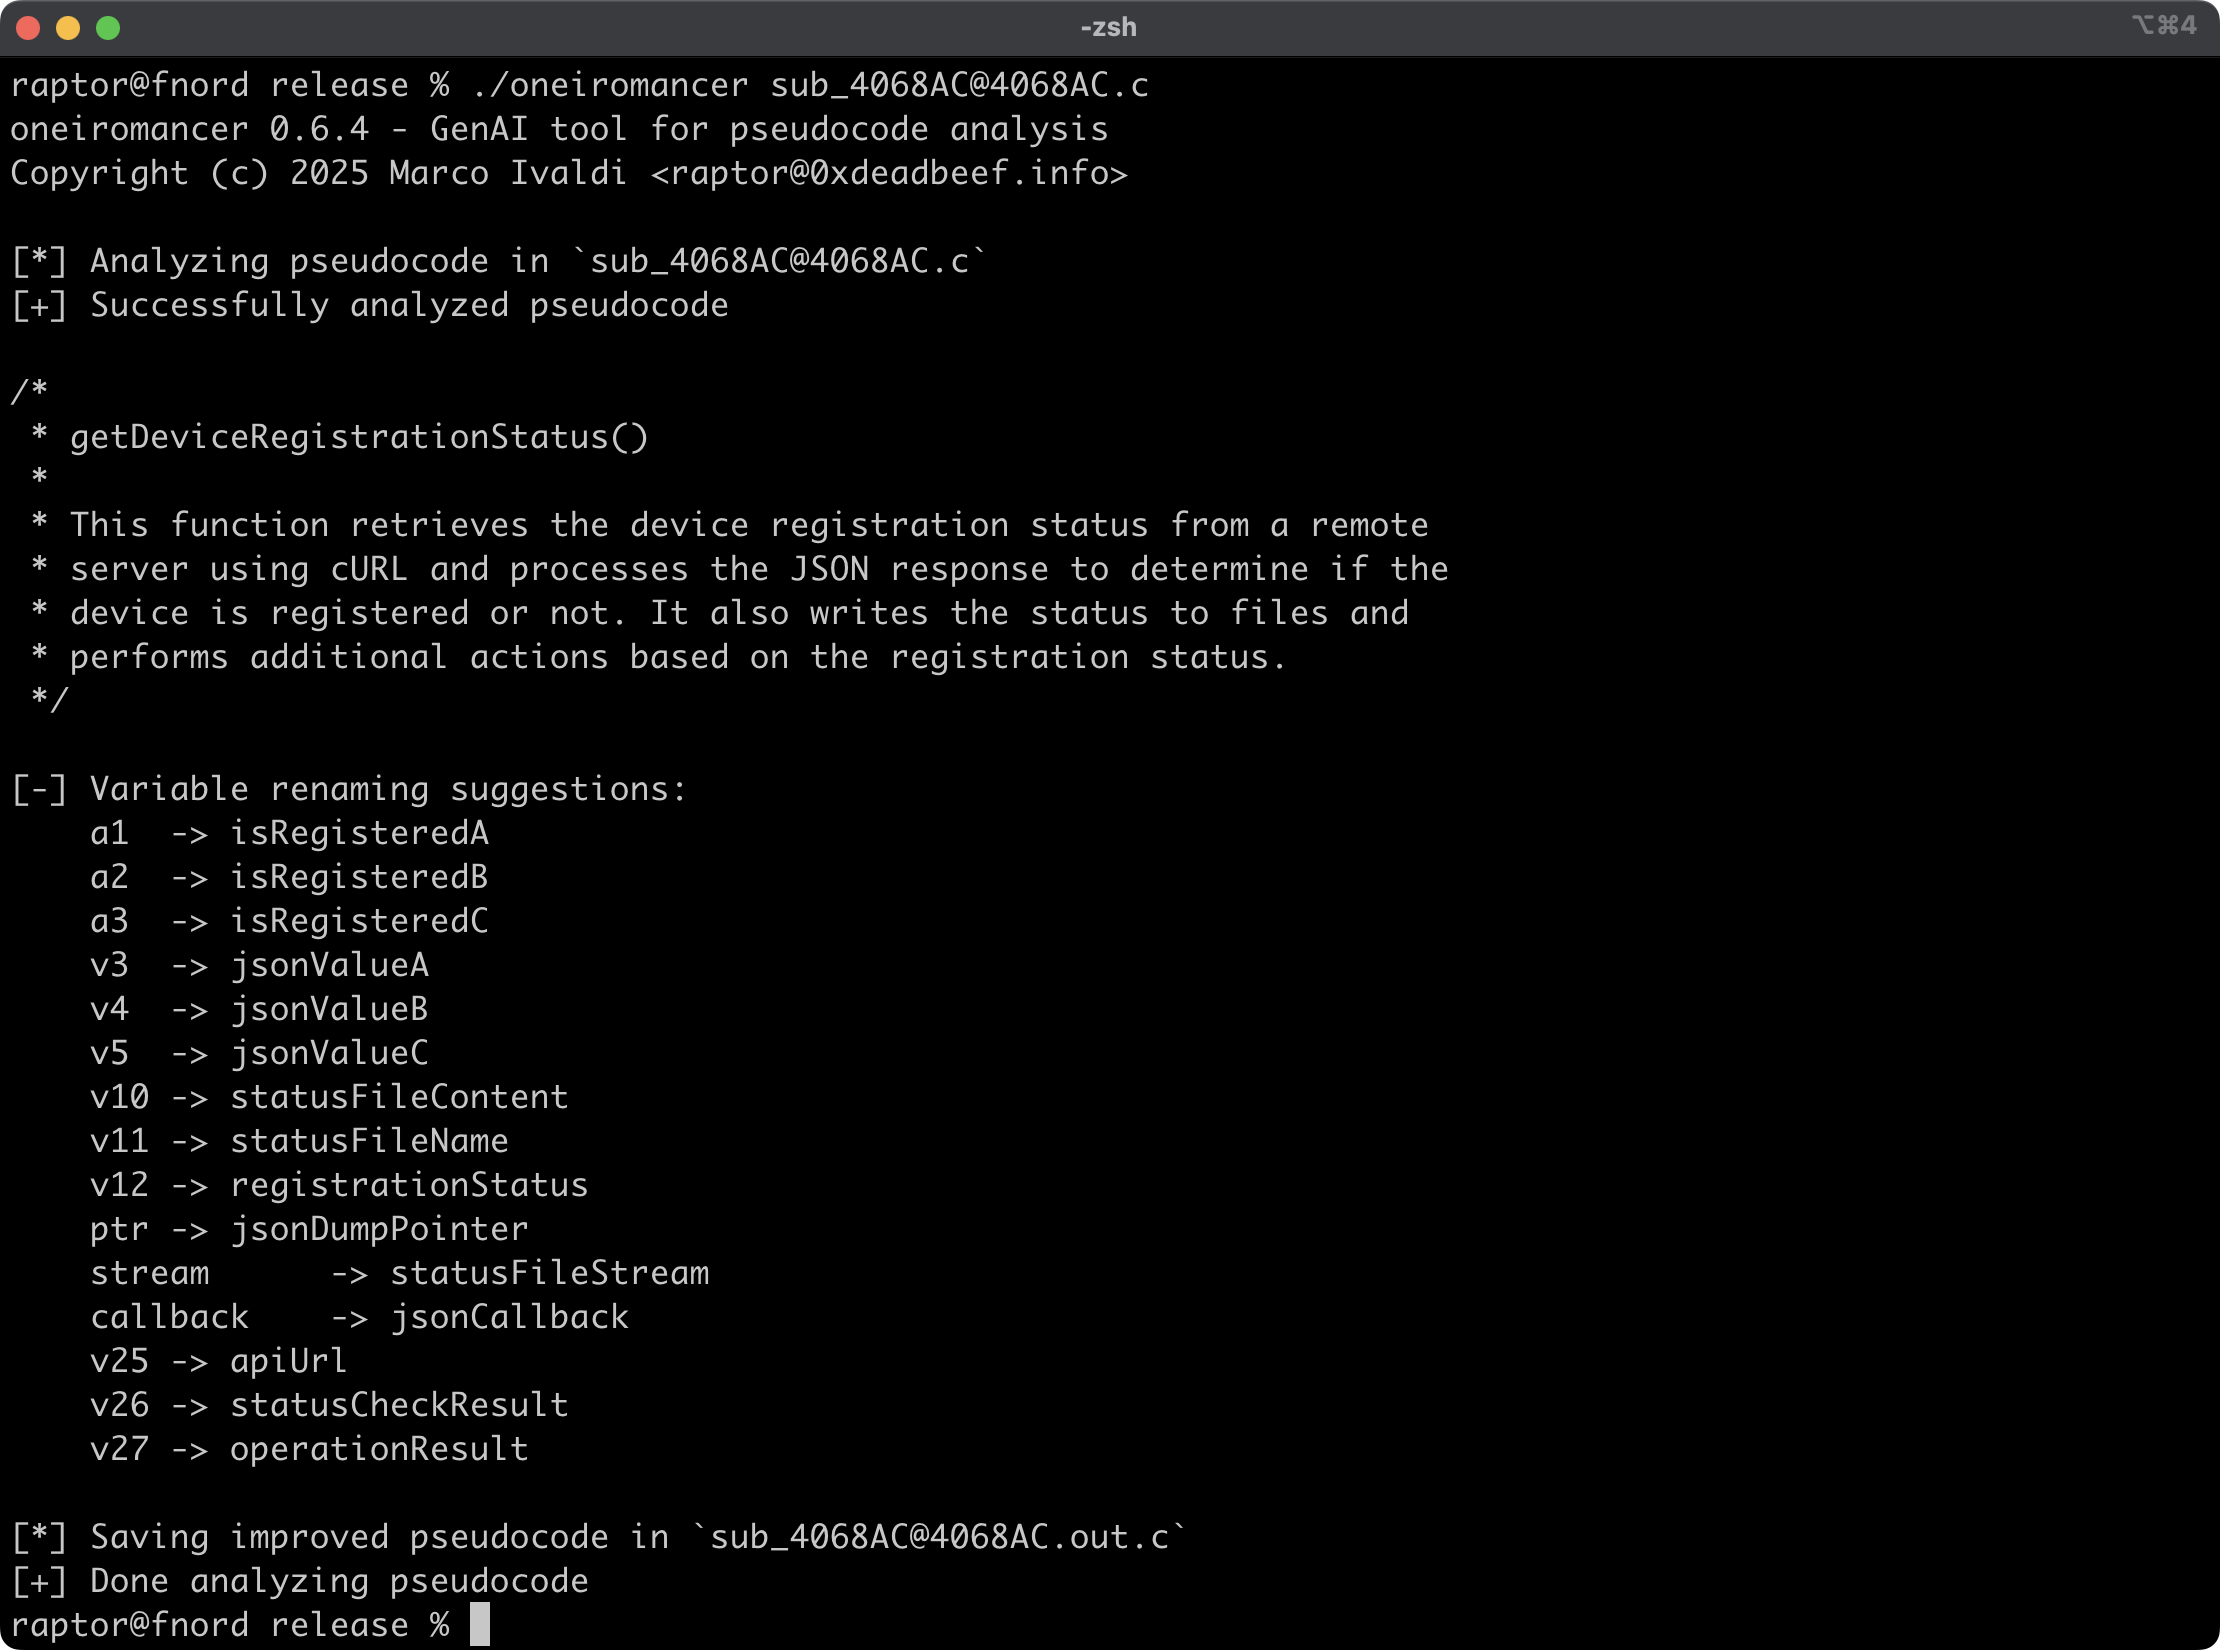 0xdea/oneiromancer
Reverse engineering assistant that uses a locally running LLM to aid with pseudocode analysis.
 yaklang/javajive
Pure-Go Java Decompiler and Serialization Operator
 nemo22/retrokit
Headless-Ghidra toolkit for reverse engineering 32-bit DOS and Win32 games (1993-2010): own LE/LX loader, Watcom calling conventions, library…
 adriancable/eternal
Minimal machine architecture with LLVM compiler backend, Linux port, and virtual machine for creating self-contained software capsules that remain…
 hasherezade/pe-bear
Portable Executable reversing tool with a friendly GUI
 erocarrera/pefile
pefile is a Python module to read and work with PE (Portable Executable) files

 clearbluejar/pyghidra-mcp
Python Command-Line Ghidra MCP
 mandiant/flare-vm
A collection of software installations scripts for Windows systems that allows you to easily setup and maintain a reverse engineering environment on…
 quarkslab/conf-presentations
Quarkslab conference talks
 devploit/awesome-ctf-resources
A list of Capture The Flag (CTF) frameworks, libraries, resources and software for started/experienced CTF players 🚩
 glmcdona/process-dump
Windows tool for dumping malware PE files from memory back to disk for analysis.
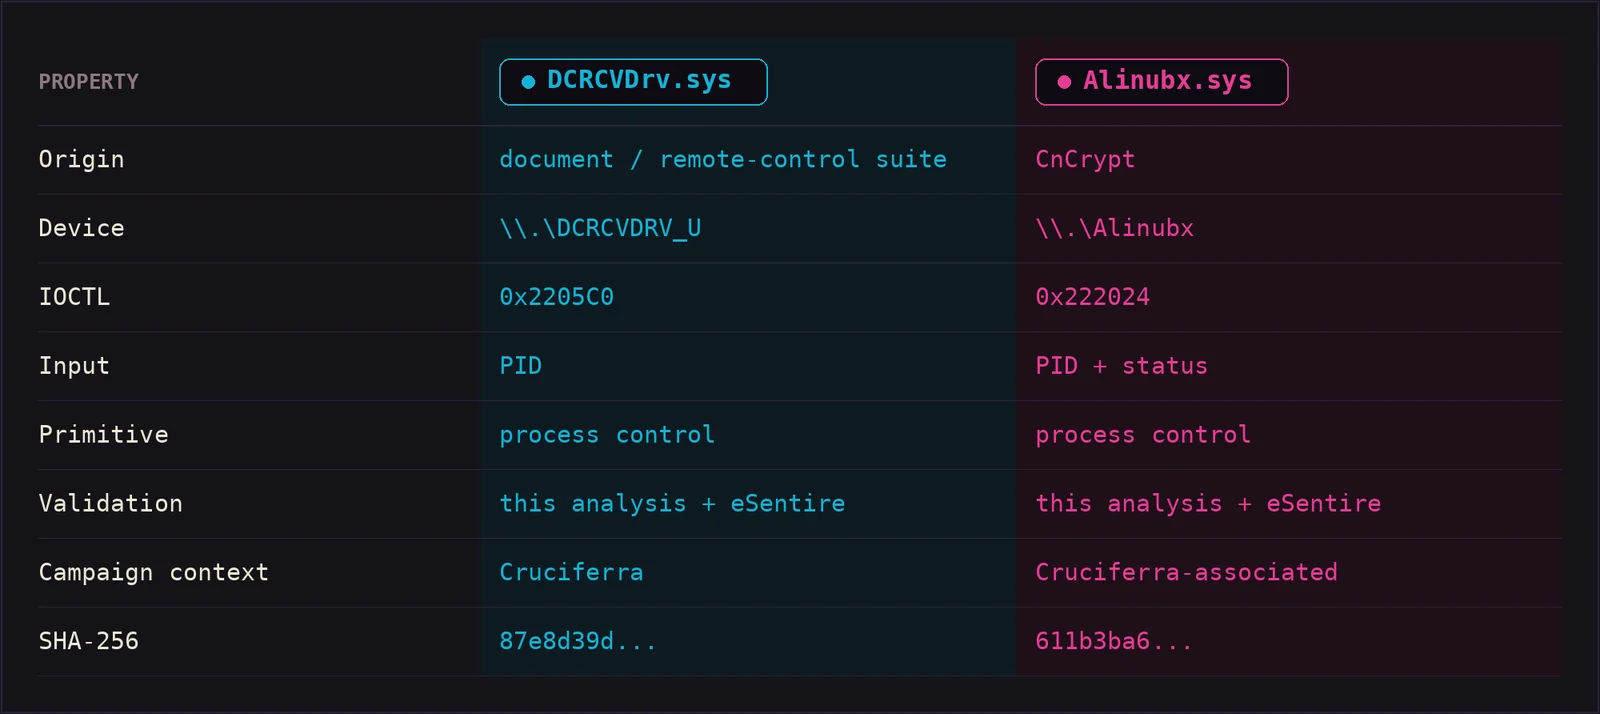 deathshotxd/0xcr0sscrush
Windows BYOVD research on DCRCVDrv.sys and Alinubx.sys, reverse engineering their kernel primitives, IOCTL surfaces, and detection opportunities.