
B2R2
 b2r2-org/b2r2
B2R2 is a fully managed binary analysis framework written in F#. It provides a rich set of algorithms, functions, and tools for reverse engineering,…
binary-analysisdynamic-analysis-sandboxingeducation+4
459
b2r2-org/b2r2B2R2 is a fully managed binary analysis framework written in F#. It provides a rich set of algorithms, functions, and tools for reverse engineering,…
 nationalsecurityagency/ghidra
Ghidra is a software reverse engineering (SRE) framework
 dynamorio/dynamorio
Runtime instrumentation framework for building dynamic analysis tools: tracing, profiling, code coverage, memory debugging, fuzzing, and disassembly…
 capstone-engine/capstone
Multi-architecture disassembly framework providing a lightweight, thread-safe API for binary analysis, reverse engineering, and malware research…
 angr/angr
A powerful and user-friendly binary analysis platform!
 radareorg/radare2
UNIX-like reverse engineering framework and command-line toolset
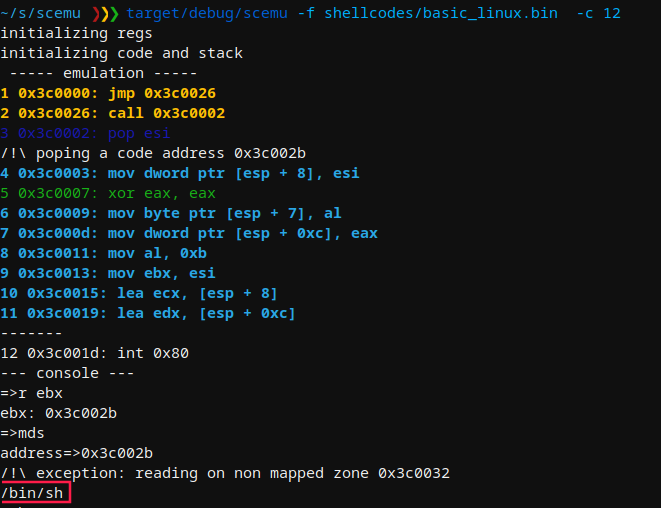 mwemuorg/mwemu
Pure Rust x86 hardware emulator and Windows process simulator for malware analysis, shellcode emulation, and payload unpacking. Supports 32/64-bit PE…
 mandiant/speakeasy
Windows malware emulation framework that executes binaries, drivers, and shellcode in a modeled runtime, emulating APIs, process/thread behavior,…
 yaklang/yakit
All-in-one penetration testing platform with MITM proxy, web fuzzer, reverse connection handler, and plugin system for automated security testing and…
 gallopsled/pwntools
CTF framework and exploit development library
 ainfosec/fissure
The RF and reverse engineering framework for everyone. Follow and ★ to show your support!
 416rehman/deepzero
Find zero-days while you sleep. DeepZero is an automated vulnerability research framework that parses, decompiles, and analyzes thousands of Windows…
 cea-sec/miasm
Reverse engineering framework in Python
 ch0pin/rdx
A native APK and DEX decompiler written in Rust
 revng/revng
Open source binary analysis framework and decompiler built on LLVM and QEMU, lifting binaries to a readable intermediate representation for reverse…
 sensepost/objection
Frida-powered runtime mobile exploration toolkit for assessing iOS and Android app security. Bypass SSL pinning, dump keychains, manipulate heap…
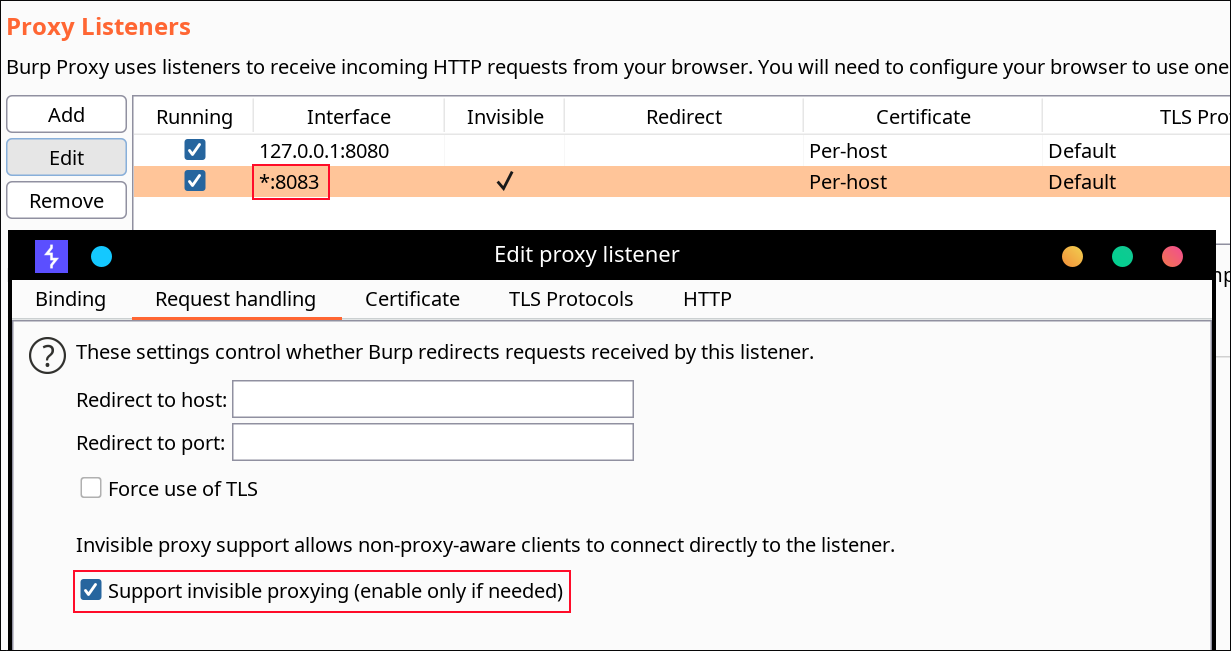 impact-i/reflutter
Patches Flutter engine libraries to enable runtime reverse engineering, traffic interception, and SSL pinning bypass for Android and iOS apps without…
 syscallx-18113/apkx-hunter
C-based Android static analysis framework for decompilation, secret detection, endpoint discovery, permission analysis, and native library scanning…