
conf-presentations
 quarkslab/conf-presentations
Quarkslab conference talks
bluetooth-securitycryptographycurated-resources+6
319
quarkslab/conf-presentationsQuarkslab conference talks
 joshuapassos/cmf-watch-pro-2-ble-protocol
Reverse-engineered BLE protocol for the CMF Watch Pro 2, documenting GATT layout, AES-128-CBC encrypted command frames, authentication handshake, and…
 adrihd/shiningappmask-reverseengineering
Reverse Engineering of the Shining App Mask
 jopohl/urh
Universal Radio Hacker: Investigate Wireless Protocols Like A Boss
 bin4ry/unipwn
BLE exploit framework for Unitree robots: command injection via hardcoded AES keys enables remote takeover, payload injection, and wormable…
 iot-ptv/iot-pt-v1
A Virtual environment for Pentesting IoT Devices
 cosmic-zip/witchcraft
WITCHCRAFT is a cyberdeck toolkit built for runners who dive deep into the mesh. It’s your all-in-one rig for data-ghosting, ICE-breaking, and…
 spiralbl0ck/cabir_analysis
cabin partial analysis
 antoinet/obike
Reverse engineering of the oBike protocol communication (BLE and HTTP)
 seemoo-lab/fitness-app
BLE-based Fitbit research tool for authentication replay, encrypted activity dump decryption, memory/firmware extraction, and custom firmware…
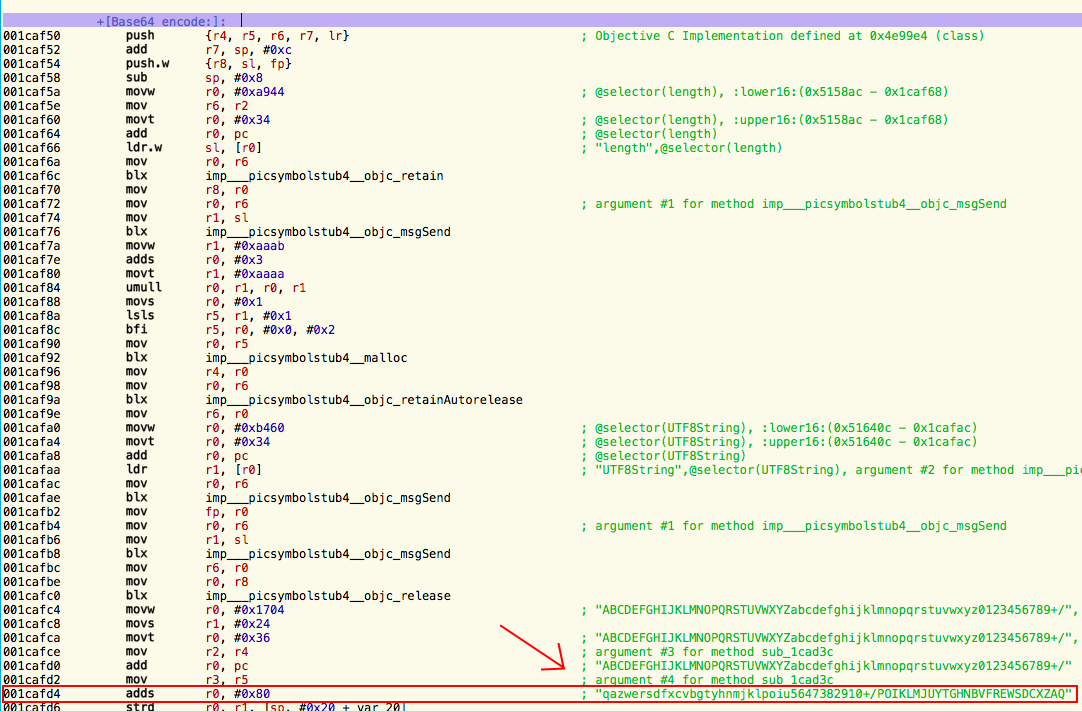 jasondoyle/komfy-switch-wifi-password-disclosure
Proof-of-concept and writeup showing how to retrieve Wi-Fi SSID/password from a D-Link Komfy smart switch over BLE by reversing the iOS app’s custom…