

hexvero
 maximilianfeix/hexvero
Know what changed inside your Electron release: diff two builds for IPC, preload, windows, fuses and hosts, with file:line. CLI, CI gate, MCP server.
ai-securityandroid-securitybinary-analysis+9
8
maximilianfeix/hexveroKnow what changed inside your Electron release: diff two builds for IPC, preload, windows, fuses and hosts, with file:line. CLI, CI gate, MCP server.
 reverserid/jurig
a fully autonomous AI agent for reverse engineering
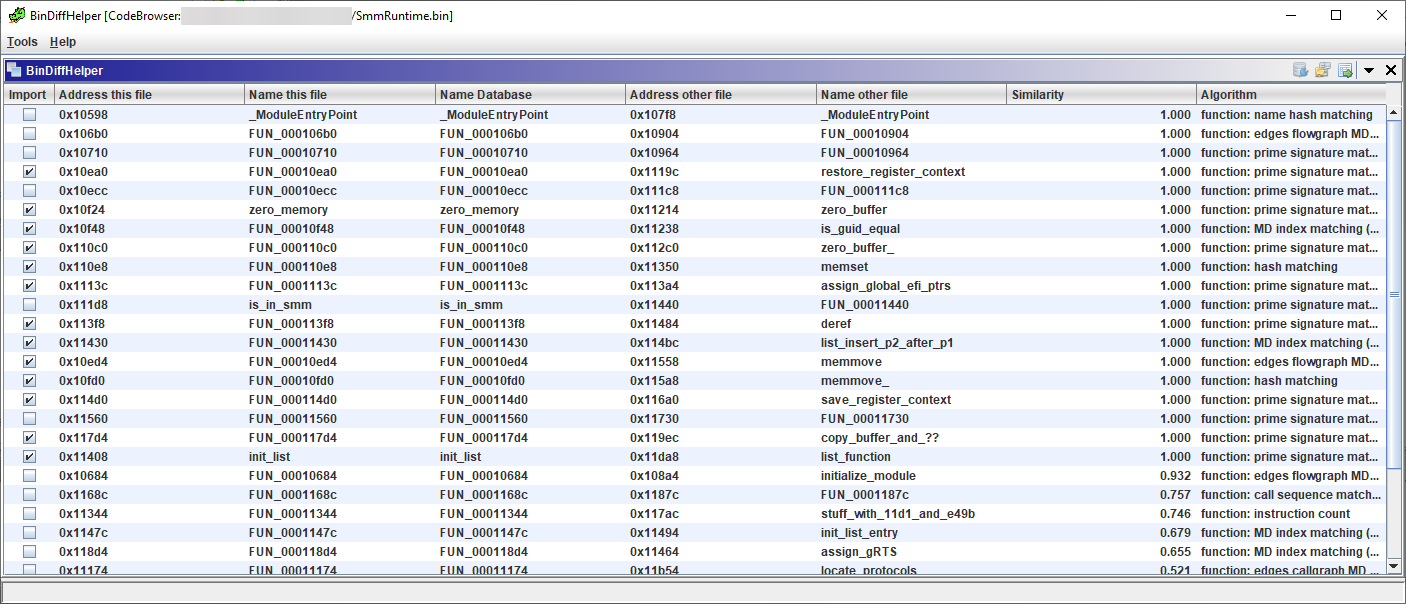 ubfx/bindiffhelper
Ghidra Extension to integrate BinDiff for function matching
 1-3-7/disrobe
Rust CLI suite that statically decompiles, deobfuscates, and unpacks native code, bytecode, scripts, firmware, and app packages across 15+ ecosystems…
 wxxsfxyzm/ghostlock-galaxy
Root your Galaxy using CVE-2026-43499
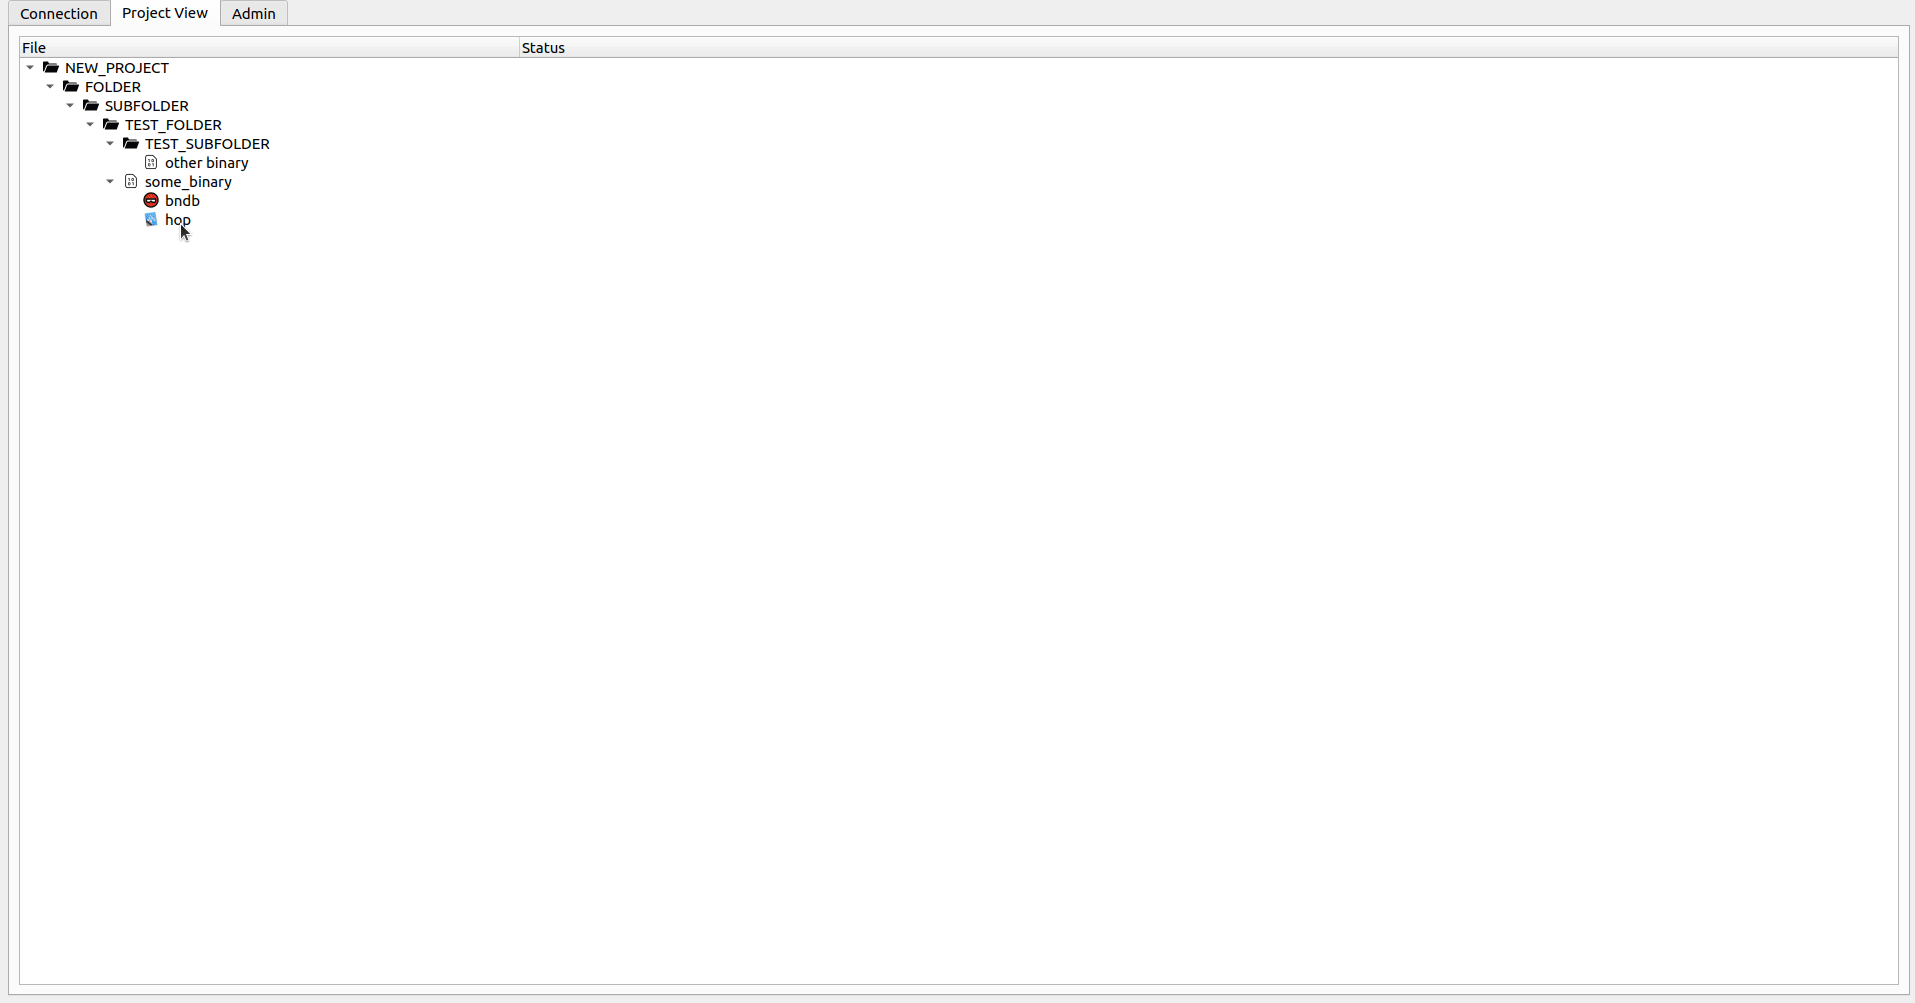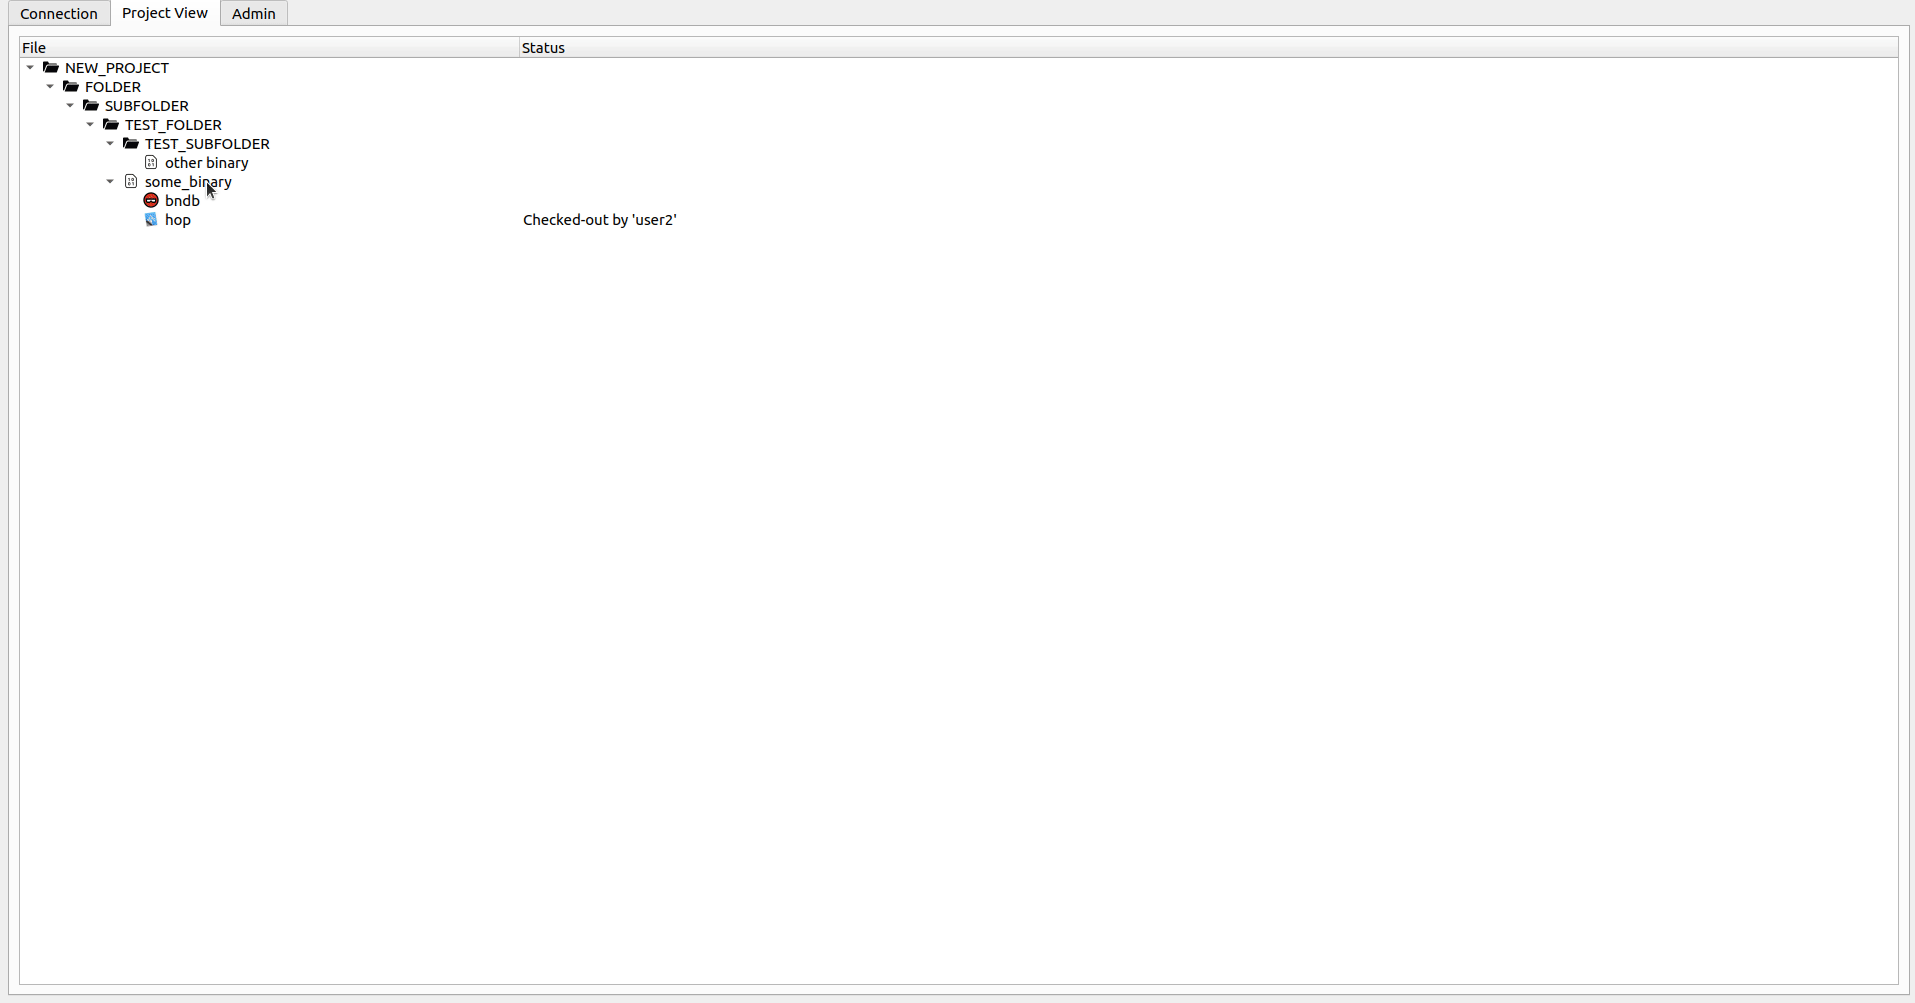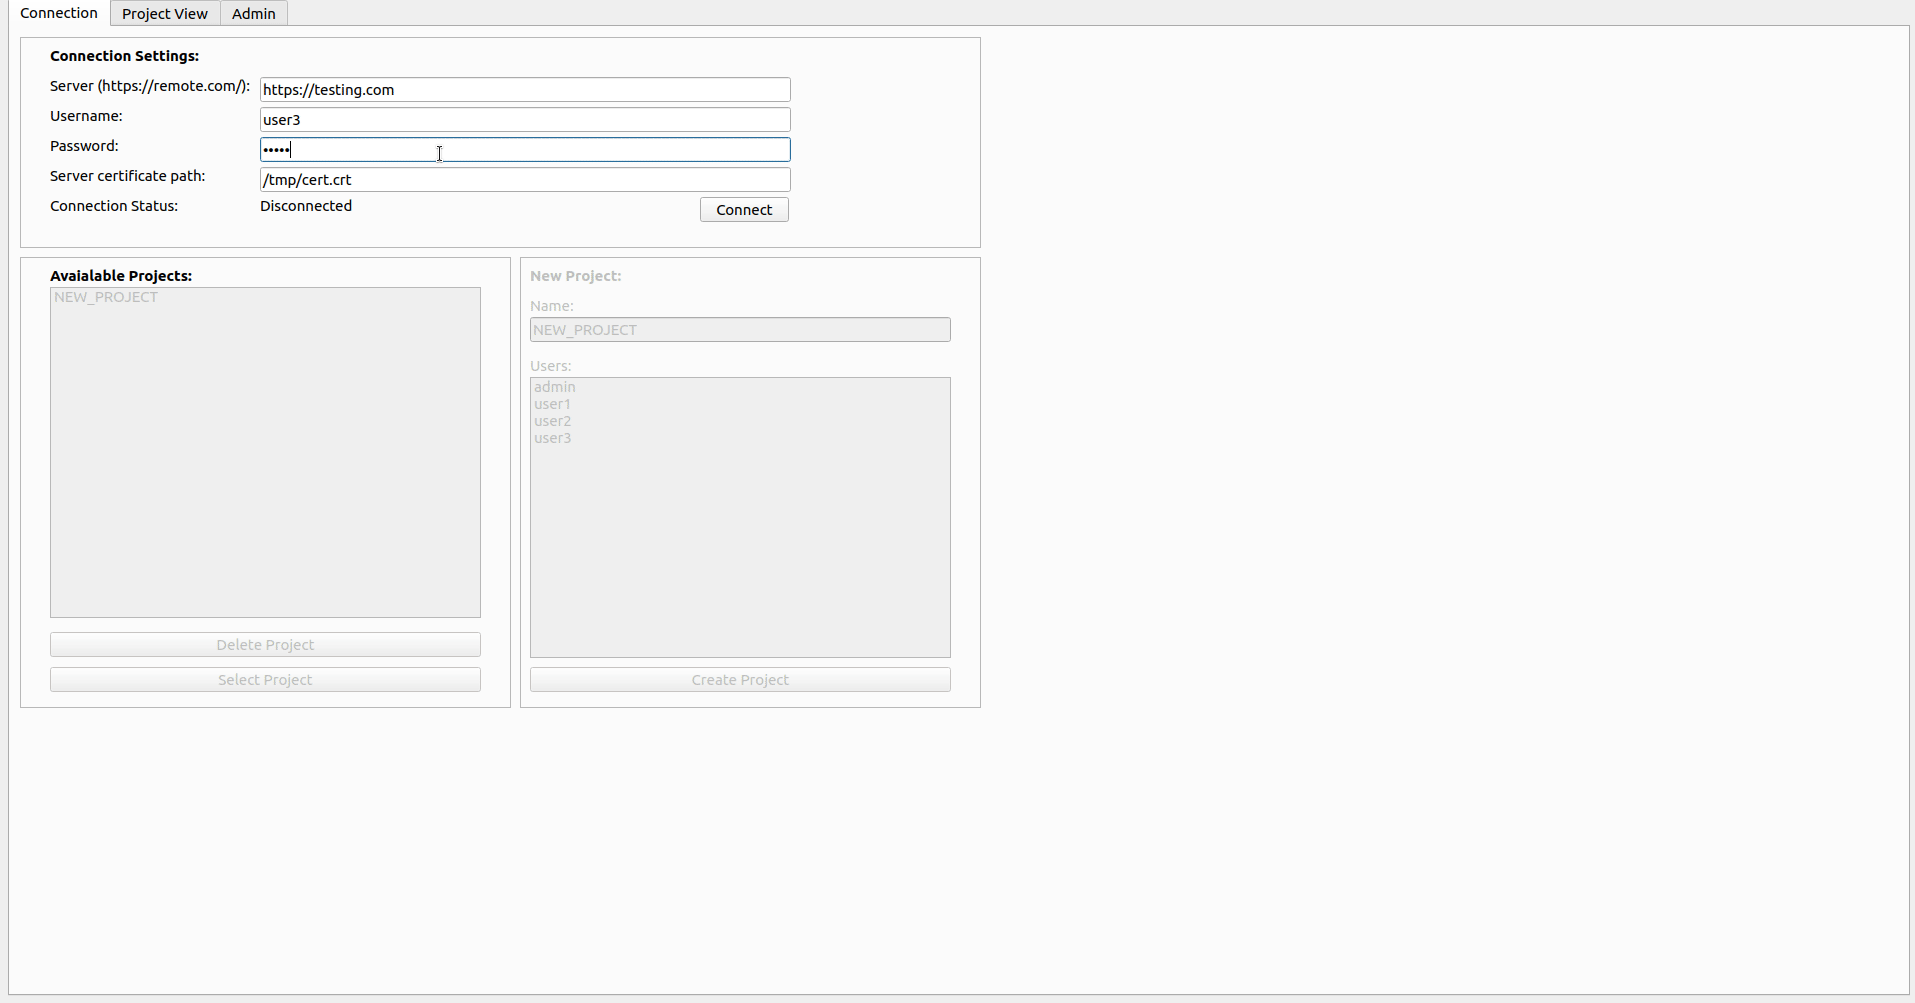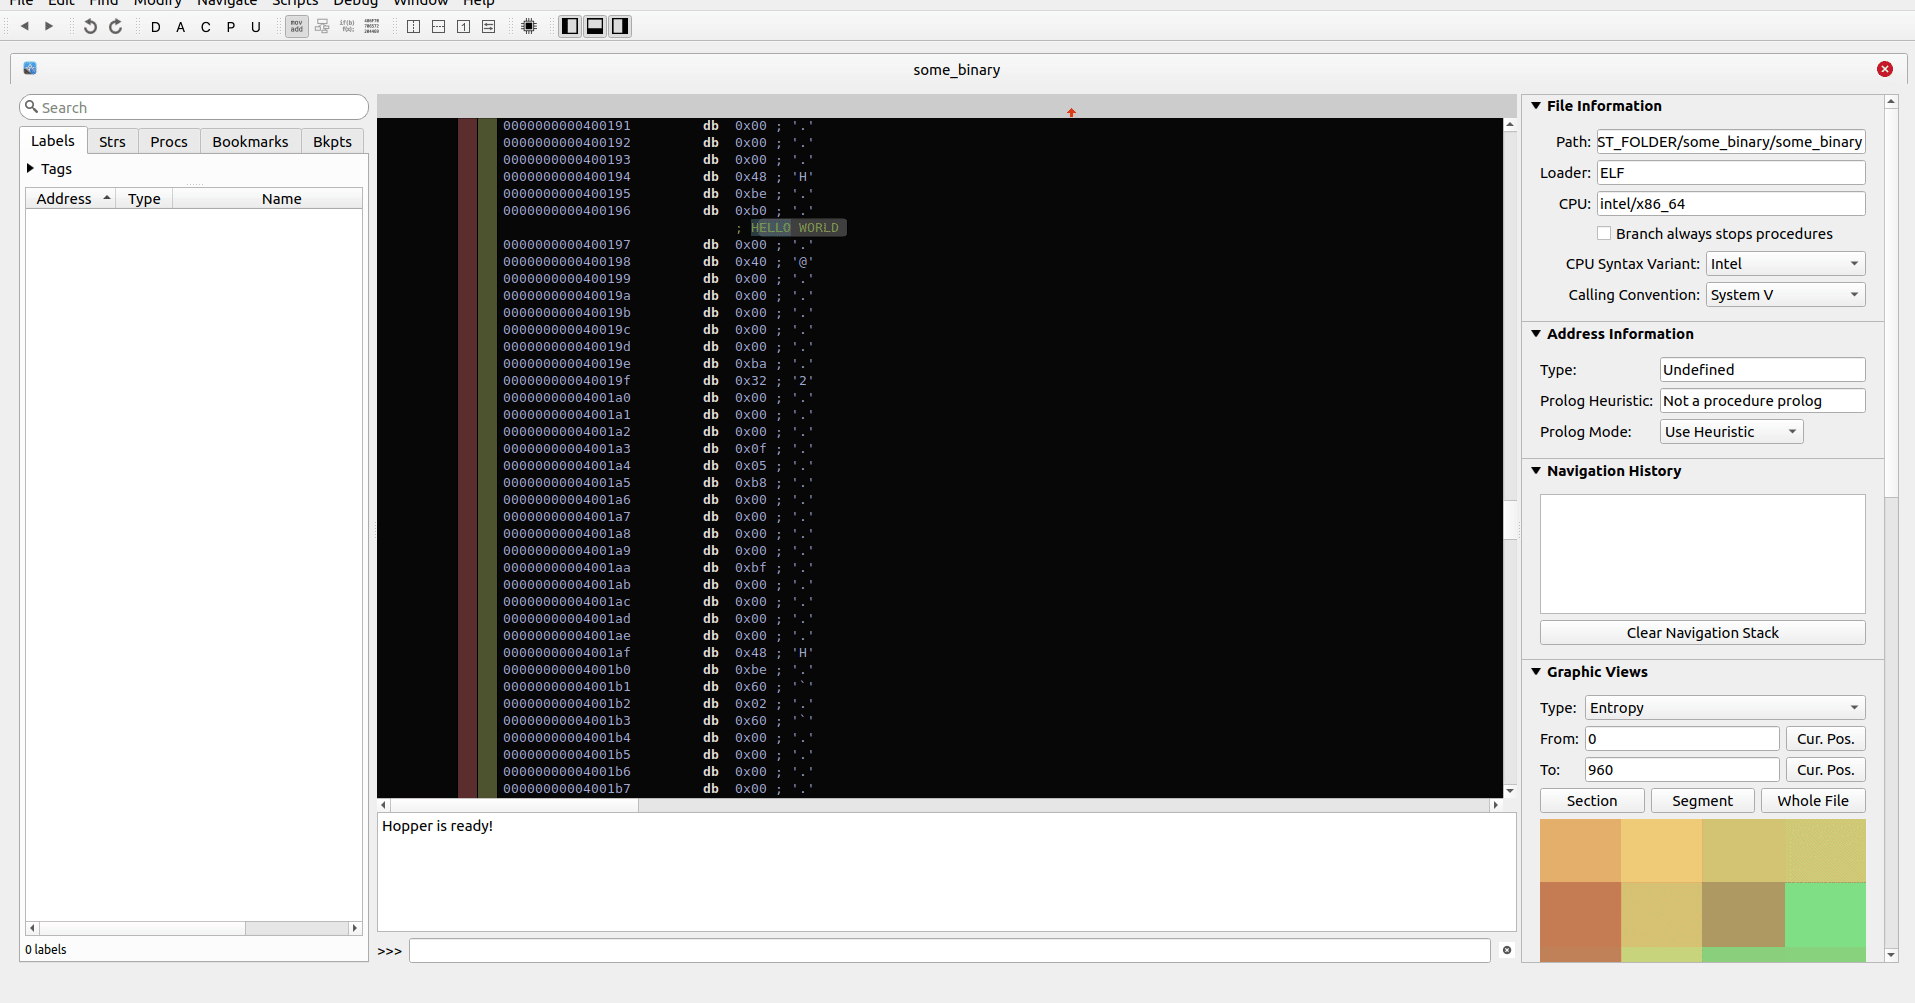 martyx00/collare
Multi-tool reverse engineering collaboration solution.
 fabrimagic72/malware-samples
A collection of malware samples caught by several honeypots i manage
 nnonickreal/openqore
unleash the full power of your BES-based headphones! :)
 therealjunior/mtk-su-reverse-cve-2020-0069
reversing mtk-su
 devianntsec/cve-2024-51324
Master's Thesis research on CVE-2024-51324 (BYOVD). Advanced exploit with 4 operational modes (SCANNER, LOADER, KILLER, CLEANUP), SHA-256 driver…
 inartin/365cam-stream
Local streaming tool for cheap WiFi cameras that bypasses cloud services and phone apps. Discovers cameras on your network, authenticates via PPPP…
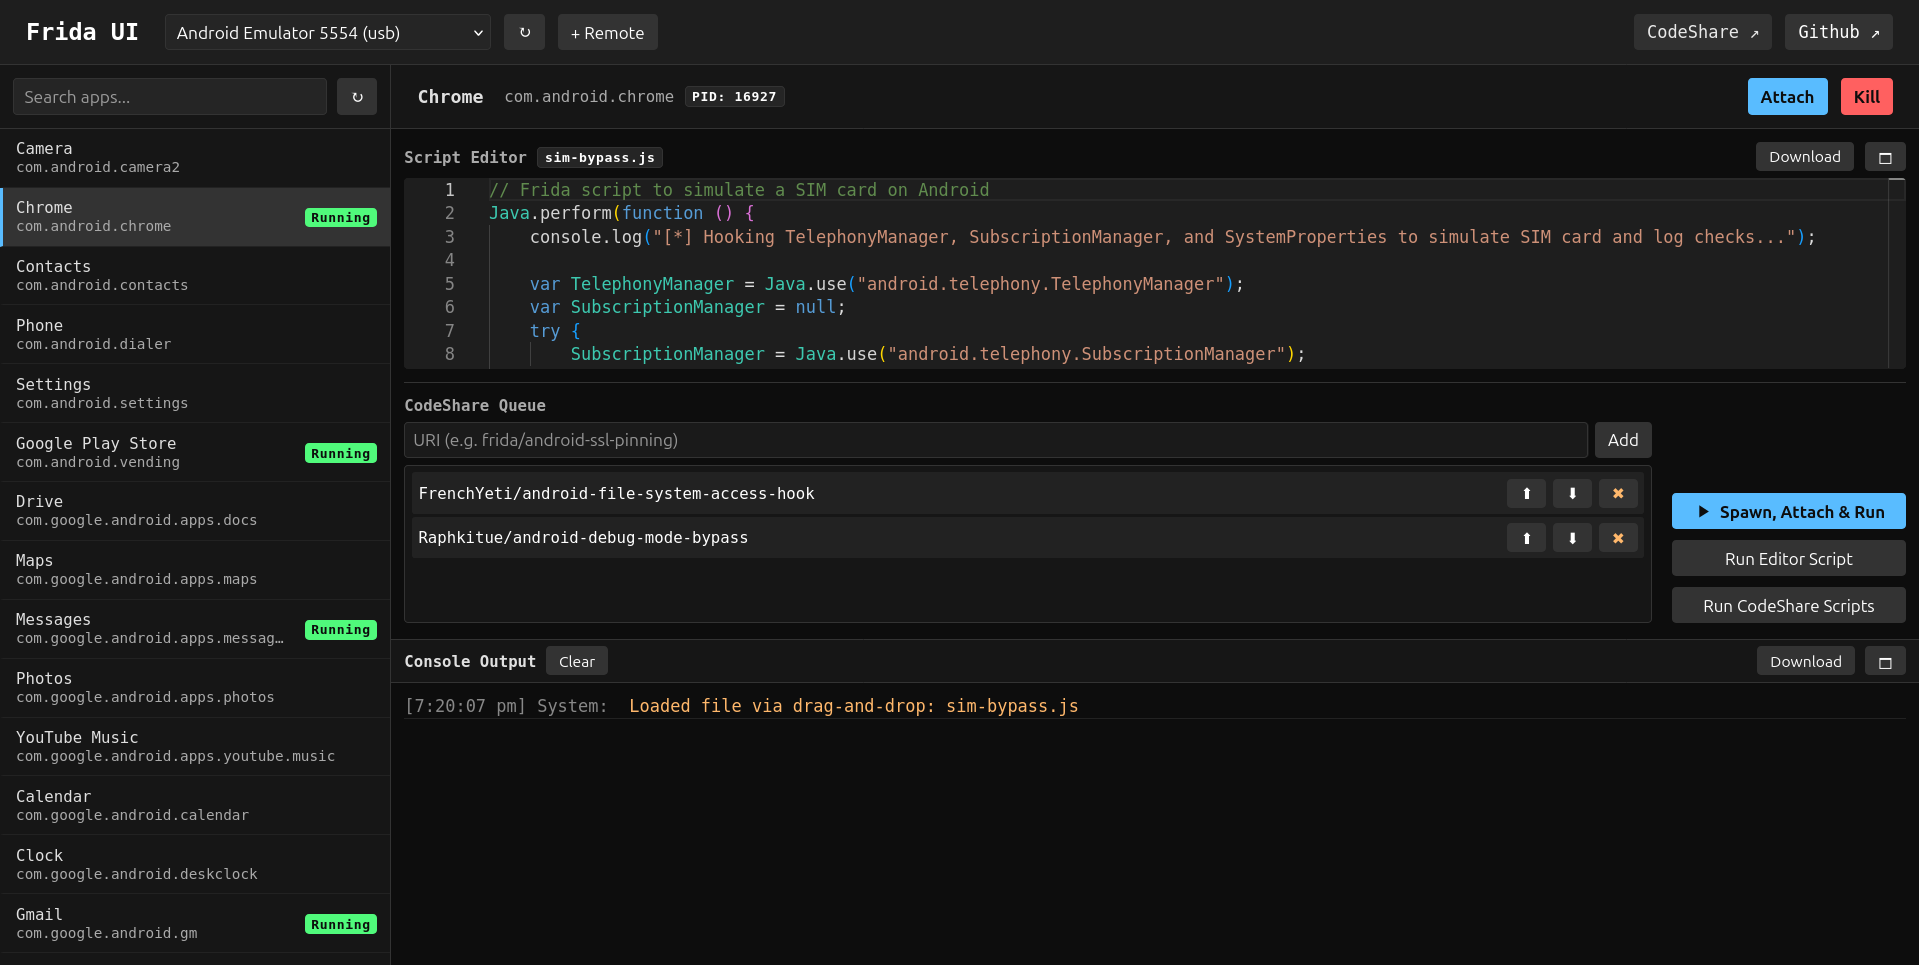 adityatelange/frida-ui
Interact with Frida devices, processes, and scripts directly from your browser.
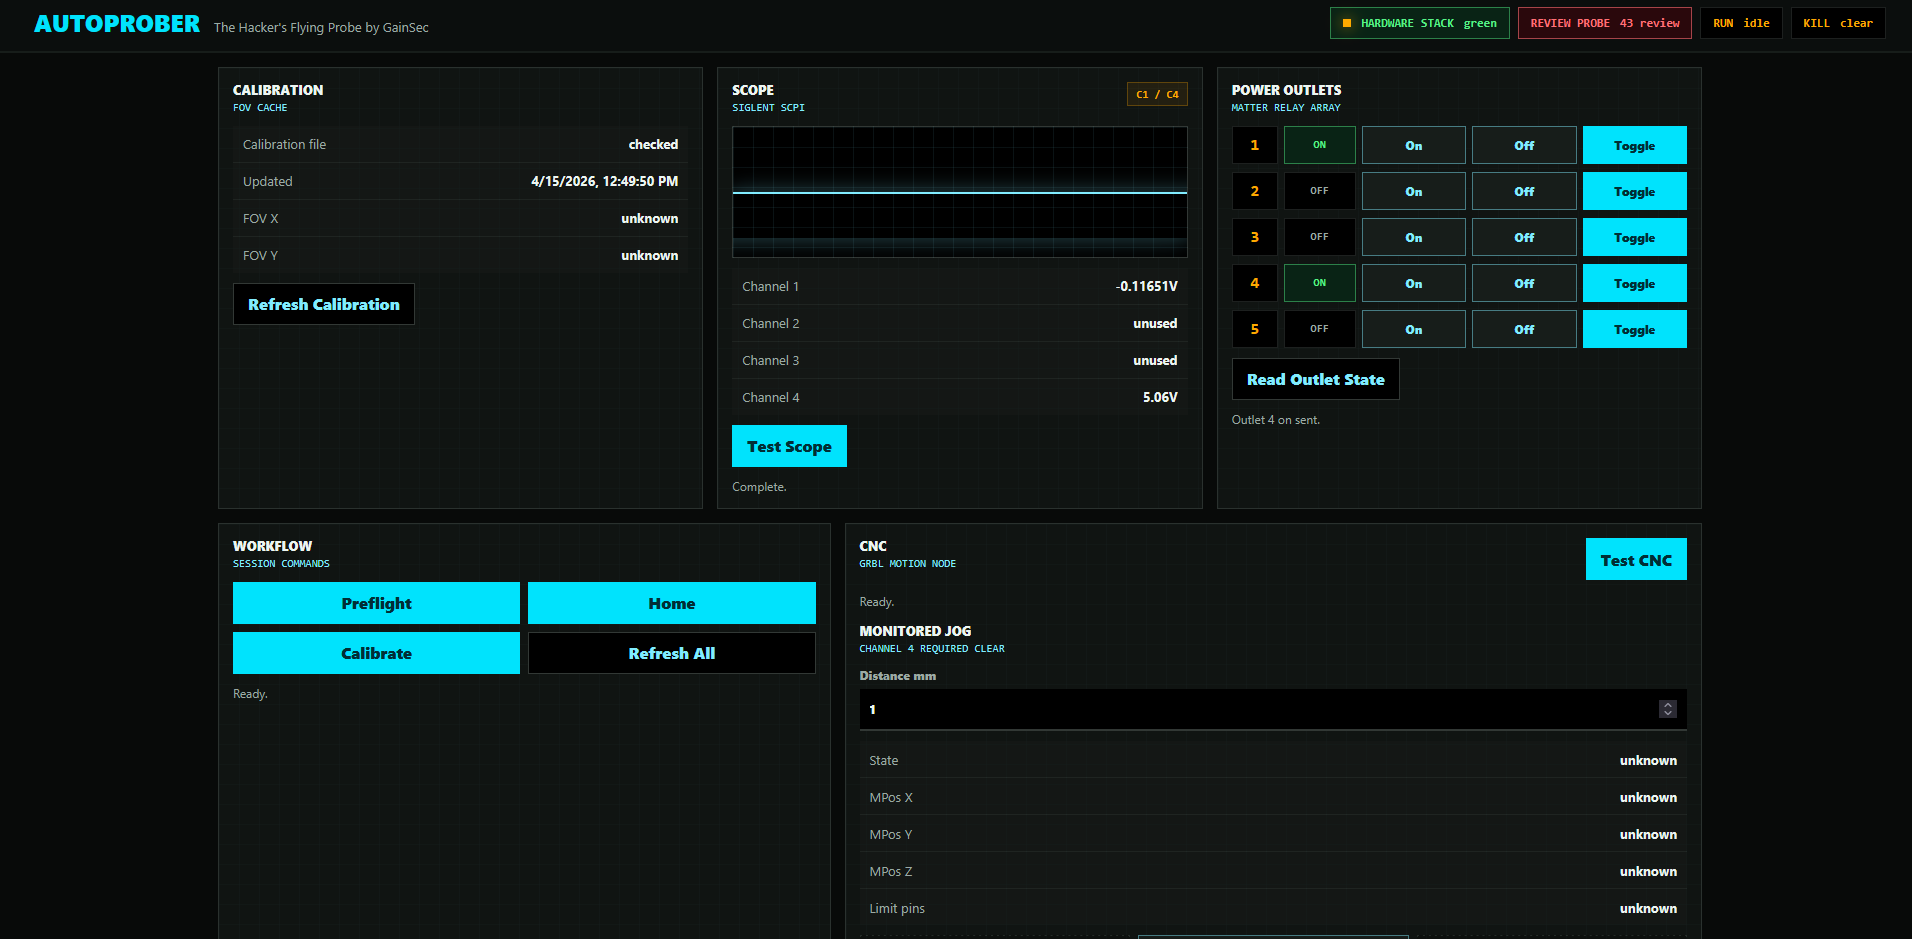 gainsec/autoprober
Hardware hacker’s flying probe automation stack for agent-driven target discovery, microscope mapping, safety-monitored CNC motion, probe review,…
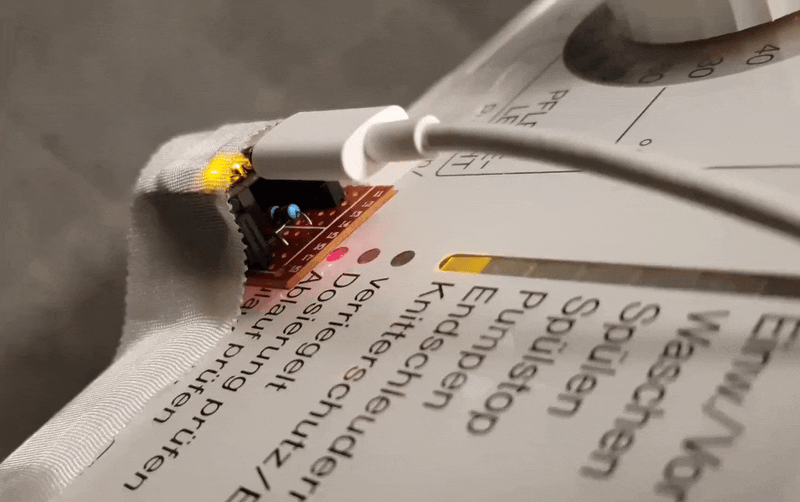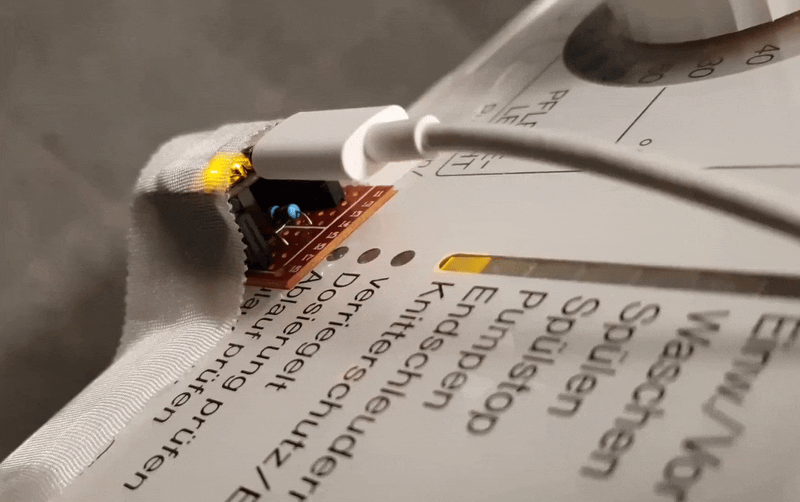 medusalix/freemdu
Open hardware and software tools for communicating with Miele appliances via their optical diagnostic interface
 sensepost/objection
Frida-powered runtime mobile exploration toolkit for assessing iOS and Android app security. Bypass SSL pinning, dump keychains, manipulate heap…
 jonathansalwan/ropgadget
Search for ROP gadgets in ELF, PE, Mach-O, and Raw binaries across x86, ARM, MIPS, and RISC-V architectures. Supports automated ROP chain generation…
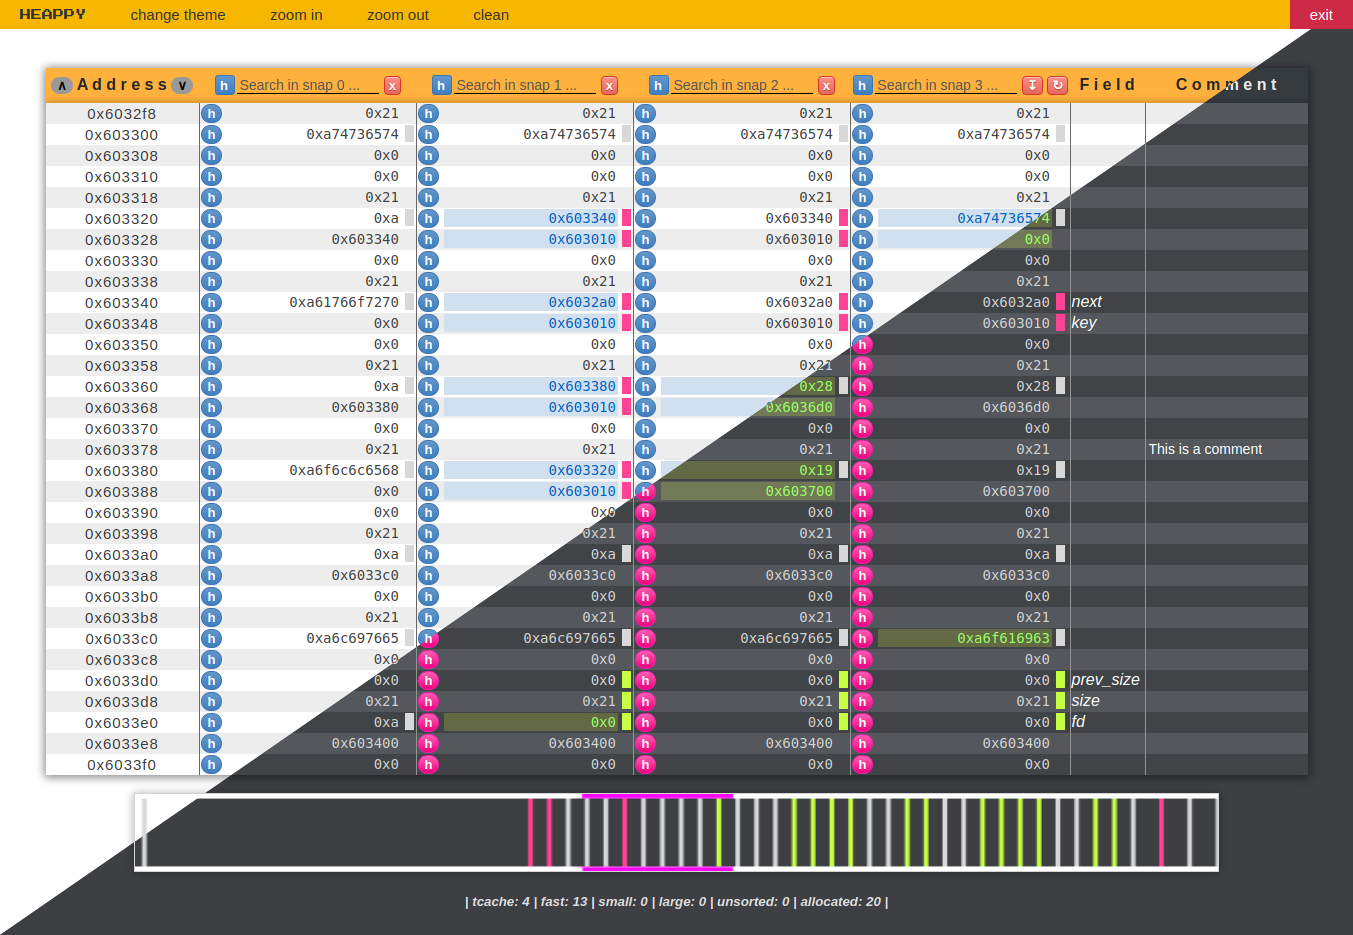 gand3lf/heappy
A happy heap editor to support your exploitation process :slightly_smiling_face:
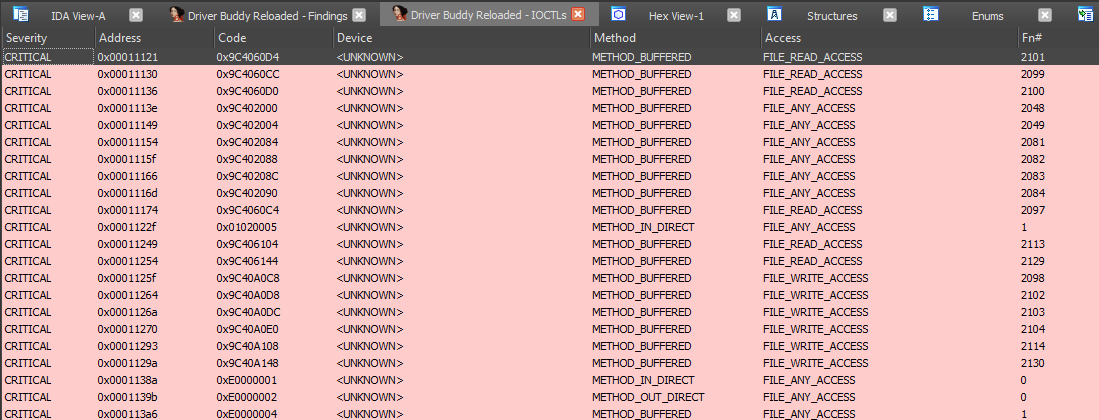 voidsec/driverbuddyreloaded
Driver Buddy Reloaded is an IDA Pro Python plugin that helps automate some tedious Windows Kernel Drivers reverse engineering tasks