Sandroid_Dexray-Intercept

A Android malware analysis tool that creates comprehensive runtime profiles by hooking into application behavior across cryptography, file systems,…

A Android malware analysis tool that creates comprehensive runtime profiles by hooking into application behavior across cryptography, file systems,…

Reverse bytenode .jsc (V8 code cache) to JavaScript — static, pure Rust, no patched V8/Node. Node 8→26 / V8 5.8–14.6; 25k .jsc tested, 0 fail.

Code written as part of our various malware investigations

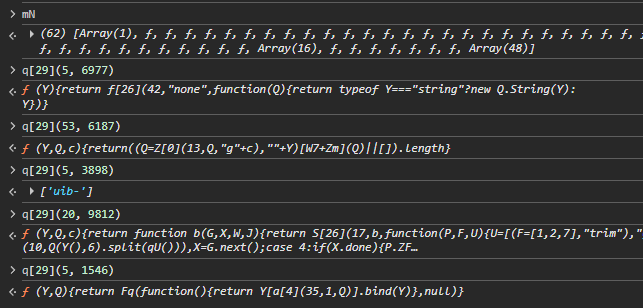
Deobfuscator for javascript-obfuscator 5.x output (string arrays, control-flow flattening, self-defending, RC4/base64)

Open-source mobile security testing suite for iOS and Android. Previously Passionfruit

CMake build of Ghidra's SLEIGH processor specification library, providing standalone disassembly and p-code lifting engines for reverse engineering…

.NET deobfuscator and unpacker.

An LLVM-based instrumentation tool for universal taint tracking, dataflow analysis, and tracing.

match functions in binaries by what they do, not what their bytes look like. behavioral function fingerprinting via microexecution.

Unpack and deobfuscate VMProtect 2 protected binaries with an emulation-based VM explorer, handler profiler, and experimental LLVM recompiler for…

Documentation and reverse engineering of reCAPTCHA

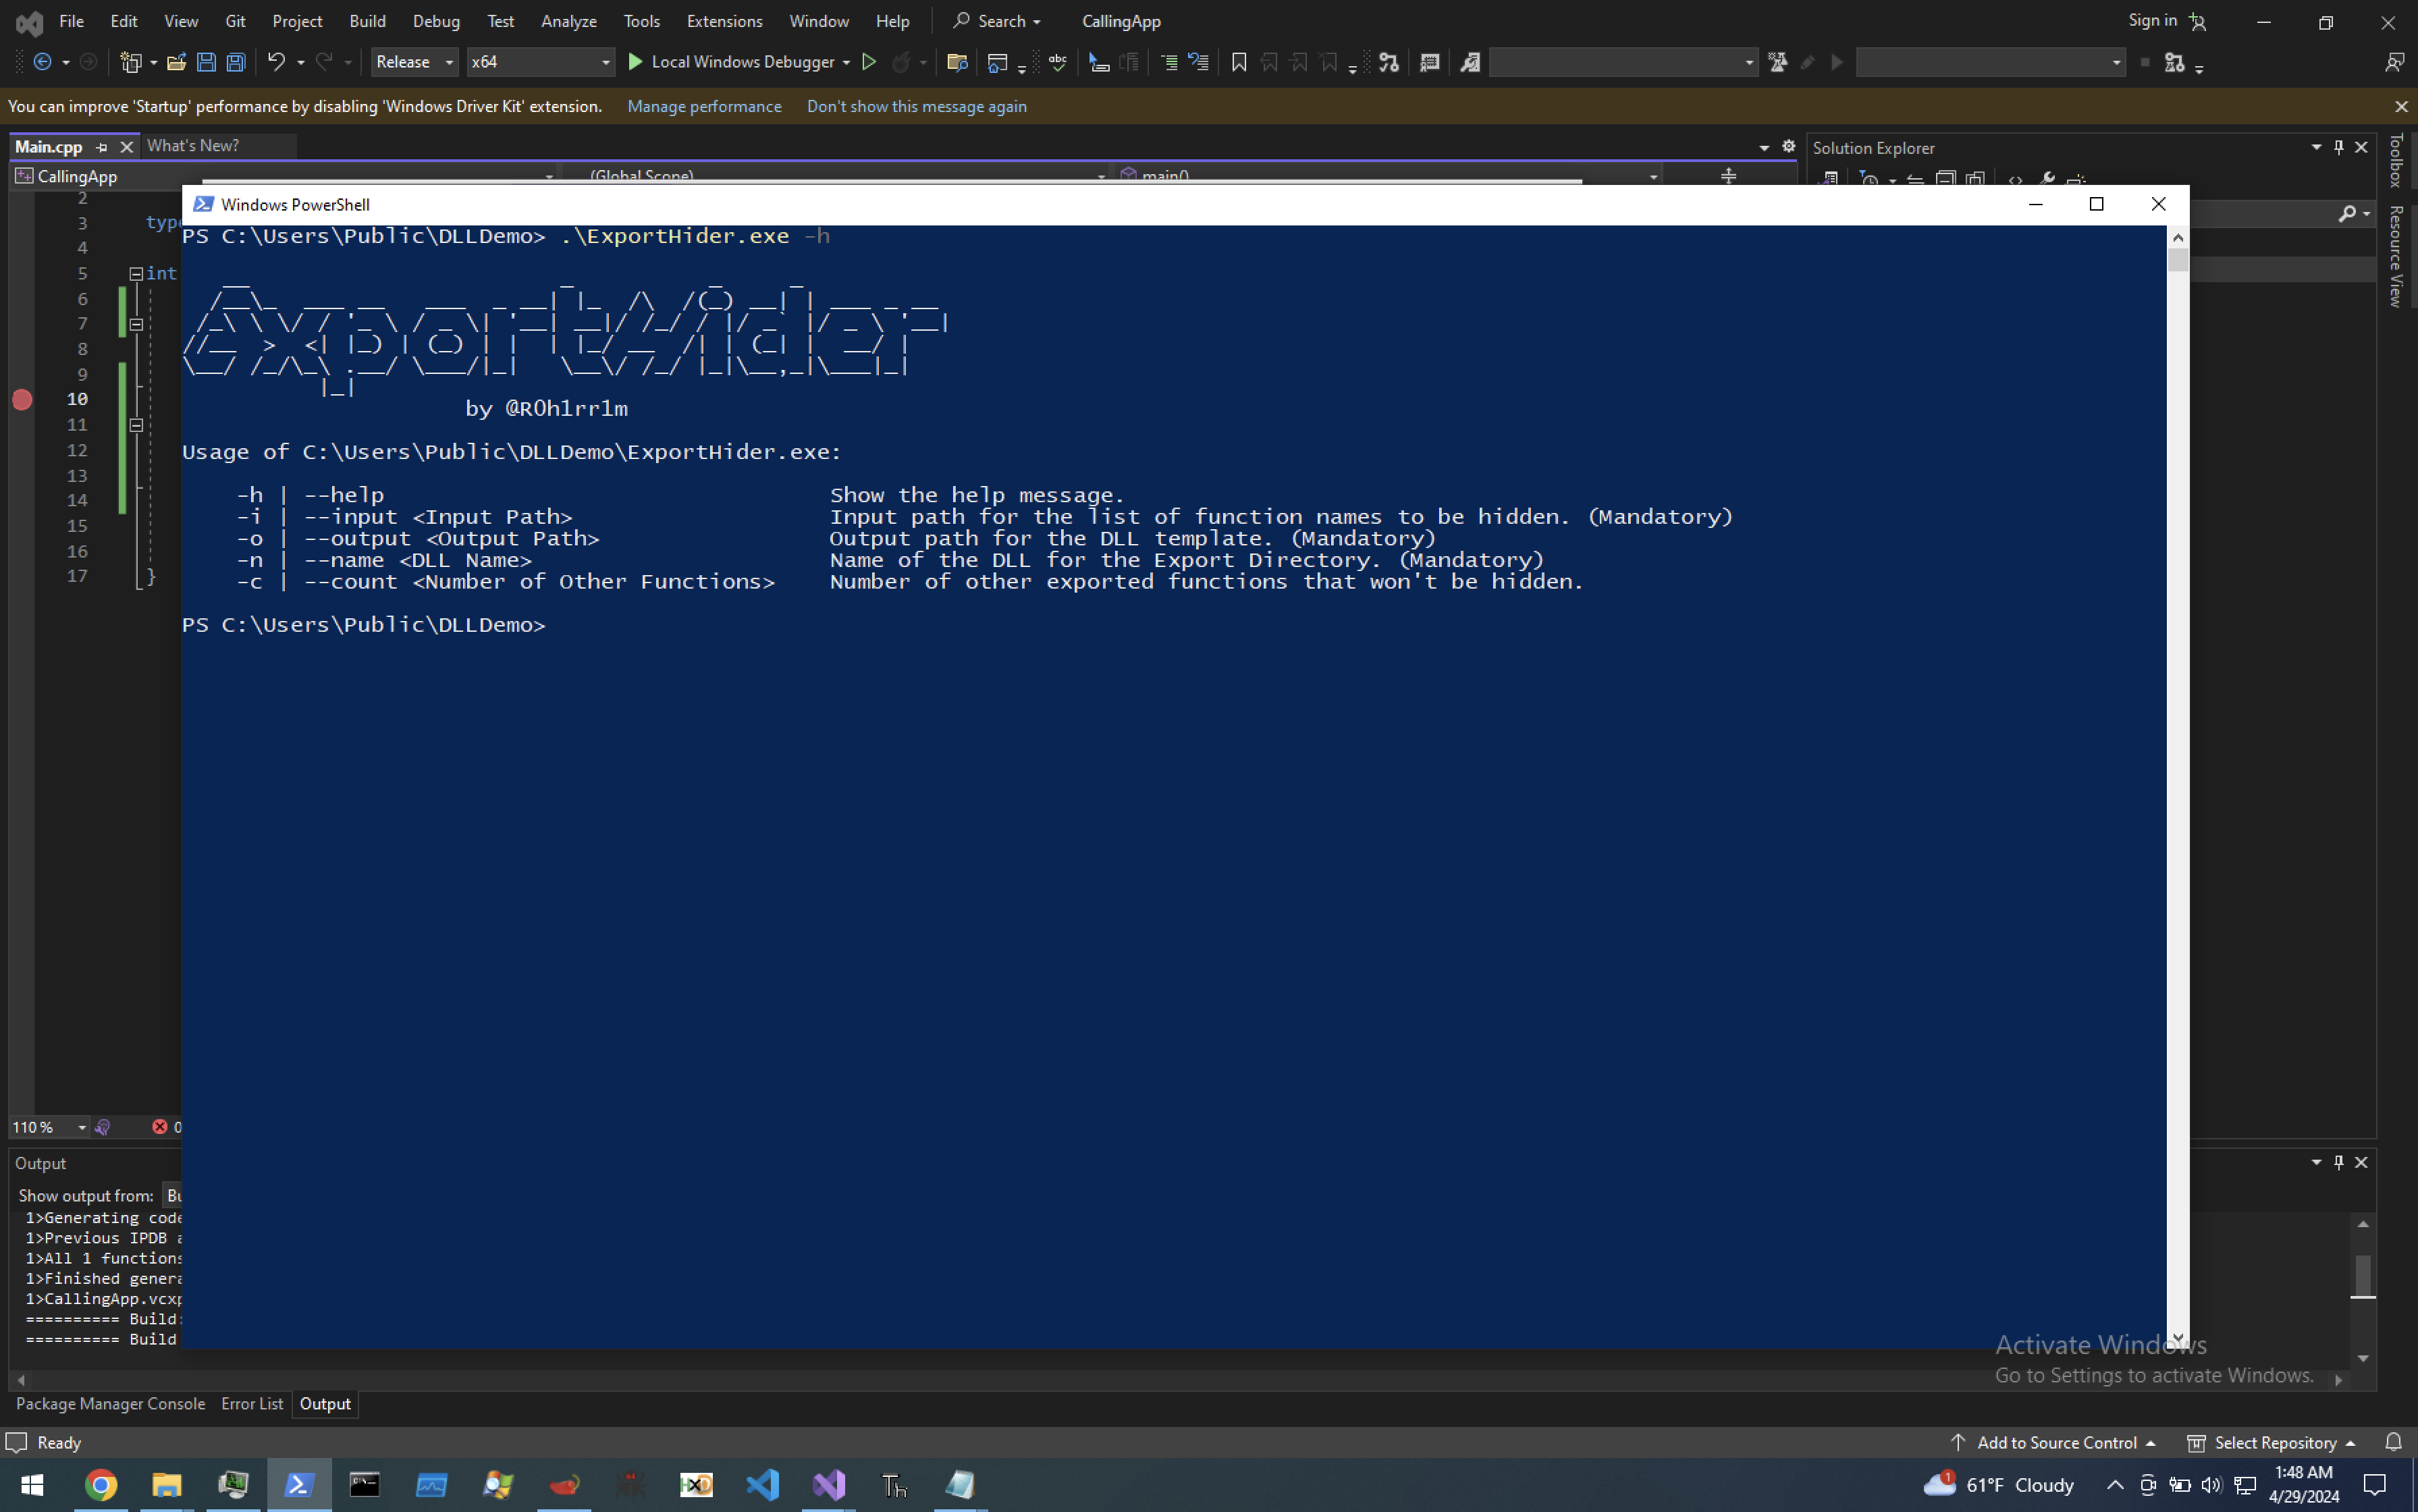
ExportHider: Generating Export Table during Runtime to Hide the Exported Functions from the DLL File.

Scriptable debugger for Android Dalvik VM using JDWP/DDM interfaces to hook methods, inspect process state, and modify runtime behavior without…

VMUnprotect.Dumper can dynamically untamper VMProtected Assembly.

The ARTful library for dynamically modifying the Android Runtime

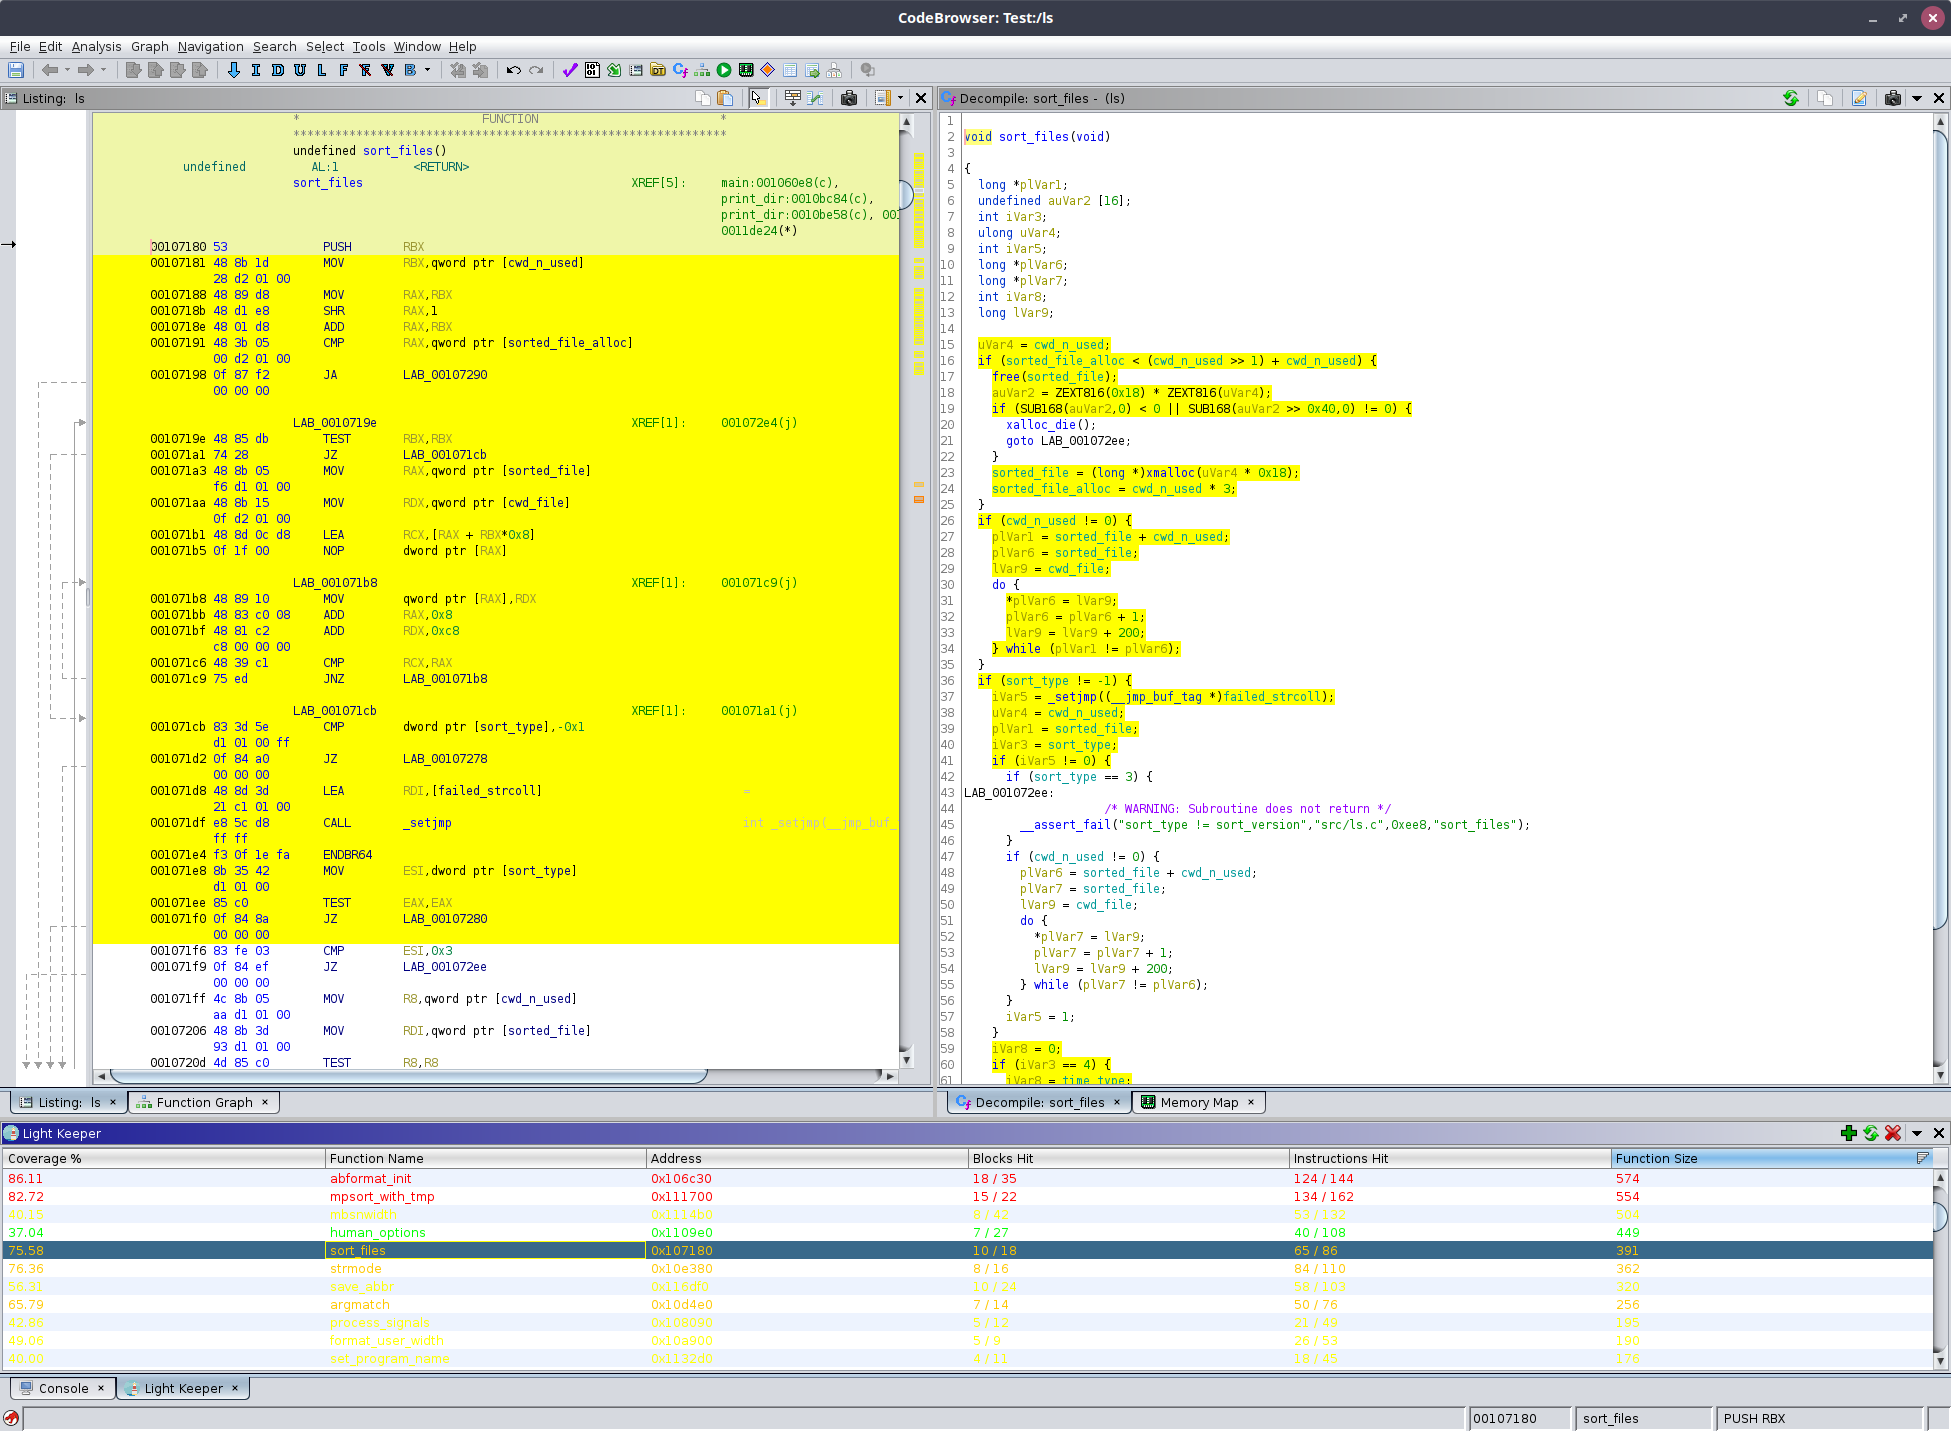
Maps execution-coverage data onto Ghidra disassembly to highlight visited code paths and accelerate reverse-engineering workflows.

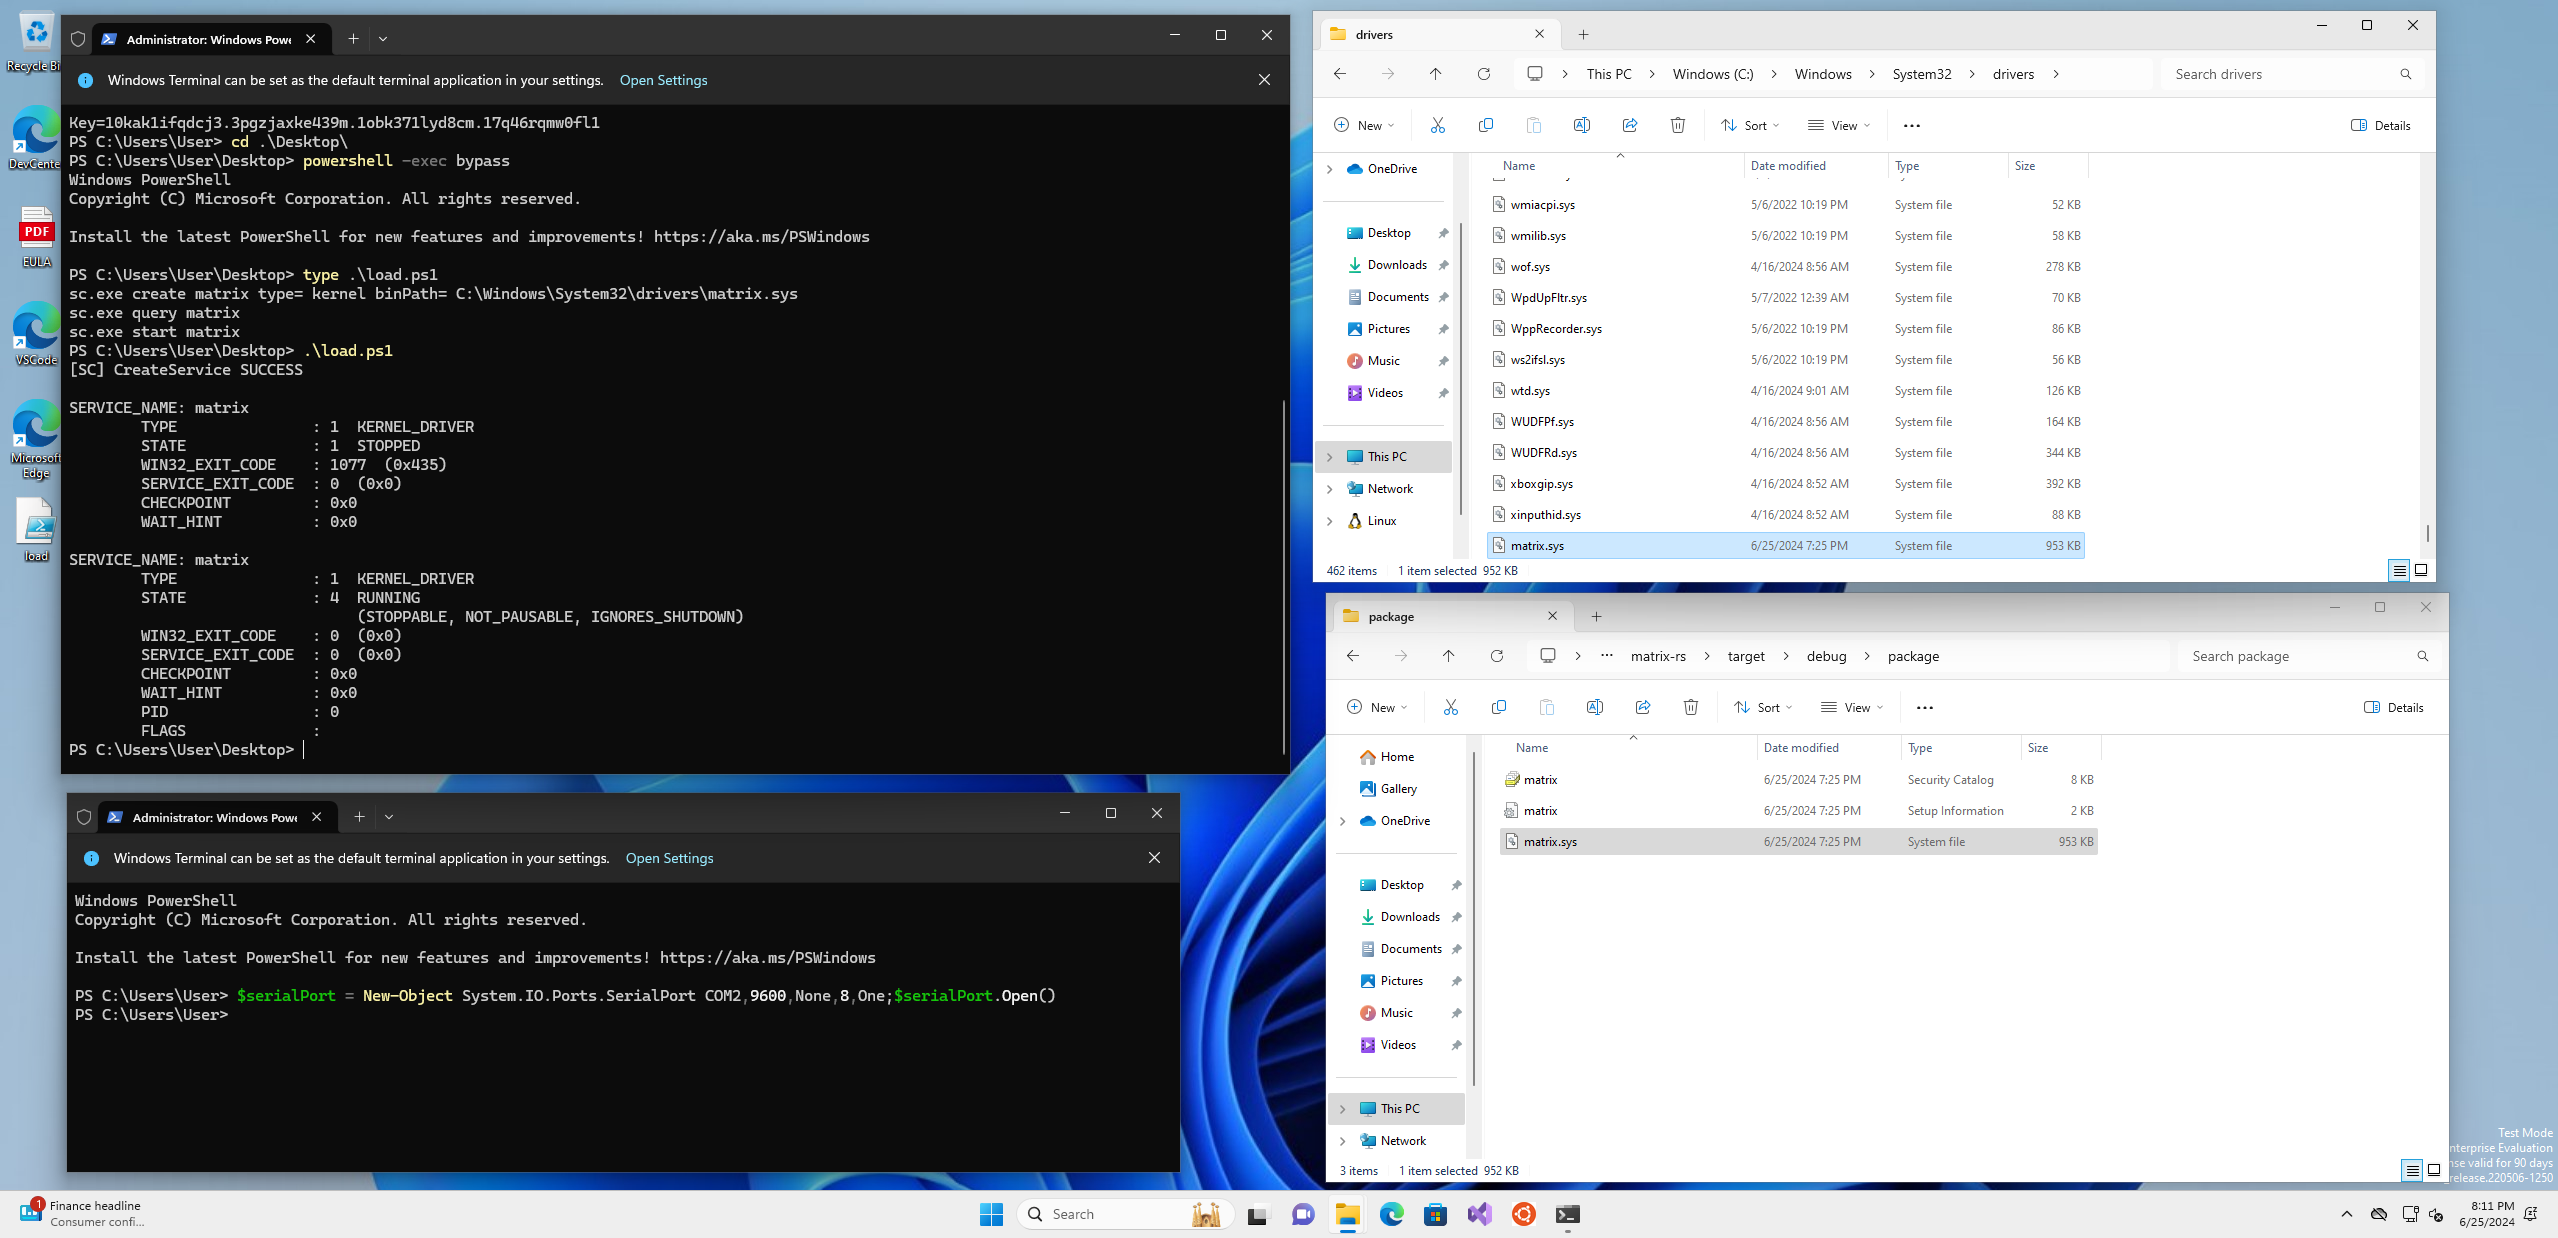
Rusty Hypervisor - Windows Kernel Blue Pill Type-2 Hypervisor in Rust (Codename: Matrix)

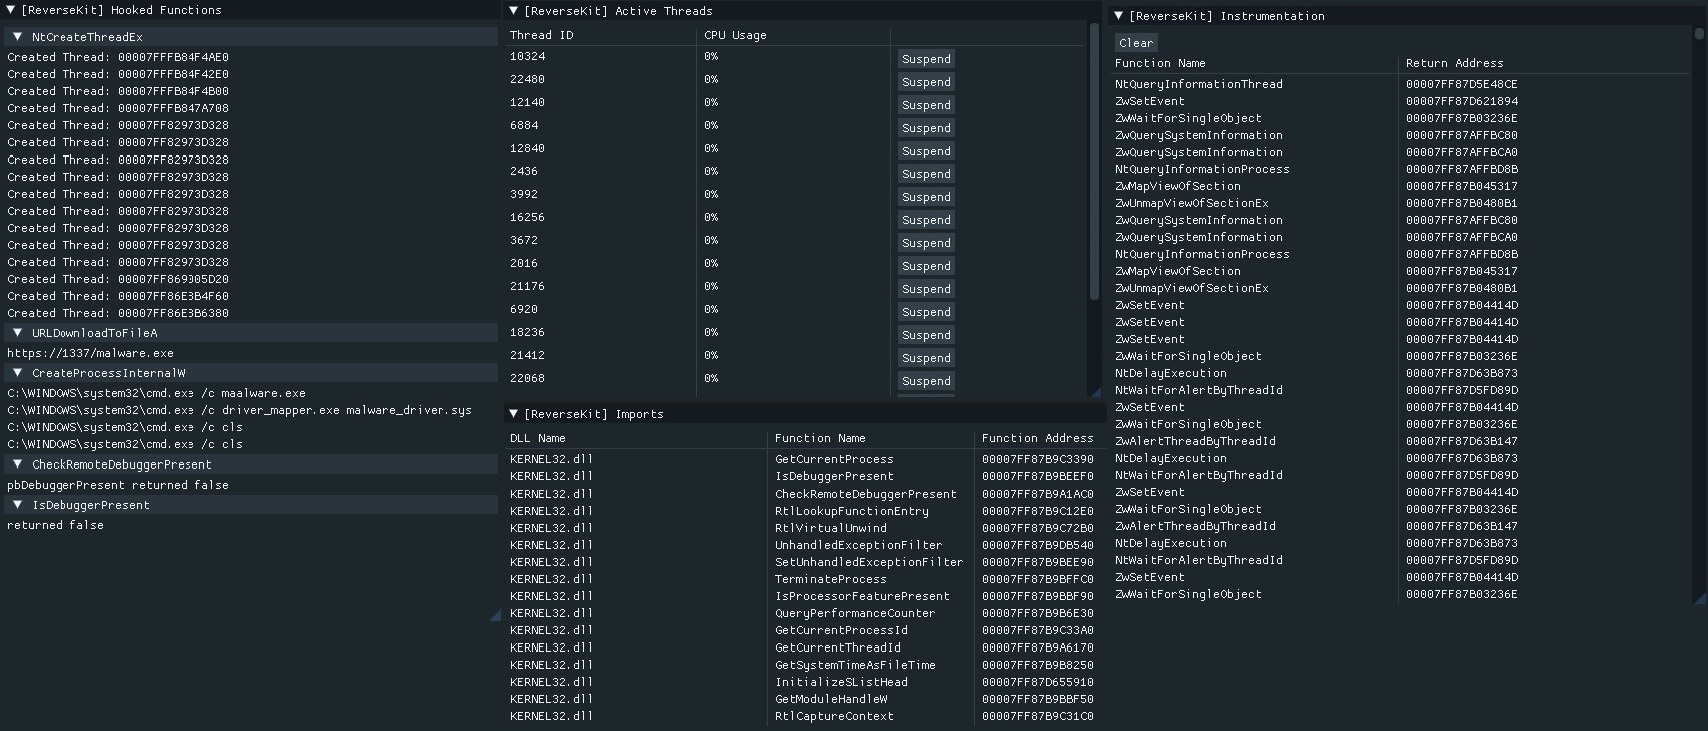
x64 Dynamic Reverse Engineering Toolkit