

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
31 results
scan preview

scan

GitHubatomdrift-project/scan

0-day malware detection for binaries, source & scripts (that doesn't suck)

binary-analysiscode-analysisdefensive-tools+9
22318h 28m ago
phantom-frida preview

phantom-frida

GitHubtheqmaks/phantom-frida

Build anti-detection Frida server from source. ~90 patches covering 16 detection vectors, weekly auto-builds with random names.

android-securitybinary-analysisdynamic-analysis-sandboxing+7
4033 months ago
radare2 preview

radare2

GitHubradareorg/radare2

UNIX-like reverse engineering framework and command-line toolset

ai-assisted-reversingandroid-securitybinary-analysis+16
25.2k14h 18m ago
Xiaomi-C200-Firmware-Analysis preview

Xiaomi-C200-Firmware-Analysis

GitHubh3xdum/xiaomi-c200-firmware-analysis

From UART to Root: Breaking Into the Xiaomi C200 via U-Boot

data-recoveryembedded-systems-securityexploitation+6
1210 months ago
frida-ios-dump preview

frida-ios-dump

GitHubalonemonkey/frida-ios-dump

Extracts decrypted IPA files from jailbroken iOS devices using Frida for reverse engineering, security analysis, and mobile app pentesting.
encryption-decryption-toolsios-securitymobile-app-pentesting+4
4.0k8 days ago
ptxNinja preview

ptxNinja

GitHubseekbytes/ptxninja

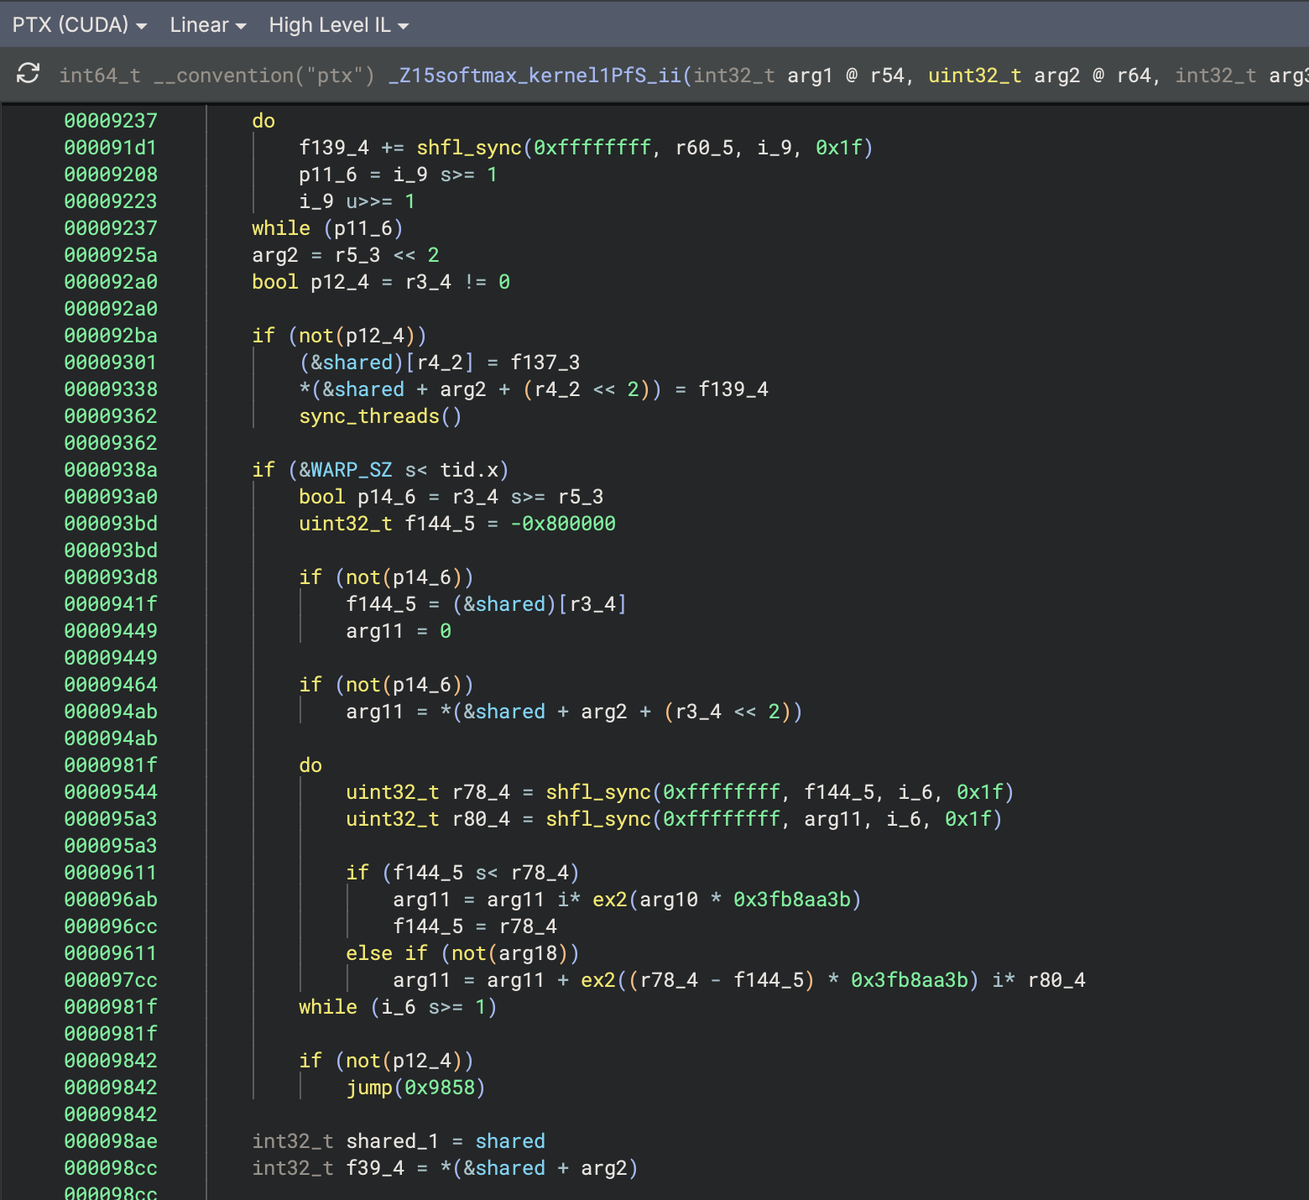
Binary Ninja plugin for reverse engineering PTX -- the virtual instruction set architecture of CUDA-based GPUs.
binary-analysiscode-analysishardware-iot-security+3
657 months ago
PwnAdventure3 preview

PwnAdventure3

GitHubliveoverflow/pwnadventure3

PwnAdventure3 Server

binary-exploitationctfeducation+5
6898 years ago
SwishDbgExt preview

SwishDbgExt

GitHubmagnetforensics/swishdbgext

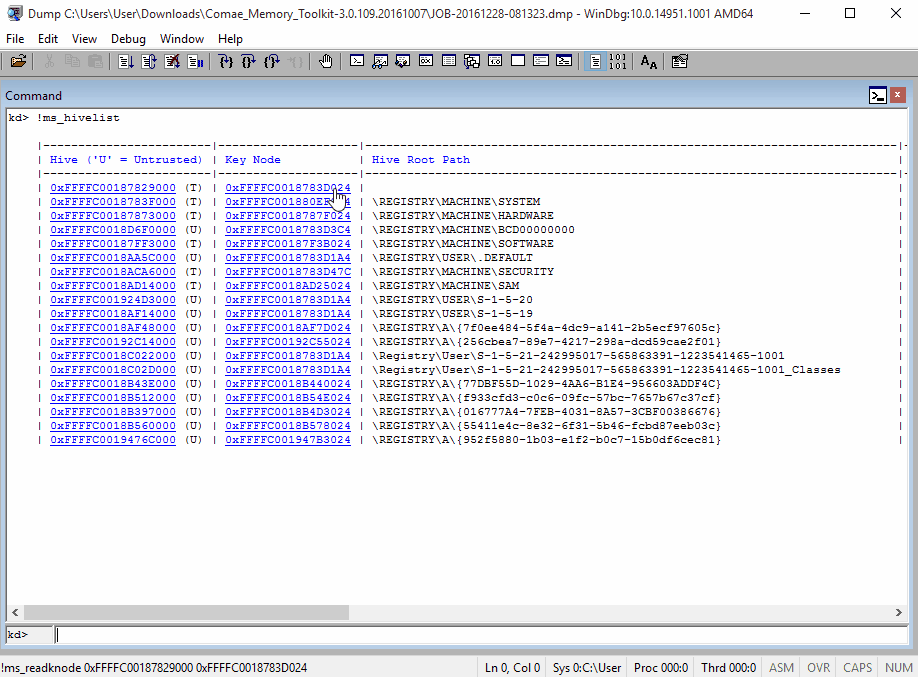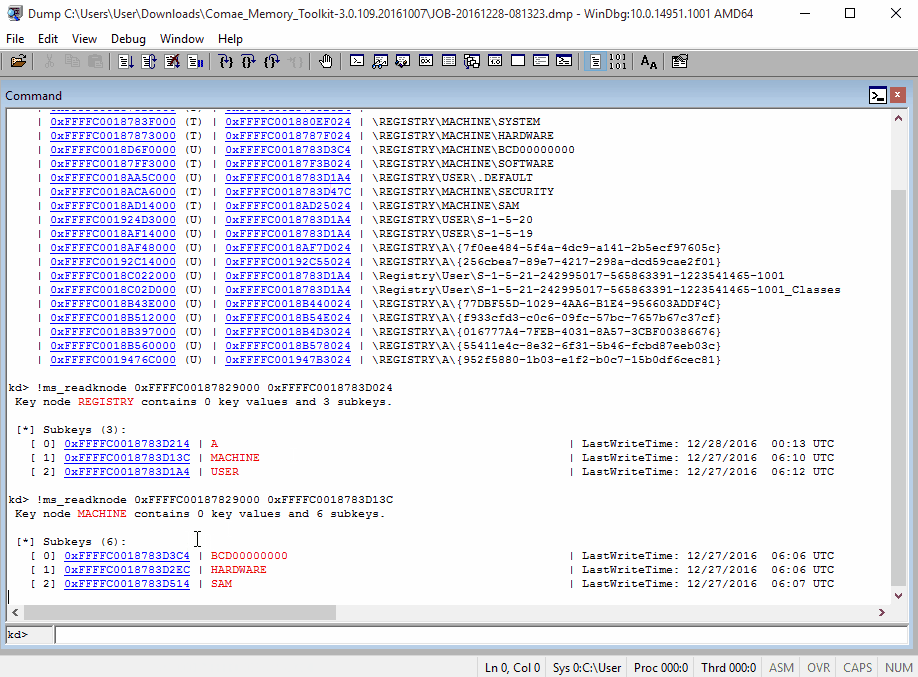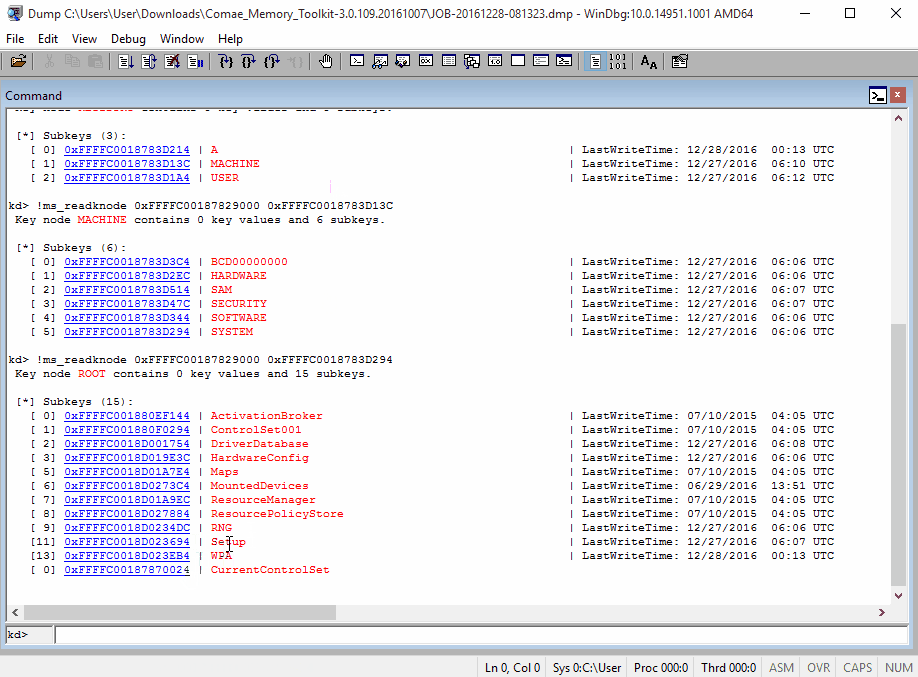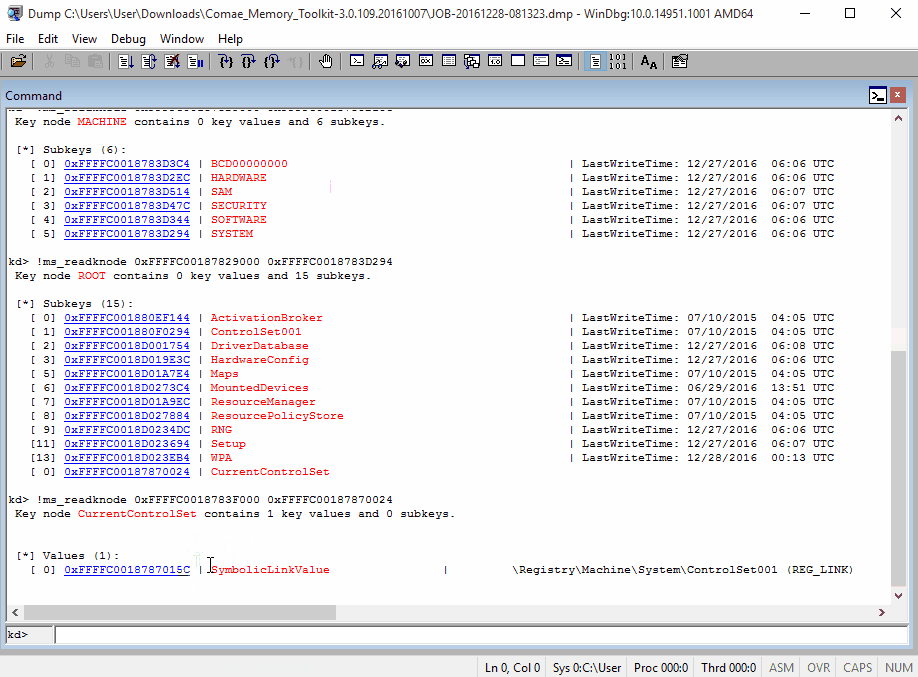
Incident Response & Digital Forensics Debugging Extension

debuggersdigital-forensicsincident-response+3
3997 years ago
gef preview

gef

GitHubhugsy/gef

GEF (GDB Enhanced Features) - a modern experience for GDB with advanced debugging capabilities for exploit devs & reverse engineers on Linux
ai-assisted-reversingbinary-analysisbinary-exploitation+10
8.4k2 months ago
sandsifter preview

sandsifter

GitHubxoreaxeaxeax/sandsifter

The x86 processor fuzzer

binary-analysisfuzzinghardware-security+2
5.1k9 years ago
dnSpy preview
Archived

dnSpy

GitHubdnspy/dnspy

.NET debugger and assembly editor

binary-analysisbinary-exploitationcode-analysis+8
29.7k5 years ago
B2R2 preview

B2R2

GitHubb2r2-org/b2r2

B2R2 is a fully managed binary analysis framework written in F#. It provides a rich set of algorithms, functions, and tools for reverse engineering,…
binary-analysisdynamic-analysis-sandboxingeducation+4
5524 days ago
uefi-firmware-parser preview

uefi-firmware-parser

GitHubtheopolis/uefi-firmware-parser

Parse BIOS/Intel ME/UEFI firmware related structures: Volumes, FileSystems, Files, etc

binary-analysisembedded-systems-securityfirmware-analysis+2
93318 days ago
Overlord-RAT-Reverse-Engineering-a-Go-Based-RAT-Injection-Keylogging-C2-Exfiltration-Analysis preview

Overlord-RAT-Reverse-Engineering-a-Go-Based-RAT-Injection-Keylogging-C2-Exfiltration-Analysis

GitHubkaandemir993/overlord-rat-reverse-engineering-a-go-based-rat-injection-keylogging-c2-exfiltration-analysis

Full static & memory analysis of Overlord RAT: Go agent architecture, HTTP/2 + WebSocket C2, reflective DLL injection, browser keylogging, and IOCs.…

command-and-controldata-exfiltrationdigital-forensics+6
920 days ago
ret-sync preview

ret-sync

GitHubbootleg/ret-sync

ret-sync is a set of plugins that helps to synchronize a debugging session (WinDbg/GDB/LLDB/OllyDbg2/x64dbg) with IDA/Ghidra/Binary Ninja…
binary-analysisdebuggersdynamic-analysis-sandboxing+2
2.4k8 months ago
Hooketh preview

Hooketh

GitHubhumoud/hooketh

A set of scripts that ease working with frida
android-securitydebuggersdynamic-analysis-sandboxing+2
26 years ago
SiMBA preview

SiMBA

GitHubdenuvosoftwaresolutions/simba

Efficient Deobfuscation of Linear Mixed Boolean-Arithmetic Expressions
binary-analysiscryptographyeducation+3
1993 years ago
KPOT-string-decrypter preview

KPOT-string-decrypter

GitHubdodo-sec/kpot-string-decrypter

IDA python scripts to decrypt strings from KPOT and set those as comments

binary-analysisencryption-decryption-toolsmalware-analysis+2
63 years ago
Previous12Next
