jscd
 ejfkdev/jscd
Reverse bytenode .jsc (V8 code cache) to JavaScript — static, pure Rust, no patched V8/Node. Node 8→26 / V8 5.8–14.6; 25k .jsc tested, 0 fail.
binary-analysiscode-analysisdynamic-code-analysis+4
32
ejfkdev/jscdReverse bytenode .jsc (V8 code cache) to JavaScript — static, pure Rust, no patched V8/Node. Node 8→26 / V8 5.8–14.6; 25k .jsc tested, 0 fail.
 eset/malware-research
Code written as part of our various malware investigations
 lolcaken/javascript-deobfuscator
Deobfuscator for javascript-obfuscator 5.x output (string arrays, control-flow flattening, self-defending, RC4/base64)
 lifting-bits/sleigh
CMake build of Ghidra's SLEIGH processor specification library, providing standalone disassembly and p-code lifting engines for reverse engineering…
 de4dot/de4dot
.NET deobfuscator and unpacker.
 trailofbits/polytracker
An LLVM-based instrumentation tool for universal taint tracking, dataflow analysis, and tracing.
 1rhino2/fnprint
match functions in binaries by what they do, not what their bytes look like. behavioral function fingerprinting via microexecution.
 aftermathlabs/vmp2
Unpack and deobfuscate VMProtect 2 protected binaries with an emulation-based VM explorer, handler profiler, and experimental LLVM recompiler for…
 elyelysiox/recaptcha
Documentation and reverse engineering of reCAPTCHA
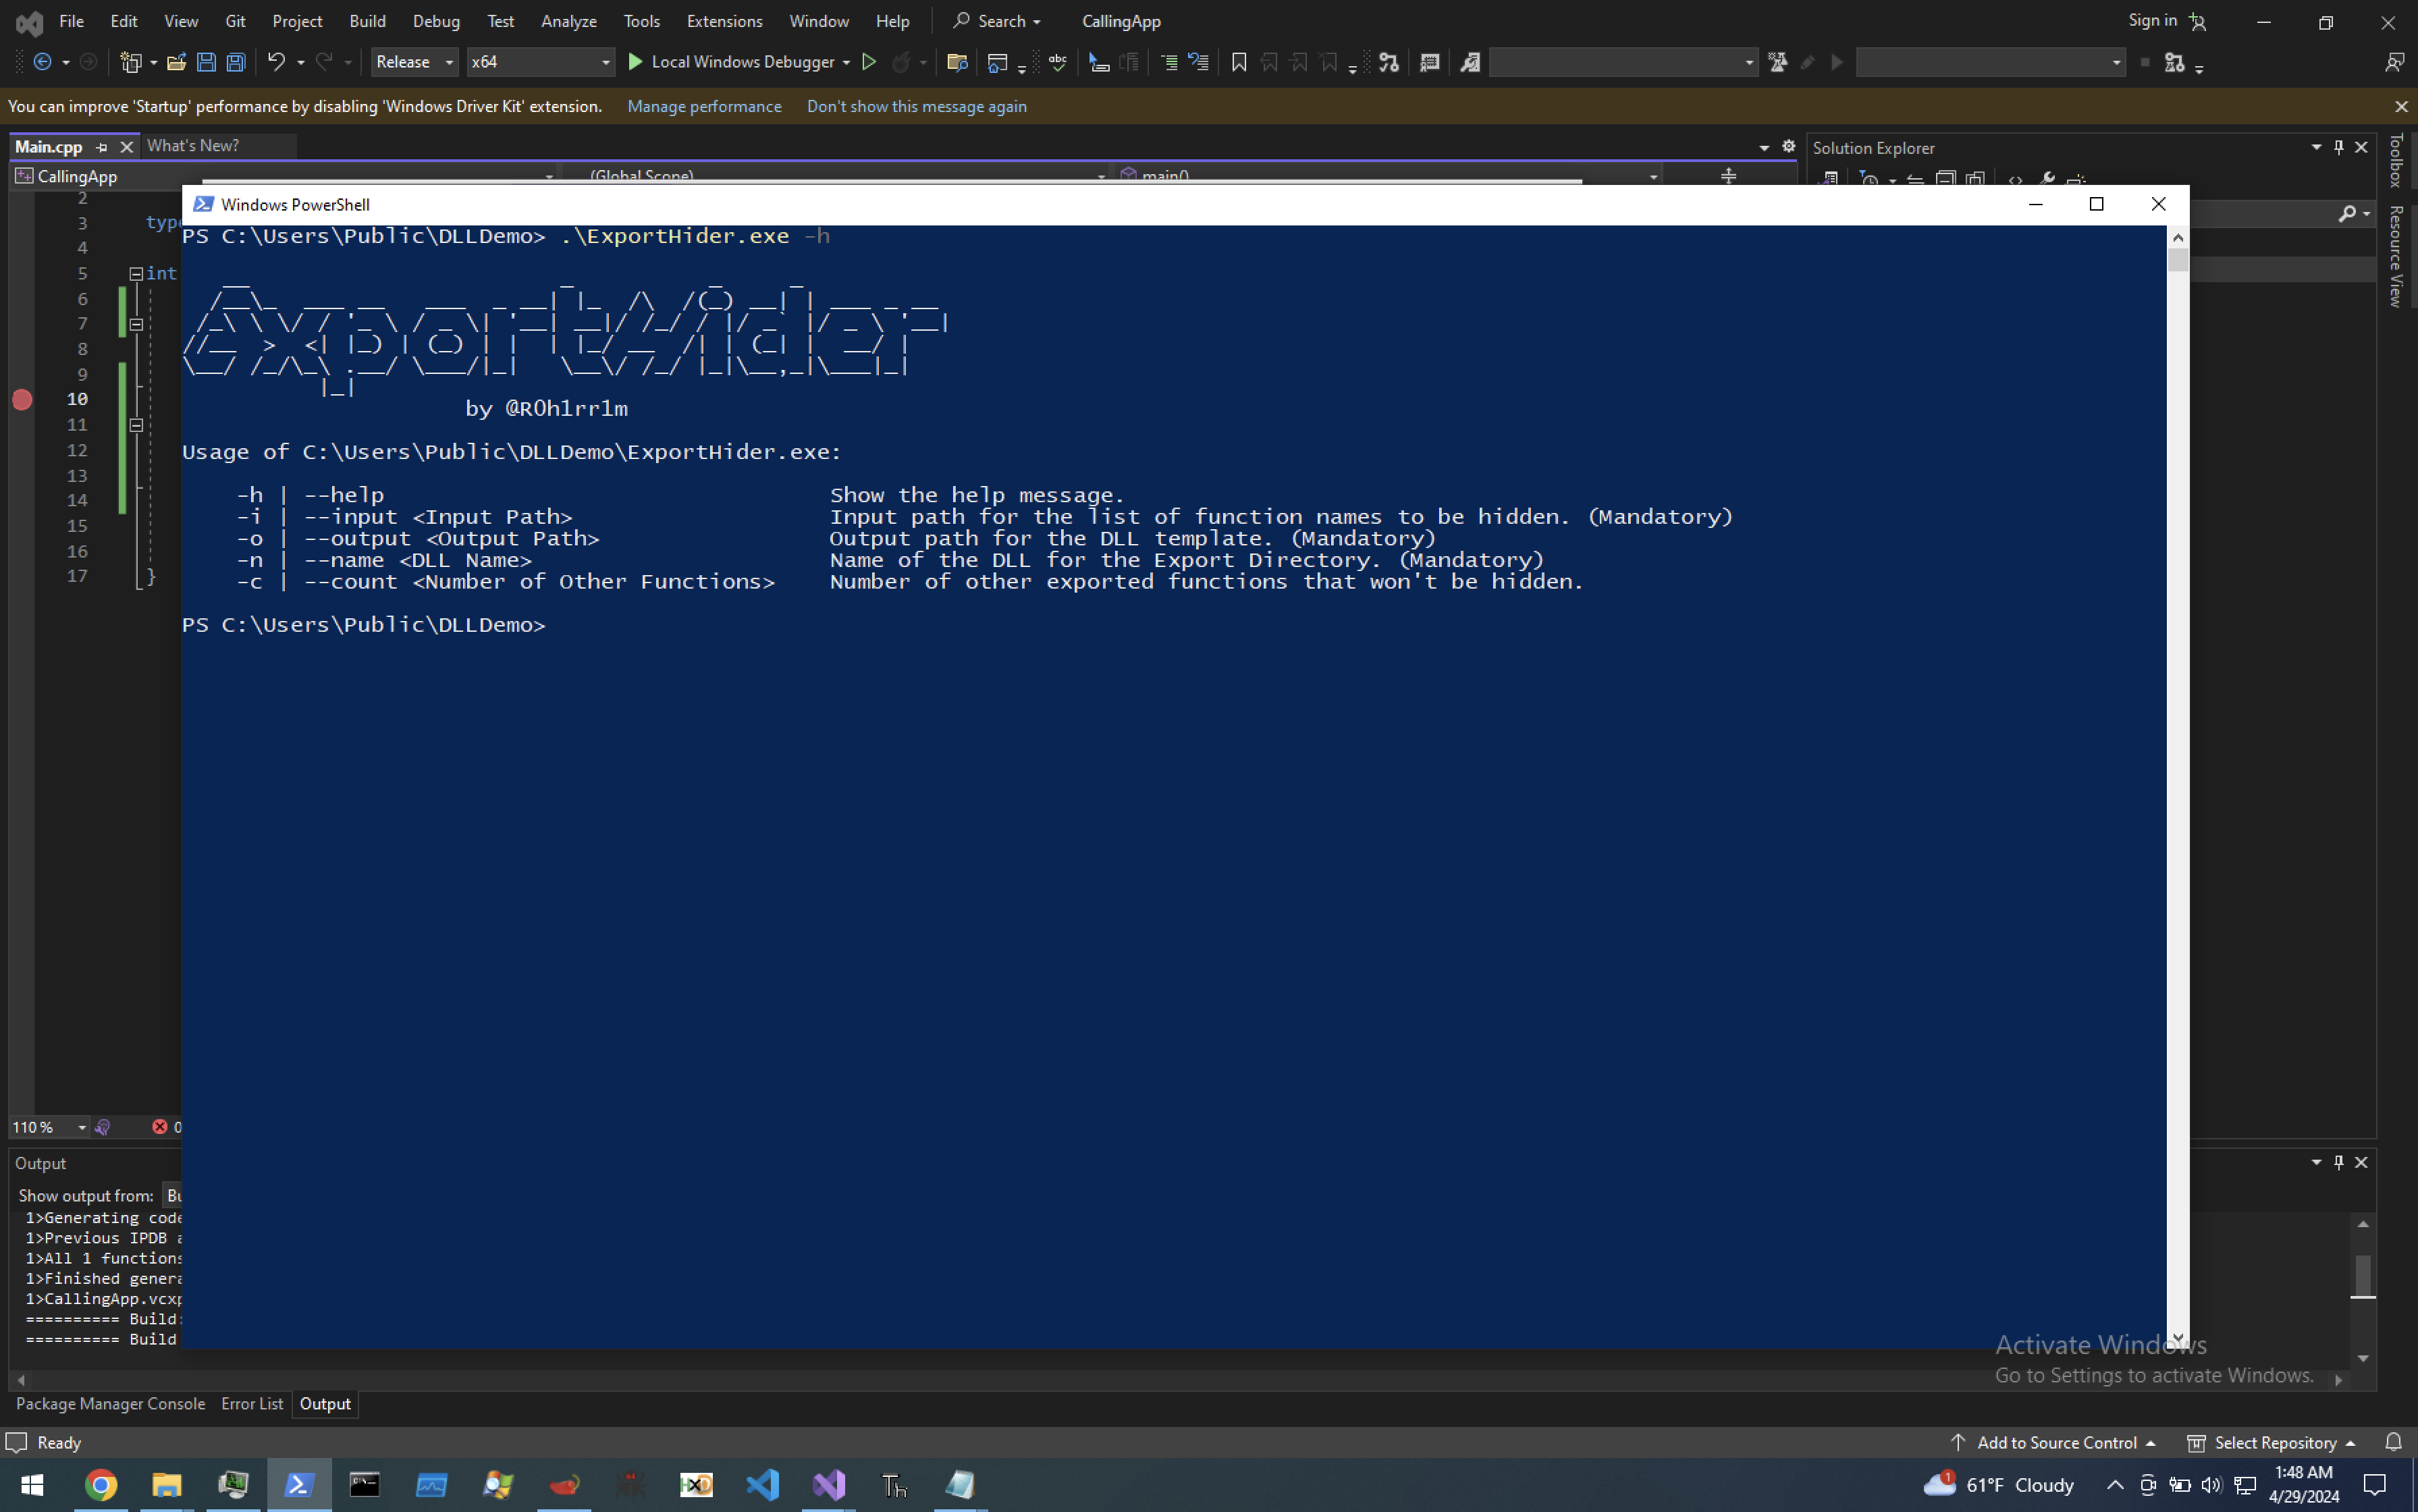 frkngksl/exporthider
ExportHider: Generating Export Table during Runtime to Hide the Exported Functions from the DLL File.
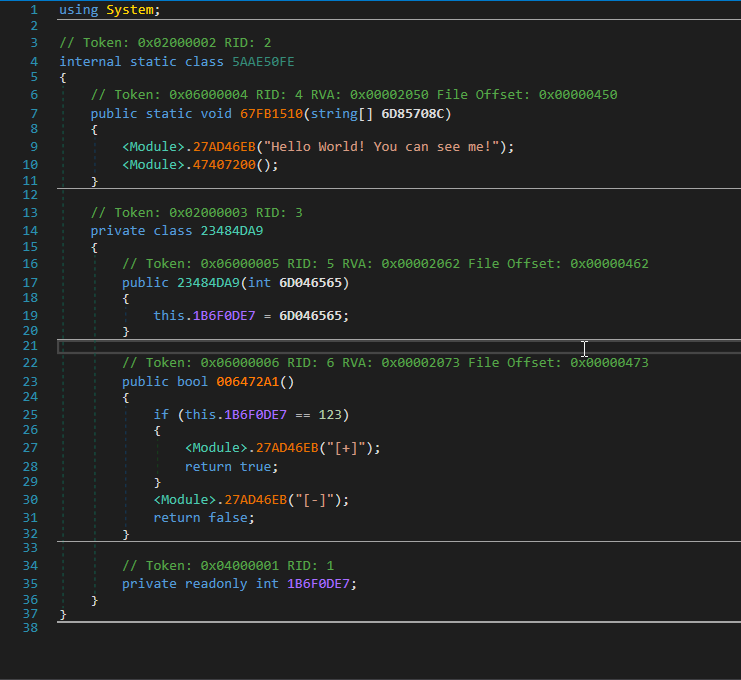 void-stack/vmunprotect.dumper
VMUnprotect.Dumper can dynamically untamper VMProtected Assembly.
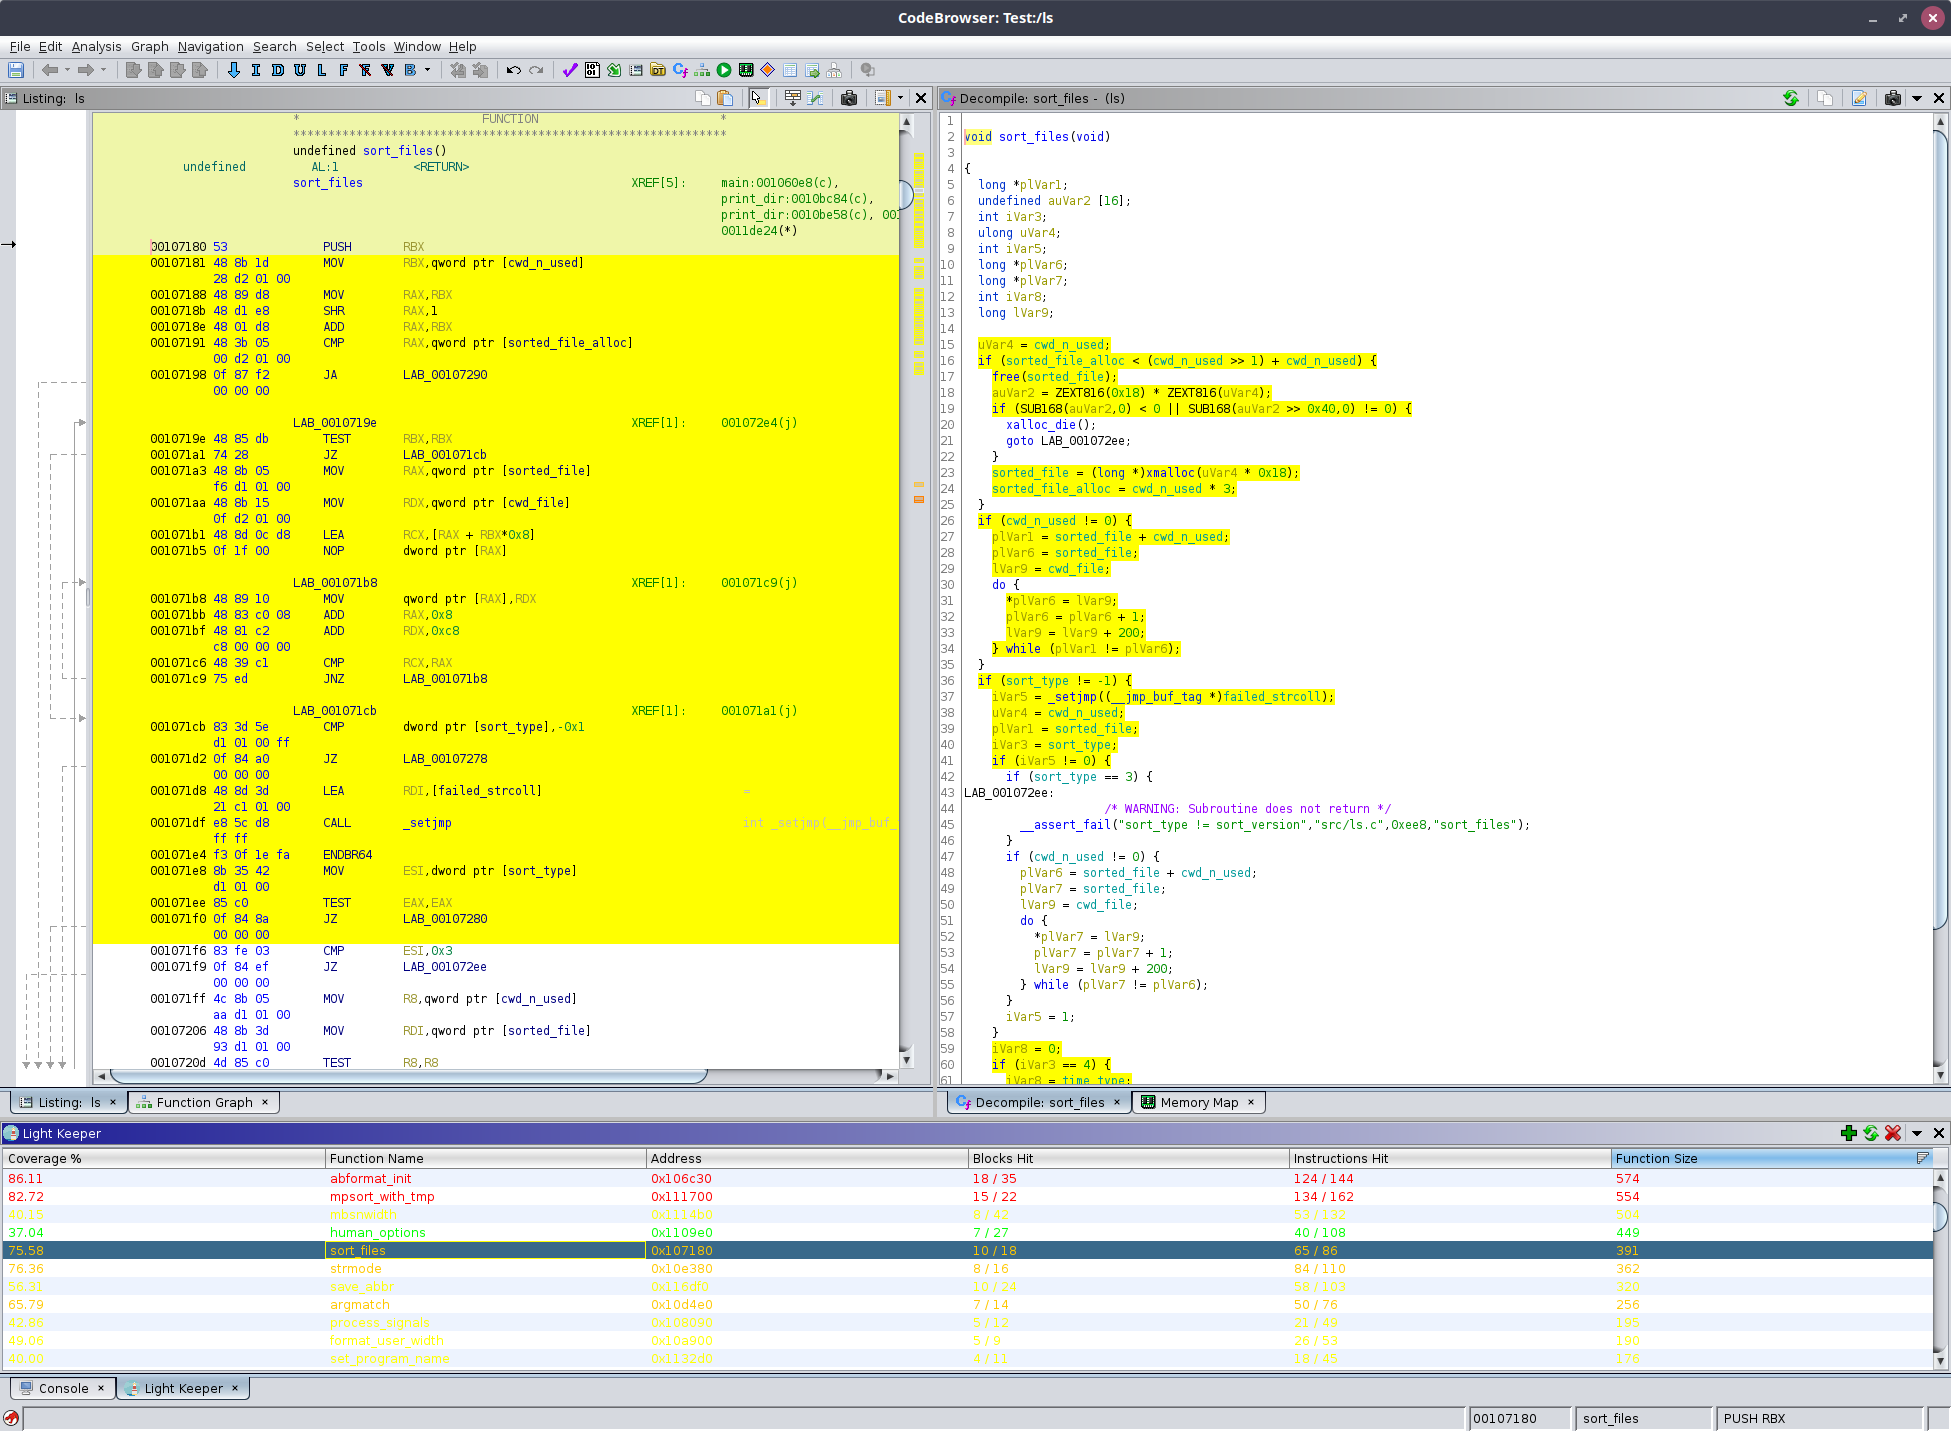 worksbutnottested/lightkeeper
Maps execution-coverage data onto Ghidra disassembly to highlight visited code paths and accelerate reverse-engineering workflows.
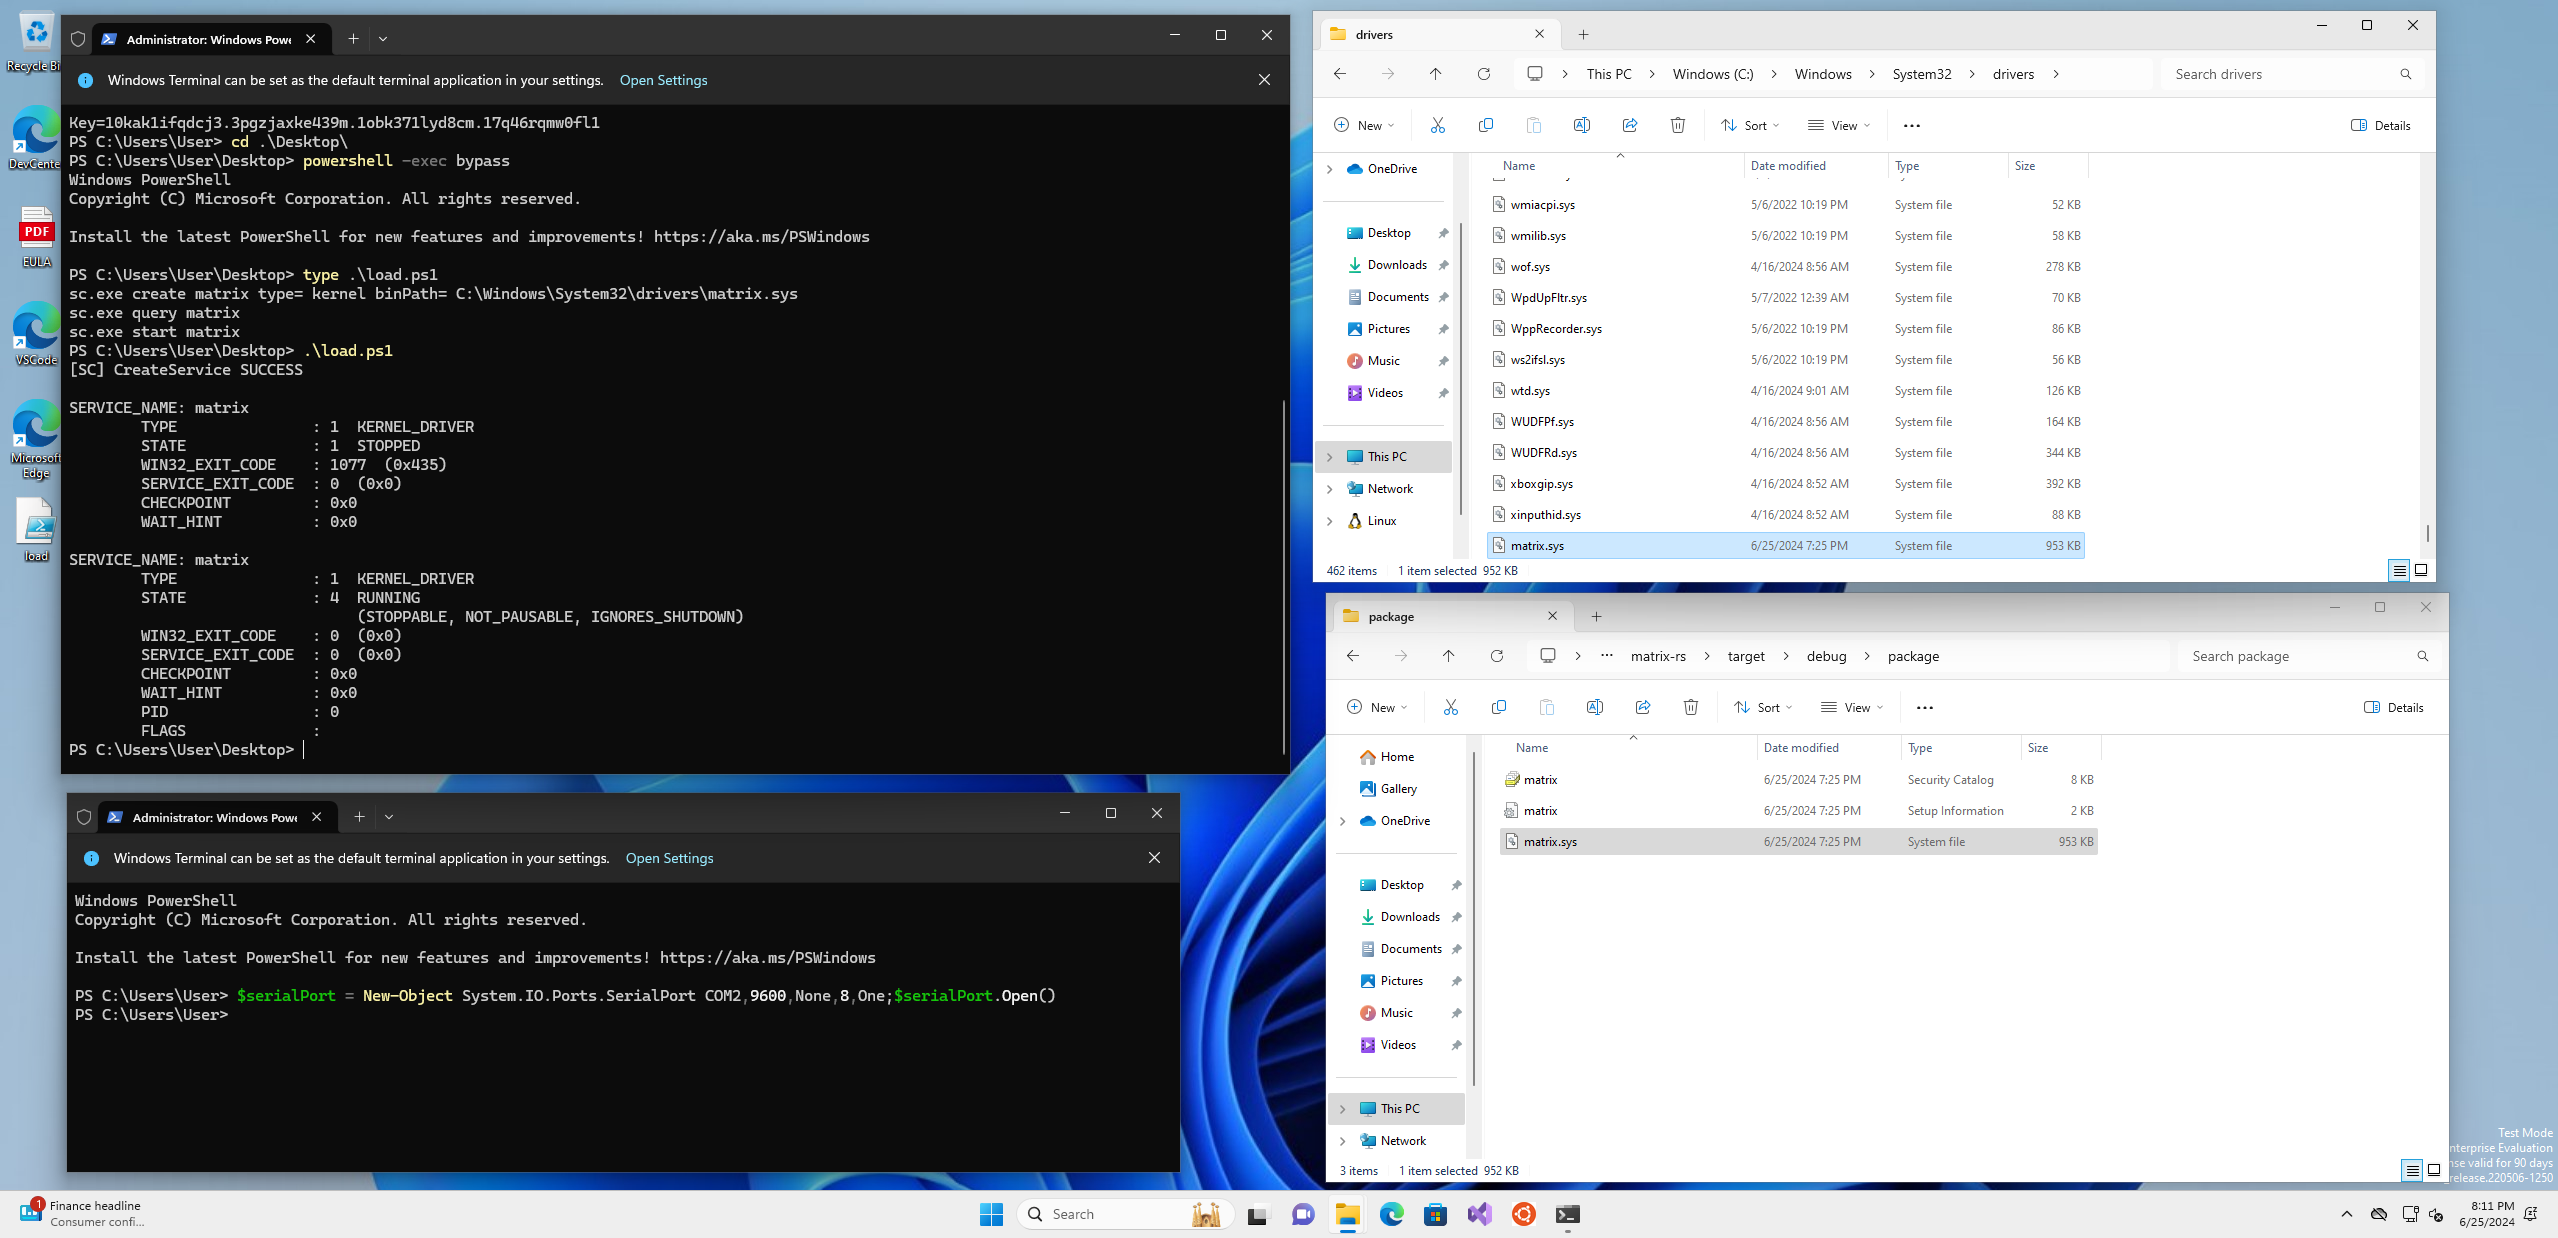 memn0ps/matrix-rs
Rusty Hypervisor - Windows Kernel Blue Pill Type-2 Hypervisor in Rust (Codename: Matrix)
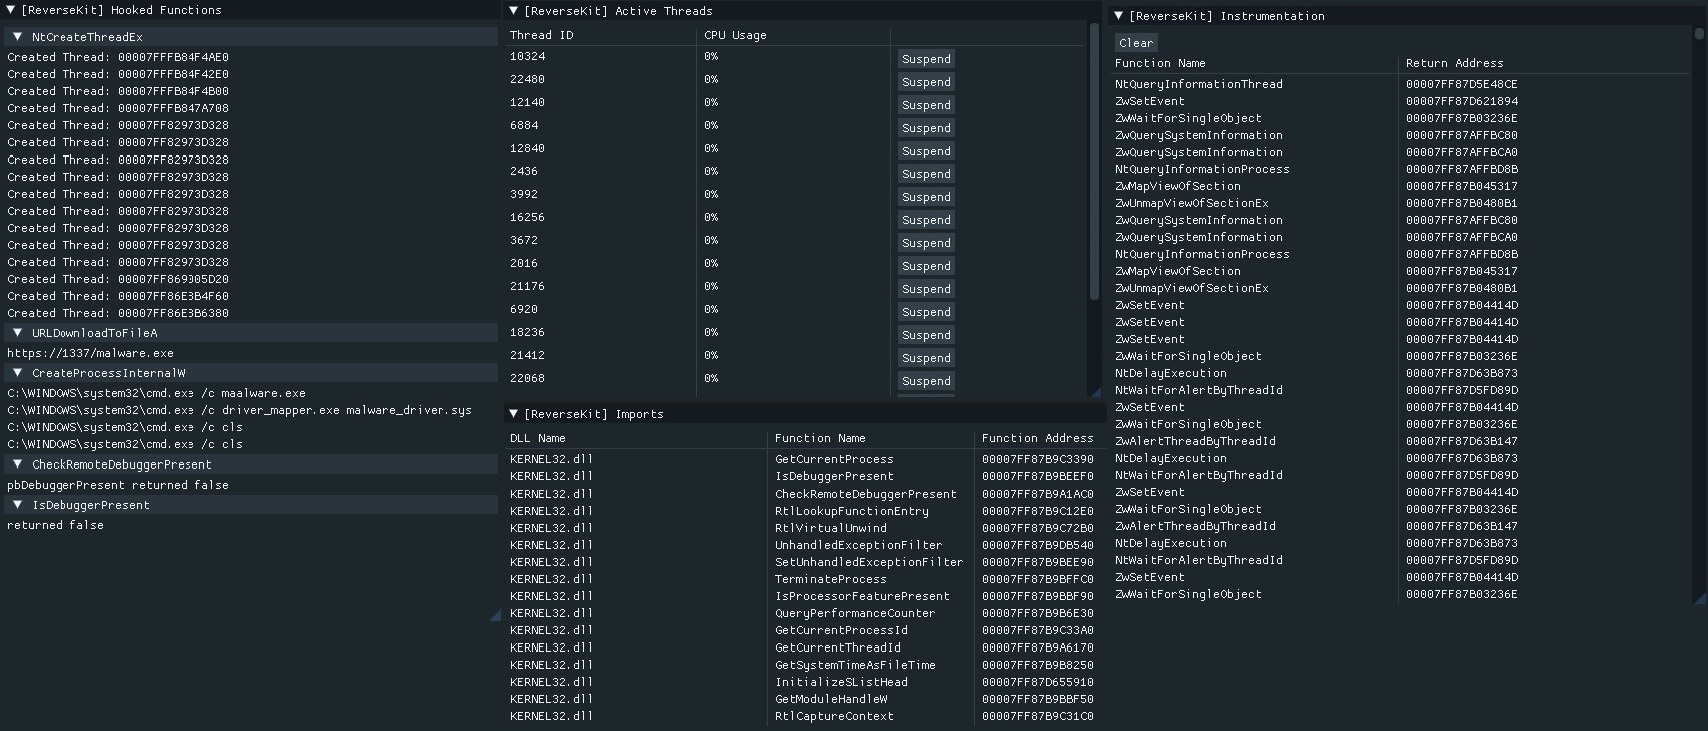 zer0condition/reversekit
x64 Dynamic Reverse Engineering Toolkit
 binsec/xyntia
Xyntia, the black-box deobfuscator
 robertdfrench/ifuncd-up
GNU IFUNC is the real culprit behind CVE-2024-3094
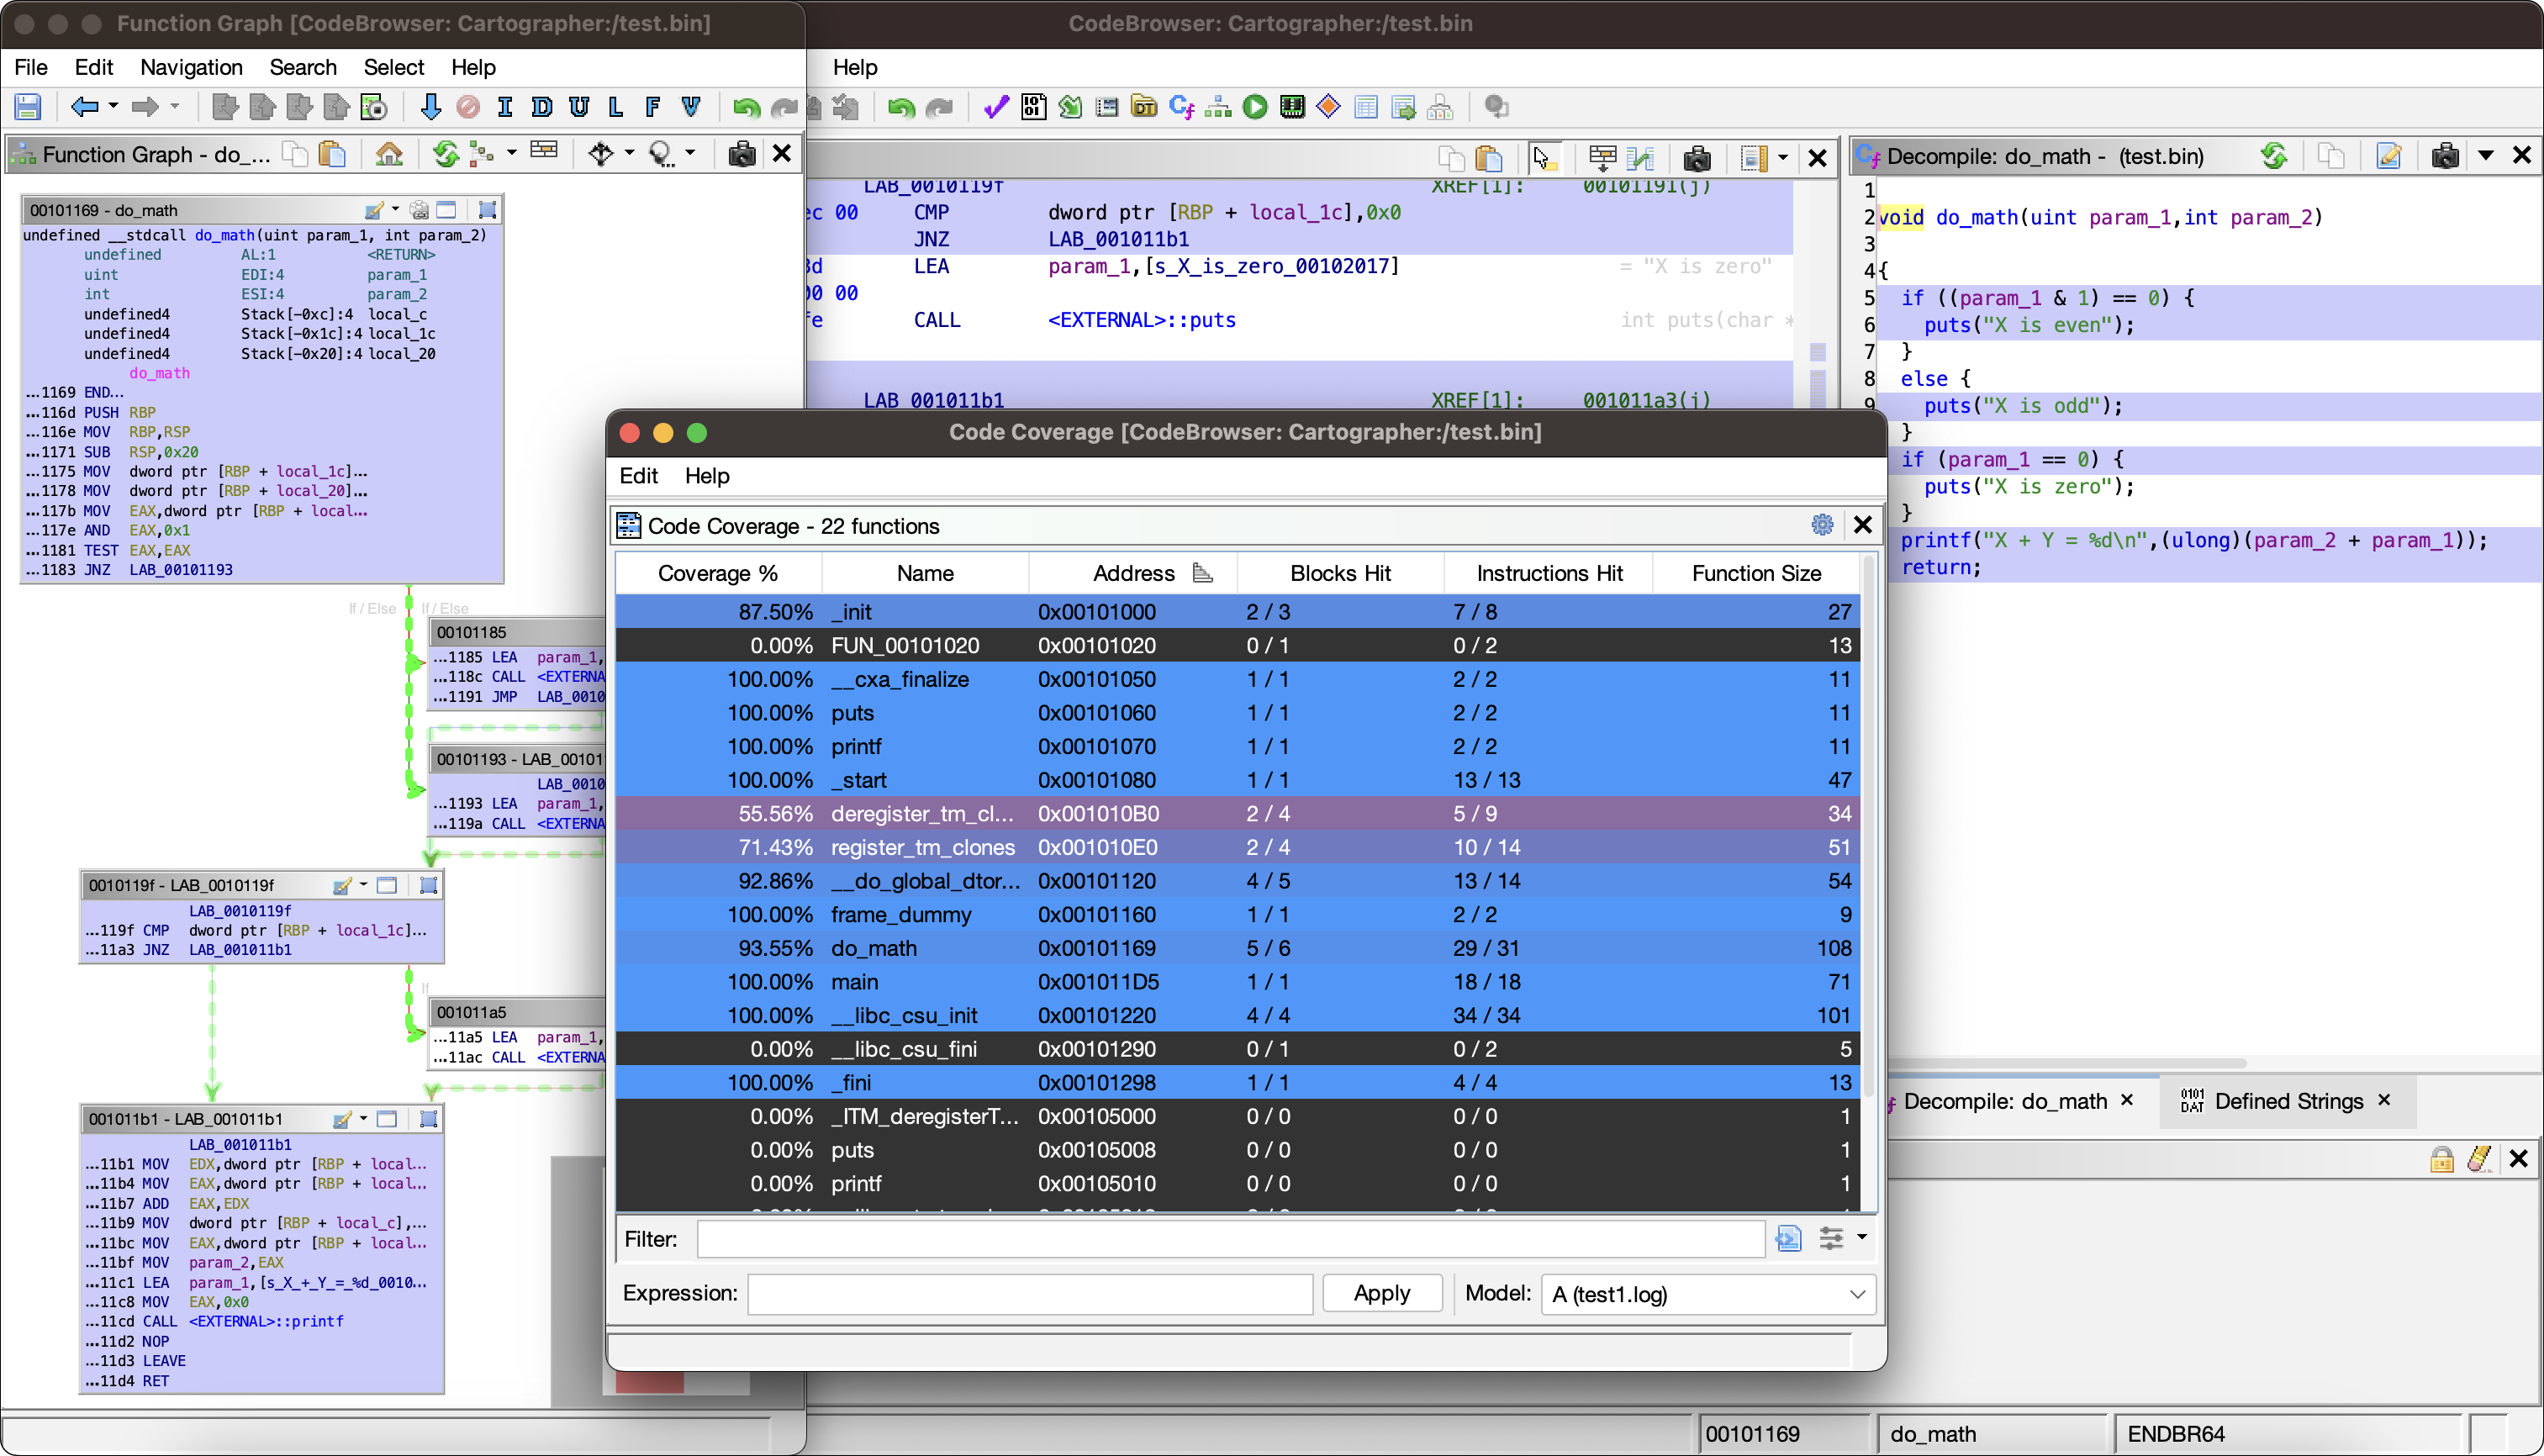 nccgroup/cartographer
Code Coverage Exploration Plugin for Ghidra