
NGINX2Root-CVE-2026-123007
 arkrwn/nginx2root-cve-2026-123007
Research Note: Turning Public Intelligence into a Root Exploit (Case Study: CVE-2026-123007)
exploitationnetwork-securitypayload-development+5
3
arkrwn/nginx2root-cve-2026-123007Research Note: Turning Public Intelligence into a Root Exploit (Case Study: CVE-2026-123007)
 im-hanzou/cve-2026-126170-fortimanager-jsonrpc-rce
PoC and exploit scripts for CVE-2026-126170, an unauthenticated JSON-RPC injection RCE in FortiManager/FortiAnalyzer, with endpoint verification,…
 psylinux/cve-2026-129110-syspass
CVE-2026-129110: unauthenticated reinstallation RCE in sysPass 3.0.1 through 3.2.11
 llcforge/cve-2026-124020
Python PoC for CVE-2026-124020: Control Web Panel < 1.30.6 host header password-reset poisoning, recovery code capture, account takeover and RCE via…
 tempiltin/duplicate2shell-cve-2026-123751
Python PoC for CVE-2026-123751: exploits an unauthenticated file upload in the WP Duplicate WordPress plugin to deploy a PHP webshell, with version…
 racoten/suture-pic
A Windows implant development framework for offensive engineering and C2 research.
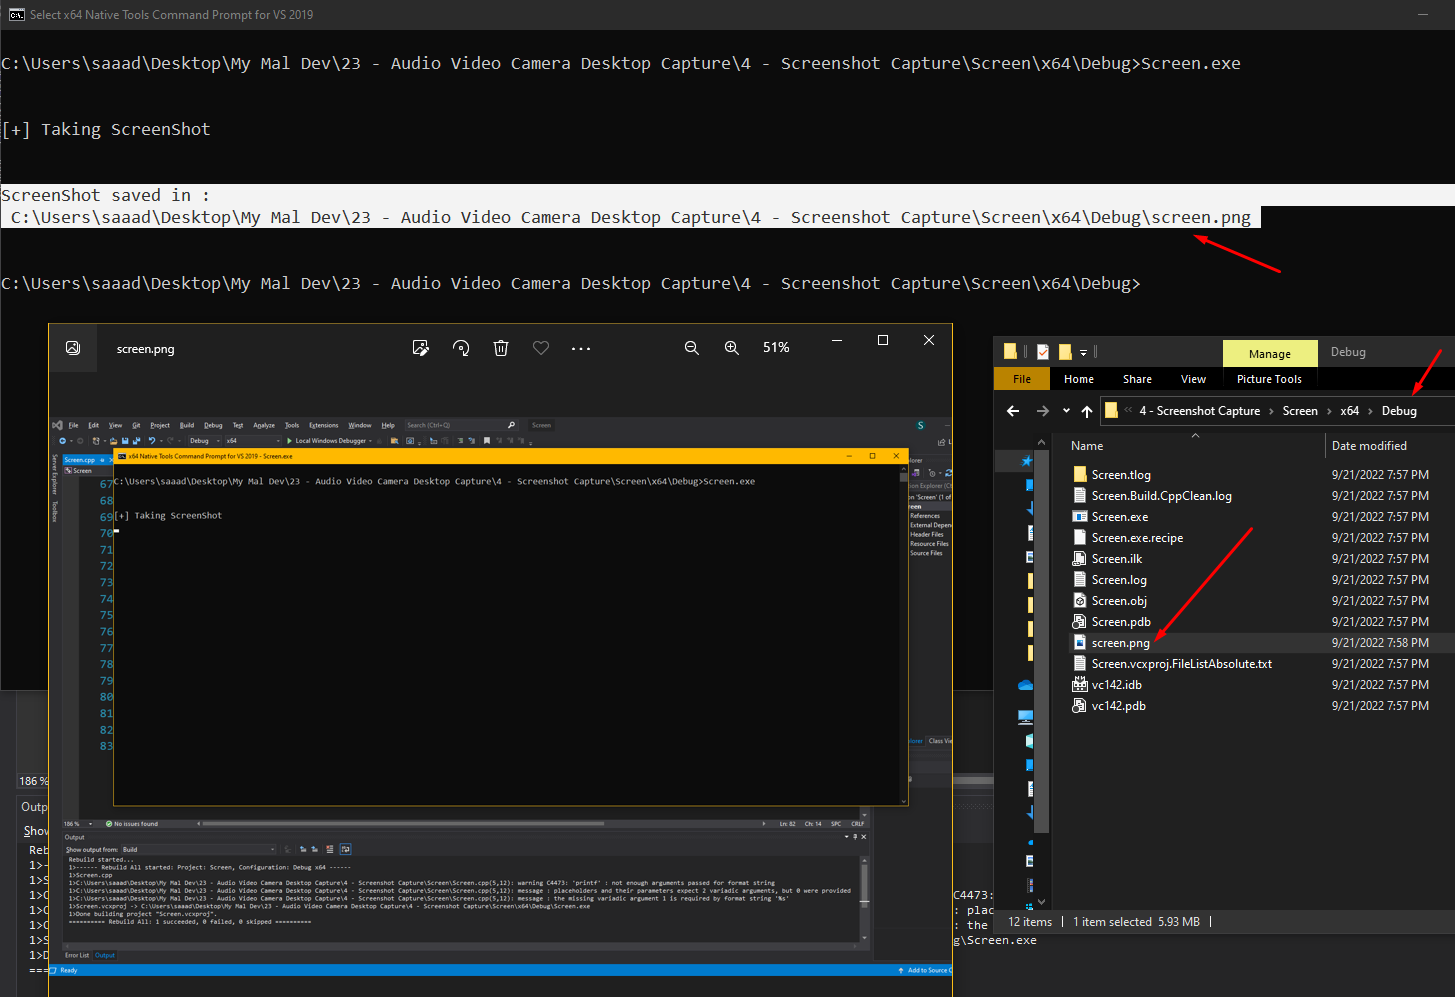 gmh5225/screenshot
C2 post-exploitation module that captures a screenshot of the compromised host's desktop and saves it as screen.png in the current working directory.
 hackerschoice/gsocket
Connect like there is no firewall. Securely.
 whitemachin3/cve-2026-31857
Python proof-of-concept that authenticates to Craft CMS control panel and verifies CVE-2026-31857 Twig injection RCE non-destructively using a…
 trx-0/cve-2026-33157-craftcms-rce
Craft CMS CVE-2026-33157 filter-hud behavior-injection RCE PoC
 hackfutsecroot/-gotenberg-rce-chain
Python exploit chain for Gotenberg CVE-2026-42589 and CVE-2026-40281: detects vulnerable instances, injects metadata payloads, and drops reverse…
 0xgh057r3c0n/cve-2026-40281
Python proof-of-concept exploit for CVE-2026-40281, an unauthenticated argument injection RCE in Gotenberg <= 8.30.1, with interactive shell and…
 industri4l-h3ll-xpl0it3rs/cve-2026-39987-marimo-rce
Python proof-of-concept exploiting an unauthenticated WebSocket terminal endpoint in Marimo (< 0.23.0) to achieve pre-auth remote code execution and…
 alannewberry/cve-2026-4480-samba-print-command-injection-rce
Exploit para CVE-2026-4480: inyeccion de comandos en la variable %J del print command de Samba para RCE sin autenticacion via spoolss.
 chu0119/vc-strike
Authorized pentest suite for VMware vCenter CVE-2026-59310 (unauth root RCE via rsyslog path traversal) and CVE-2026-59309 (SRP auth bypass), with…
 ly0kha/cve-2026-59774
Python PoC exploiting Gitea CVE-2026-59774: Org-mode #+INCLUDE local file read chained through INTERNAL_TOKEN admin takeover and git hook injection…
 alisalive/xss2shell
CVE-2026-64638 | WordPress < 7.0.3 Pre-Auth Stored XSS → RCE
 t54r/cve-2026-10795_poc
AI amended PoC for CVE-2026-10795 - for educational purposes only - use at your own risk on labs you own ;)