Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
Auto-Elevate — Escalate from a low-integrity Administrator account to NT AUTHORITY\SYSTEM without an LPE exploit by combining a COM UAC bypass and Token Impersonation | Kitploit
Tools/GitHubGitHub/fullshade/auto-elevate
Privilege EscalationExploitationPenetration TestingRed Teaming
GitHubfullshade/auto-elevate

Auto-Elevate

Escalate from a low-integrity Administrator account to NT AUTHORITY\SYSTEM without an LPE exploit by combining a COM UAC bypass and Token Impersonation

View Repository
16179324 years agoReviewed by Kitploit
Share

Auto-Elevate

This tool demonstrates the power of UAC bypasses and built-in features of Windows. This utility auto-locates winlogon.exe, steals and impersonates it's process TOKEN, and spawns a new SYSTEM-level process with the stolen token. Combined with UAC bypass method #41 (ICMLuaUtil UAC bypass) from hfiref0x's UACME utility, this utility can auto-elevate a low privileged Administrative account to NT AUTHORITY\SYSTEM.


The following image demonstrates using UACME combined with Auto-Elevate to go from a low-privileged Administrator account to NT AUTHORITY\SYSTEM on Windows 10 21H1.

image

The following image demonstrates escalation from a high-privileged Administrator account to SYSTEM without a UAC bypass
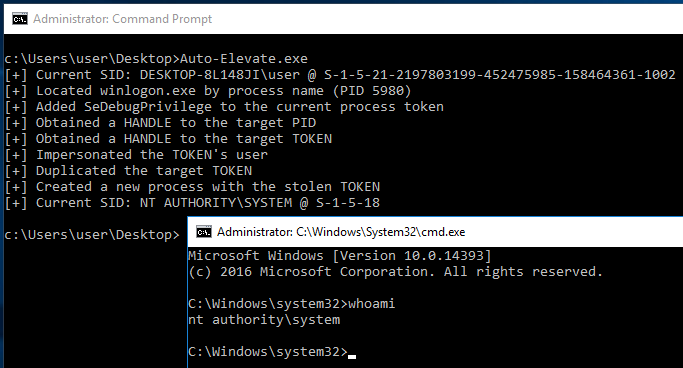
image

Technical Explanation

The following steps are performed by Auto-Elevate to escalate from a low-privileged Administrator to SYSTEM:
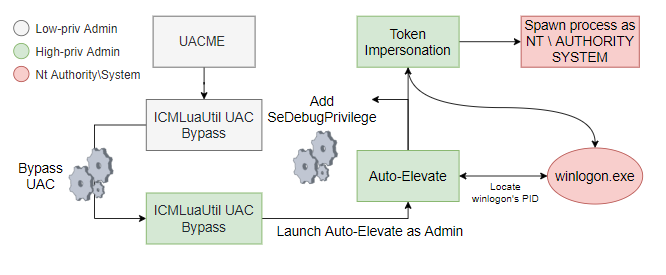
image

Auto-Elevate

  1. The winlogon.exe process is located by enumerating the systems running processes with CreateToolhelp32Snapshot, Process32First, and Process32Next
  2. SeDebugPrivilege is enabled for the current process via a call to AdjustTokenPrivileges, as it's required to open a HANDLE to winlogon.exe
  3. A handle to the winlogon.exe process is opened by calling OpenProcess, for this call PROCESS_ALL_ACCESS is used (however, it's overkill)
  4. A handle to winlogon's process token is retrieved by calling OpenProcessToken combined with the previously obtained process handle 
  5. The user (SYSTEM) of winlogon is impersonated by calling ImpersonateLoggedOnUser
  6. The impersonated token handle is duplicated by calling DuplicateTokenEx with SecurityImpersonation, this creates a duplicated token we can use
  7. Using the duplicated, and impersonated token a new CMD instance is spawned by calling CreateProcessWithTokenW

To-Do

  • Implement a standalone version of method 41 from UACME (or similar) to automate the process further

MITRE ATT&CK Mapping

  • Token Manipulation: T1134
  • Access Token Manipulation: Token Impersonation/Theft: T1134.001
  • Access Token Manipulation: Create Process with Token: T1134.002
  • Access Token Manipulation: Make and Impersonate Token: T1134.003

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    871
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    548
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    383
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    361
  • 5

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    305
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    280

Explore all tools

Browse our collection of tools

View all tools →








