
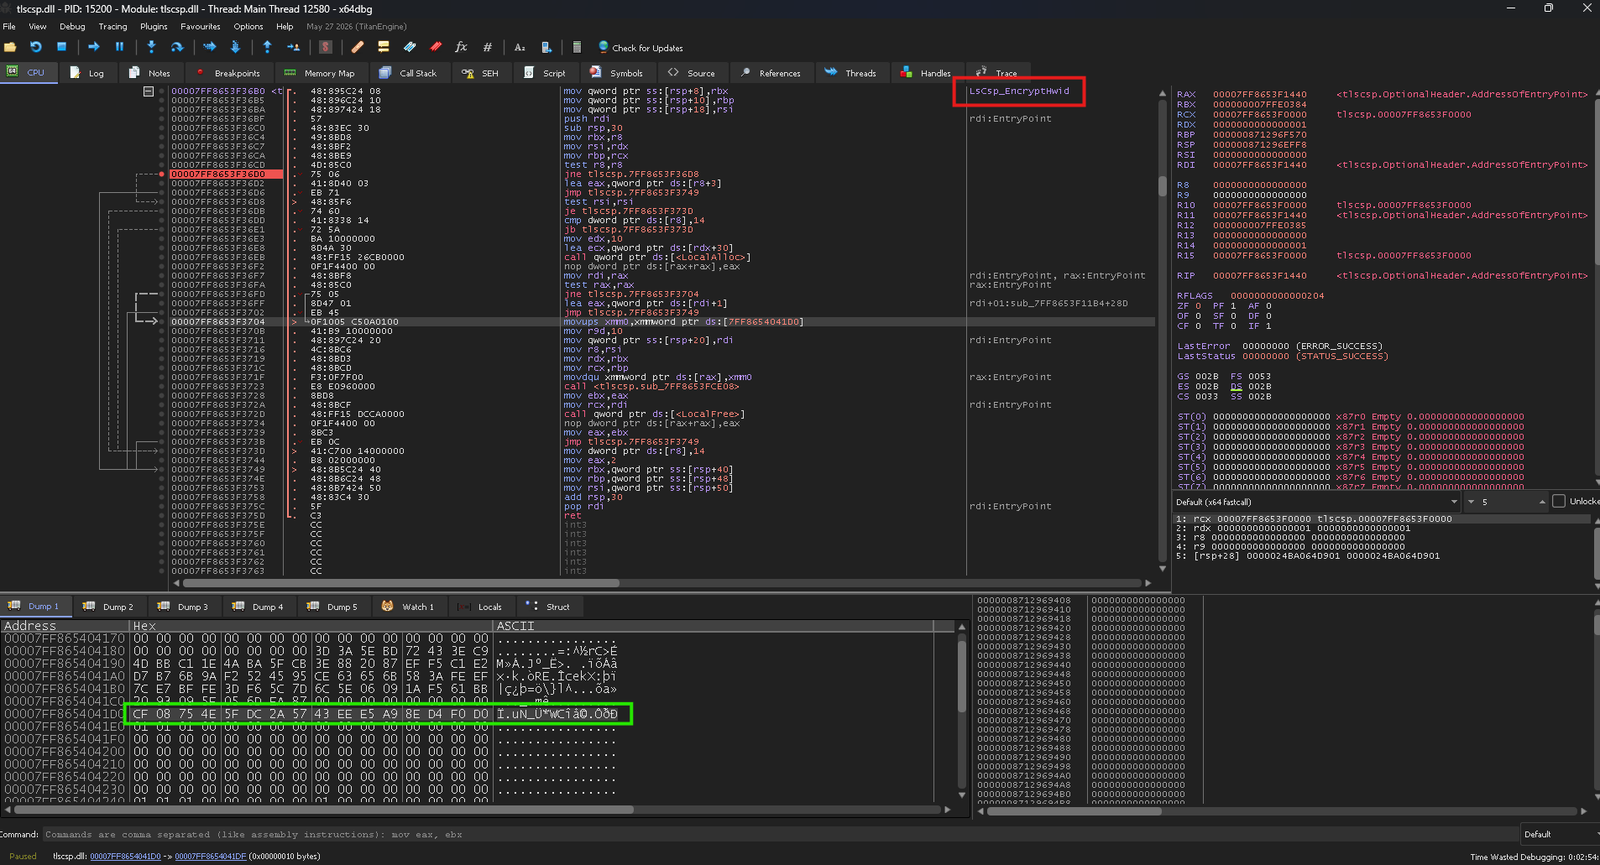
RC4Decryption
 weedhashpeddler/rc4decryption
Abuses the Microsoft-signed tlscsp.dll LOLBin to run RC4 encrypt/decrypt via LsCsp_EncryptHwid, patching the hardcoded key in memory for BYOK…
binary-analysiscryptographydefensive-tools+6
35
weedhashpeddler/rc4decryptionAbuses the Microsoft-signed tlscsp.dll LOLBin to run RC4 encrypt/decrypt via LsCsp_EncryptHwid, patching the hardcoded key in memory for BYOK…
 racoten/reflectivepluginloader
A minimal PE mapper that loads DLLs straight from memory and calls into a clean plugin interface, no LoadLibrary needed.
 jssngc/ontheedge
Windows research PoC in C that scans Microsoft Edge process memory for credential-related data, with a standalone executable and a BOF variant for C2…
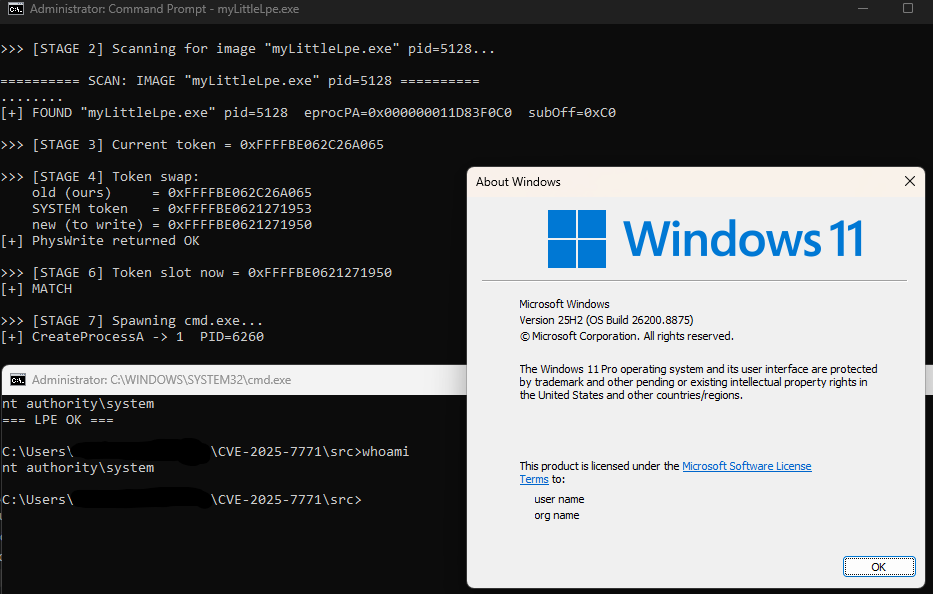 yulisec/cve-2025-7771
Full exploit chain for CVE-2025-7771 in ThrottleStop.sys, abusing unvalidated physical memory R/W IOCTLs to escalate from administrator to SYSTEM on…
 nbs32k/localstranger
PoC for WinNotify, demonstrated through a driver mapper, and local privilege escalation.
 rurixis/msrkit
A concept of using a ROP chain paired with a WRMSR primitive to call kernel functions and map unsigned drivers through BYOVD (AmdTools64.sys)
 geozstevenzz/cve-2024-30804
Windows LPE PoC exploiting the AsInsHelp64.sys driver via arbitrary physical memory read/write to overwrite kernel tokens and gain SYSTEM privileges.
 gmh5225/exploit-asio-exploit
AsIO3.sys auth bypass and local privesc proof-of-concept
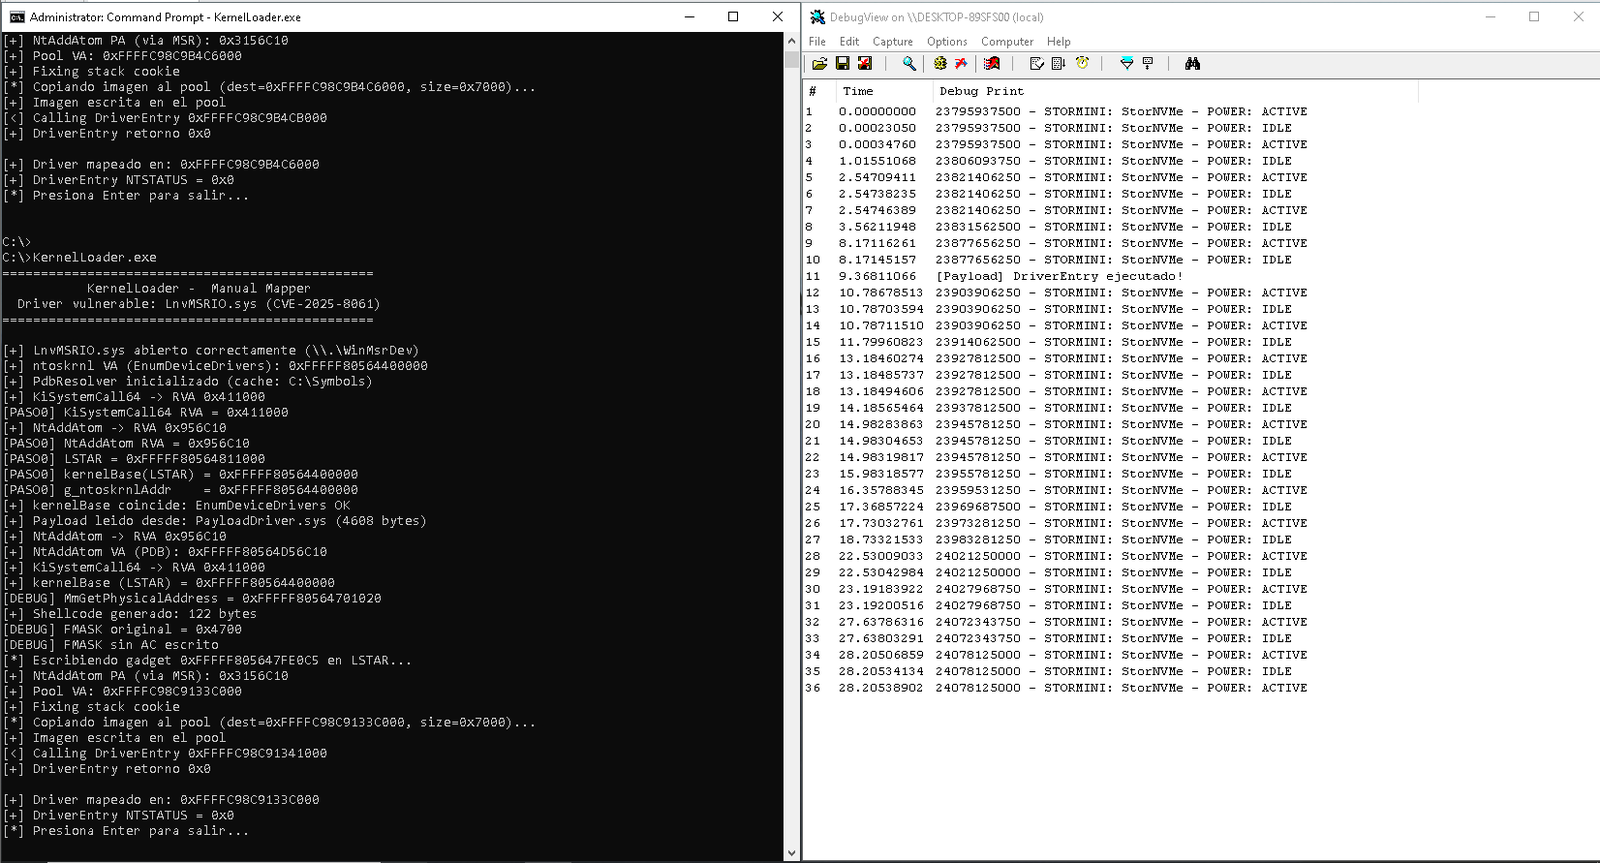 ull0a/msrmapper
Manual kernel driver mapper for Windows x64 that abuses CVE-2025-8061 in Lenovo's LnvMSRIO.sys to perform a BYOVD attack, mapping PE64 drivers into…
 idov31/silverseal
Linux post-exploitation framework with a UEFI bootkit that persistently and stealthily loads a Rust-based kernel module rootkit on modern Linux…
 gmh5225/dsark64
BYOVD proof-of-concept abusing the WHQL-signed DsArk64.sys driver for ring-0 process termination and kernel read/write via encrypted IOCTLs and…
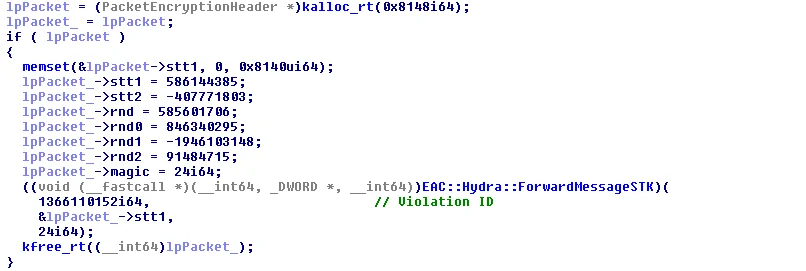 gmh5225/eac-kernel-packet-fucker
Reverse-engineered Easy Anti-Cheat kernel driver bypass that intercepts memory allocation to suppress violation packets, with report decryption…
 0xf9b6a41ec/cve-2026-69328
Windows privilege escalation exploit that plants SprintCSP.dll in a user-writable HKLM PATH directory to hijack StorSvc and execute as SYSTEM.
 ull0a/bdapiutil-bydov
C++ Windows research tool for studying the BdApiUtil64.sys vulnerable driver and CVE-2024-51324
 wqsv/throttlestoppoc
CVE-2025-7771: Arbitrary physical memory and I/O port read/write via ThrottleStop driver
 rubbxalc/cve-2021-32675
Functional DoS exploit for CVE-2021-32675 in Redis, leveraging oversized bulk string headers to trigger memory exhaustion. Includes usage…
 ymsniper/umbra
External read-only game overlay for Linux. Derived offsets, composed skeletons, optional kernel module for ptrace-independent memory reads and…
 gmh5225/cs-memoryevasion
A Cobalt Strike memory evasion loader for redteamers