CVE-2026-33439-PoC
Python PoC exploiting CVE-2026-33439, a pre-auth RCE in OpenAM via Java deserialization of the jato.clientSession parameter, with interactive and…

Python PoC exploiting CVE-2026-33439, a pre-auth RCE in OpenAM via Java deserialization of the jato.clientSession parameter, with interactive and…

PEASS - Privilege Escalation Awesome Scripts SUITE (with colors)

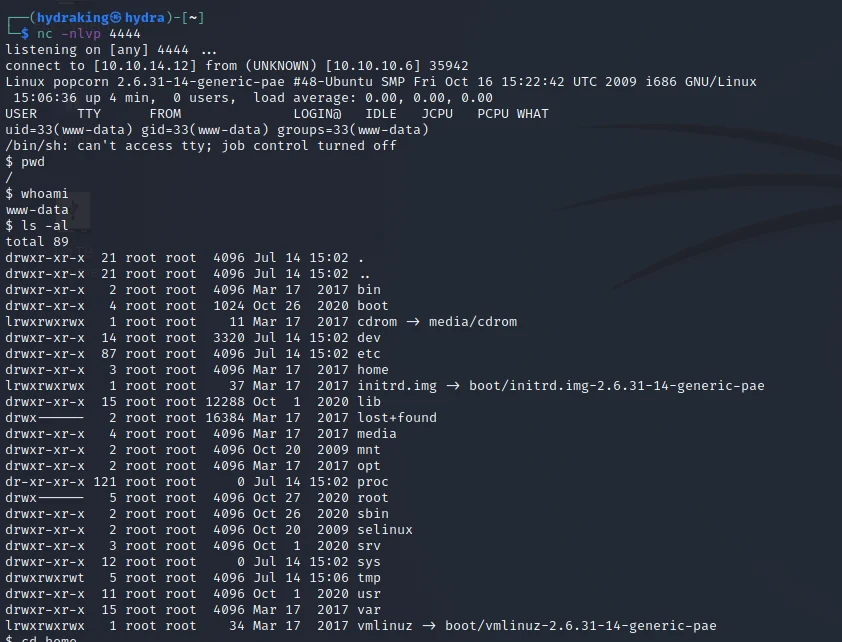
Simple PHP reverse shell script for establishing remote command execution on target systems. Ideal for penetration testing and security assessments.

A Windows reverse shell payload generator and handler that abuses the http(s) protocol to establish a beacon-like reverse shell.

A fileless reverse shell and C2 framework leveraging direct syscalls, proxy tunneling, and ChaCha20 encryption for AV evasion.

红/蓝队环境自动化部署工具 | Red/Blue team environment automation deployment tool

Multi-session reverse shell handler with PTY upgrade, post-exploitation modules, Layer 3 tunneling, payload obfuscation for EDR evasion, session…

Hosted Reverse Shell generator with a ton of functionality. -- (Great for CTFs)

Embed a reverse shell in Notion pages using the Notion API as a proxy, enabling stealthy remote shell sessions with encrypted and authenticated…

Authenticated remote code execution exploit for Roundcube 1.6.10 (CVE-2025-49113). Delivers a reverse shell via a crafted PHP payload through the…

Exploit for CVE-2025-50505 in Clash Verge Rev, demonstrating local privilege escalation and remote code execution via unauthenticated API, including…

Python exploit for CVE-2021-22941 targeting Citrix ShareFile RCE with shell and ping options for remote command execution and network probing.

Proof-of-concept exploit for CVE-2021-44228 (Log4Shell) remote code execution vulnerability in Apache Log4j. Includes shell script for testing and…

Netcat with automated NAT traversal, secure P2P, and advanced features for shell access, file transfer, and network proxying.

An interactive command-line shell for BloodHound API.

Linux privesc enumerator that confirms exploitability and gives you the exact root shell command - no GTFOBins searching. MCP server + AI-agent…

Exploiting a Cross-site request forgery (CSRF) attack to creat a new privileged user through the Webmin's add users feature

A webshell plugin and interactive shell for pentesting a Joomla website.