
cve-2021-42013
 walnutsecurity/cve-2021-42013
cve-2021-42013.py is a python script that will help in finding Path Traversal or Remote Code Execution vulnerability in Apache 2.4.50
exploitationlabs-practicepenetration-testing+3
27
walnutsecurity/cve-2021-42013cve-2021-42013.py is a python script that will help in finding Path Traversal or Remote Code Execution vulnerability in Apache 2.4.50
 davuxvi/cve-2023-27163
Proof-of-concept exploit for CVE-2023-27163, a Server-Side Request Forgery (SSRF) vulnerability in request-baskets up to v1.2.1. Includes automated…
 romain-deperne/cve-2026-33715
Unauthenticated SSRF and open email relay in Chamilo LMS — CVE-2026-33715 / CVSS 7.2
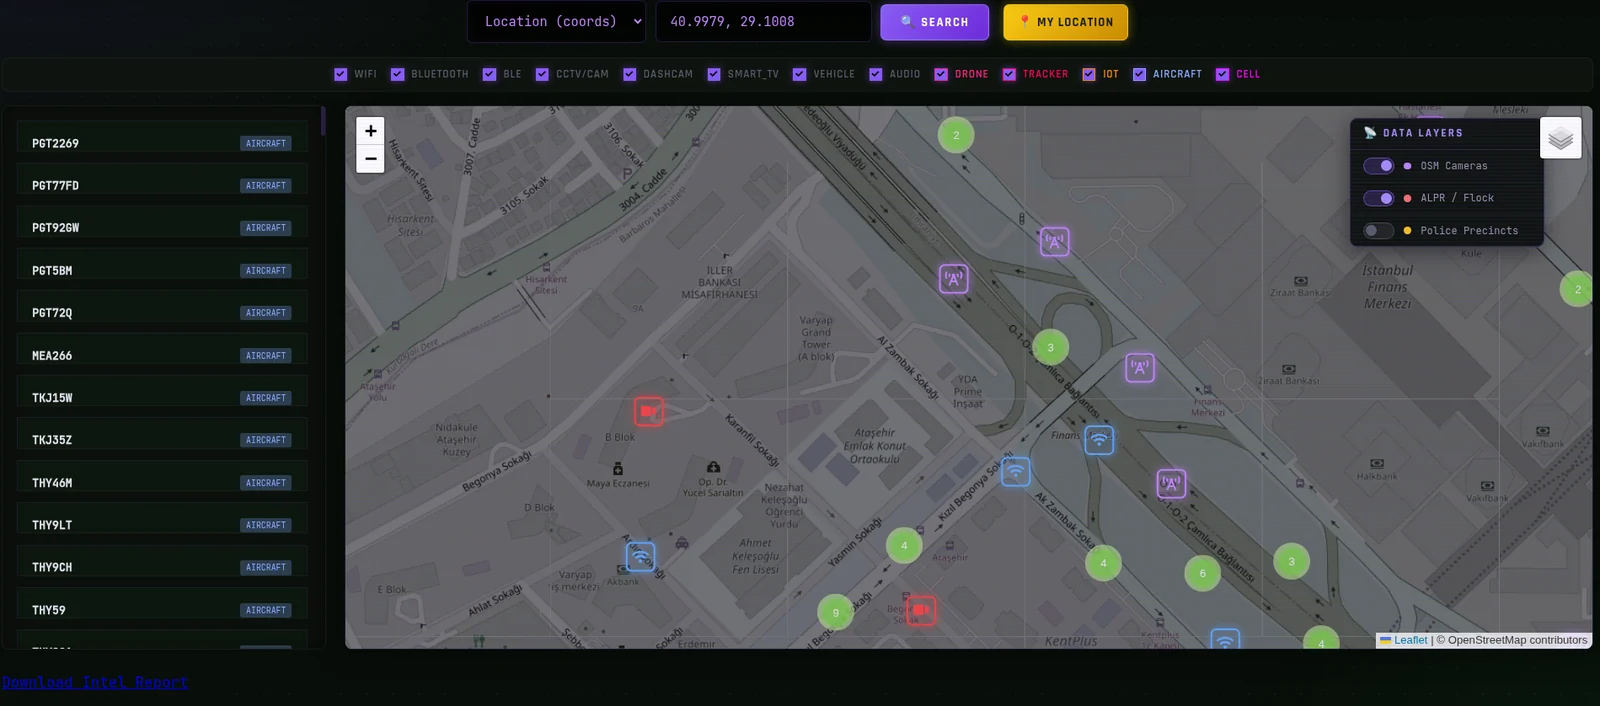 emrekybs/signalops
All-source intelligence fusion dashboard — WiFi, cellular, CCTV, ADS-B, orbital & SDR feeds unified into a single tactical map. Security research…
 justicerage/freedomfighting
A collection of scripts which may come in handy during your freedom fighting activities.
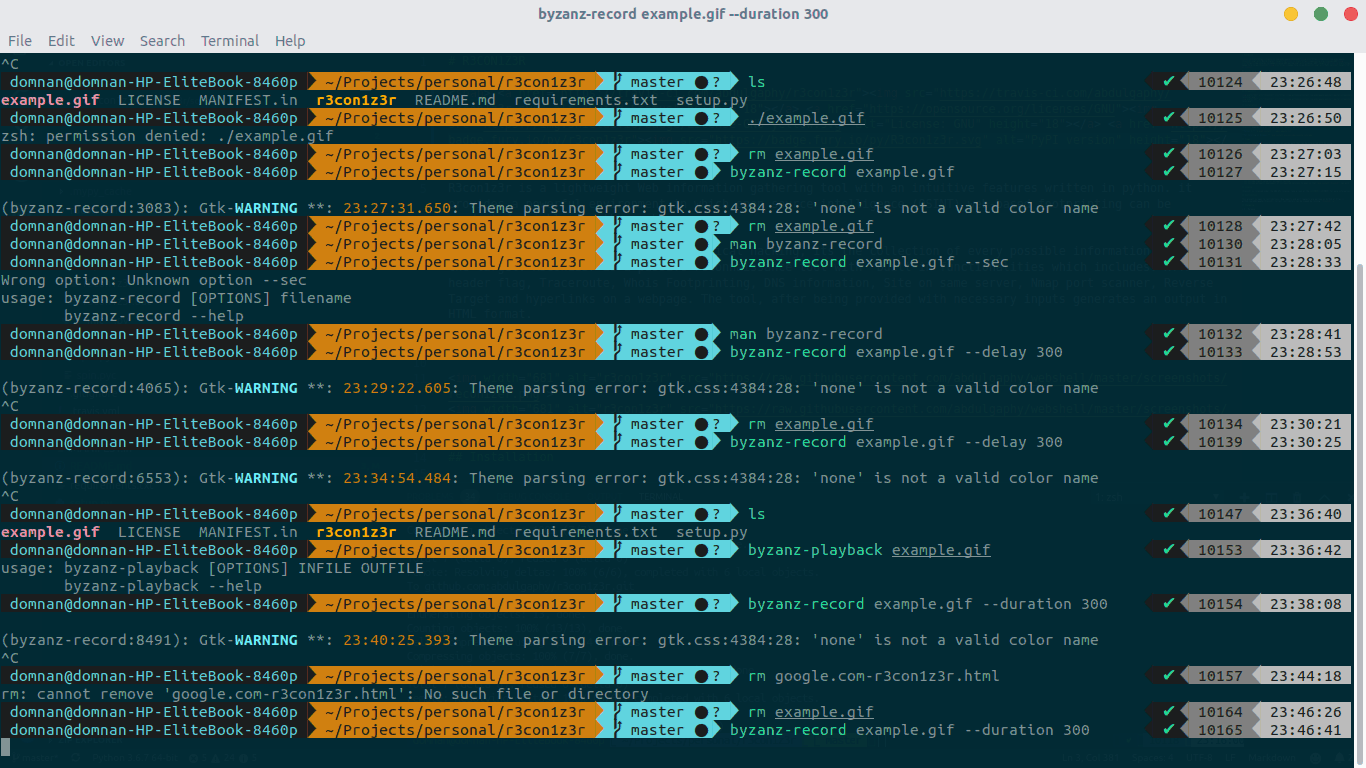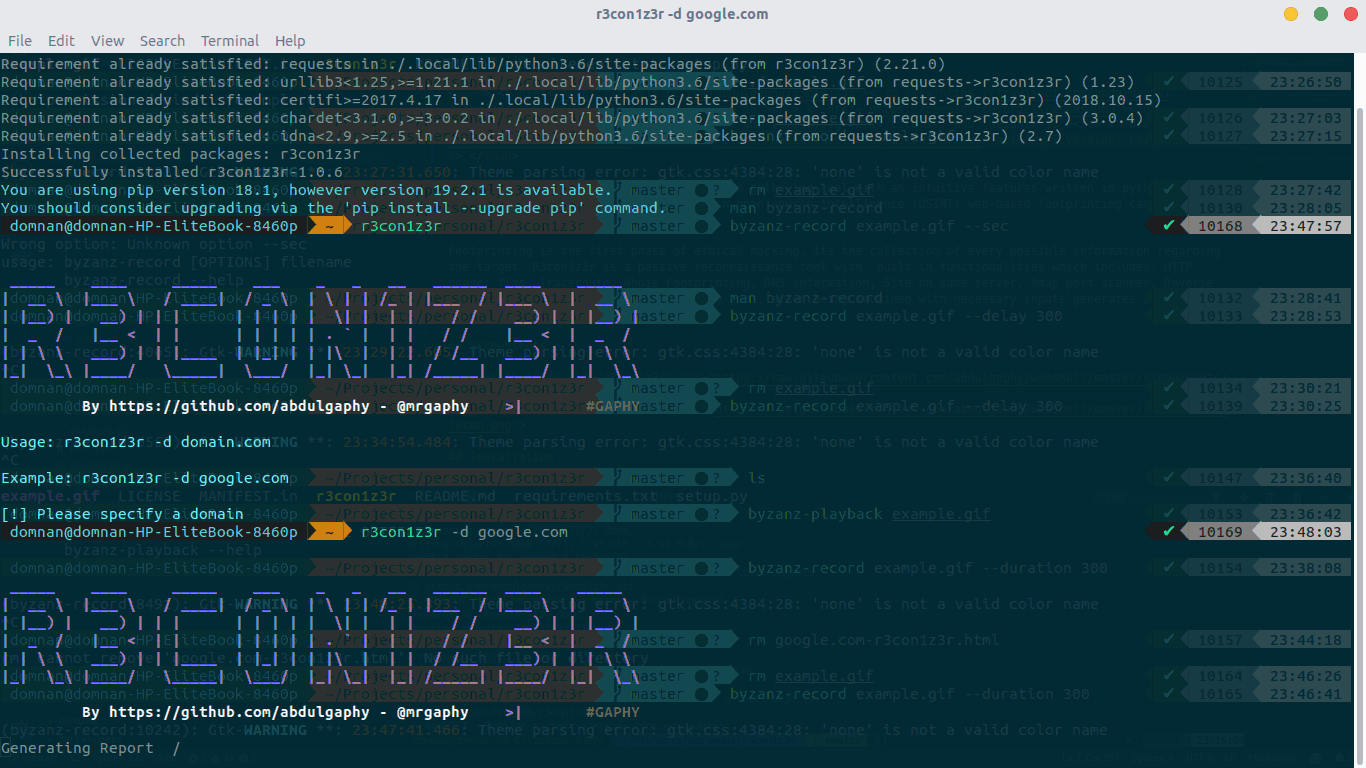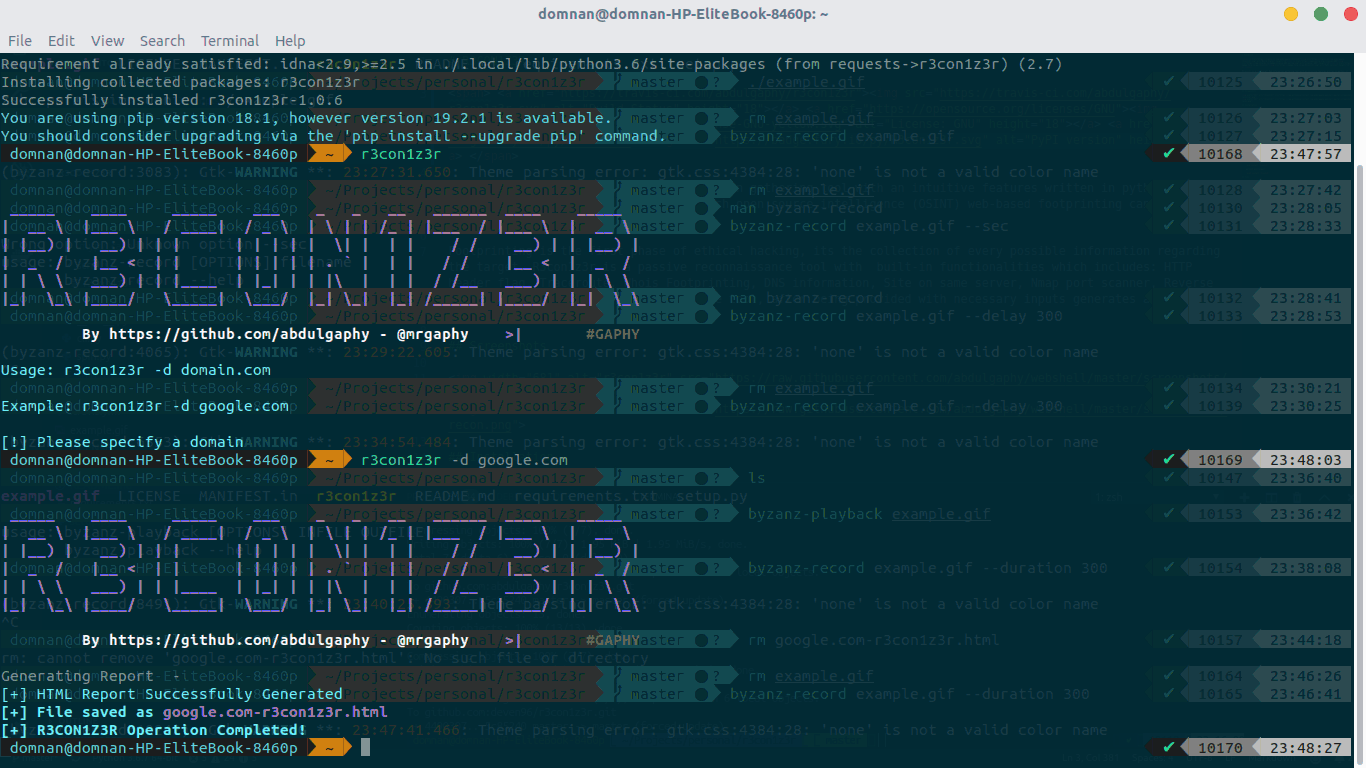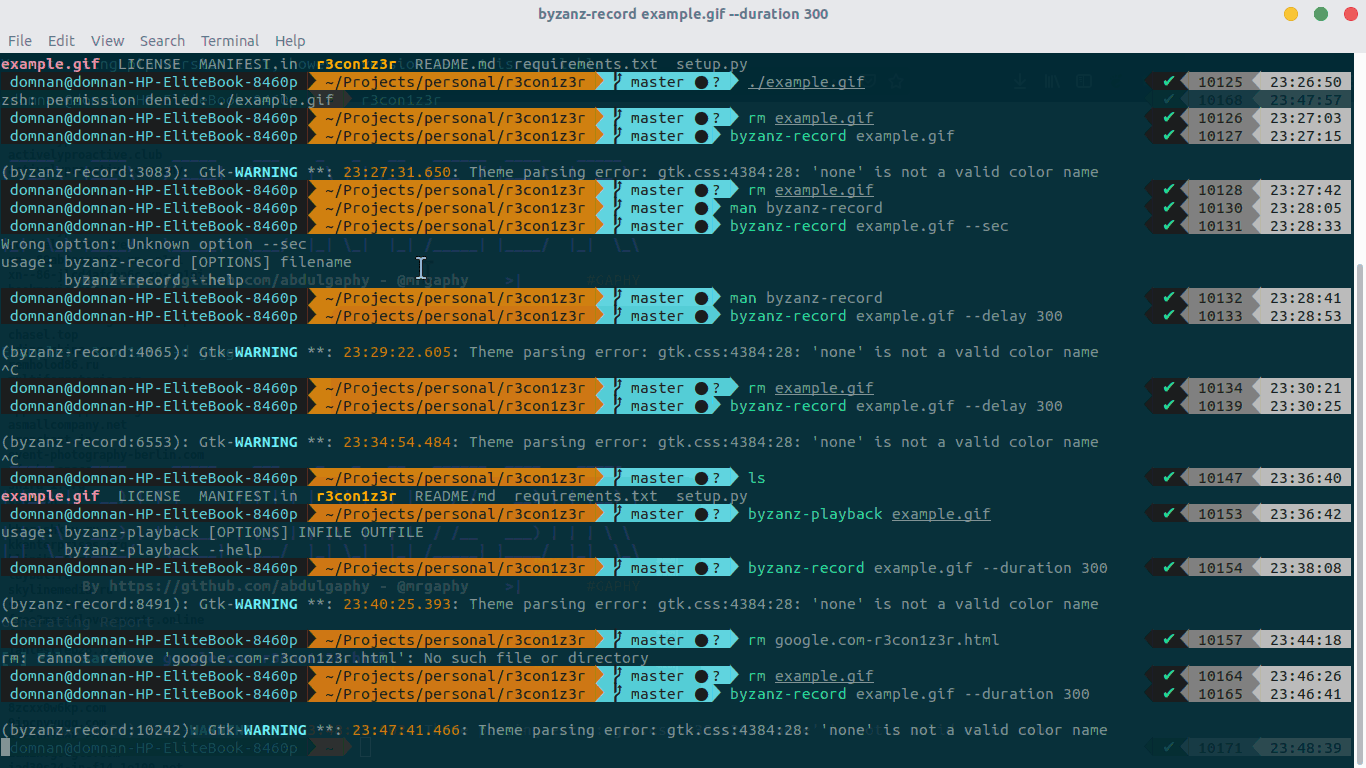 abdulgaphy/r3con1z3r
R3con1z3r is a lightweight Web information gathering tool with an intuitive features written in python. it provides a powerful environment in which…
 agampreet-singh/redroot
RedRoot is a Python-based, CLI-driven offensive security framework that brings essential red teaming tools into one unified terminal environment.…
 leo4j/invoke-adenum
Automated Active Directory auditing and enumeration tool that generates detailed HTML audit reports with CSV/XLSX export, designed for security…
 hackhermind-pixel/vulnerable-lab-exploitation
A hands-on project demonstrating the setup of virtual security lab, network reconnaissance, and exploitation of CVE-2012-1823.
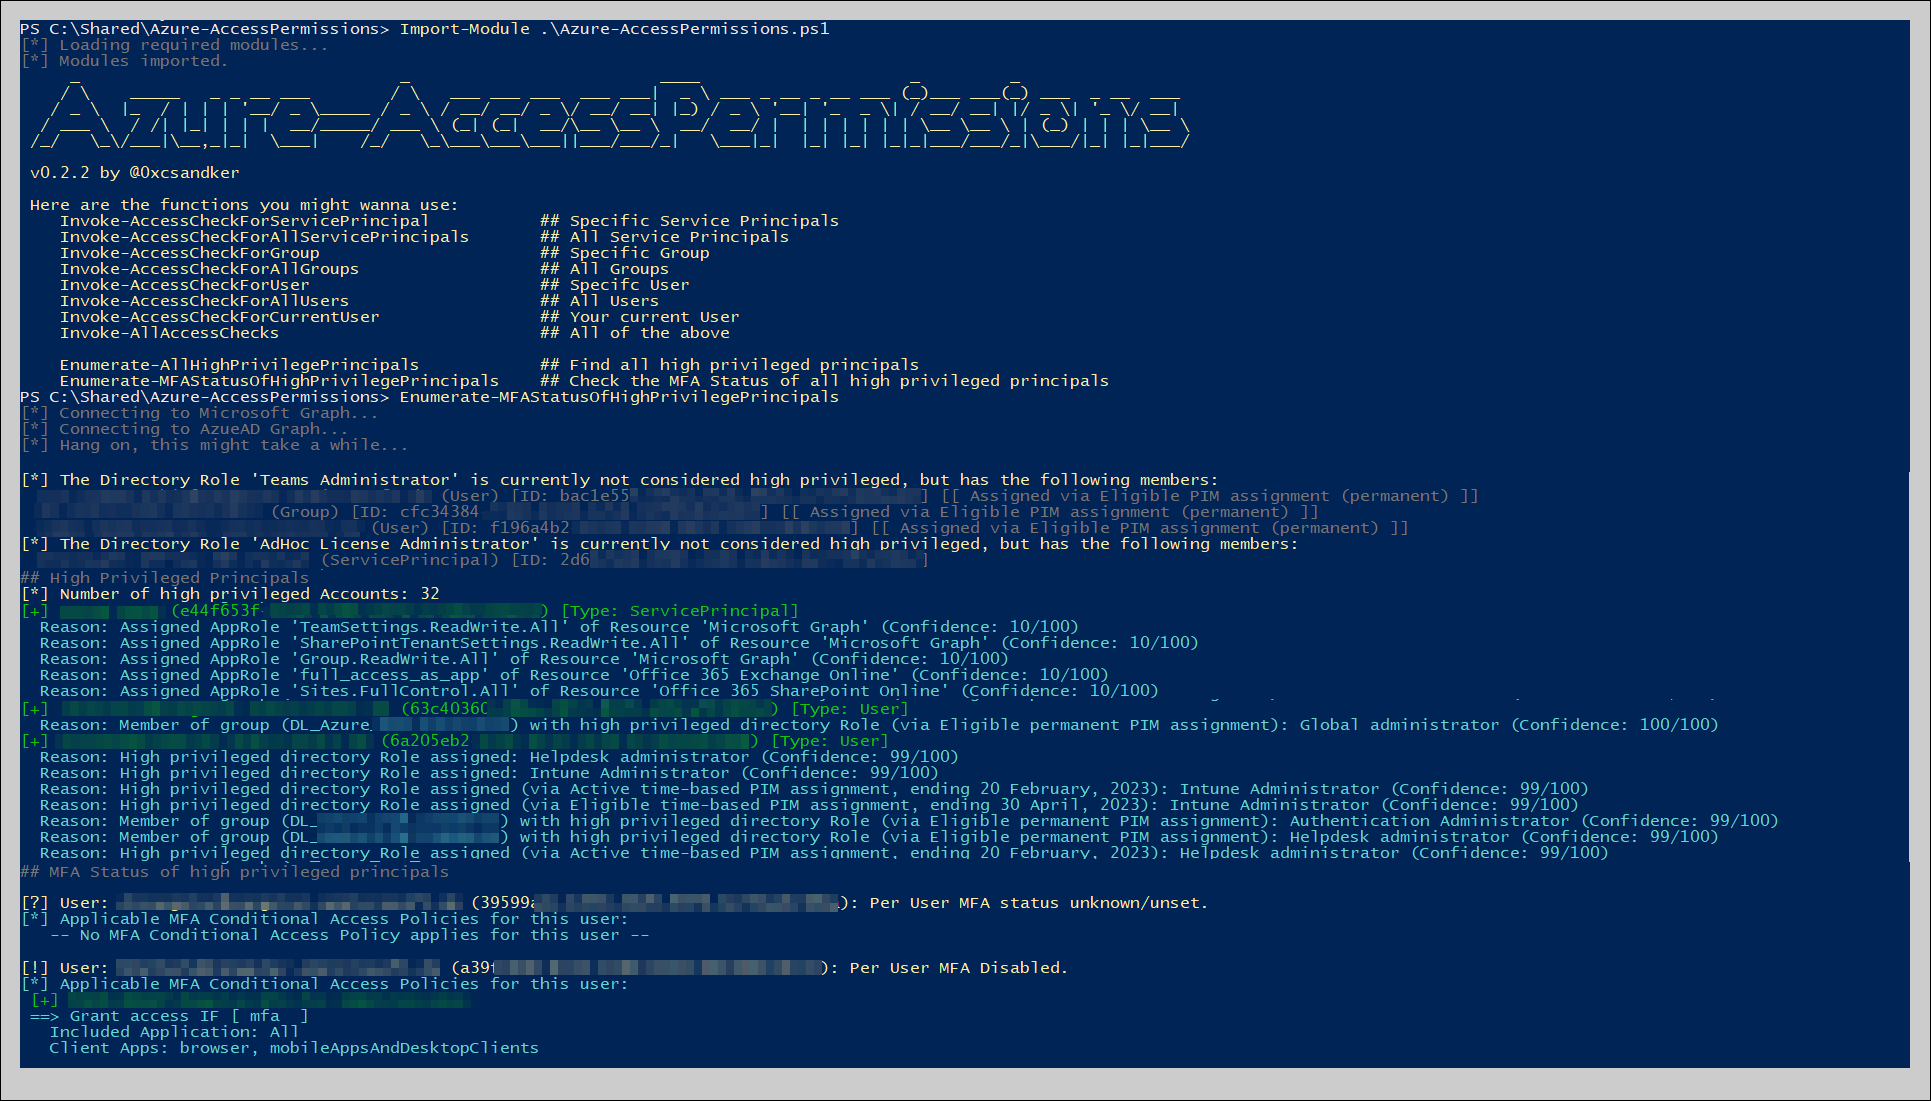 csandker/azure-accesspermissions
PowerShell script to enumerate Azure Active Directory access permissions, including role assignments, service principals, and privileged access…
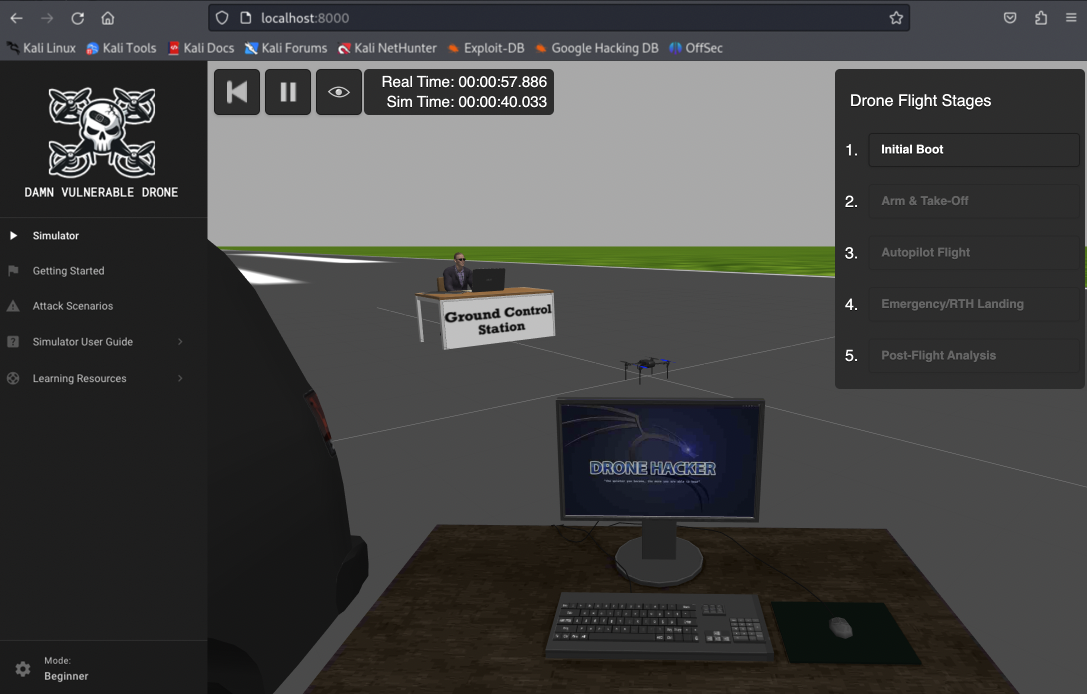 nicholasaleks/damn-vulnerable-drone
Damn Vulnerable Drone is an intentionally vulnerable drone hacking simulator based on the popular ArduPilot/MAVLink architecture, providing a…
 aaaguirrep/offensive-docker
Offensive Docker is an image with the more used offensive tools to create an environment easily and quickly to launch assessment to the targets.
 zephrfish/azureattackkit
Collection of Azure Tools to Pull down for Attacking an Environment + quick tips and other useful information
 adfortunato/metasploitable3-pentest-writeup
Home-lab penetration test report of Metasploitable3 covering Nmap recon, Drupalgeddon RCE, SQL injection, SSH credential reuse, sudo privilege…
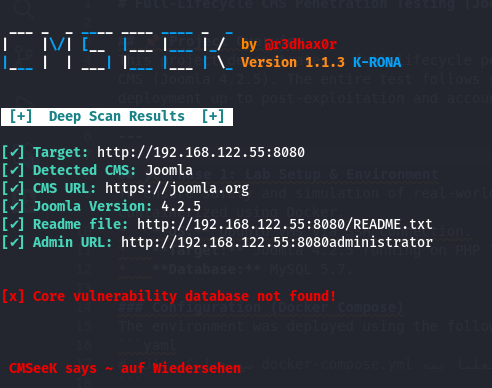 marwan651/joomla-cms-full-lifecycle-pentest
A comprehensive full-lifecycle penetration testing project on Joomla 4.2.5 exploiting CVE-2023-23752 inside a Dockerized lab environment
 captmag/maldev
Creation of multiple Malware tools consisting of evasion, enumeration and exploitation
 amirmuhammadmarvi/network-security-lab
Controlled virtual attack & defense lab — CVE-2011-2523 exploitation, Nmap recon, Nikto scanning, UFW hardening on Metasploitable 2
 deepakkcybersec-eng/kioptrix-level1-vulnerability-analysis
Technical audit of Kioptrix Level 1. Focus: Samba 2.2.1a exploitation (CVE-2003-0201), manual enumeration, and internal infrastructure hardening.